TipHand-cipher rules: CAESAR C = (P + k) mod 26 ·
VIGENÈRE add the repeated key letter (subtract to decrypt) ·
PLAYFAIR pairs: same row → right, same column → below, rectangle
→ own row, other letter’s column; X between doubles · HILL row
vector × K mod 26, decrypt with K⁻¹ (det must be coprime with
26) · TRANSPOSITION write in rows, read columns in key order.
Exam weight Low
- Encryption/decryption → foundations → classical ciphers → block ciphers → modes → attacks.
Exam weight Low
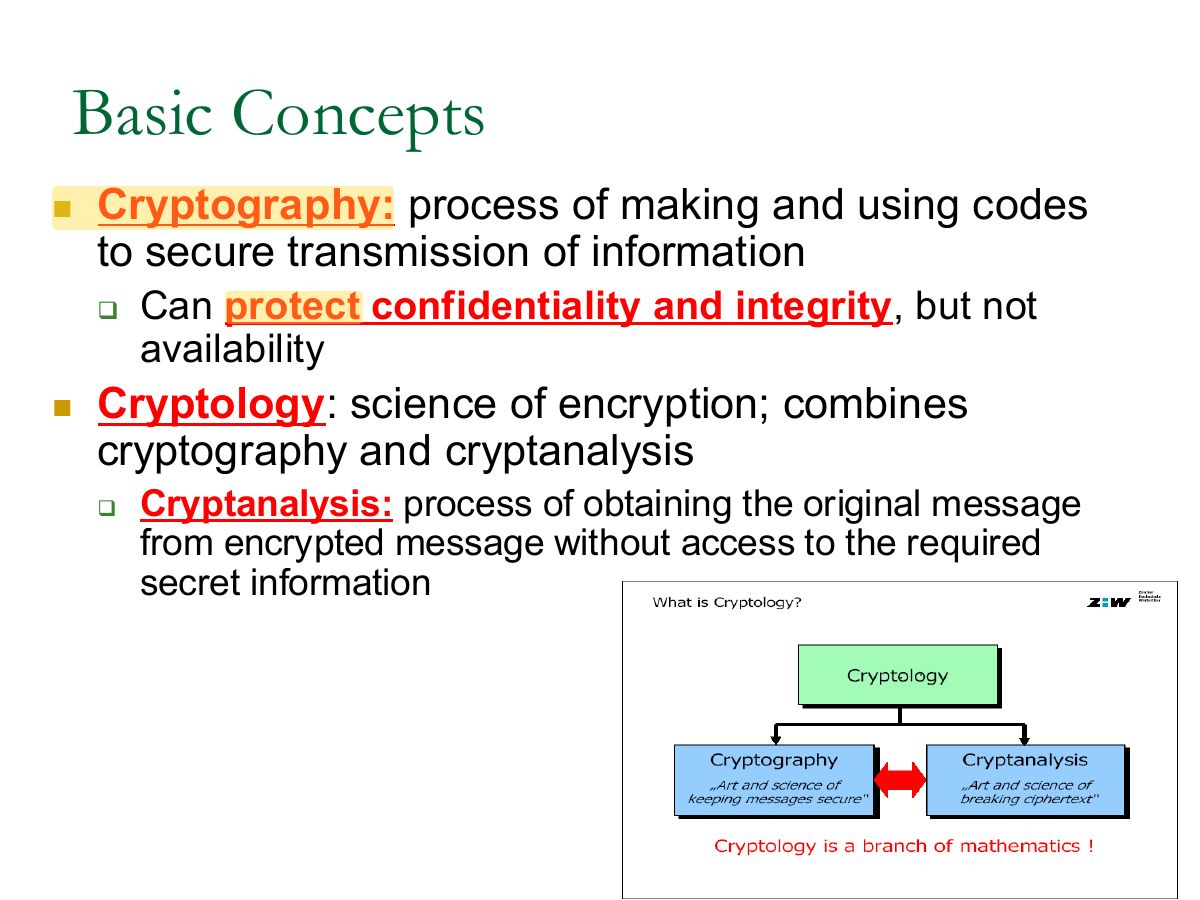
- Cryptography = “secret writing”: the science and art of transforming messages to make them secure.
Exam weight Low
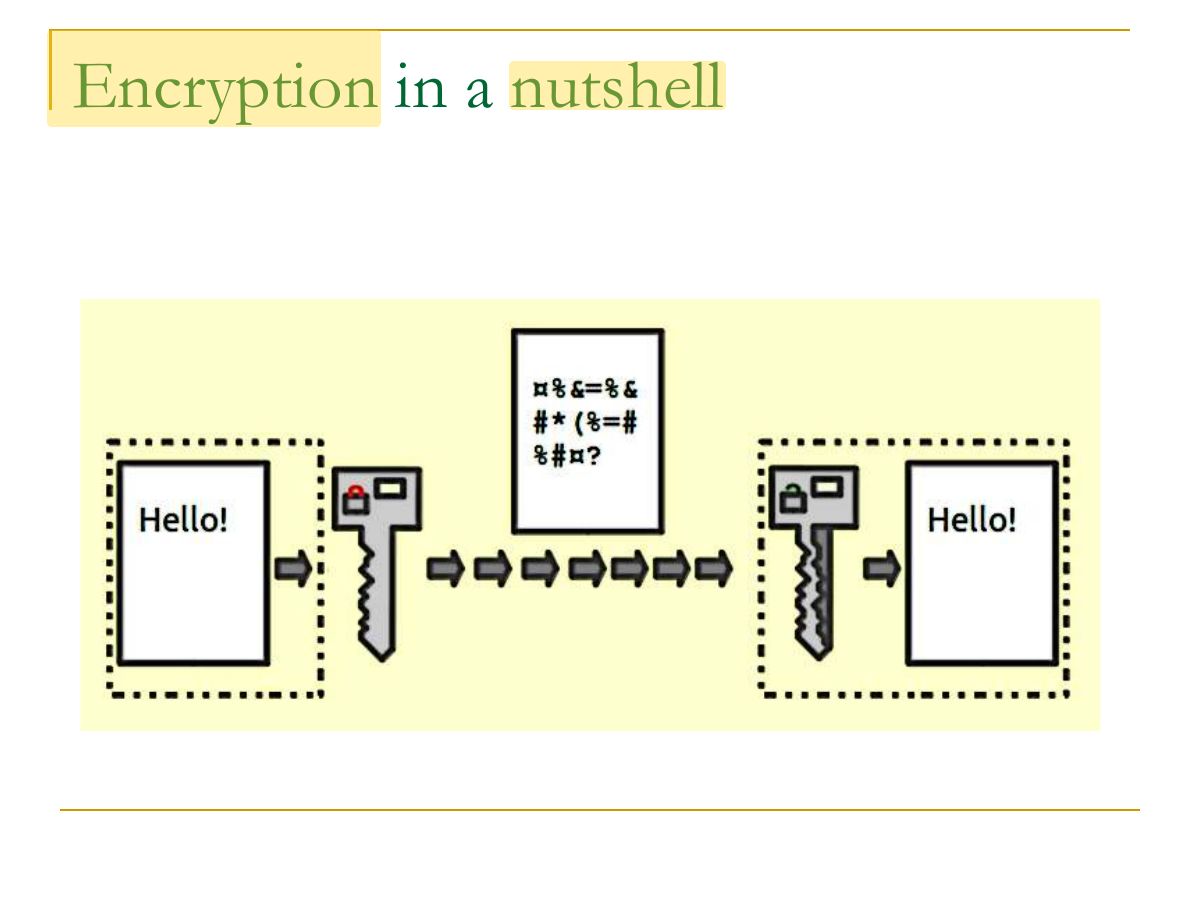
- Encryption in a nutshell: plaintext + key → ciphertext → (key) → plaintext.
Exam weight Low
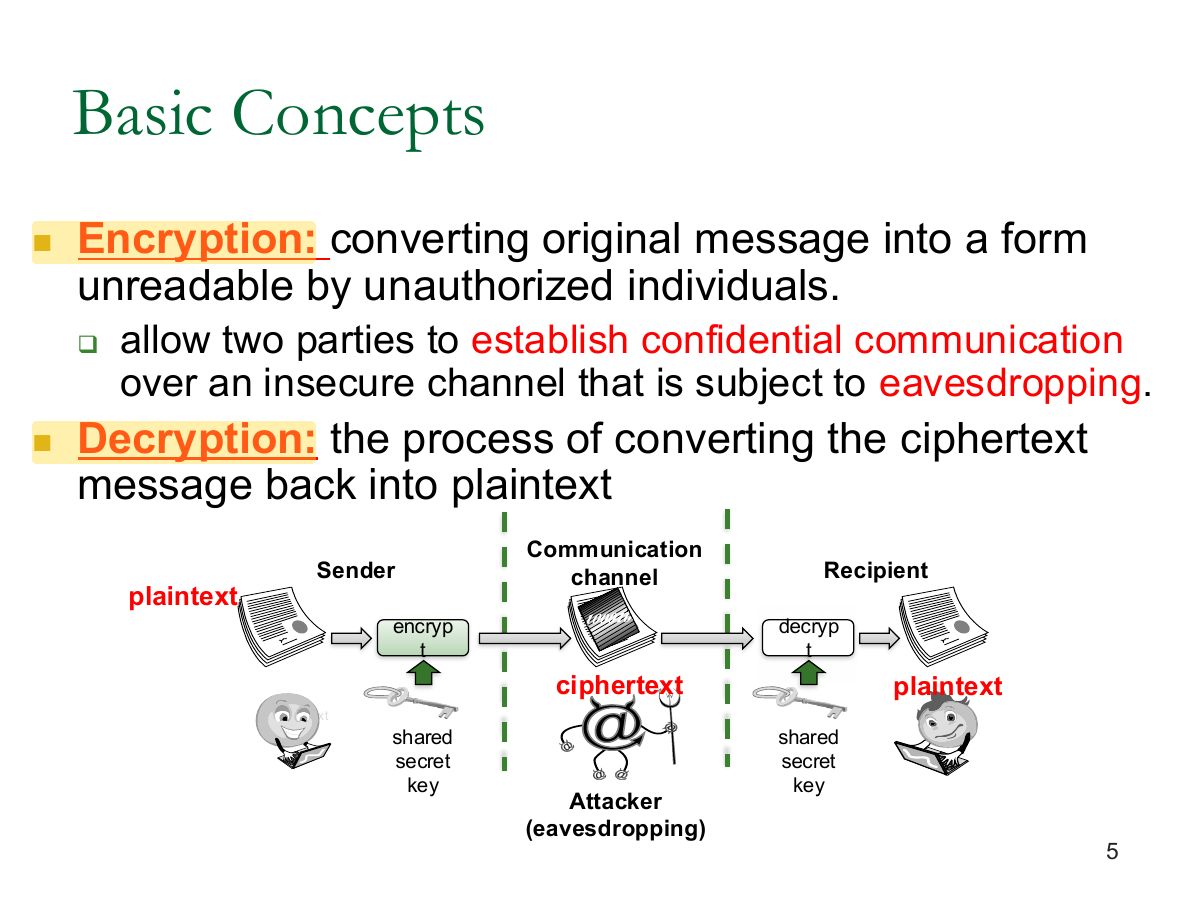
- Encryption converts a message into a form unreadable by unauthorized people, giving confidential communication over an insecure channel.
Exam weight Low
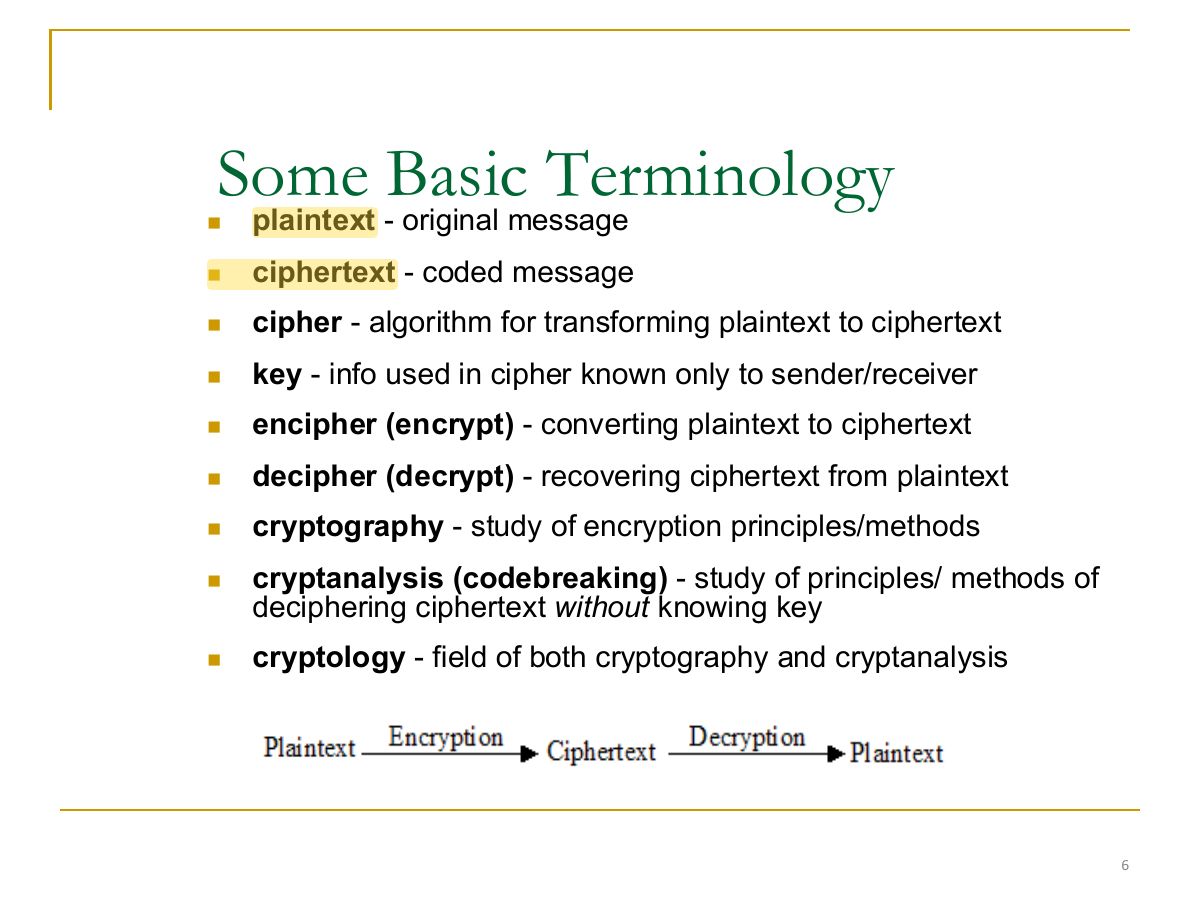
- Plaintext, ciphertext, cipher (algorithm), key, encipher/decipher, cryptanalysis, cryptology.
Exam weight Low
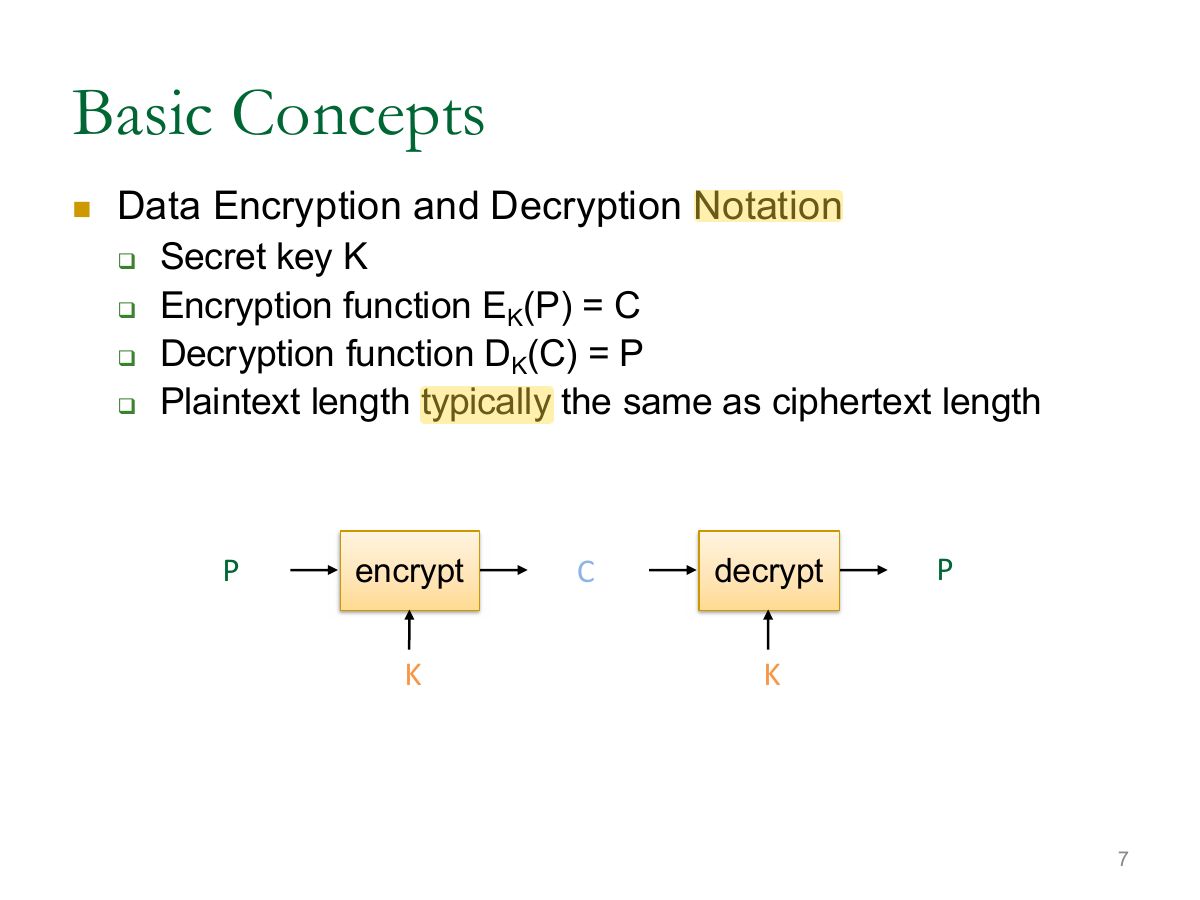
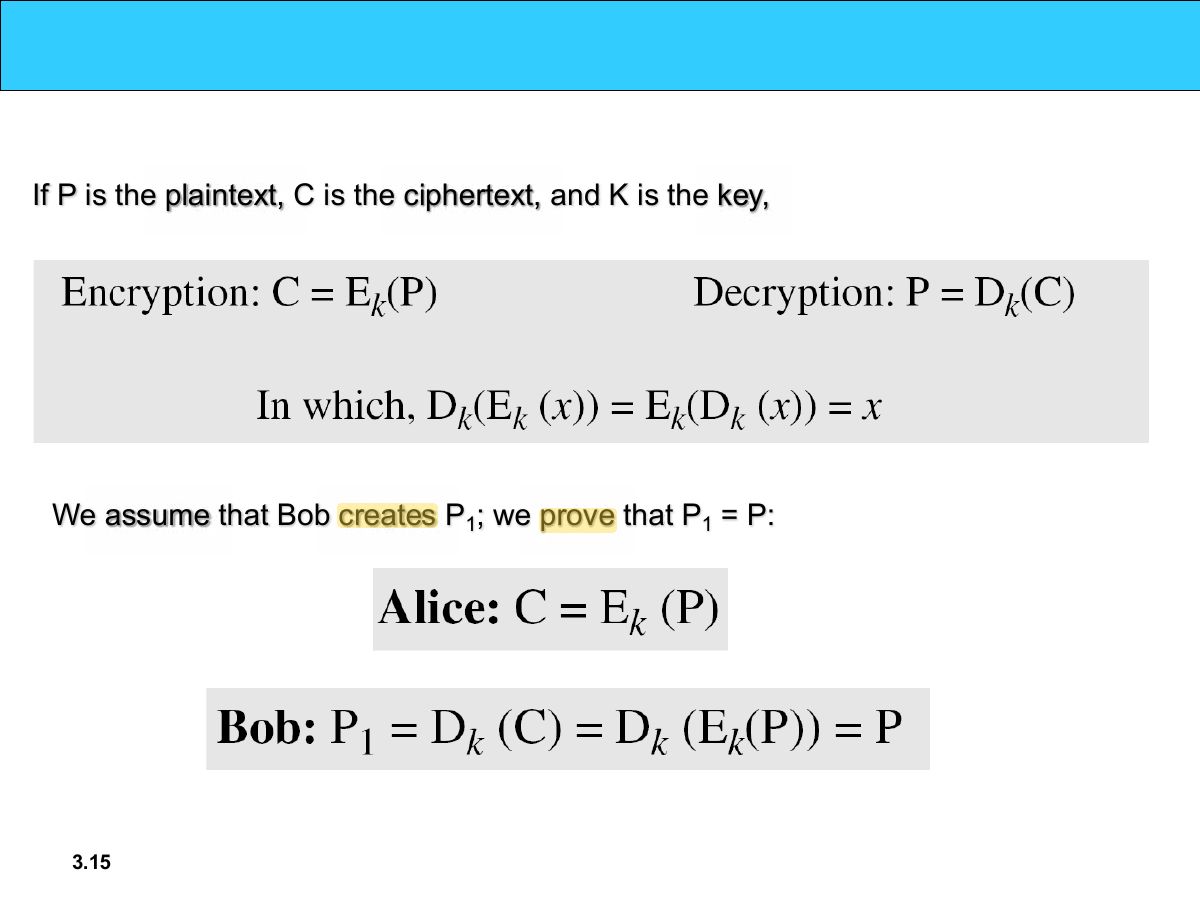
- Notation: C = E_K(P), P = D_K(C).
Exam weight
Medium
- Cryptography protects confidentiality and integrity, NOT availability.
🎯 How this can come up · 1 question
True / False
Cryptography can protect availability.
False. Confidentiality and integrity only.
Exam weight
High
- Kerckhoffs’s principle: a cryptosystem must stay secure even if everything except the KEY is public. Assume Eve knows the algorithm.
🎯 How this can come up · 1 question
MCQ
Kerckhoffs’s principle says the security of a cryptosystem should depend only on:
Correct: The secrecy of the key.
Exam weight Low
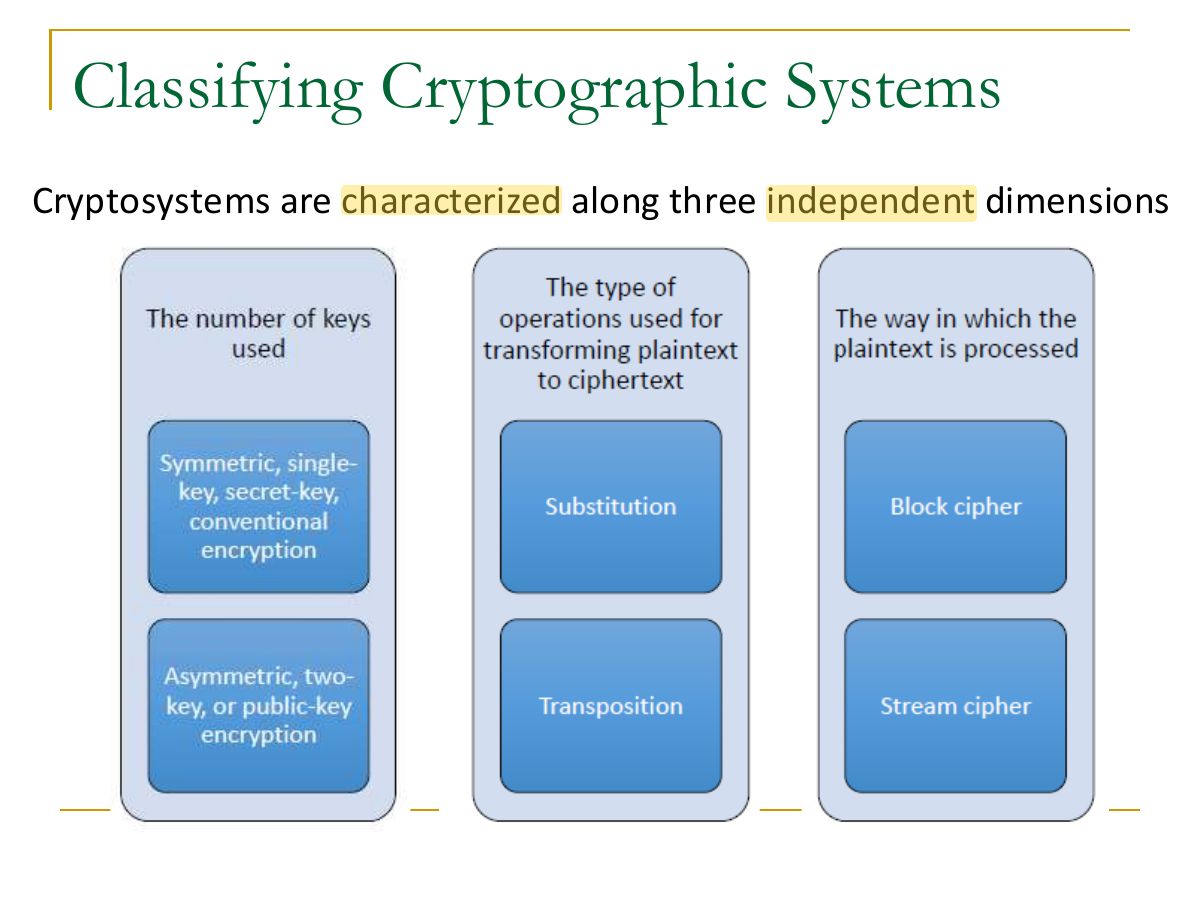
- Three dimensions: operations used (substitution, transposition), number of keys (symmetric, asymmetric), how plaintext is processed (block, stream).
Exam weight Low
- Same key for both = symmetric (conventional). Different keys = asymmetric (public-key).
Exam weight Low
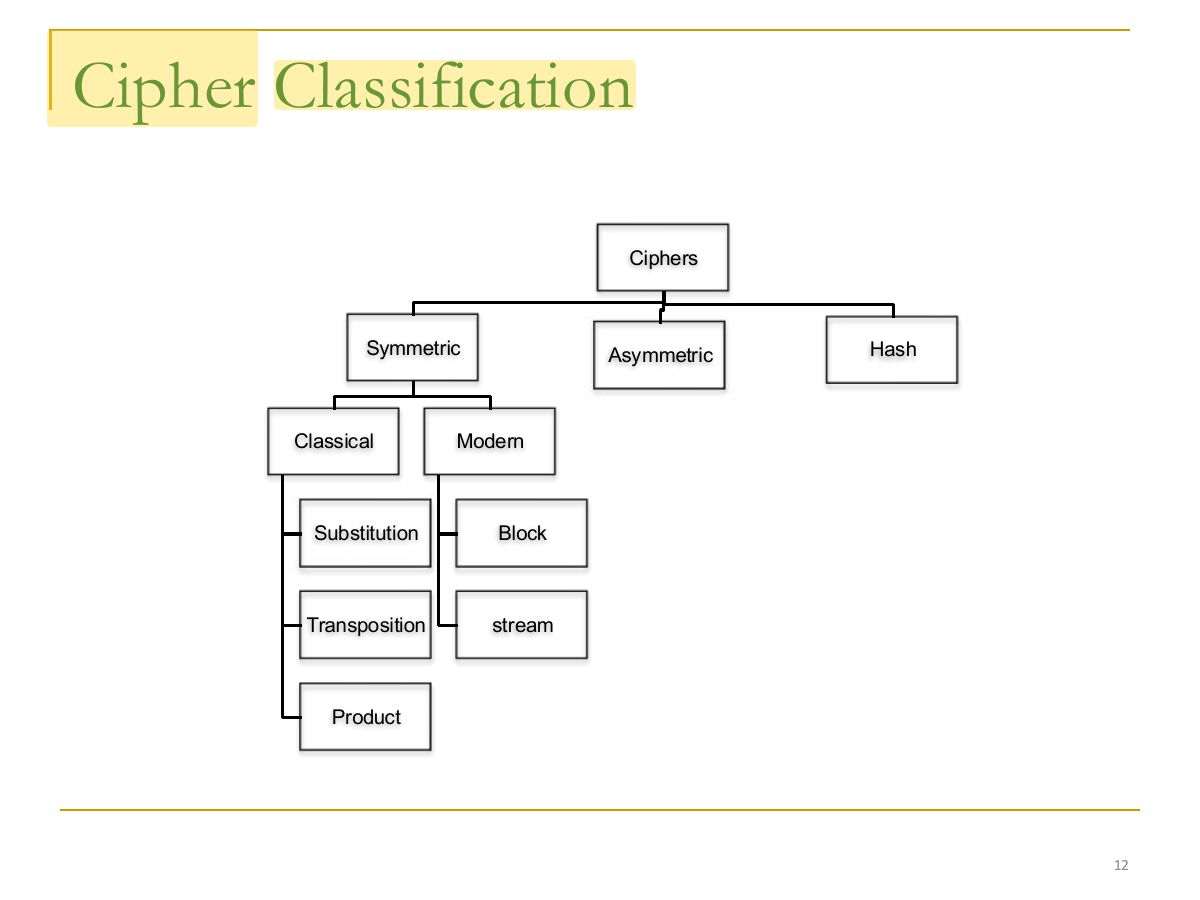
- Cipher classification tree.
Exam weight Low
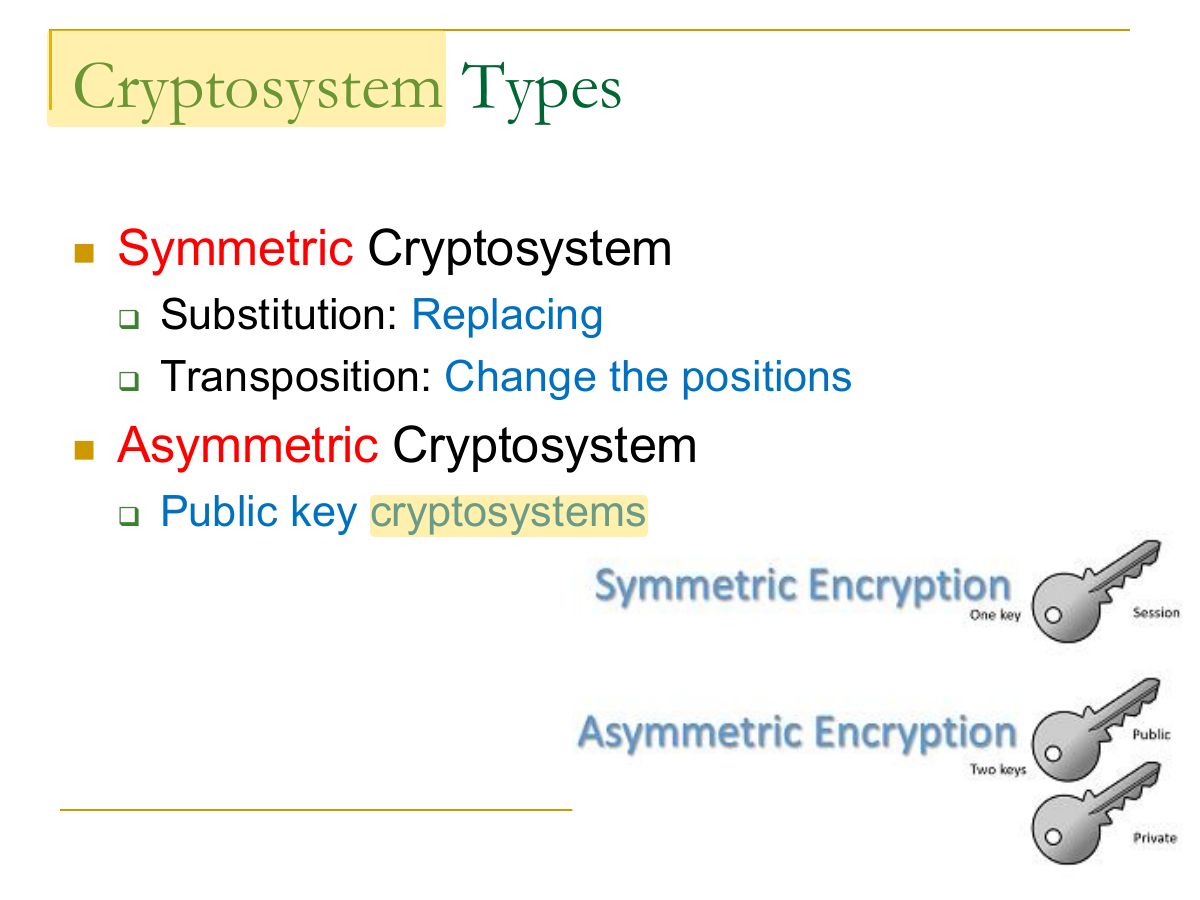
- Symmetric cryptosystems use substitution (replace) and transposition (rearrange).
Exam weight Low
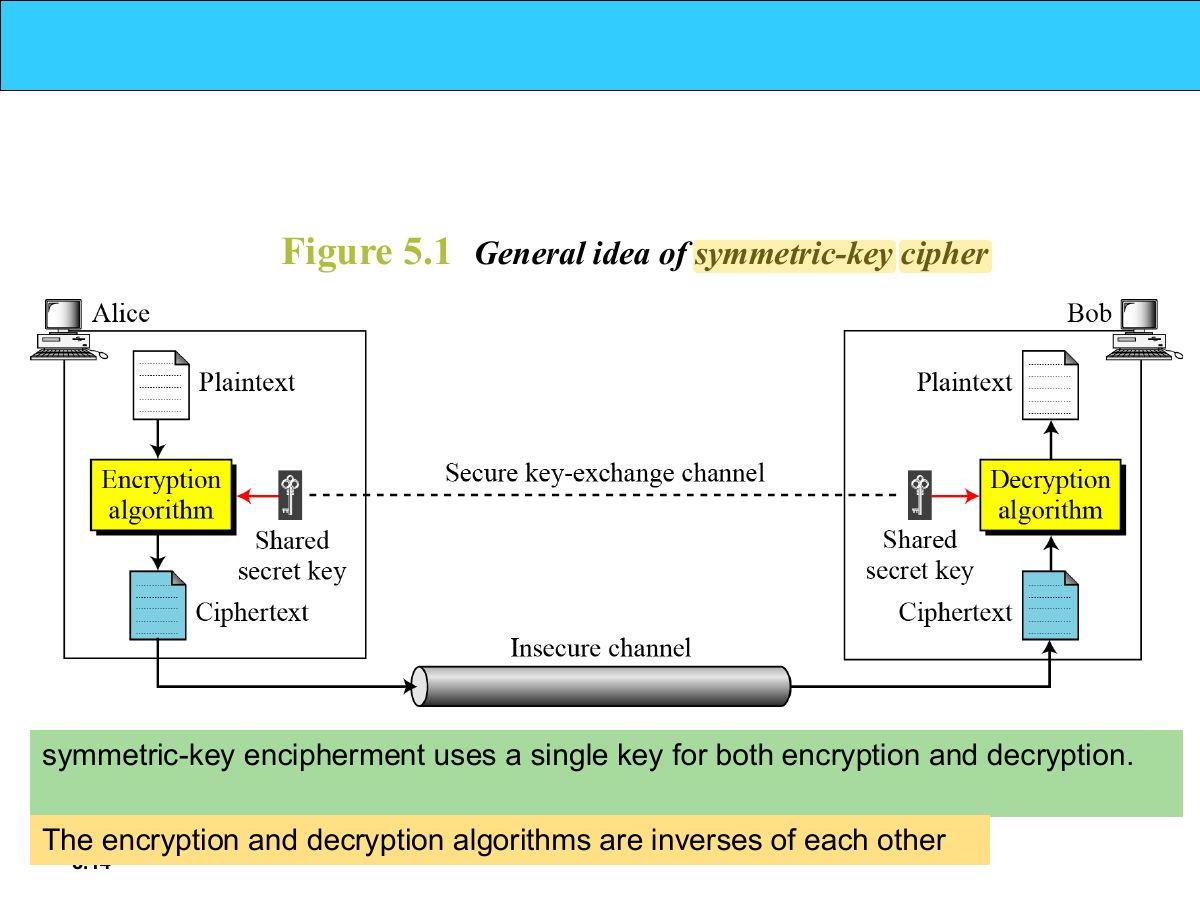
- Symmetric key: one shared key encrypts and decrypts.
Exam weight Low
- Proof that decryption recovers P.
Exam weight Low
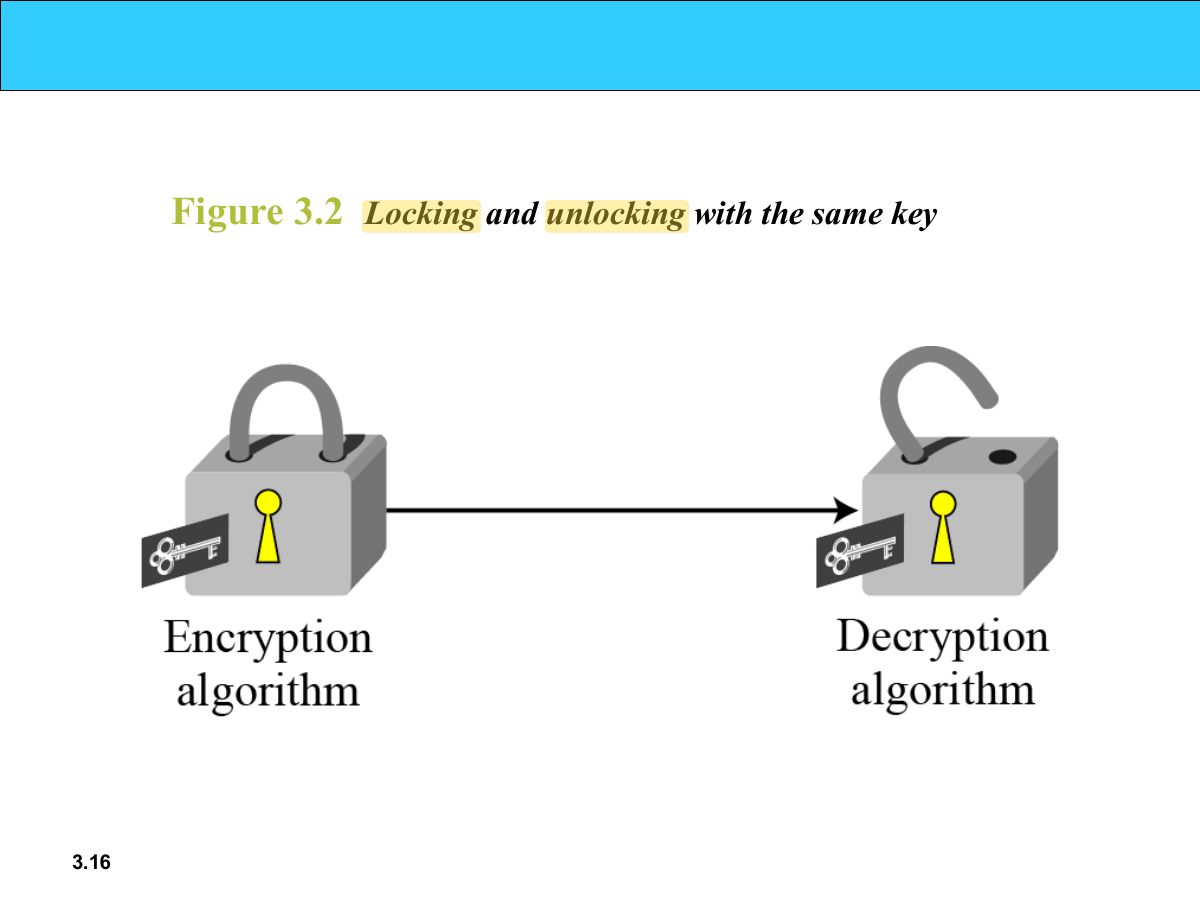
- Same key locks and unlocks.
Exam weight
High
- Symmetric needs: efficient E and D, and the ciphertext must be hard to invert without the key. Problem: secure key distribution.
Asked in a real exam
🎯 How this can come up · 2 questions
MCQ
The classic problem with symmetric encryption is:
Major 181.
Written
Why is symmetric encryption preferred for large amounts of data? (Major C)
It uses one shared key and simple, fast operations (substitution, permutation, XOR), so it is far faster and lighter than asymmetric algorithms, which do heavy maths on huge numbers. Asymmetric is used only to exchange the symmetric key or to sign (hybrid encryption).
★ Past exam
Exam weight
High
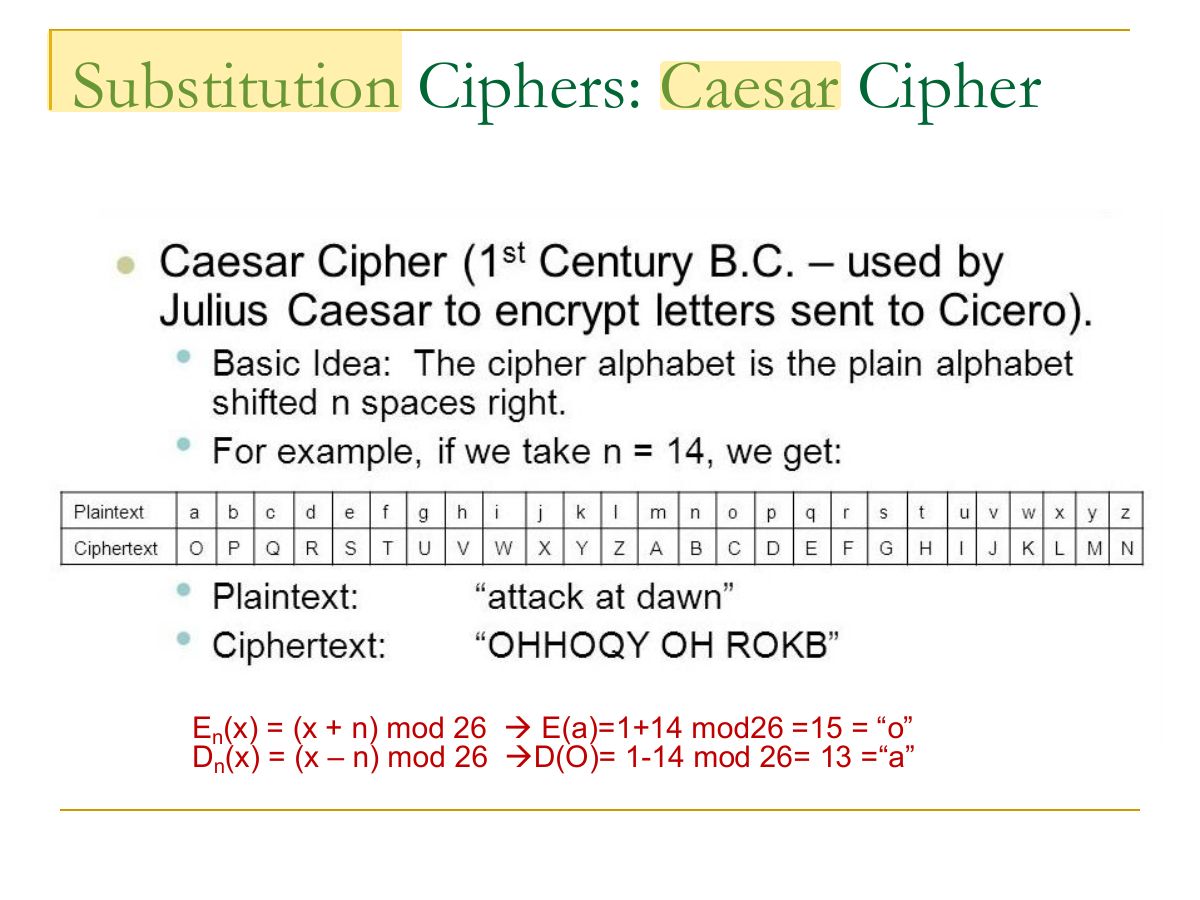
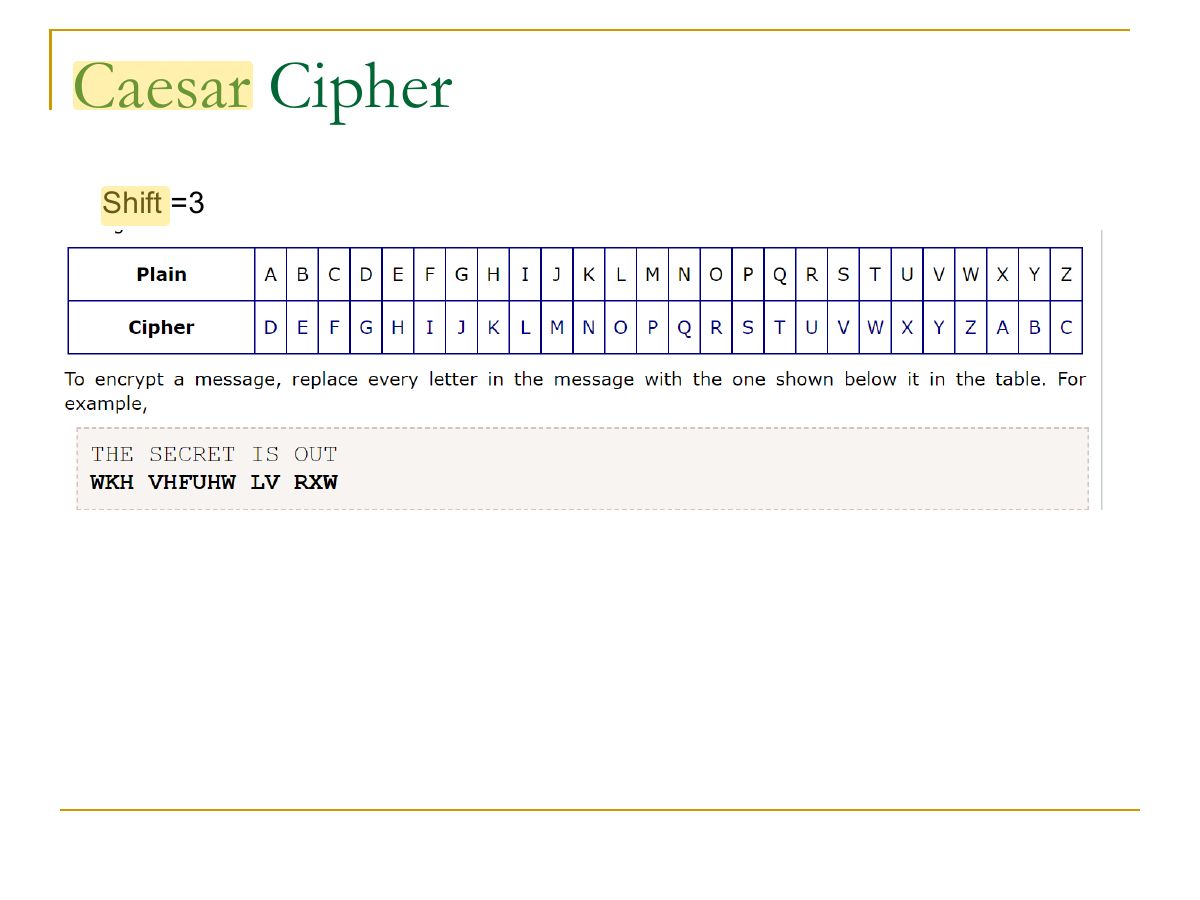
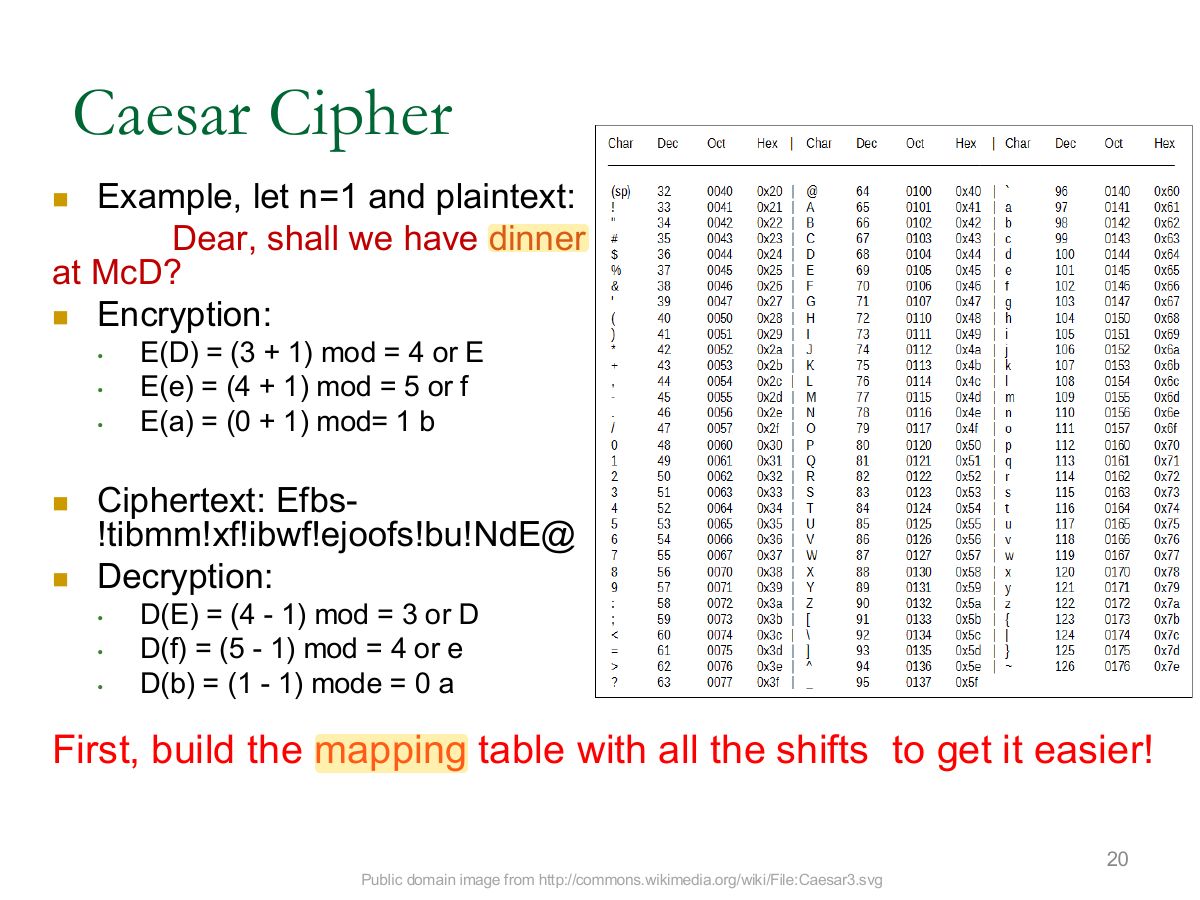
- Caesar: shift every letter by k: C = (P + k) mod 26.
TipHand-cipher rules: CAESAR C = (P + k) mod 26 ·
VIGENÈRE add the repeated key letter (subtract to decrypt) ·
PLAYFAIR pairs: same row → right, same column → below, rectangle
→ own row, other letter’s column; X between doubles · HILL row
vector × K mod 26, decrypt with K⁻¹ (det must be coprime with
26) · TRANSPOSITION write in rows, read columns in key order.
Asked in a real exam
🎯 How this can come up · 2 questions
MCQ
Plaintext GLOBAL… becomes QVYLKV…. What is the Caesar key?
Major A: G(6) → Q(16).
MCQ
Caesar with shift 3 encrypts HELLO as:
Correct: KHOOR.
Exam weight Low
- Shift 3 example.
Exam weight Low
- Shift 1 example.
Exam weight Low
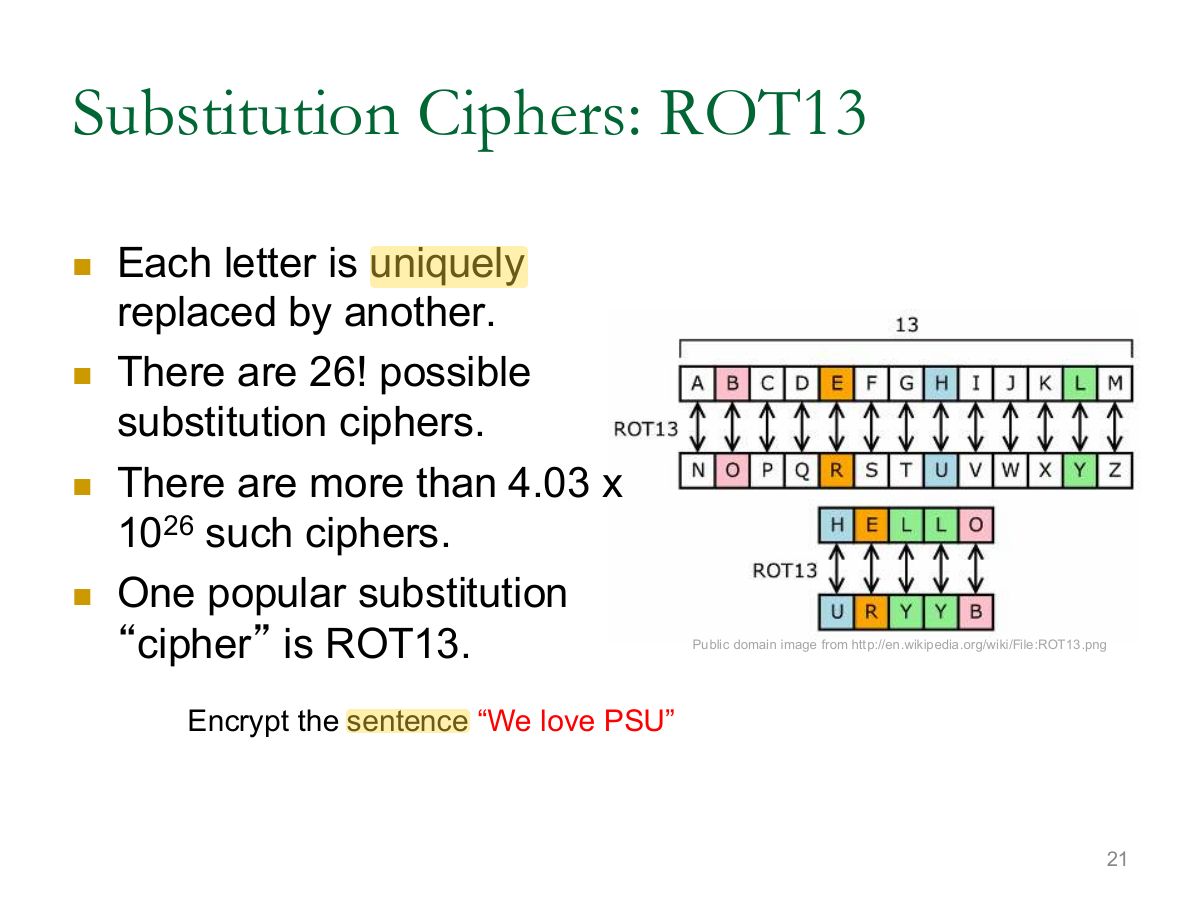
- ROT13; a general substitution cipher has 26! keys.
Exam weight Low
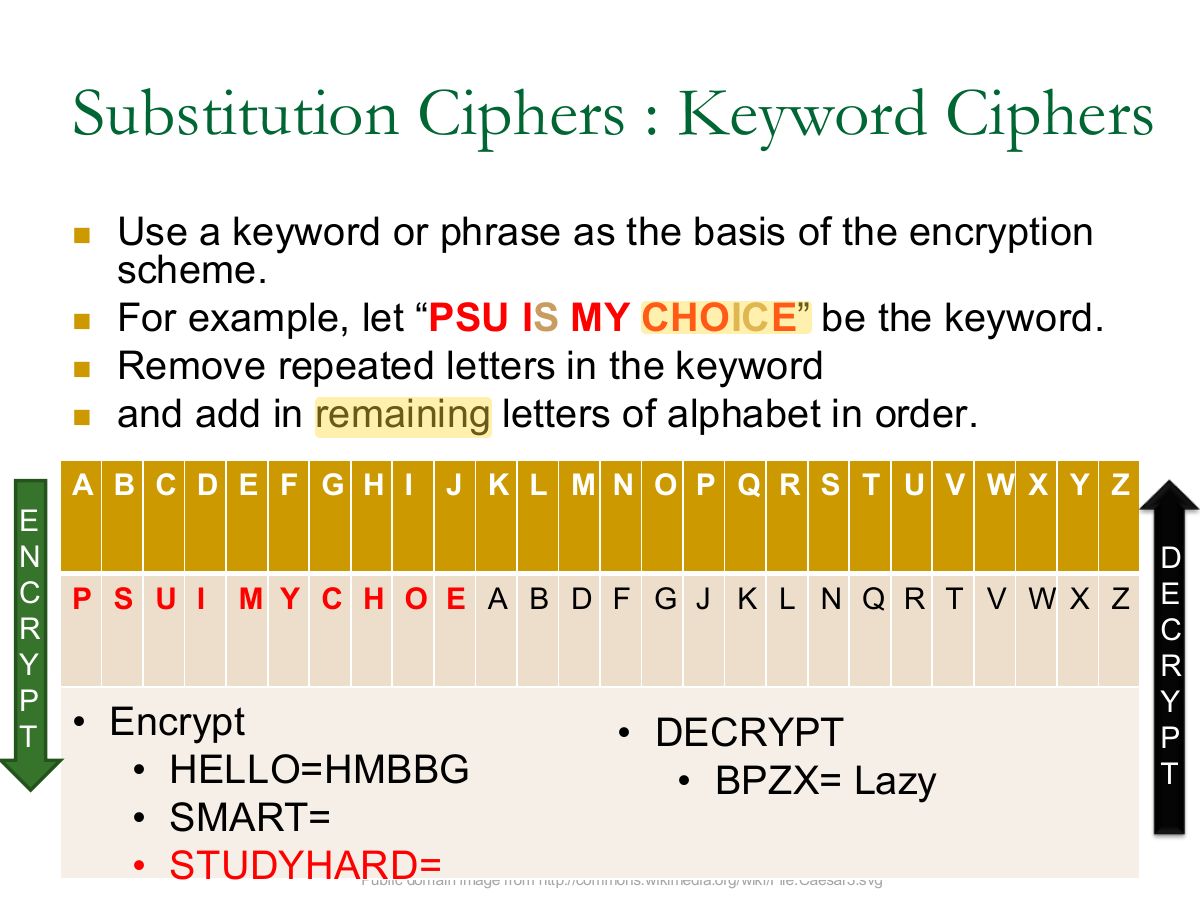
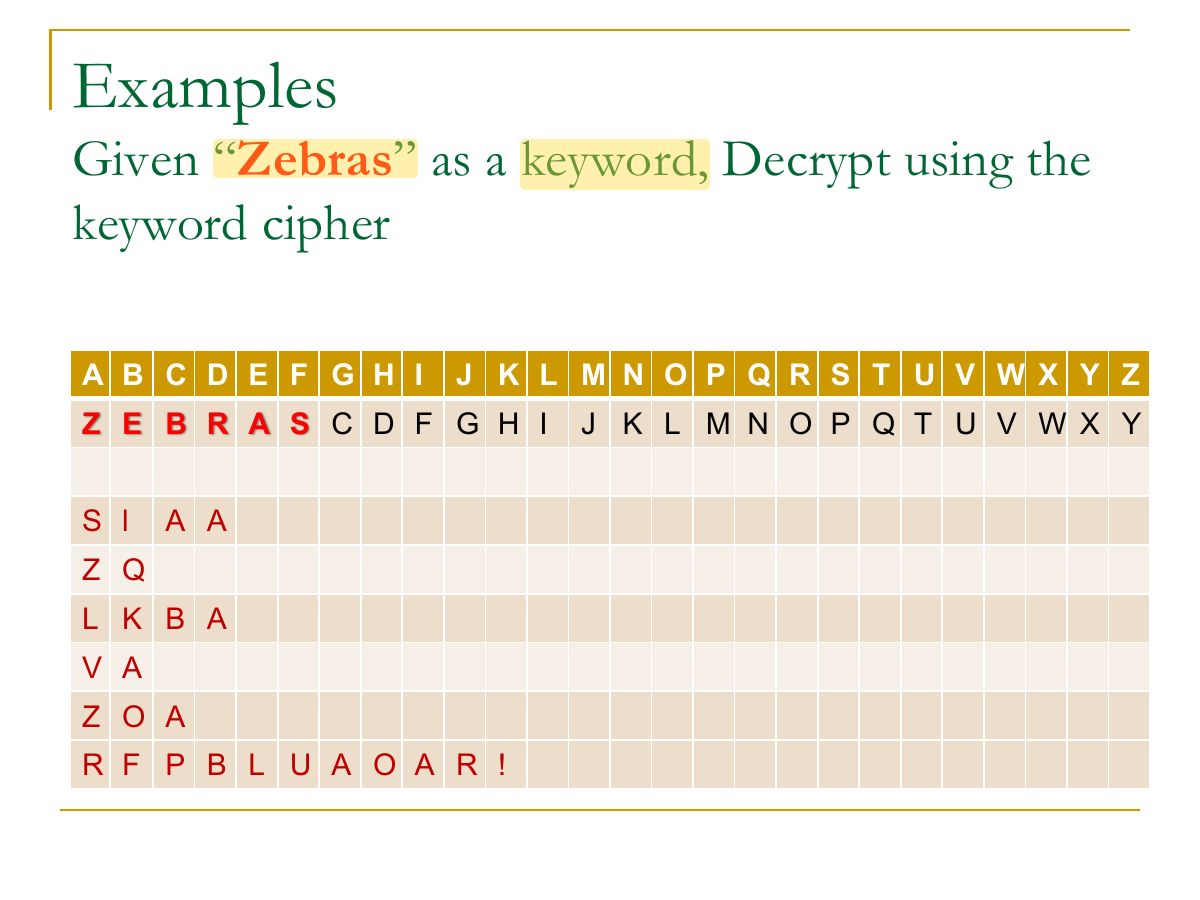
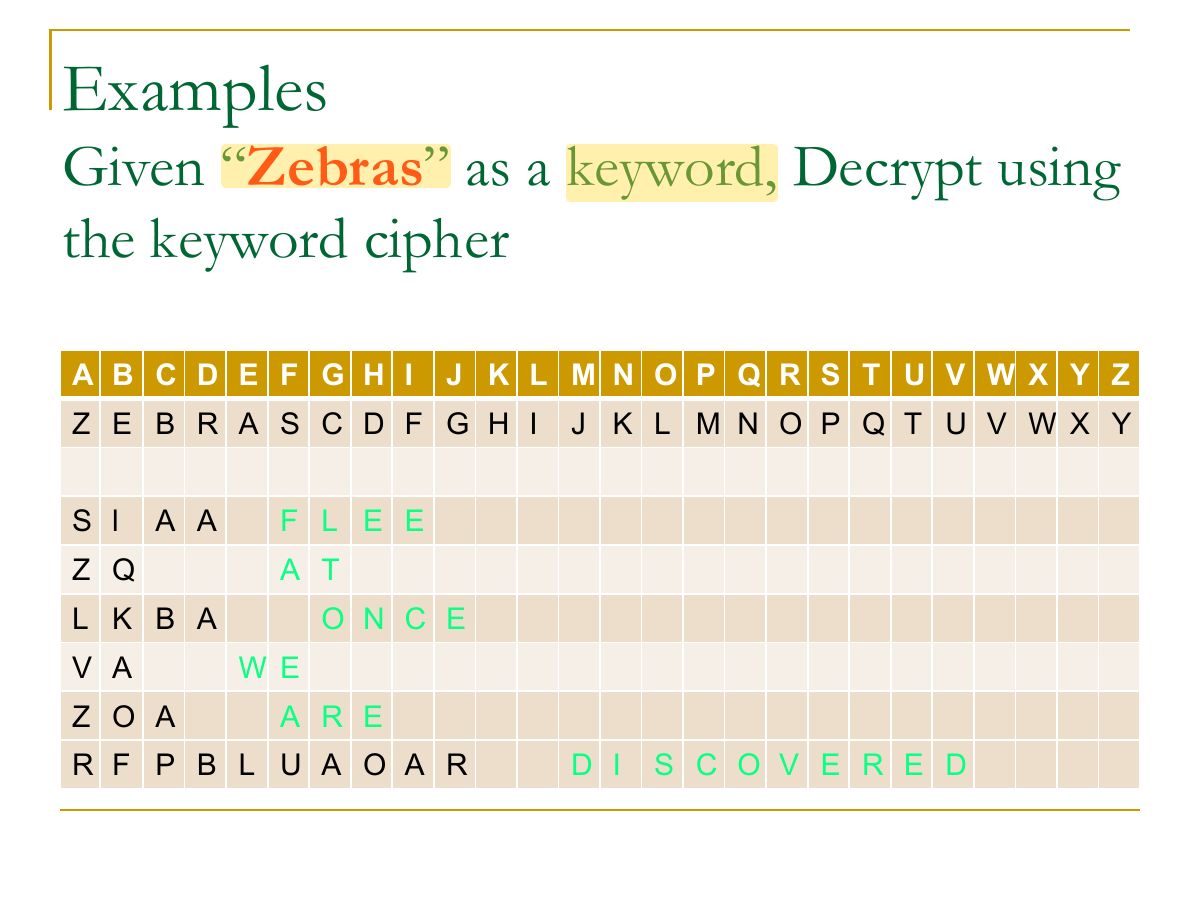
- Keyword cipher: write the keyword (no repeats) then the rest of the alphabet as the cipher alphabet.
Exam weight Low
- Keyword example (“zebras”).
Exam weight Low
- Keyword example, continued.
Exam weight Low
- Monoalphabetic ciphers fall to frequency analysis → encrypt pairs of letters (Playfair).
Exam weight Low
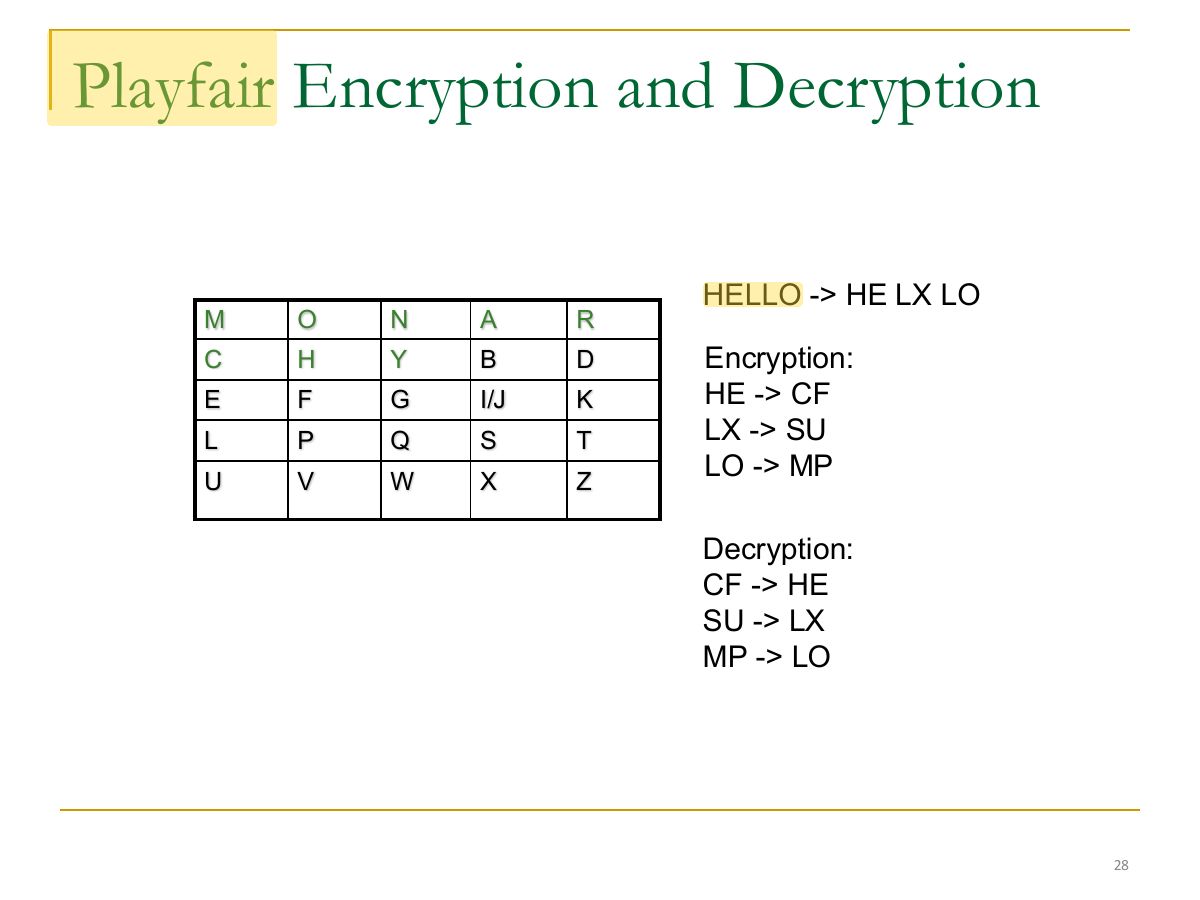
- Playfair 5×5 matrix: keyword letters (no repeats), then the remaining letters; I/J share a cell.
Exam weight
High
- Rules: pairs; X between doubled letters; same row → right; same column → below; rectangle → own row, other letter’s column.
TipHand-cipher rules: CAESAR C = (P + k) mod 26 ·
VIGENÈRE add the repeated key letter (subtract to decrypt) ·
PLAYFAIR pairs: same row → right, same column → below, rectangle
→ own row, other letter’s column; X between doubles · HILL row
vector × K mod 26, decrypt with K⁻¹ (det must be coprime with
26) · TRANSPOSITION write in rows, read columns in key order.
Asked in a real exam
🎯 How this can come up · 2 questions
Written
Encrypt COMMITTEES with Playfair, keyword EFFECTIVENESS (I/J together). (Major B)
Matrix rows: E F C T I / V N S A B / D G H K L / M O P Q R / U W X Y Z. Pairs: CO MX MI TX TE ES → FP PU RE CY IF CV.
MCQ
In Playfair, two letters in the same row are replaced by:
Correct: The letters to their right.
Exam weight Low
- HELLO → HE LX LO.
Exam weight
Medium
- 26 × 26 = 676 digrams: much better than monoalphabetic, but still breakable with digram frequencies.
🎯 How this can come up · 1 question
Written
In Playfair, what does cryptanalysis depend on? (Major C)
Recovering the 5×5 key square built from the keyword, usually through digram frequency analysis.
★ Past exam
Exam weight
High
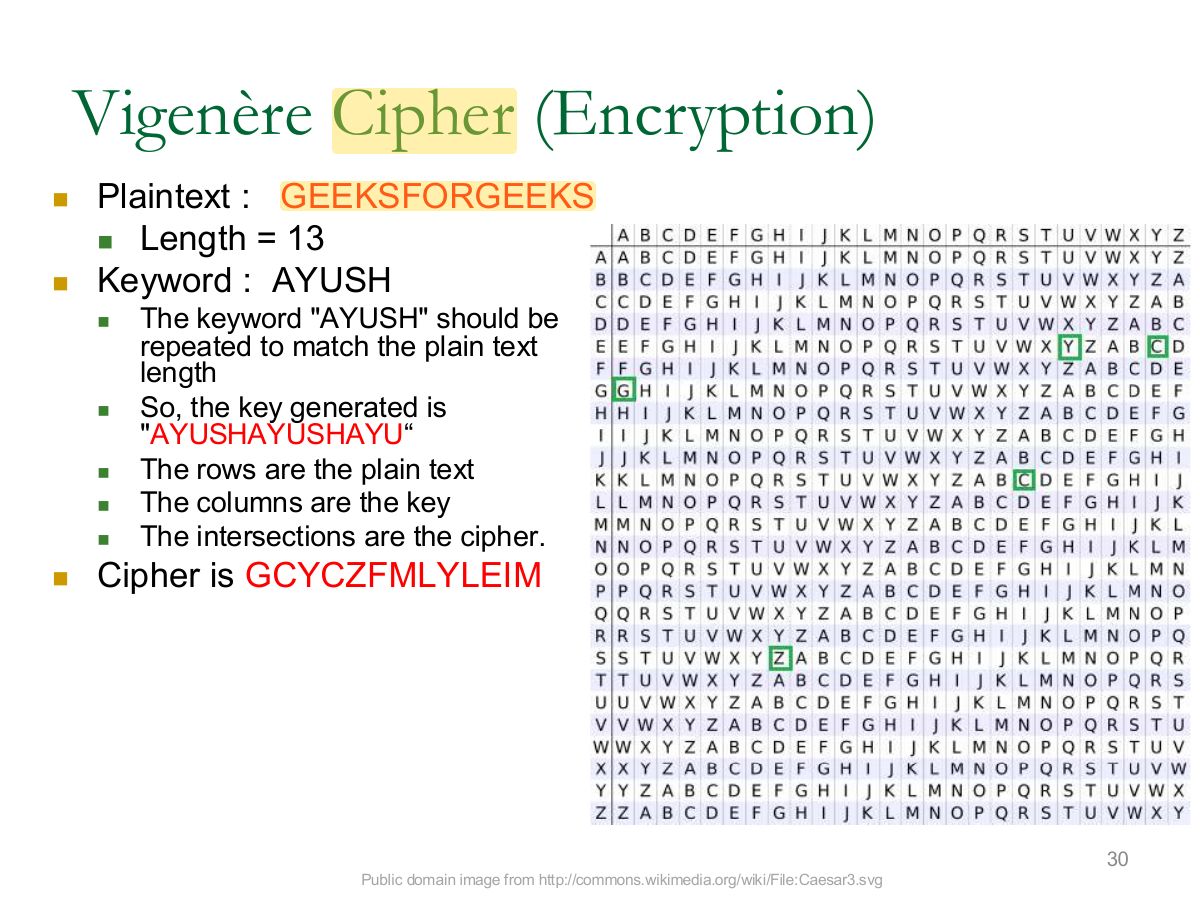
- Vigenère: repeat the key; C = (P + K) mod 26.
Asked in a real exam
🎯 How this can come up · 2 questions
MCQ
An advanced Caesar cipher that shifts each letter by a keyword letter is:
Final 221 A.
Written
Decrypt CMRUVLERMYOLRX with Vigenère key RIYADH. (Major B)
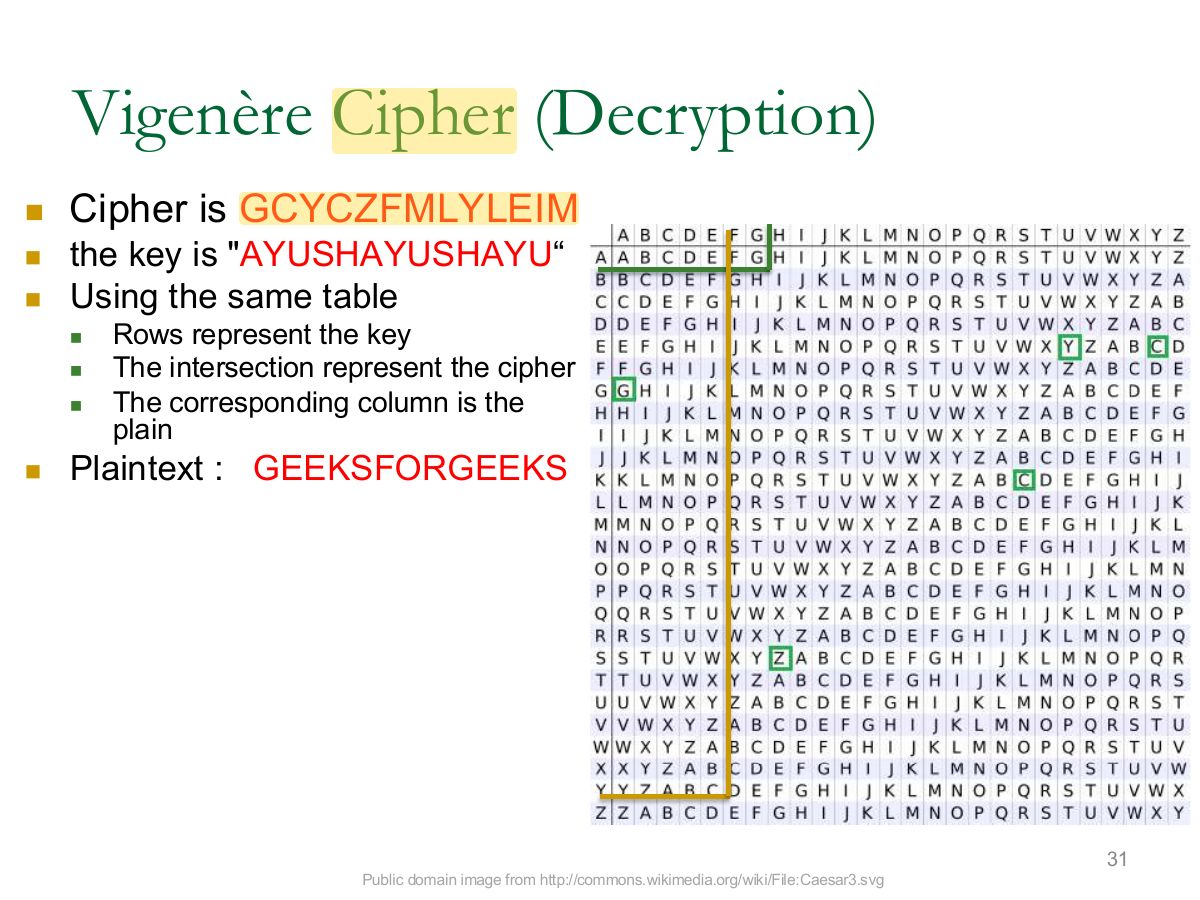
Subtract the repeated key RIYADHRIYADHRI letter by letter: LETUSENJOYLEAP (“let us enjoy LEAP”).
Exam weight Low
- Vigenère decryption: subtract the key letter.
Exam weight Low
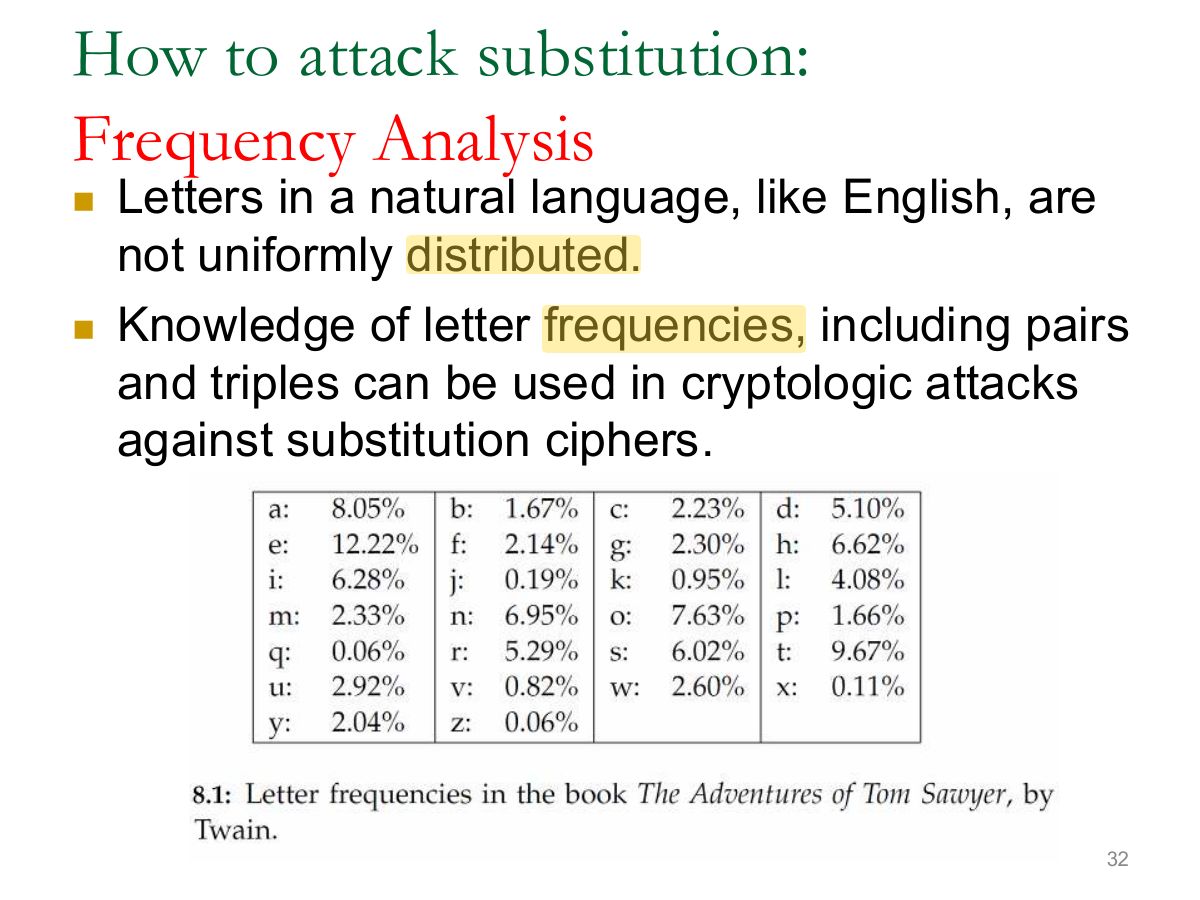
- Frequency analysis breaks substitution ciphers (E, T, A are most common in English).
Exam weight
High
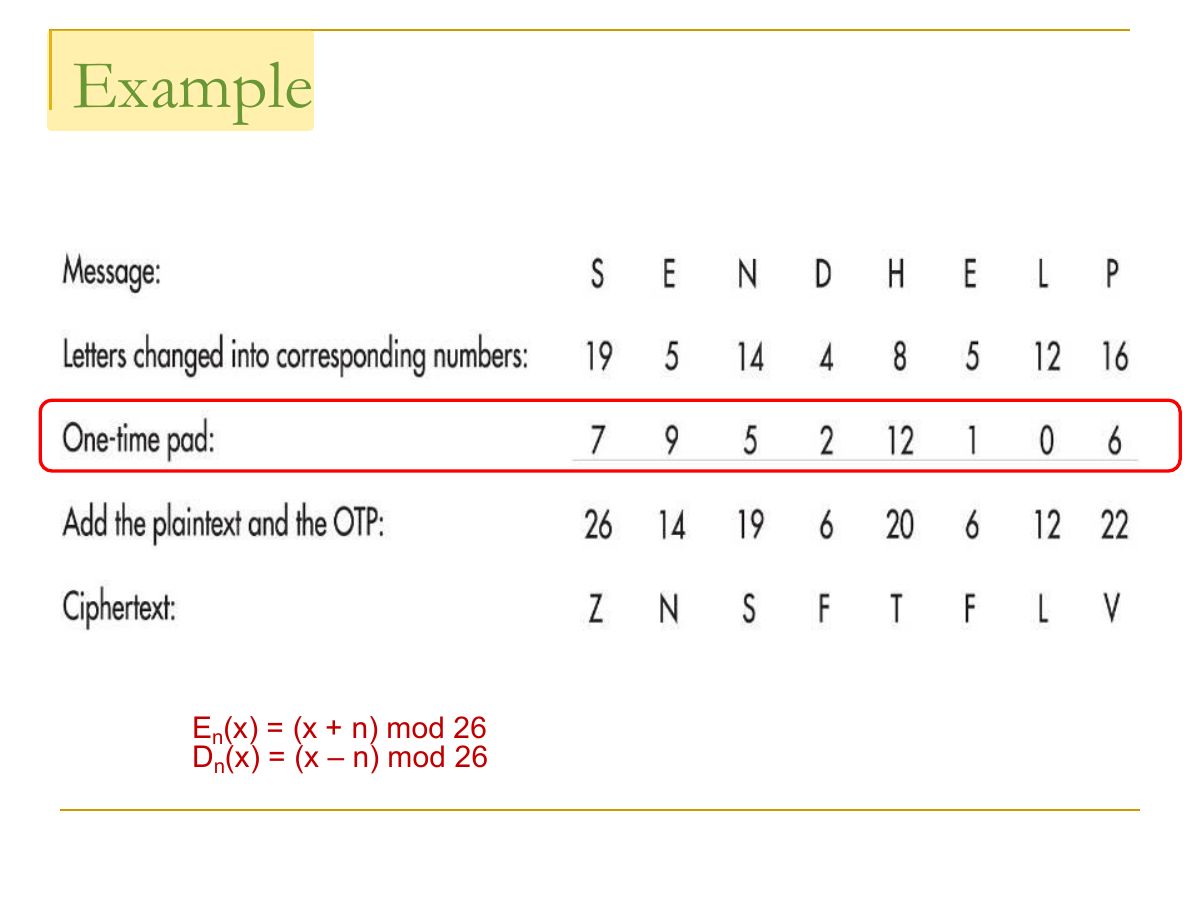
- One-time pad (Vernam/Mauborgne 1917): a truly random key as long as the message, used once → unbreakable.
🎯 How this can come up · 1 question
MCQ
Which cipher is theoretically unbreakable?
Correct: One-time pad.
Exam weight Low
- One-time pad example.
Exam weight
High
- Hill (1929): m letters at a time as a vector, multiplied by an m × m key matrix mod 26.
Asked in a real exam
🎯 How this can come up · 2 questions
Written
Encrypt HE with a Hill key K = [[3, 3], [2, 5]] using the row approach. (Major A)
HE = (7, 4). (7, 4) × K = (7·3 + 4·2, 7·3 + 4·5) = (29, 41) mod 26 = (3, 15) → DP.
True / False
Any 2 × 2 matrix can be used as a Hill cipher key.
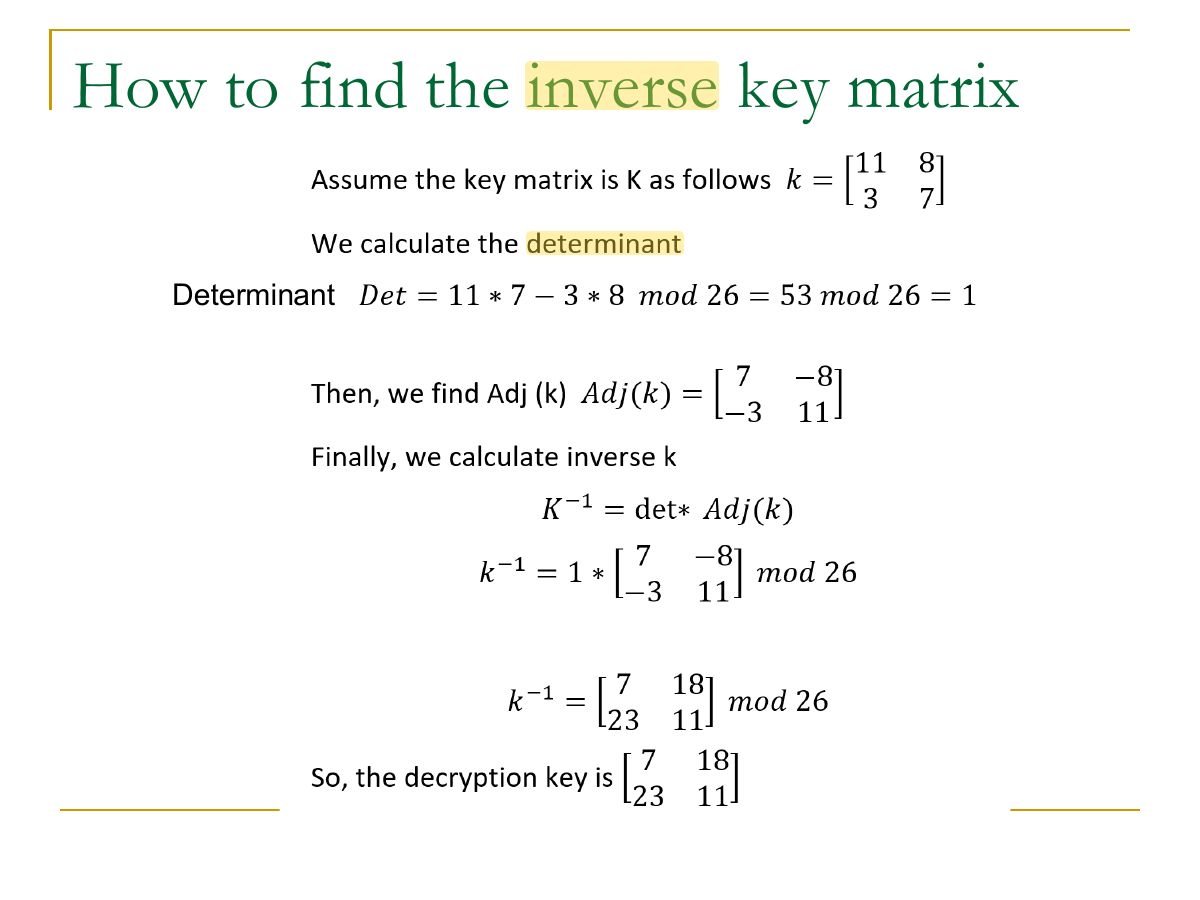
False. Its determinant must have an inverse mod 26 (coprime with 26).
Exam weight Low
- Hill example.
Exam weight Low
- Letter numbering A = 0 … Z = 25.
Exam weight Low
- Hill matrix multiplication.
Exam weight Low
- Inverse key: K⁻¹ = det⁻¹ × adj(K) mod 26.
Exam weight
High
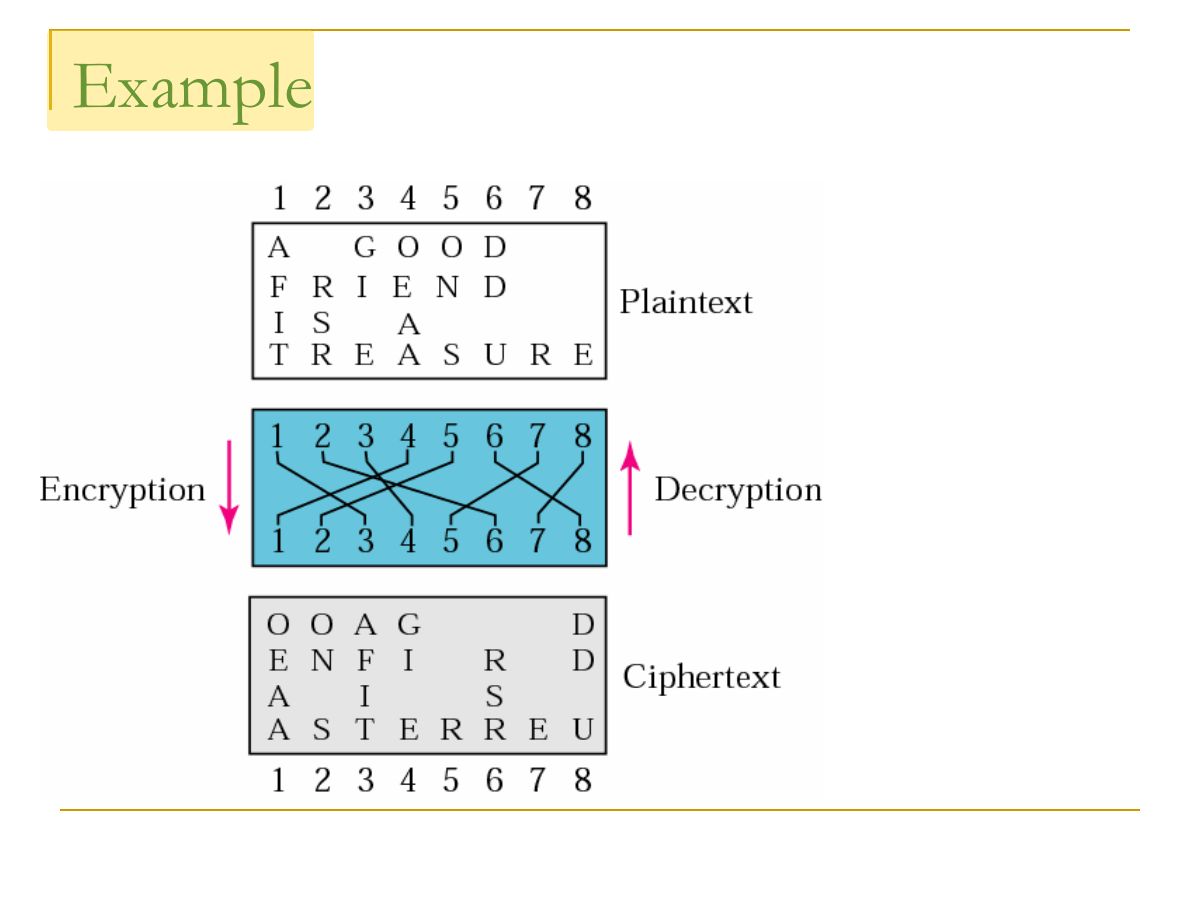
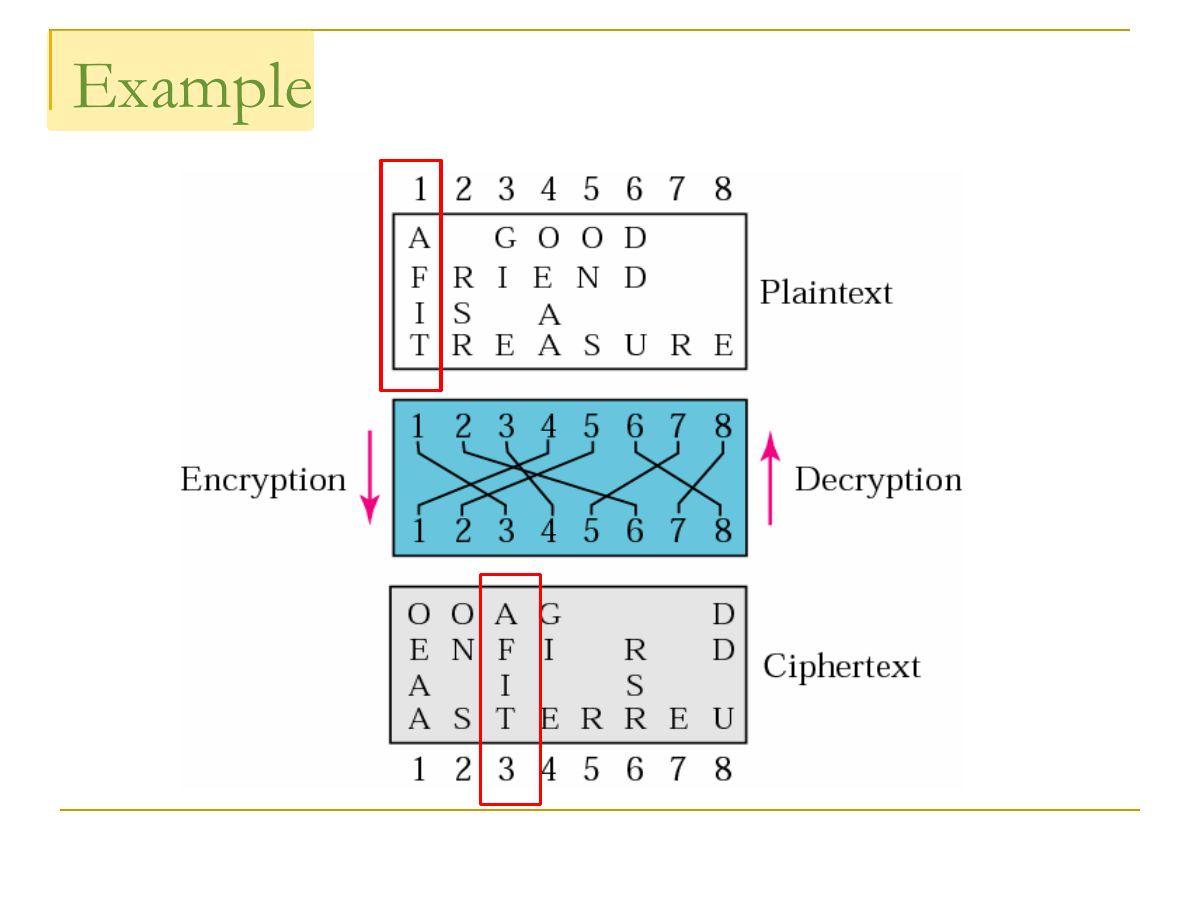
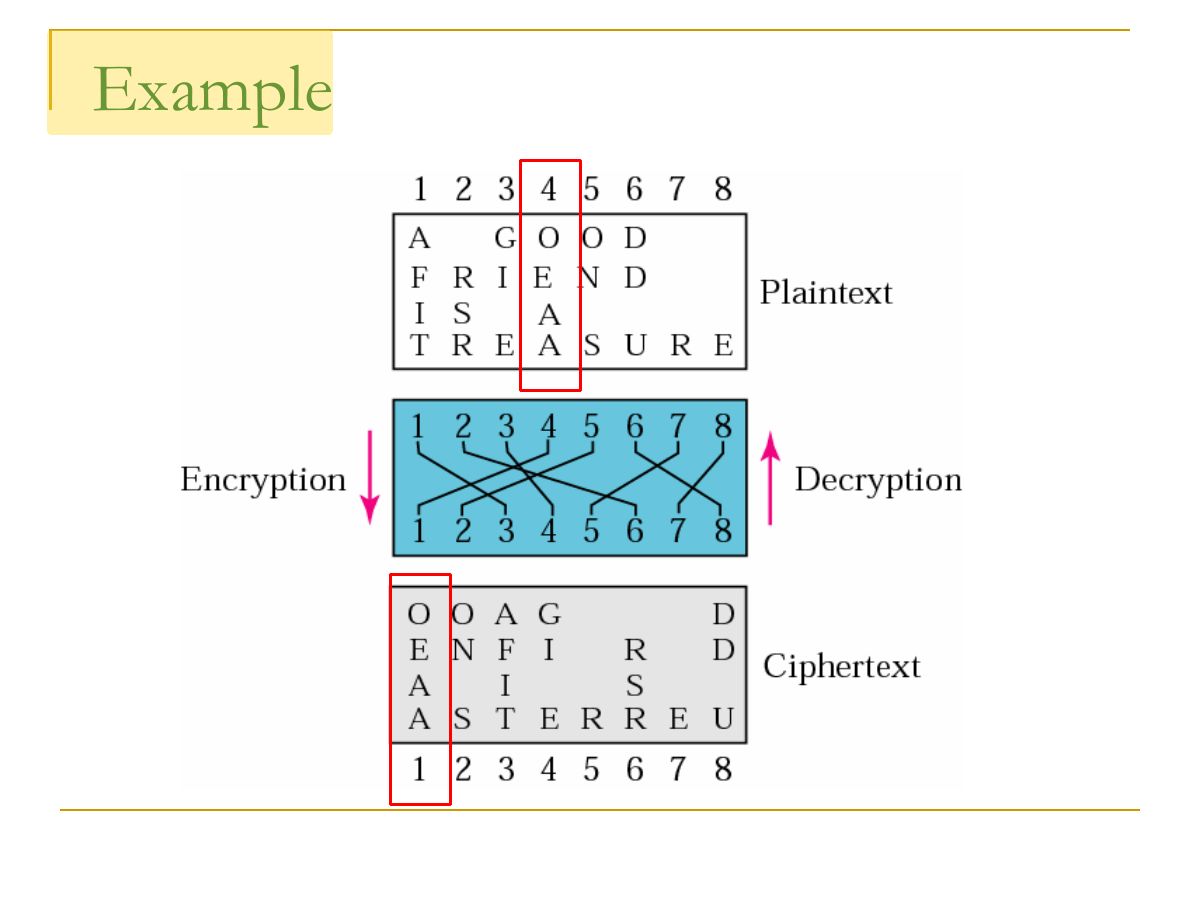
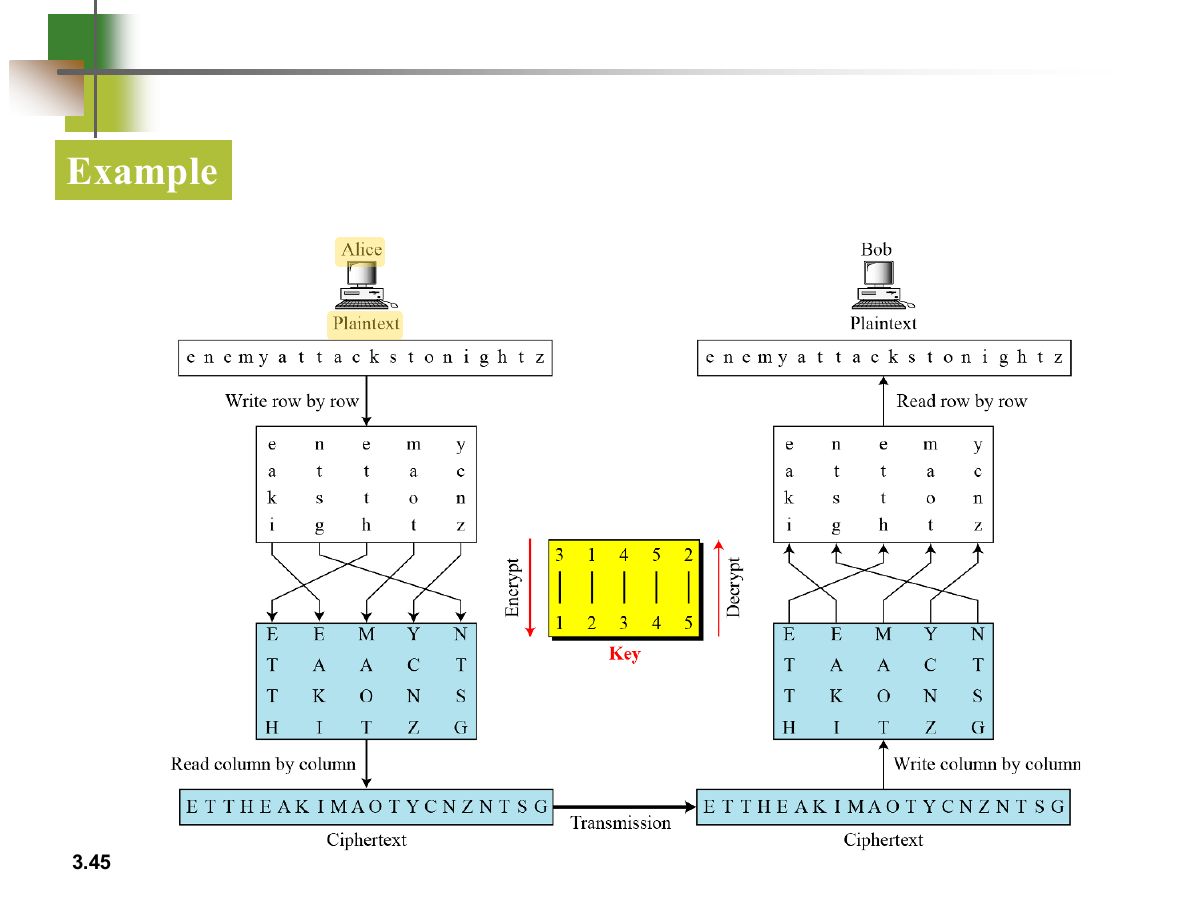
- Transposition keeps the letters but changes their positions: write in rows, permute/read columns by the key.
Asked in a real exam
🎯 How this can come up · 1 question
MCQ
A cipher that keeps the letters but rearranges their positions is a:
Correct: Transposition cipher.
Exam weight Low
- Transposition example.
Exam weight Low
- Example.
Exam weight Low
- Example.
Exam weight Low
- Example.
Exam weight Low
- Modern ciphers overview.
Exam weight Low
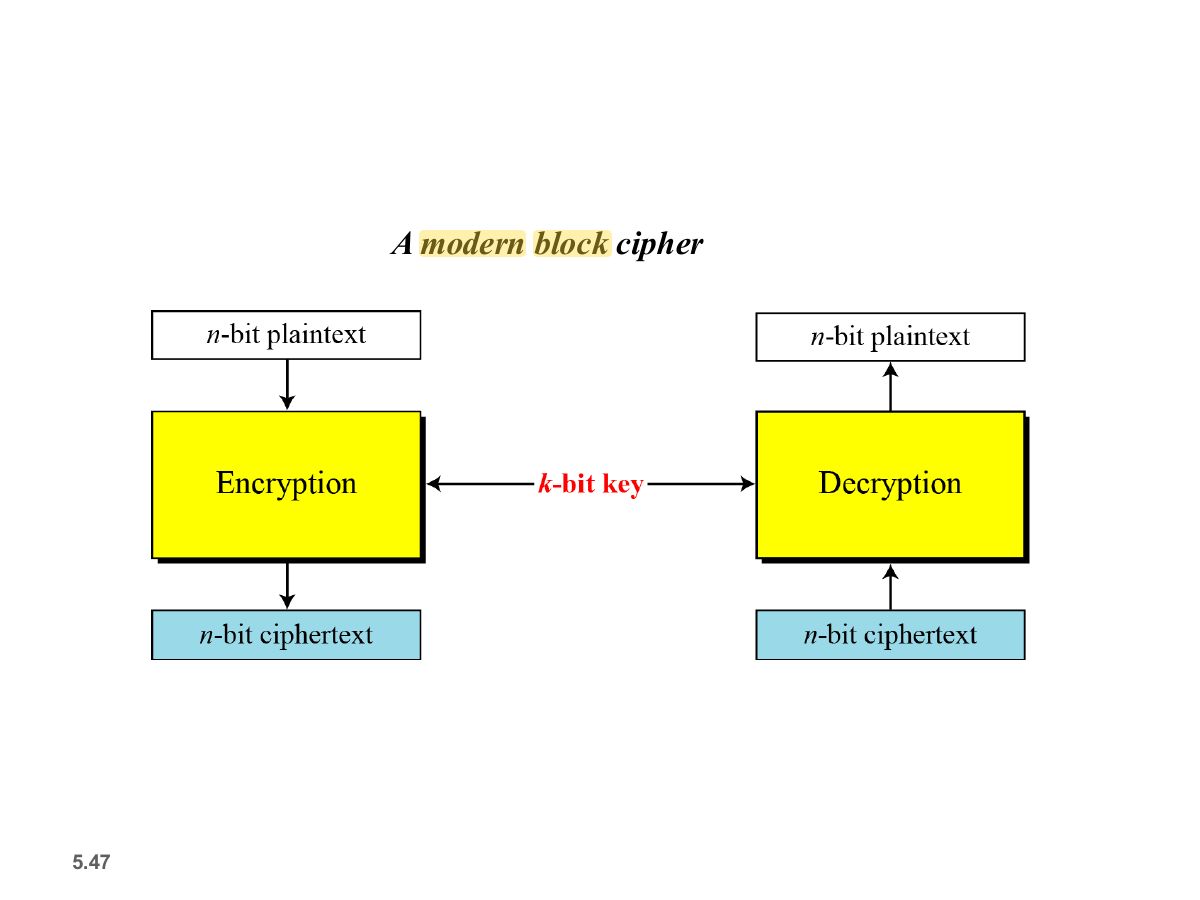
- A modern block cipher.
Exam weight Low
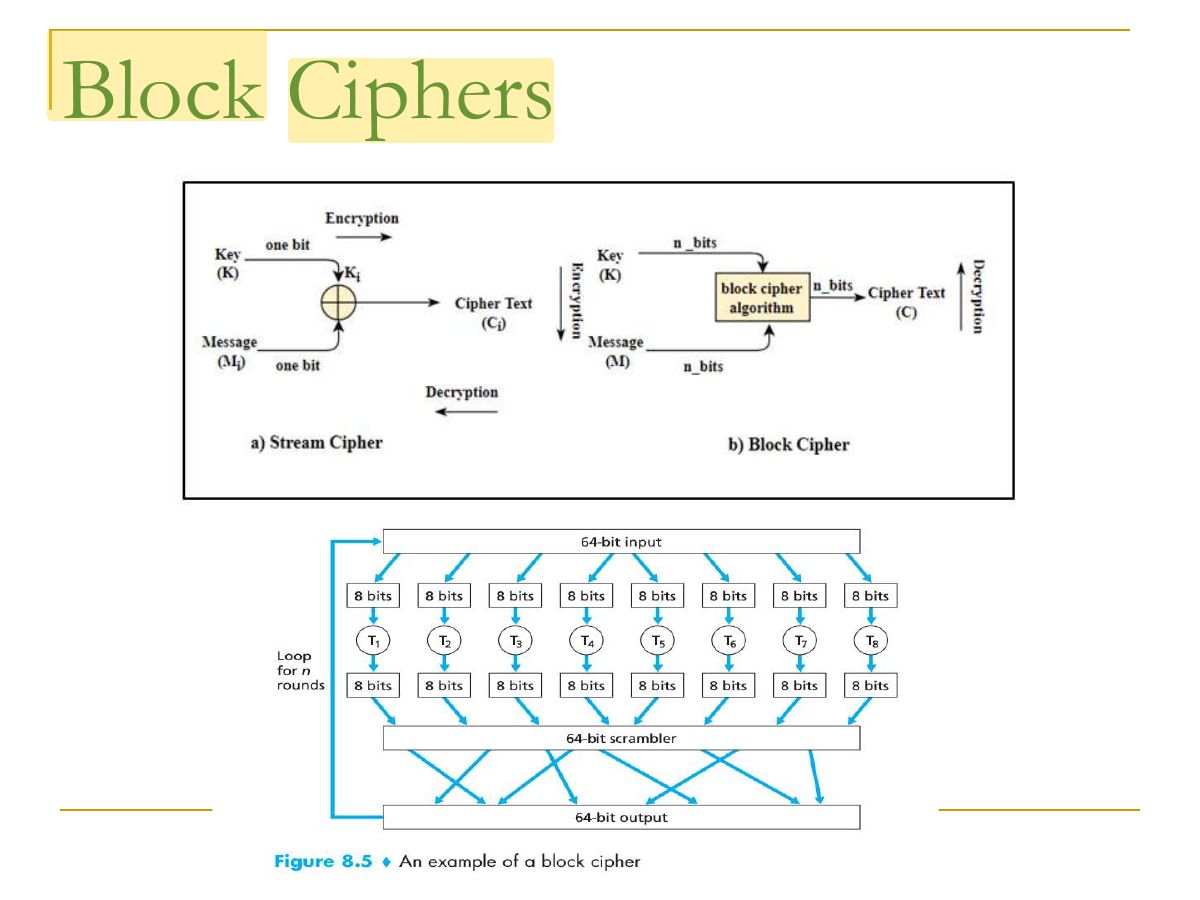
- Block ciphers.
Exam weight Low
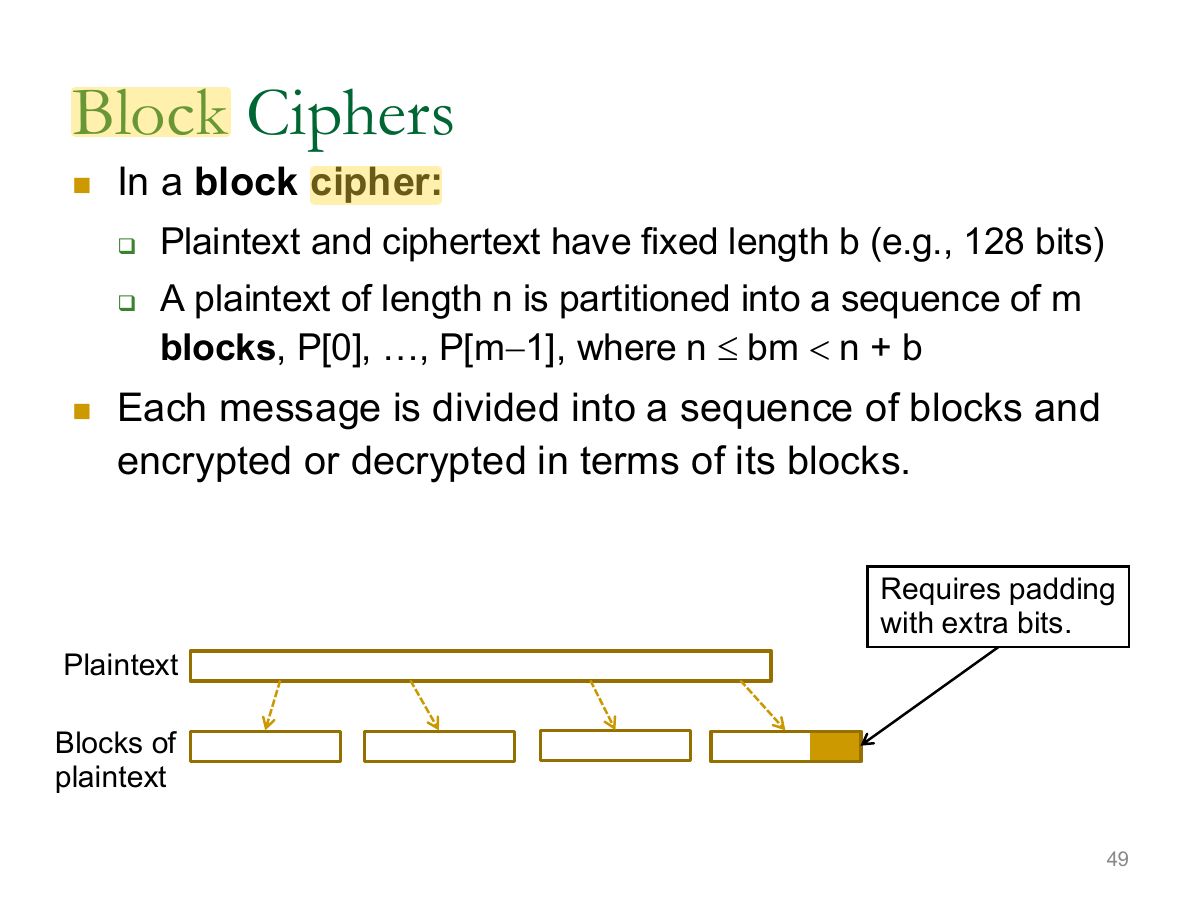
- Block cipher: fixed-length blocks of b bits (e.g., 128).
Exam weight Low
- Plaintext length must be a multiple of b → pad the last block unambiguously.
Exam weight
High
- Count characters as bytes; blocks = ceil(bytes / (b/8)); padding = blocks × (b/8) − bytes.
Asked in a real exam
🎯 How this can come up · 2 questions
Written
b = 128 bits. Plaintext “Incomprehensibilities”. How many blocks and how many padded bits? (Major A)
21 characters = 21 bytes. A block holds 16 bytes → 2 blocks (32 bytes). Padding = 32 − 21 = 11 bytes = 88 bits.
MCQ
b = 64 bits, plaintext of 29 bytes. How many blocks?
Major B: 8 bytes per block → 4 blocks, 3 bytes (24 bits) of padding.
Exam weight Low
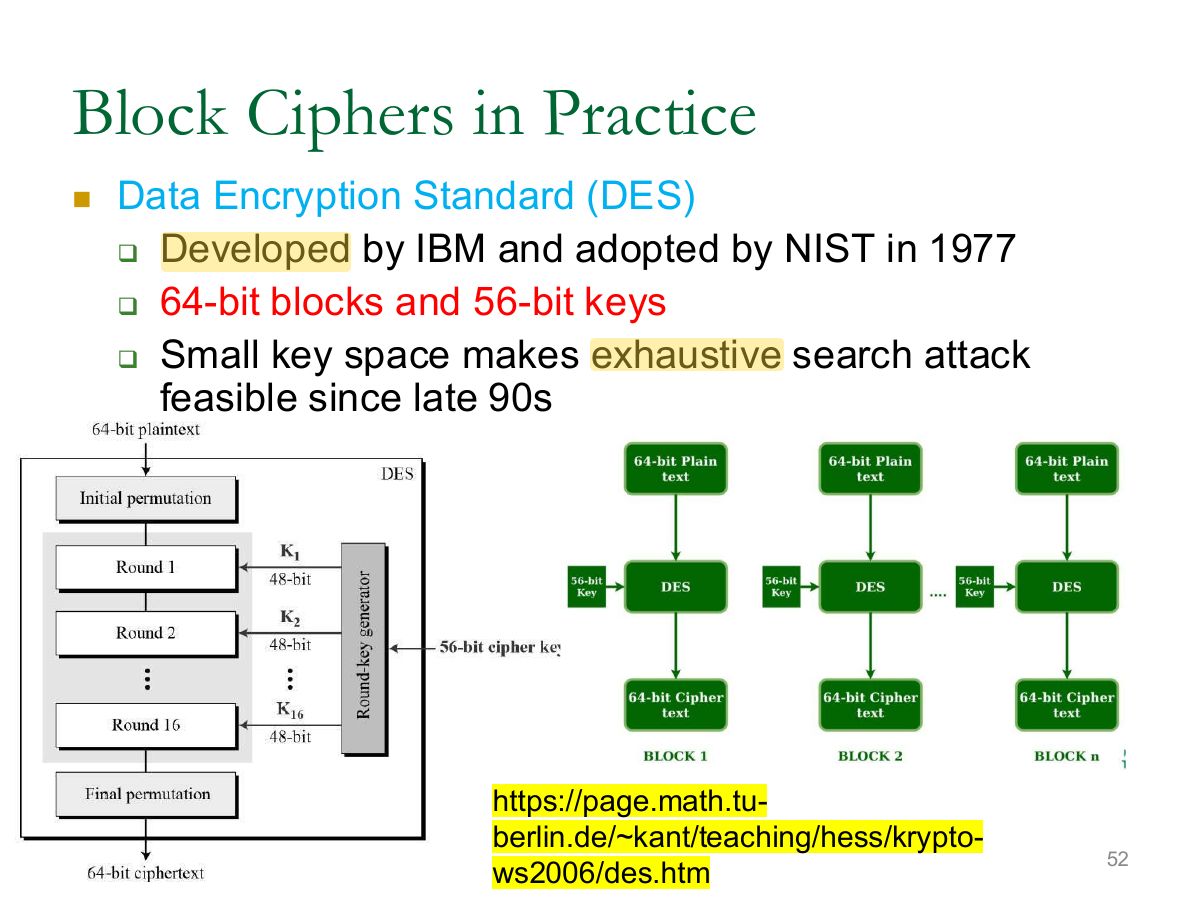
- DES: IBM, adopted 1977, 56-bit key, 64-bit blocks; now broken by brute force.
Exam weight Low
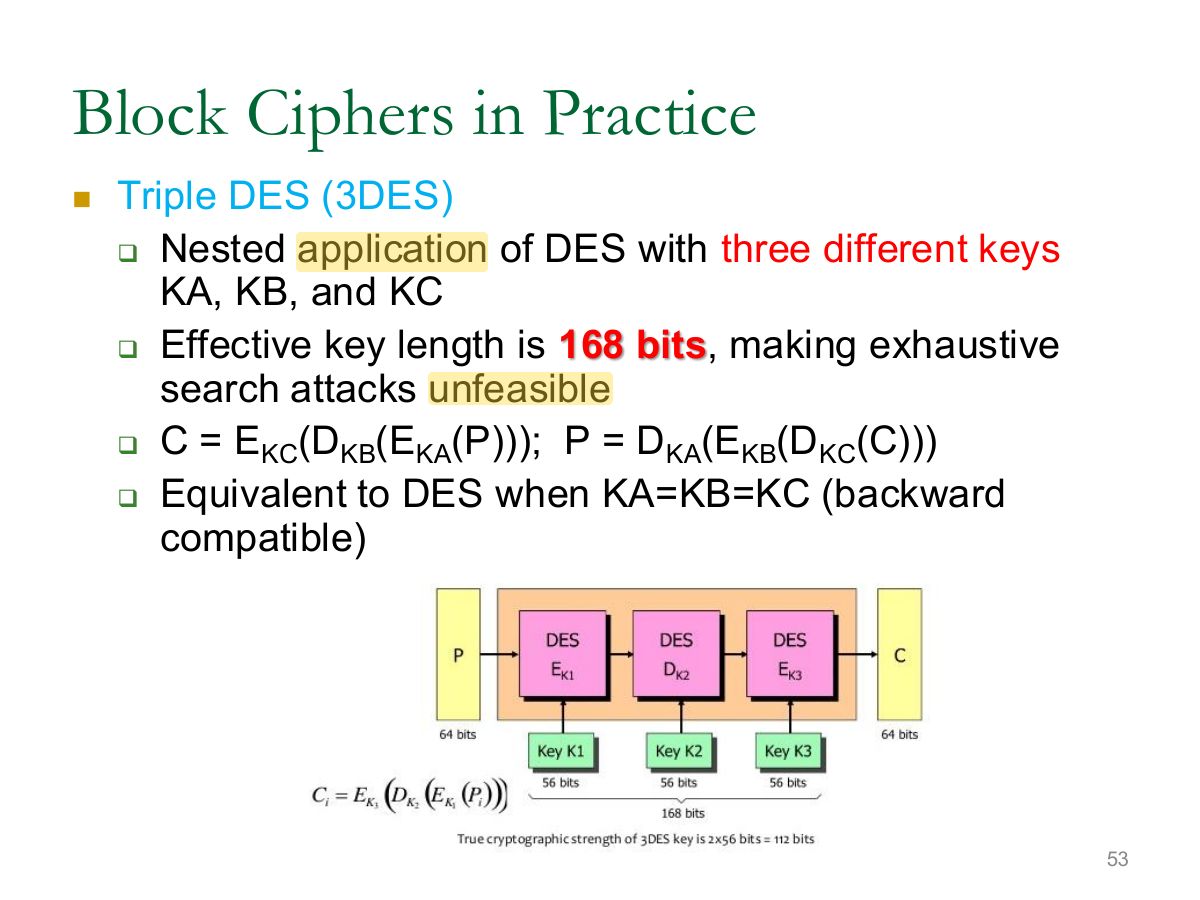
- 3DES: three DES passes with three keys: C = E_K3(D_K2(E_K1(P))).
★ Past exam
Exam weight
High
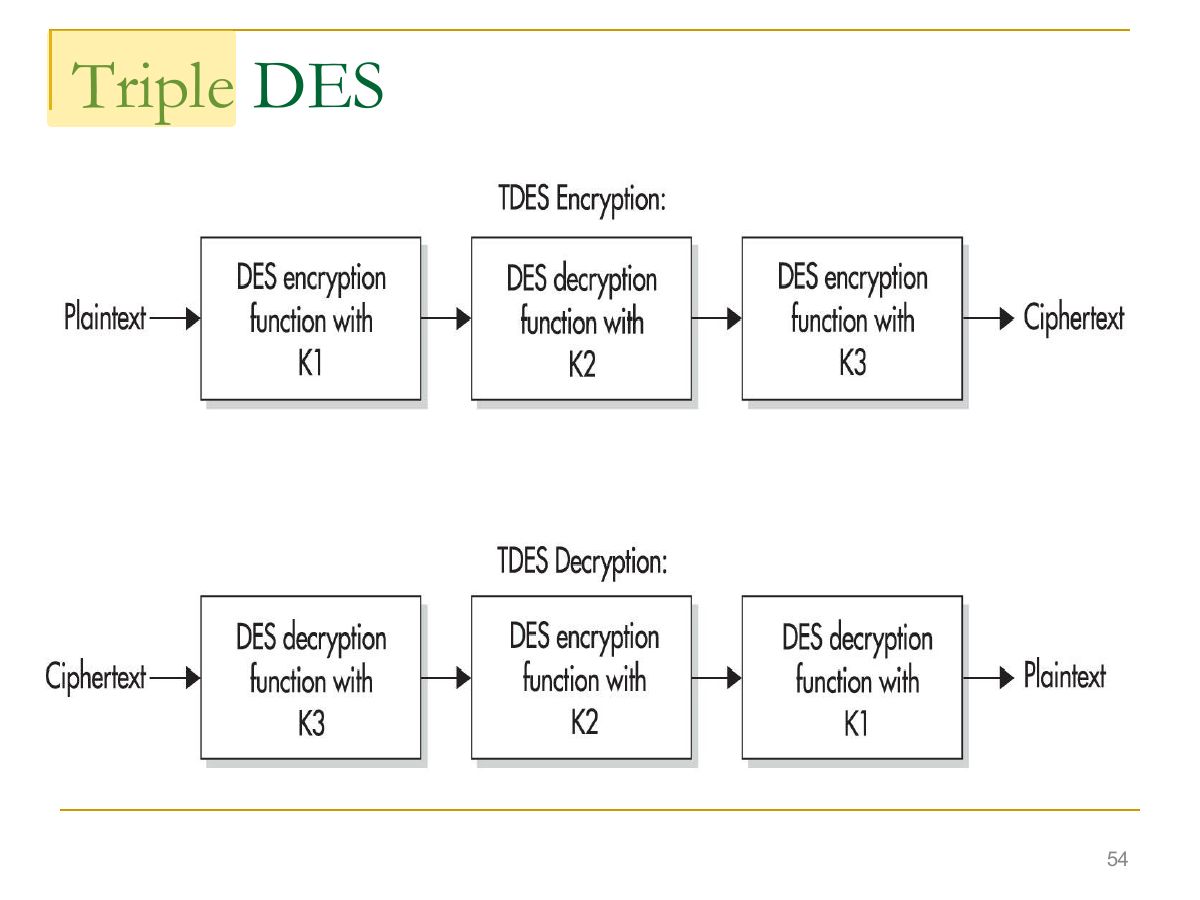
- 3DES decryption reverses it: P = D_K1(E_K2(D_K3(C))).
Asked in a real exam
🎯 How this can come up · 1 question
MCQ
3DES decryption order is:
Final 221 A and Major A.
Exam weight
Medium
- AES: NIST 2001 (Rijndael), 128-bit blocks, 128/192/256-bit keys.
🎯 How this can come up · 1 question
MCQ
AES uses a block size of:
Correct: 128 bits.
Exam weight Low
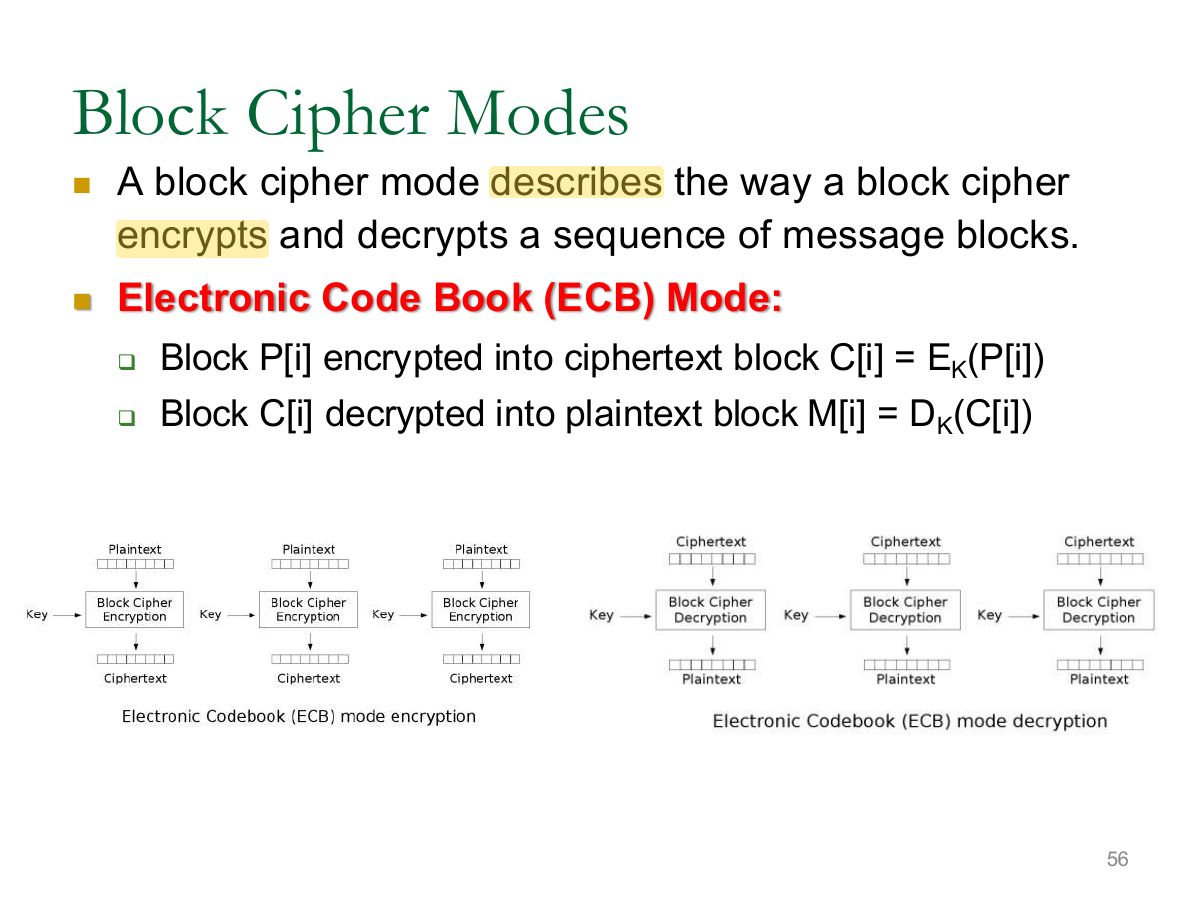
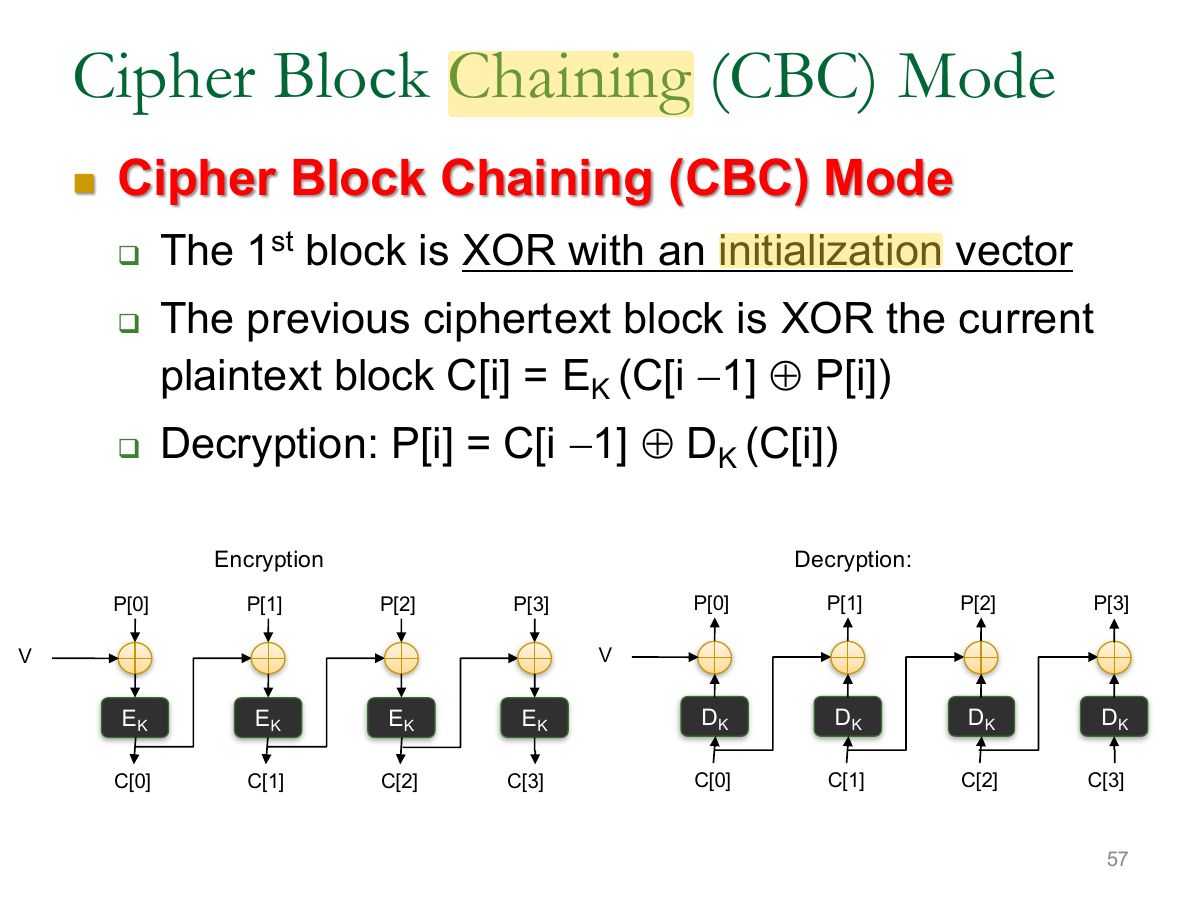
- A mode describes how a block cipher handles a sequence of blocks. ECB: each block alone (identical blocks → identical ciphertext).
TipModes: ECB C=E(P) · CBC C[i]=E(P[i] ⊕ C[i−1]),
C[−1]=IV · CFB C[i]=E(C[i−1]) ⊕ P[i] · OFB keystream
V[i]=E(V[i−1]) · CTR keystream E(counter).
★ Past exam
Exam weight
High
- CBC: XOR each plaintext block with the previous ciphertext block (IV first), then encrypt. Decrypt: P[i] = D_K(C[i]) ⊕ C[i−1].
Asked in a real exam
🎯 How this can come up · 2 questions
Written
In CBC, write the decryption function for P[2]. (Major A)
P[2] = D_K(C[2]) ⊕ C[1] (with C[−1] = IV for the first block).
MCQ
Which mode XORs each plaintext block with the previous ciphertext block before encryption?
Correct: CBC.
★ Past exam
Exam weight
High
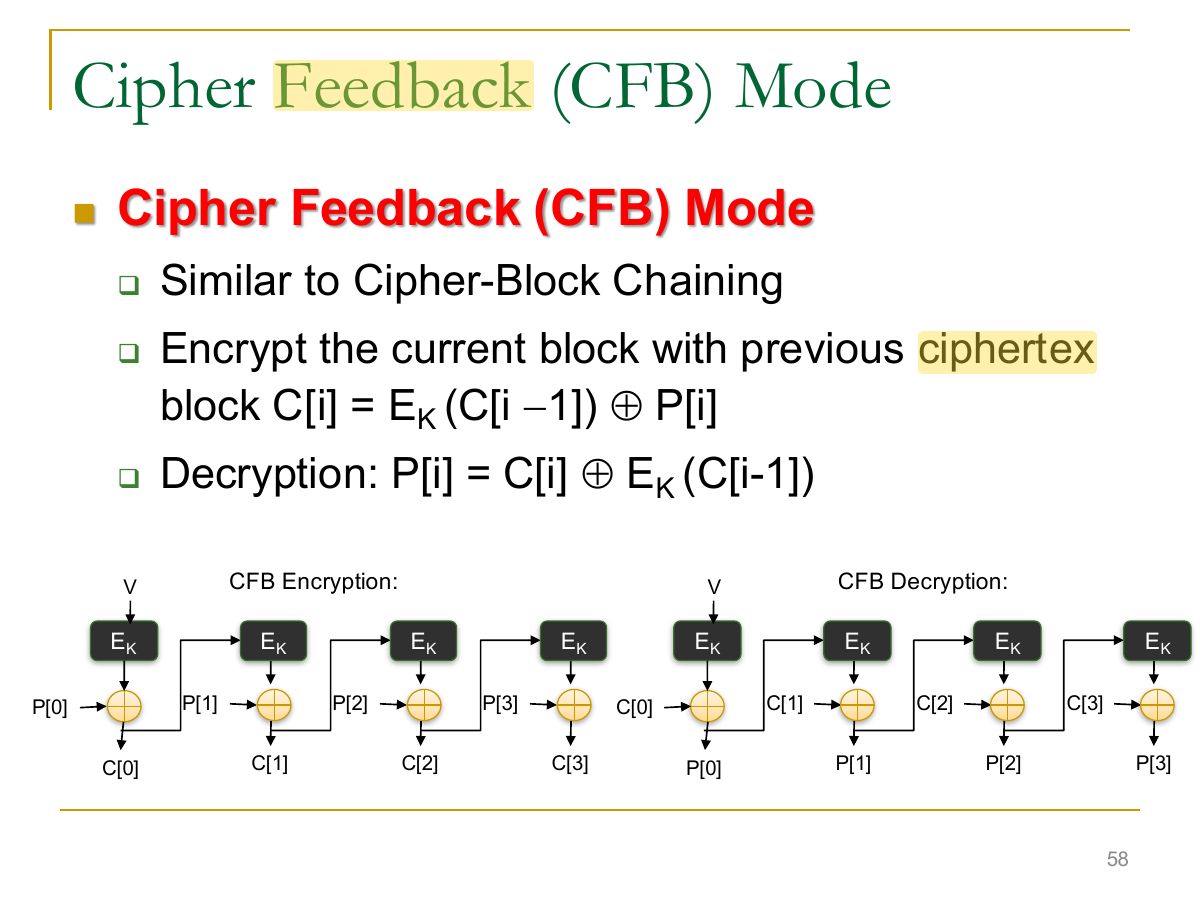
- CFB: encrypt the previous ciphertext block, then XOR with the plaintext: C[i] = E_K(C[i−1]) ⊕ P[i].
Asked in a real exam
🎯 How this can come up · 1 question
MCQ
C[i] = E_K(C[i−1]) ⊕ P[i] describes:
Major A.
Exam weight Low
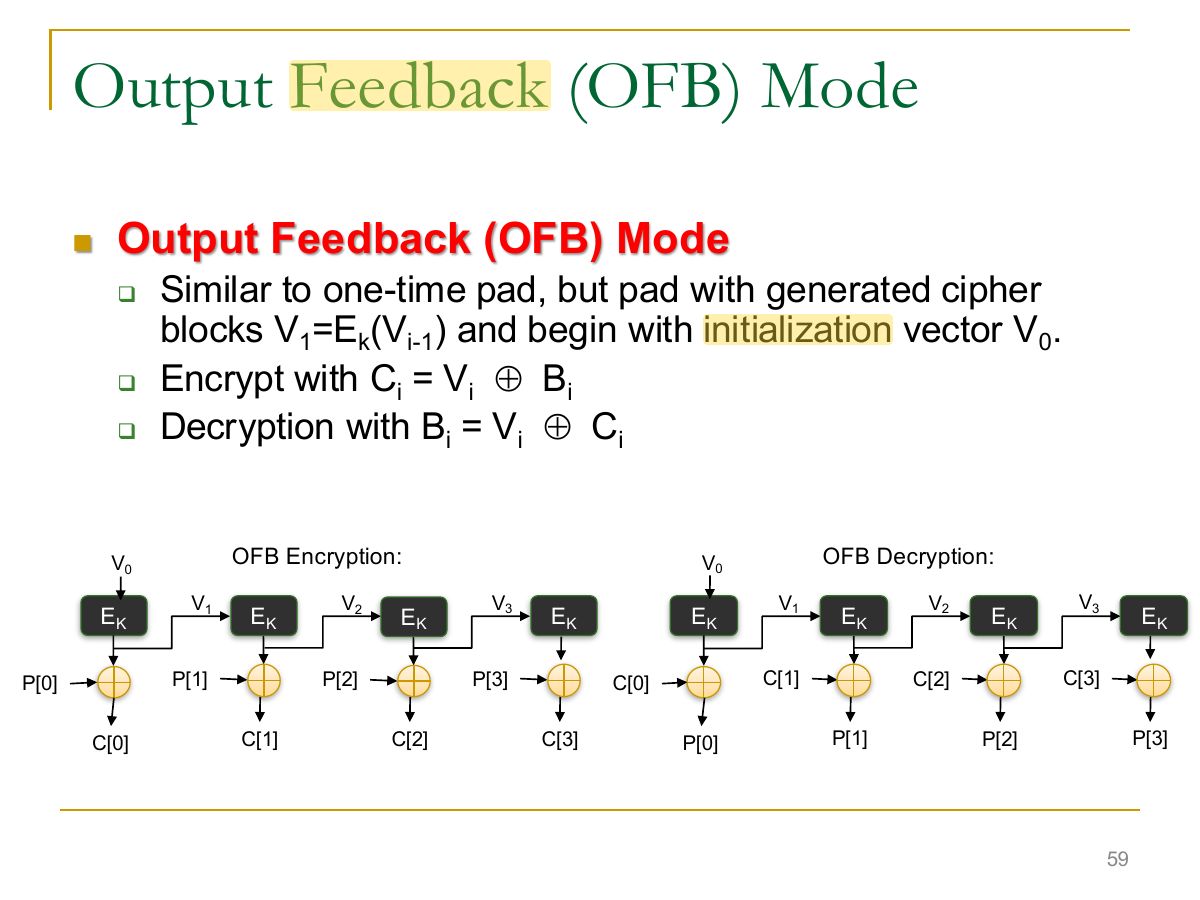
- OFB: keystream from repeatedly encrypting the IV; C[i] = V[i] ⊕ P[i].
Exam weight Low
- CTR: keystream = E_K(counter); blocks can be processed in parallel.
Exam weight Low
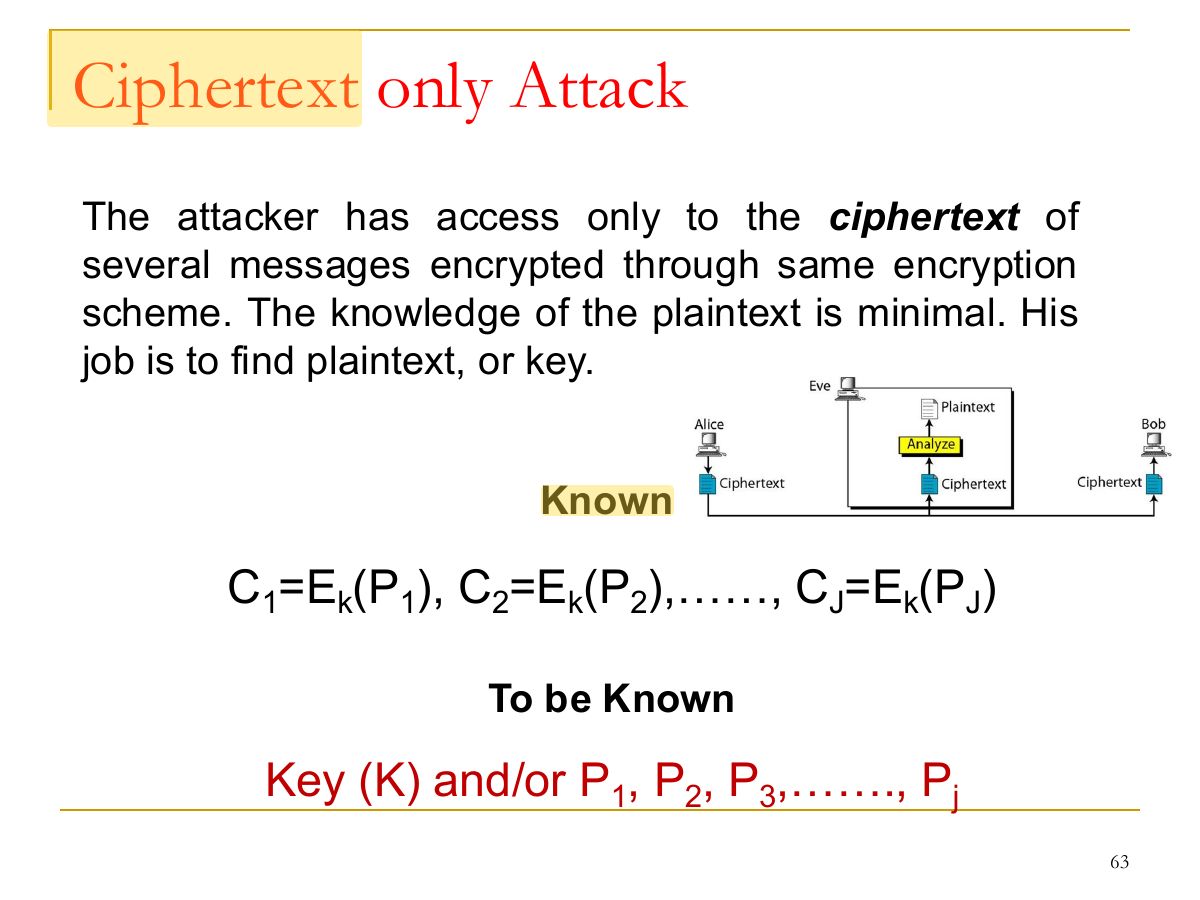
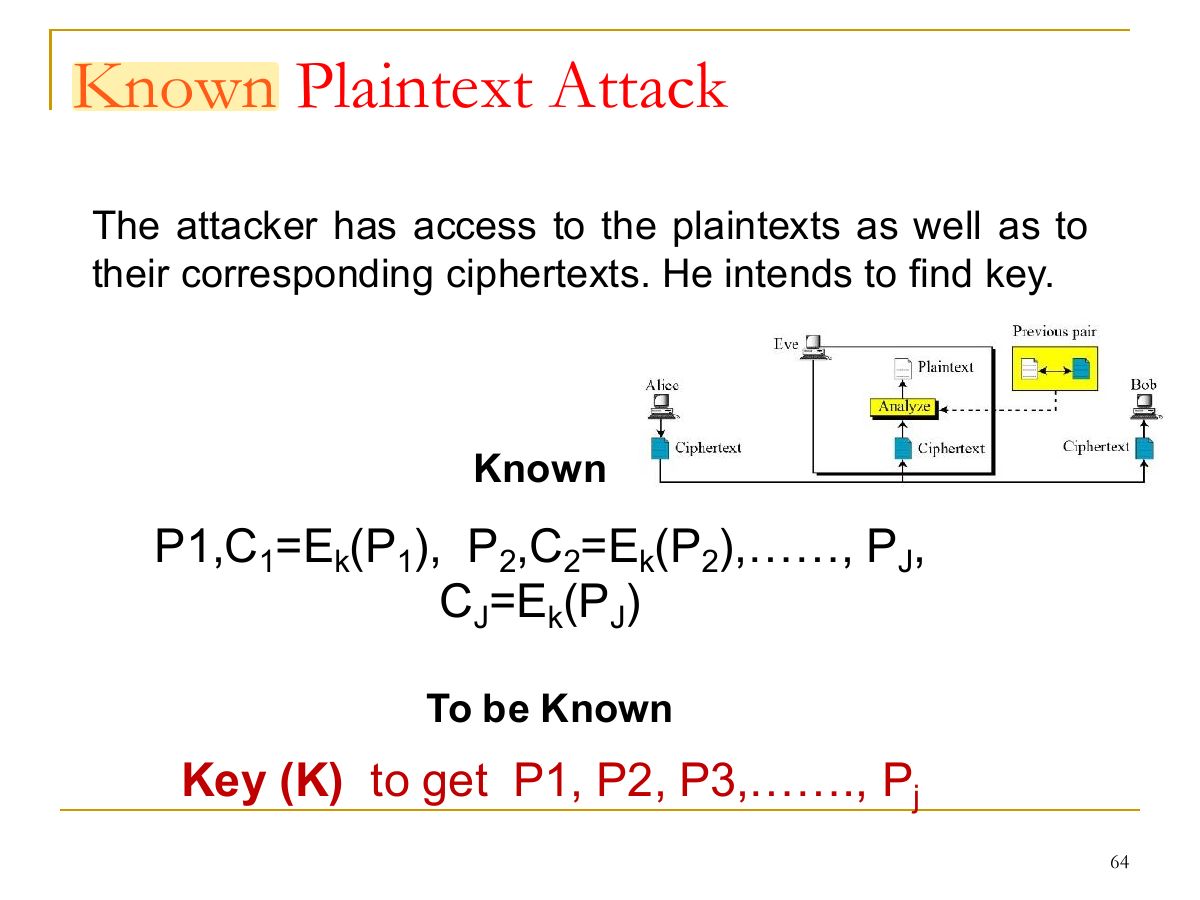
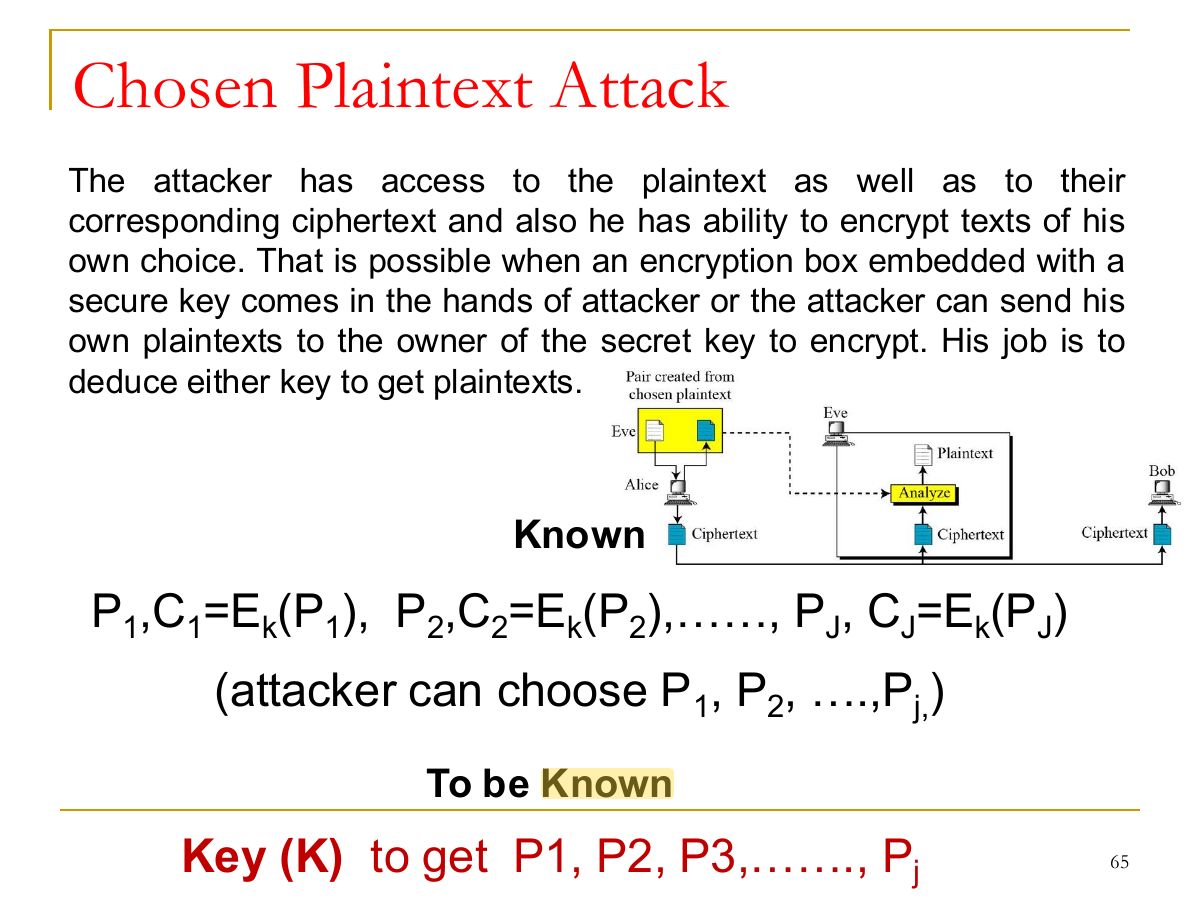
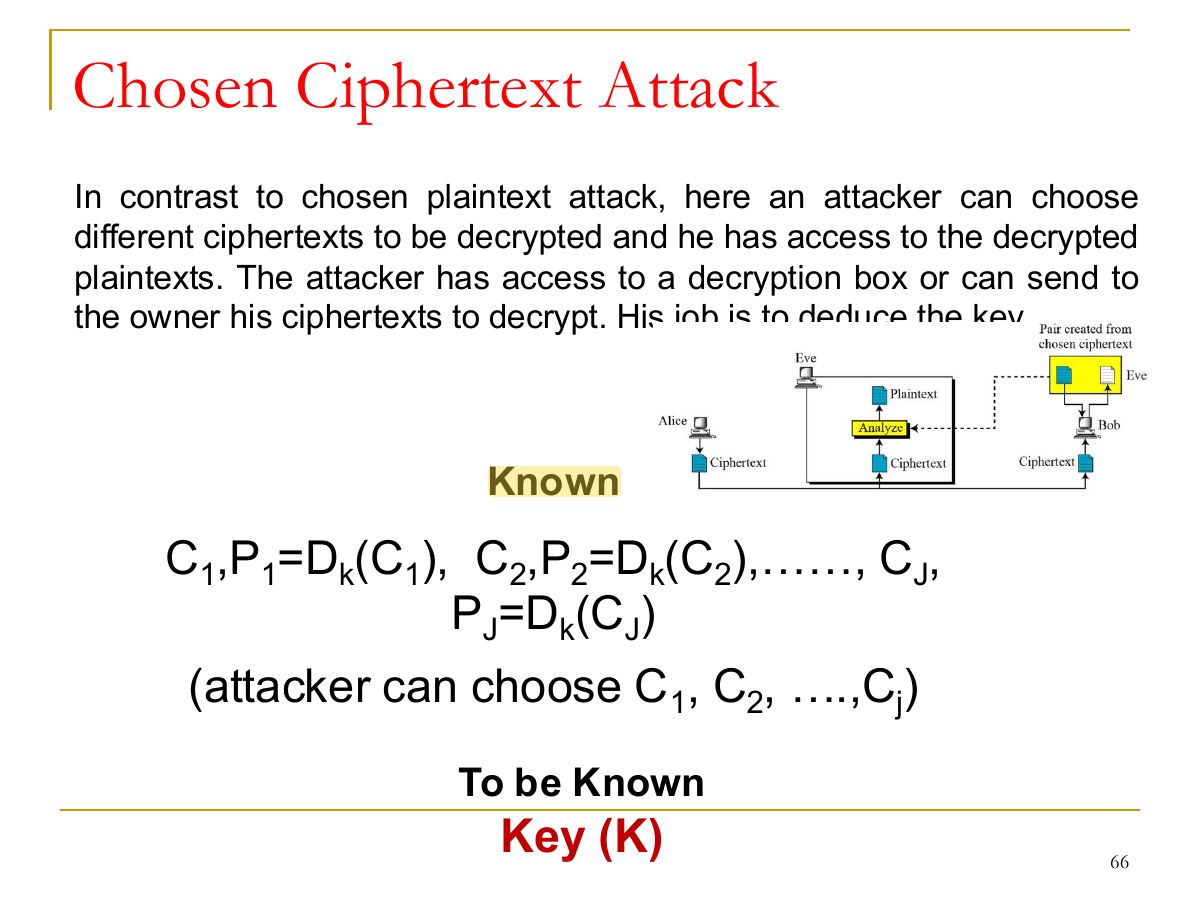
- Attacker’s objective: recover the KEY. Two approaches: cryptanalysis and brute force.
Exam weight Low
- Cryptanalysis by attacker knowledge: ciphertext only, known plaintext, chosen plaintext, chosen ciphertext.
Exam weight Low
- Ciphertext only: the attacker has only ciphertext (hardest for the attacker).
Exam weight Low
- Known plaintext: has plaintext–ciphertext pairs.
Exam weight
Medium
- Chosen plaintext: can encrypt texts of their choice.
🎯 How this can come up · 1 question
MCQ
An attacker who can get any plaintext of their choice encrypted is performing a:
Correct: Chosen-plaintext attack.
Exam weight Low
- Chosen ciphertext: can get chosen ciphertexts decrypted.
Exam weight Low
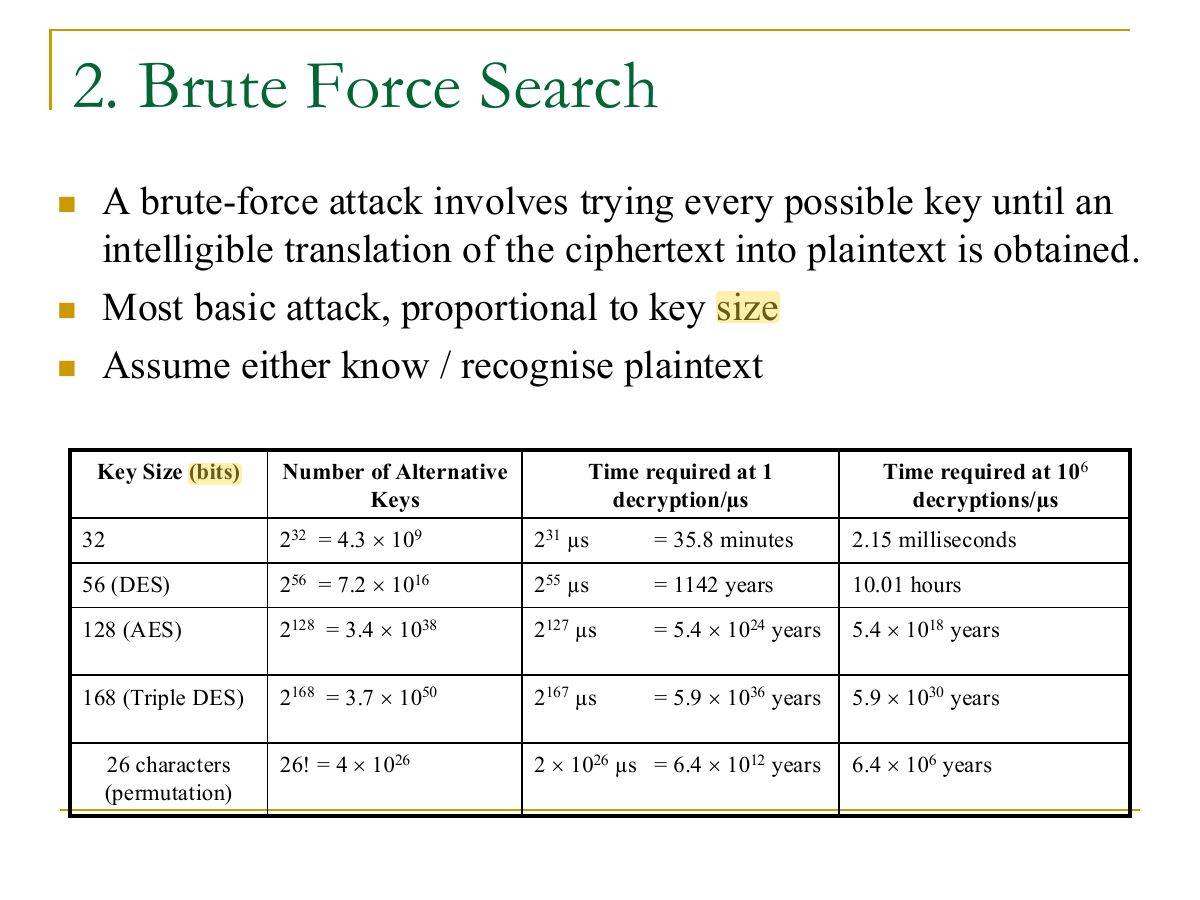
- Brute force: try every key; effort grows with key size.
Exam weight Low
- End of chapter.
Seen again
No slides match this filter.