Chapter 1 · Annotated slides
Network Security Fundamentals
Threats, vulnerabilities, attacks and threat actors, attacker methodologies, the goals and principles of network defense (information assurance), defense approaches, administrative controls: regulatory frameworks, ISO standards, security policies and awareness training, then physical and technical controls.
- 47 slides
- 0 asked in real exams
- 0 related to real exam questions
- 4 practice questions
Slide text
Study notes
Highlight: key words
Tips, tricks & traps
Seen again elsewhere
How it can come up
Exam weight ●○○ Low
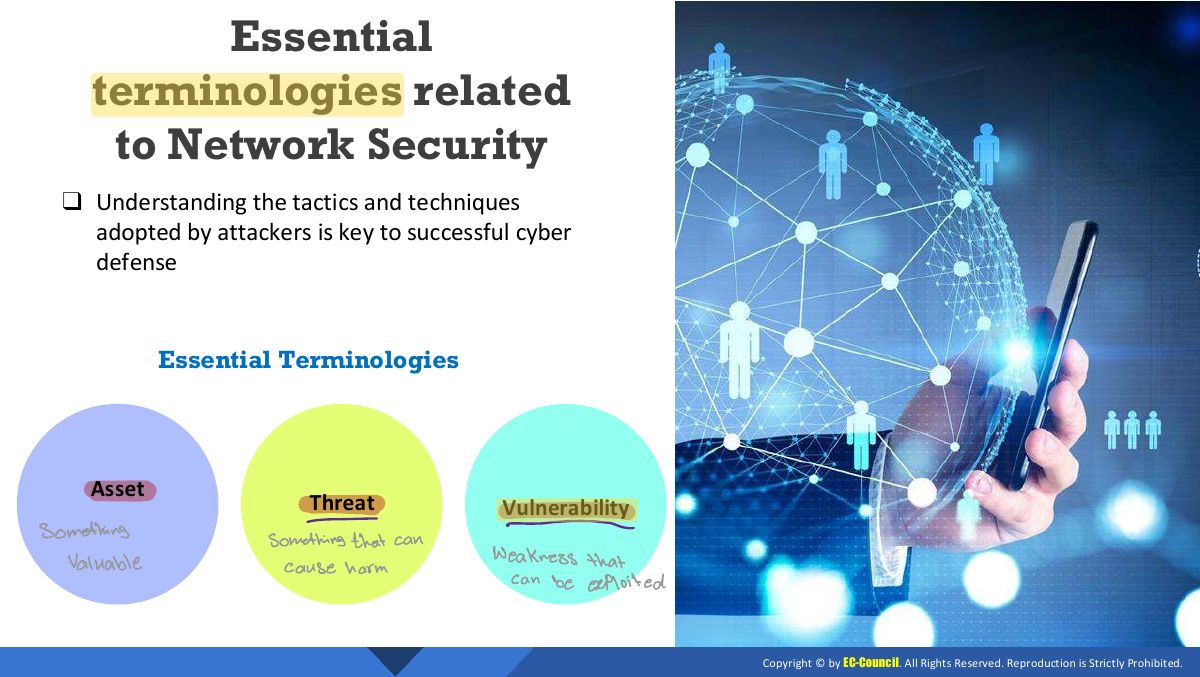
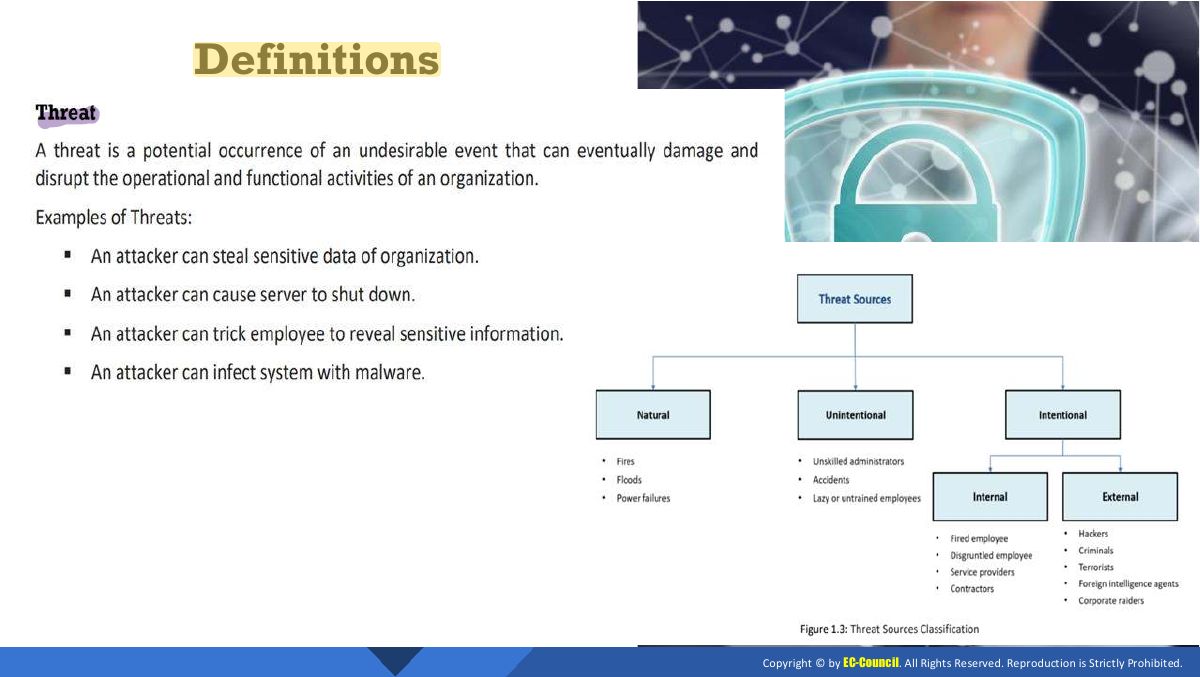
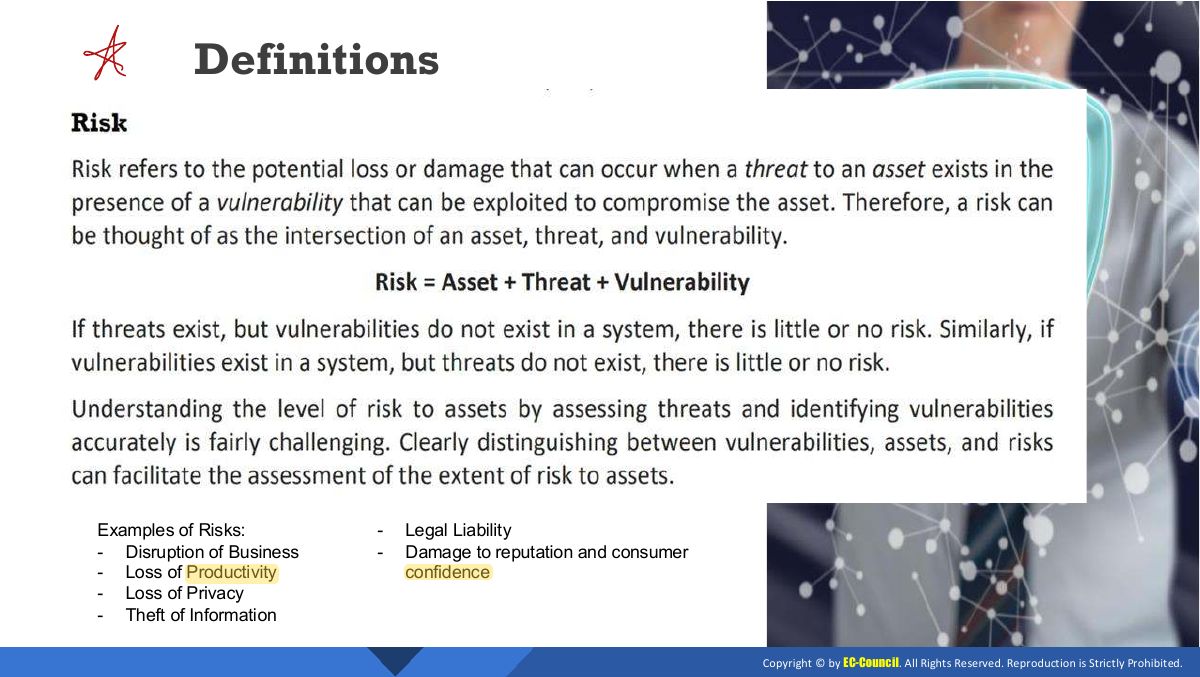
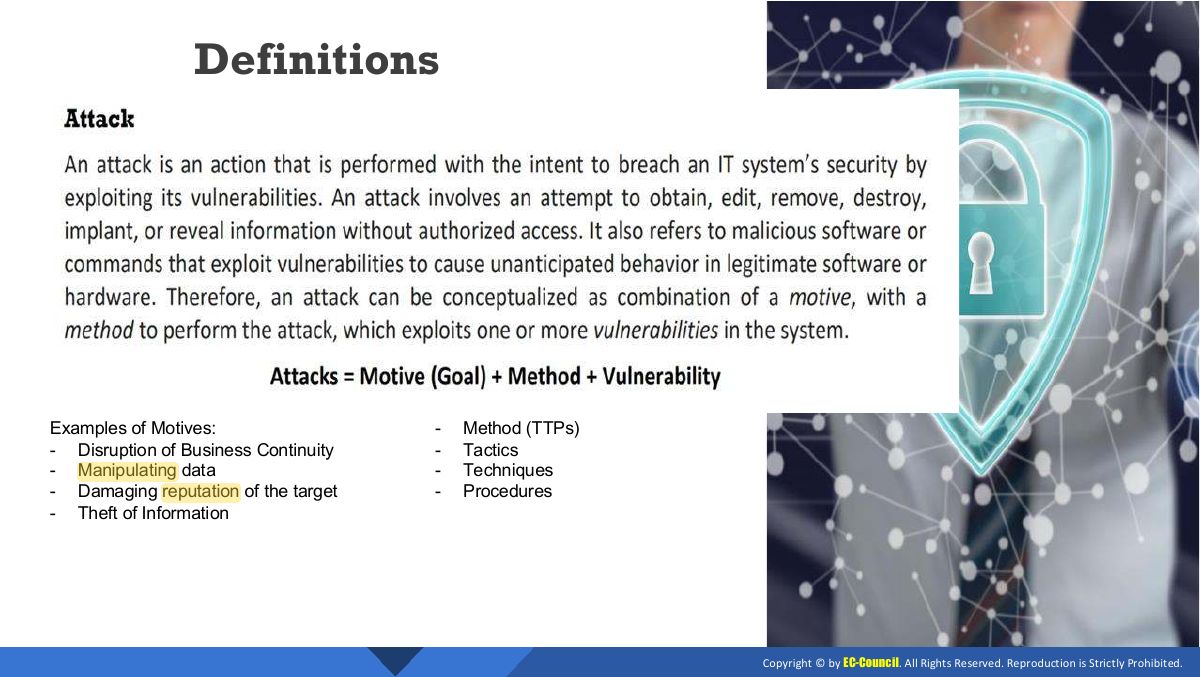
- Threat: potential harm. Vulnerability: weakness. Attack: an attempt to exploit a vulnerability. Risk: threat × vulnerability × impact.
Exam weight ●○○ Low
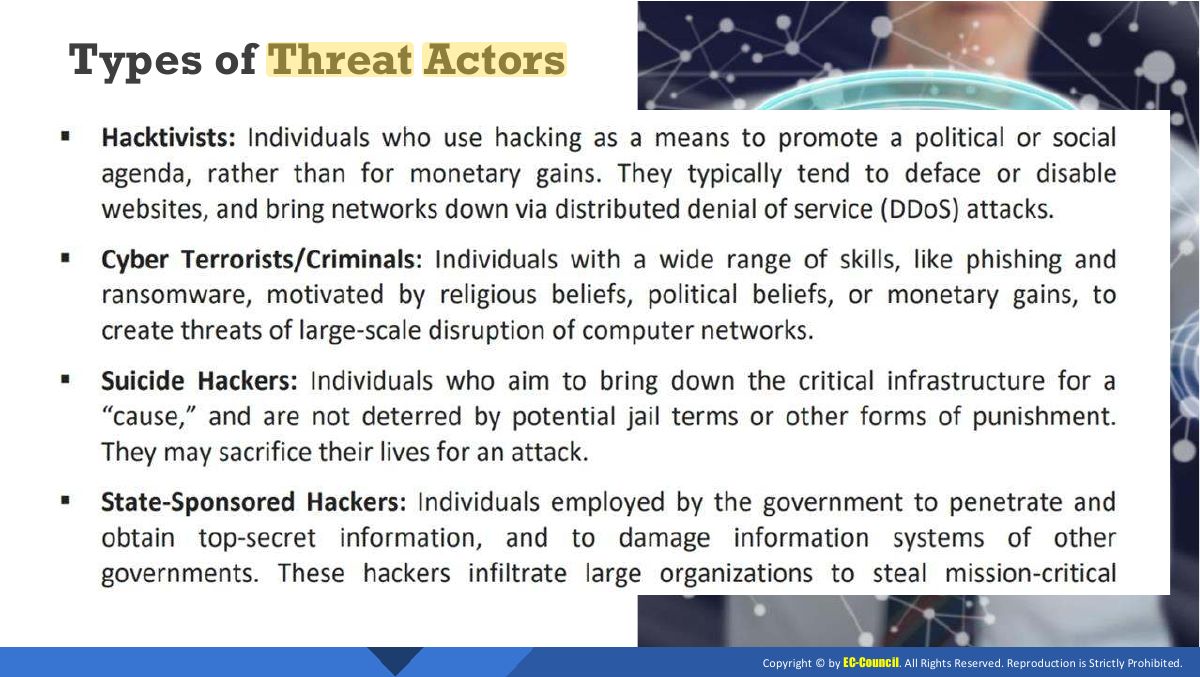
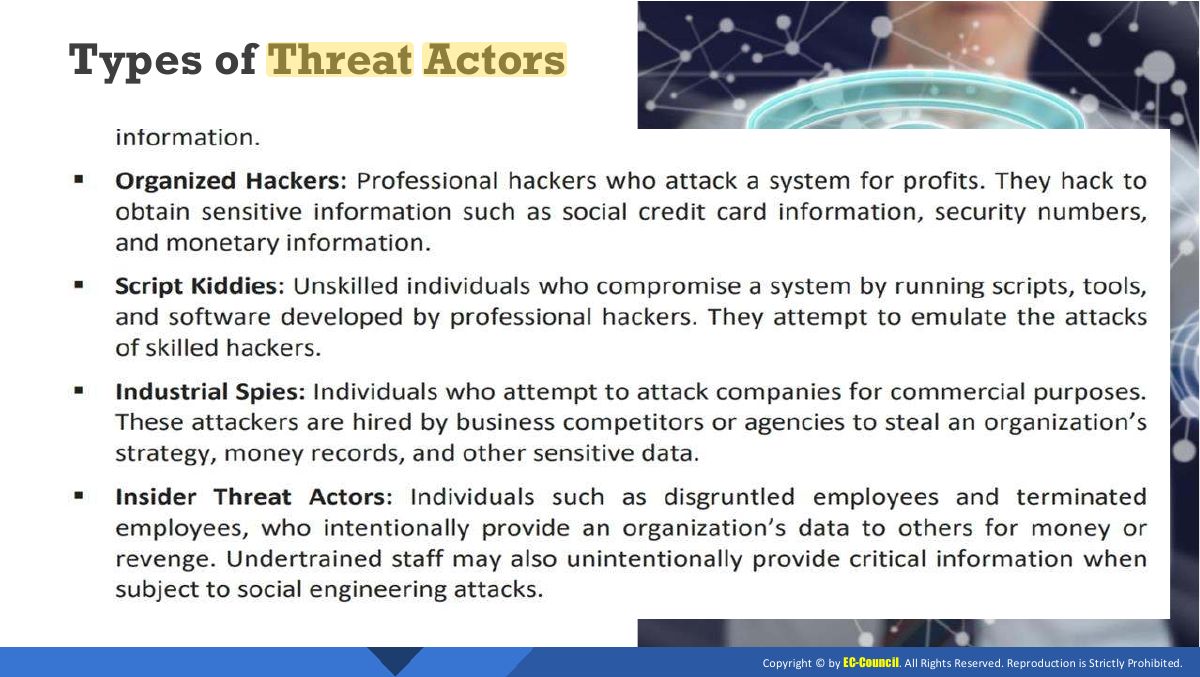
- Threat actors: script kiddies, hacktivists, organized crime, nation states, insiders, cyber terrorists.
Exam weight ●○○ Low
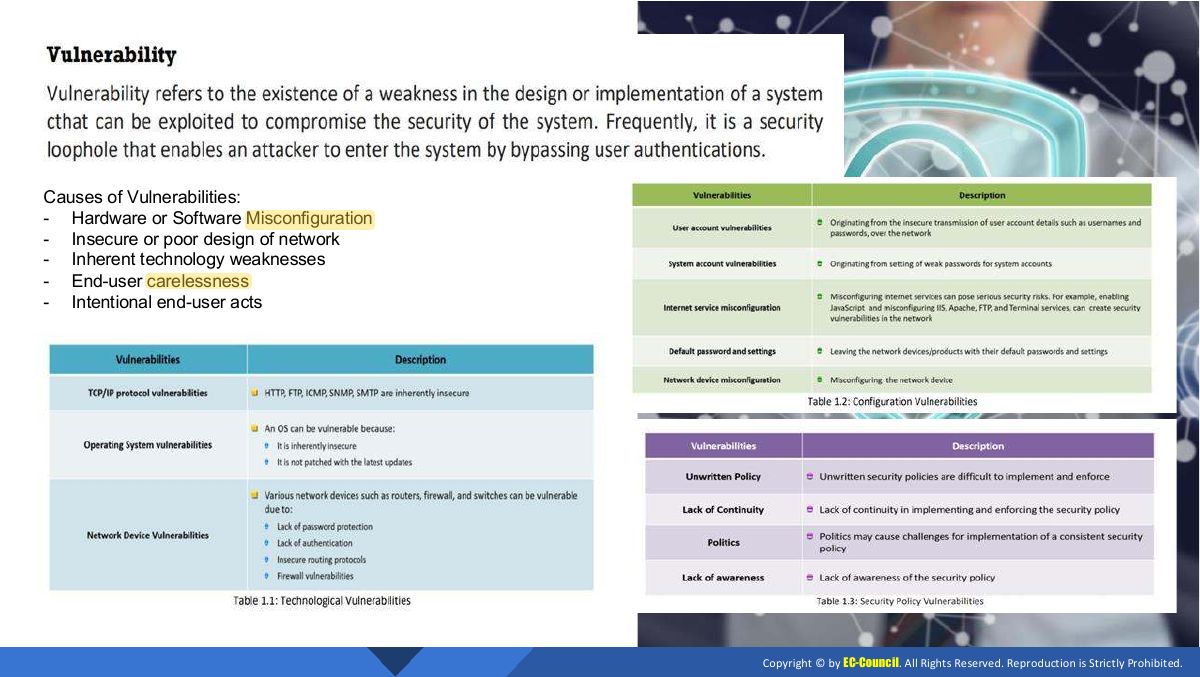
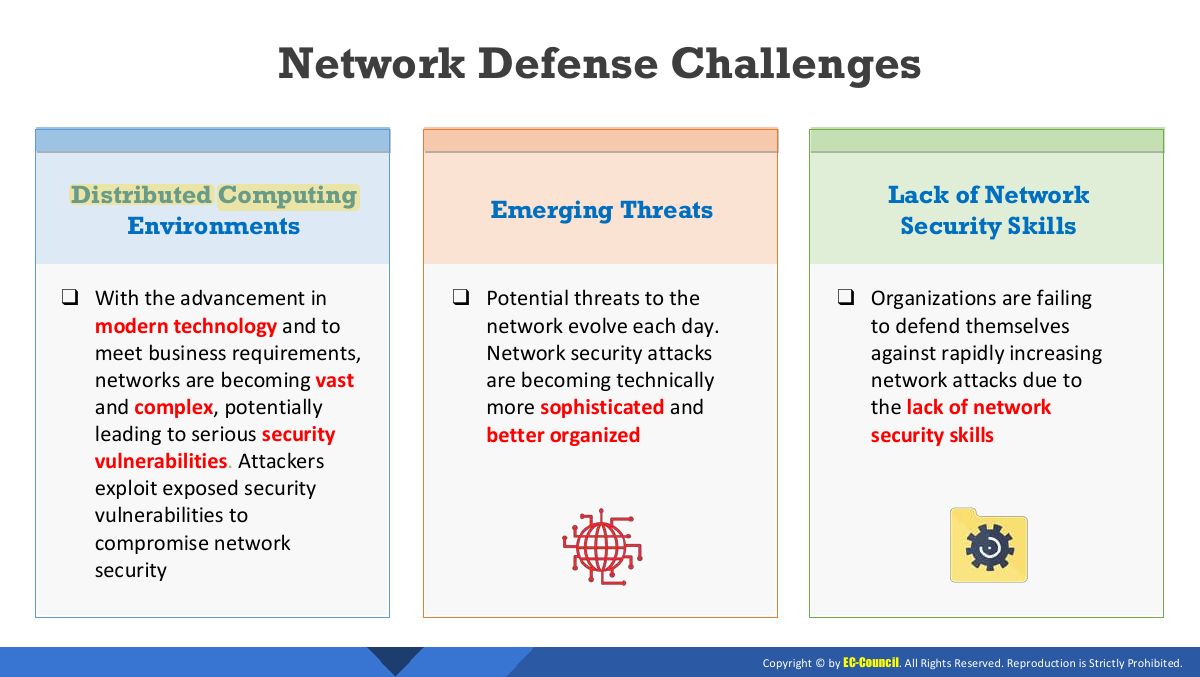
- Vulnerabilities come from misconfiguration, design flaws, unpatched software, weak policies and human error.
Exam weight ●○○ Low
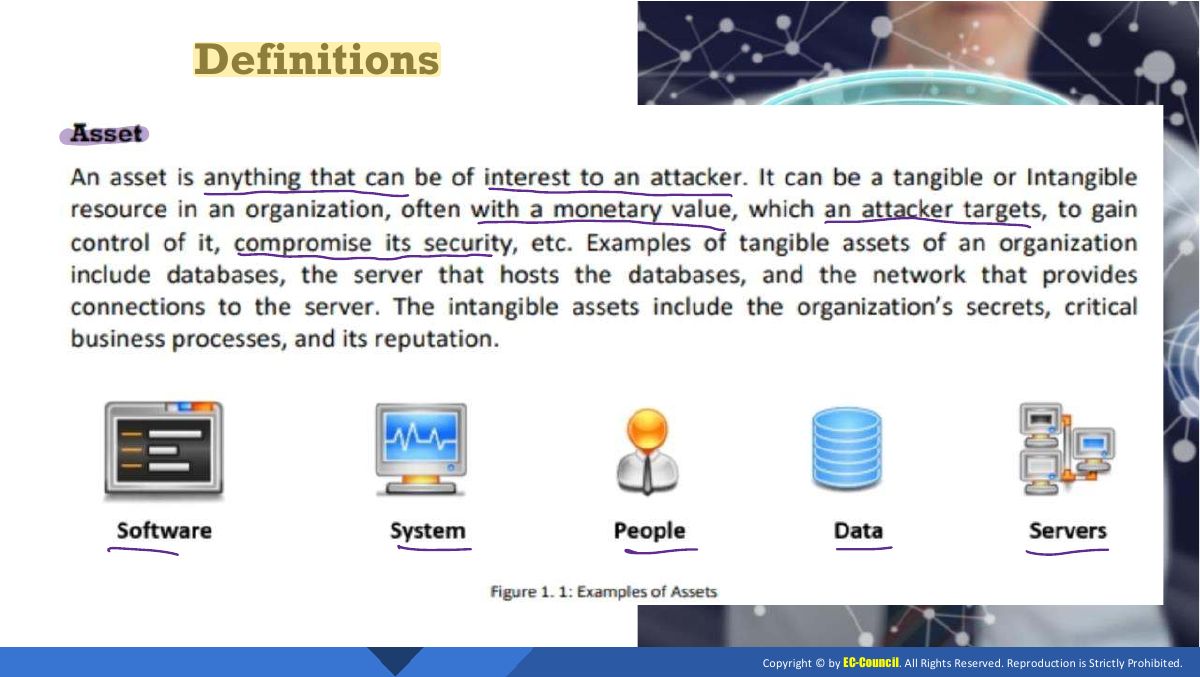
- Goal of network defense: protect information, resources and services from unauthorized access, misuse and disruption.
Exam weight ●●● High
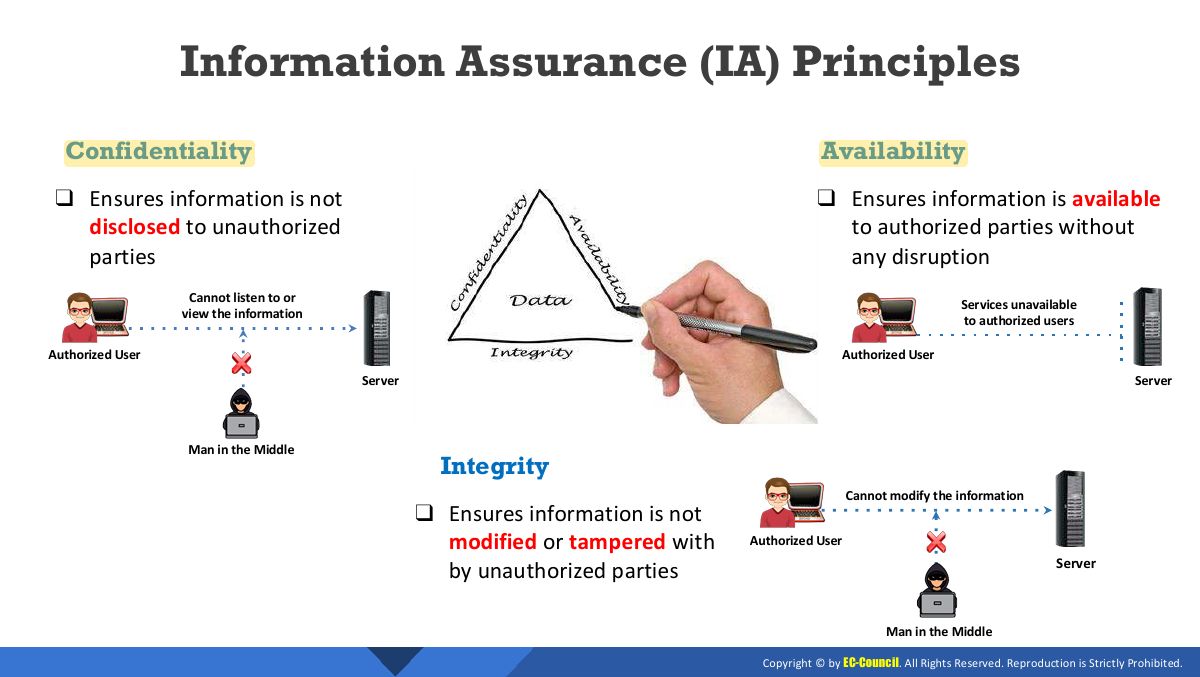
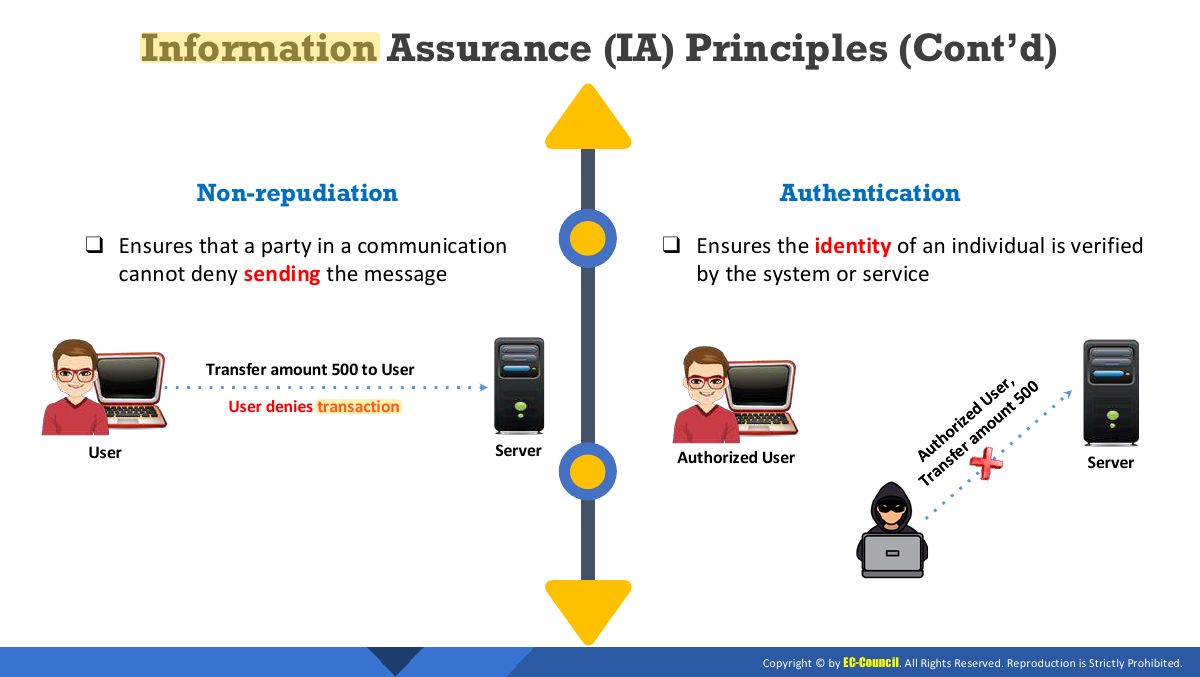
- Information Assurance principles: confidentiality, integrity, availability, authentication, non-repudiation.
Exam weight ●●○ Medium
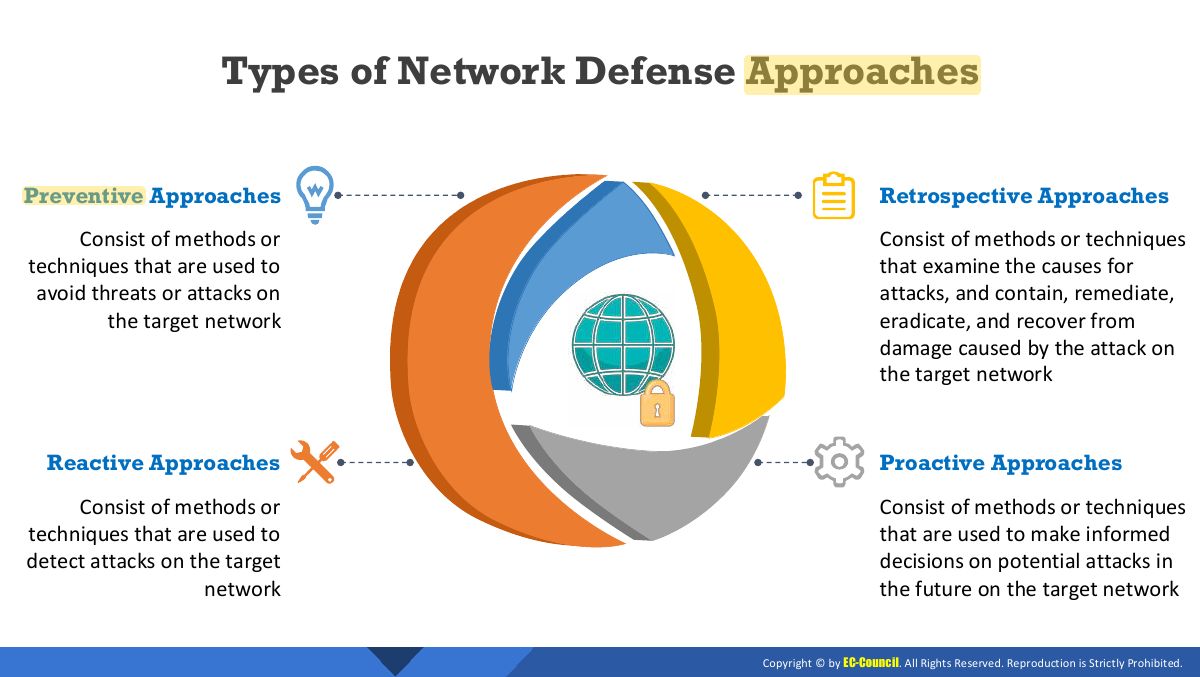
- Defense approaches: preventive, reactive, retrospective, proactive.
Exam weight ●○○ Low
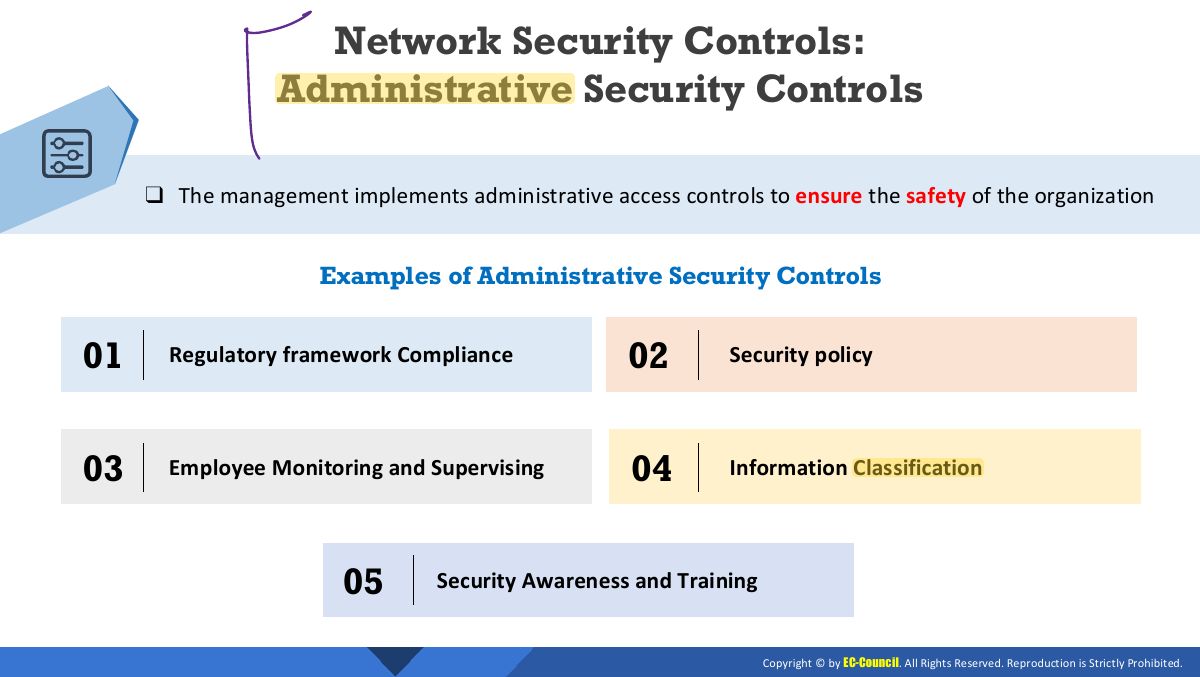
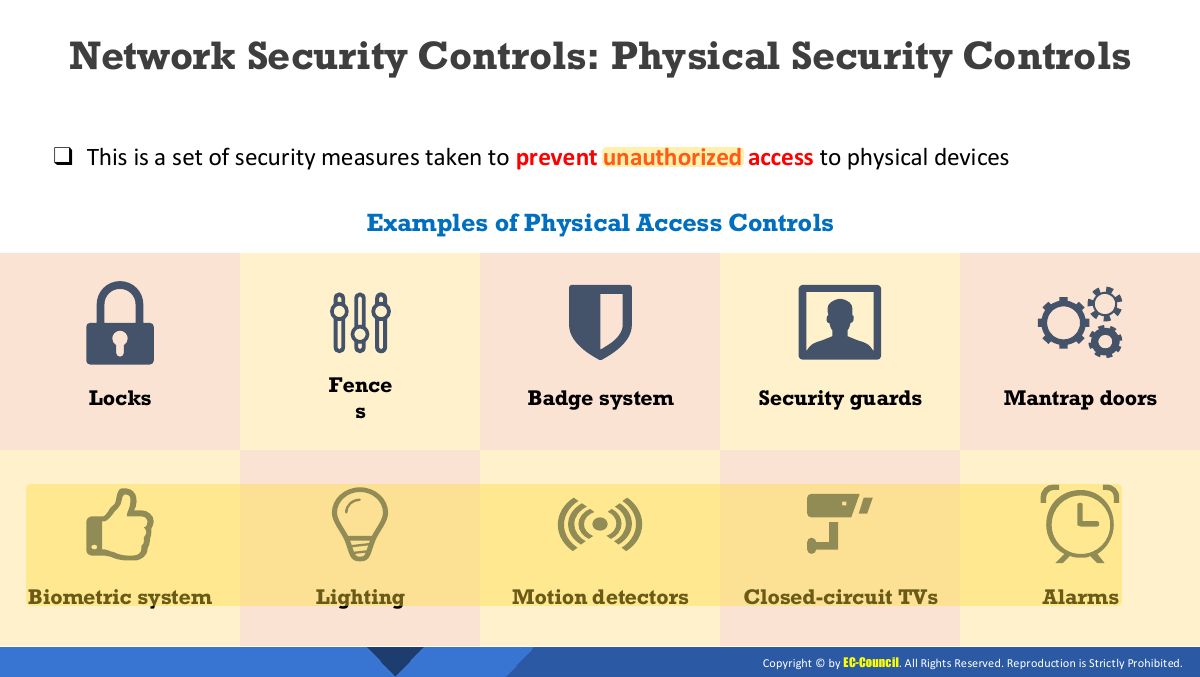
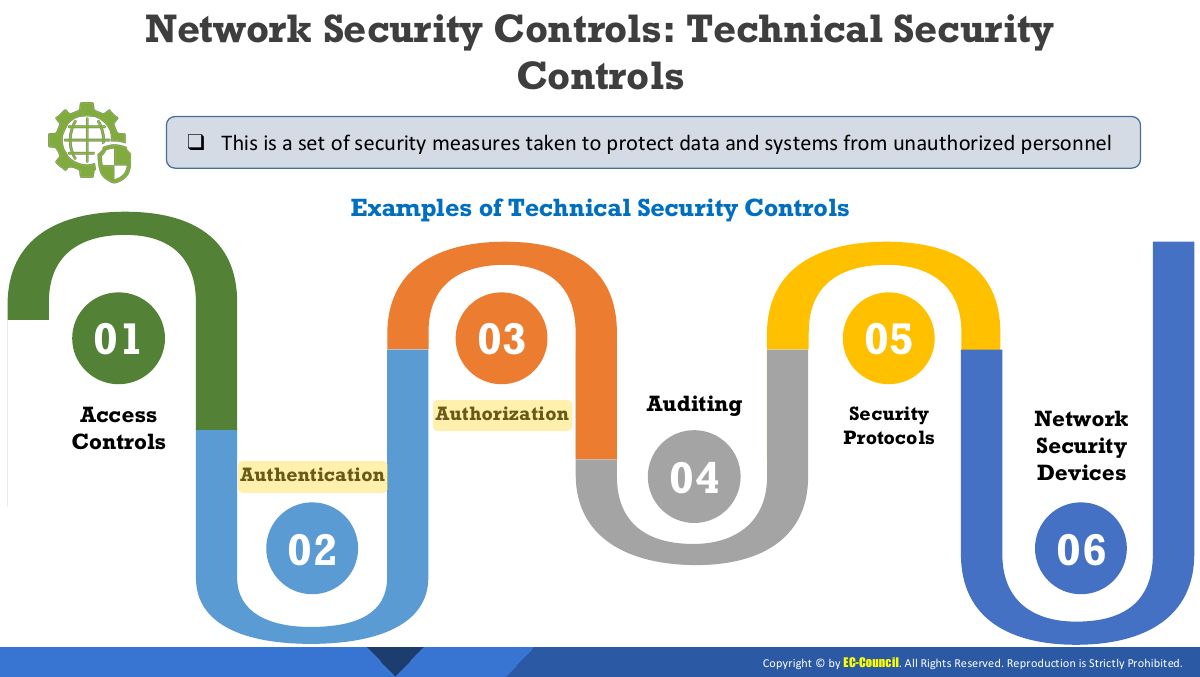
- Three control families: administrative (policies, training), physical (locks, guards), technical (firewalls, encryption, access control).
Exam weight ●●● High
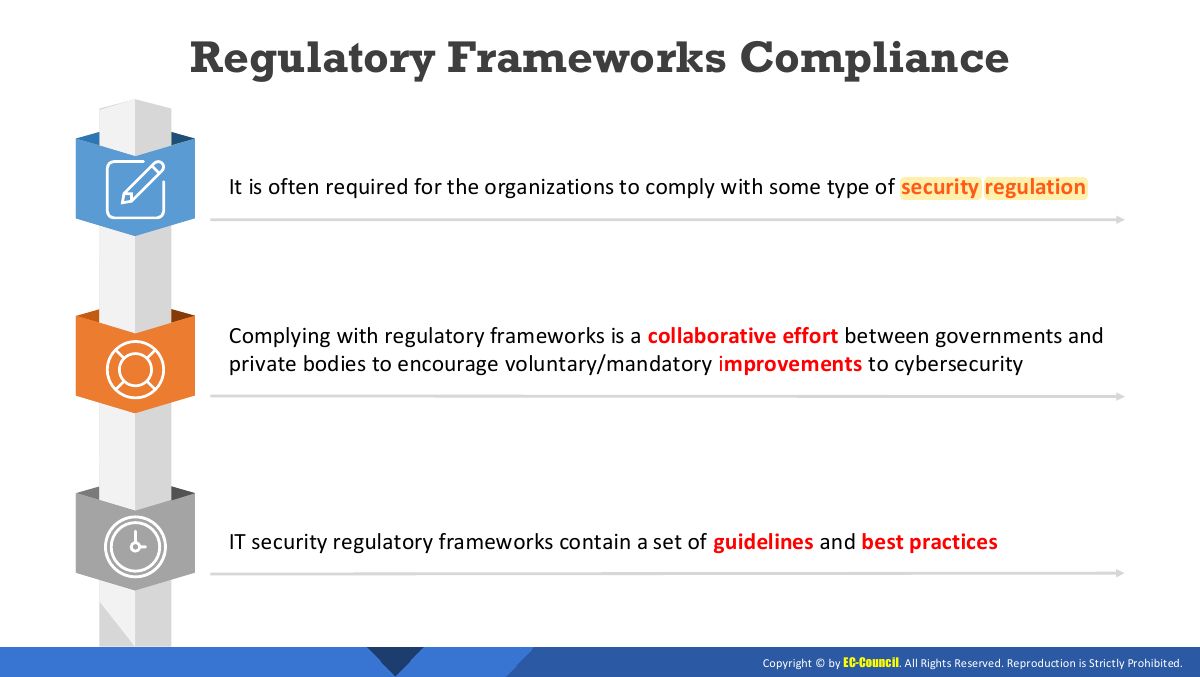
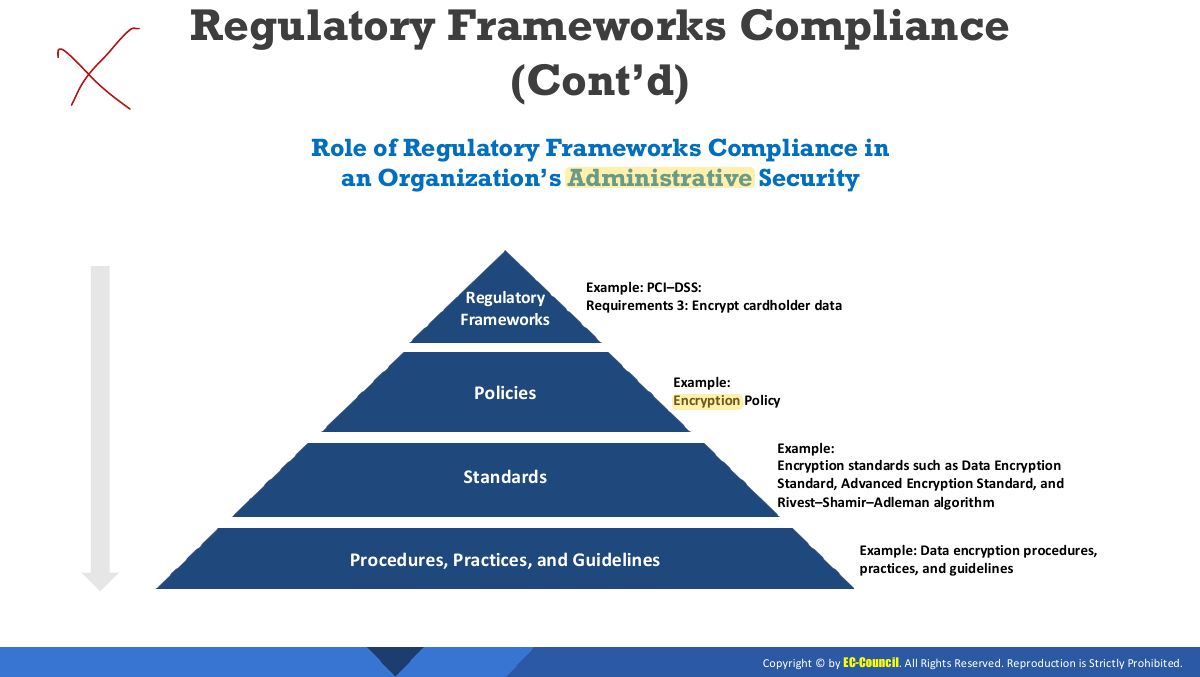
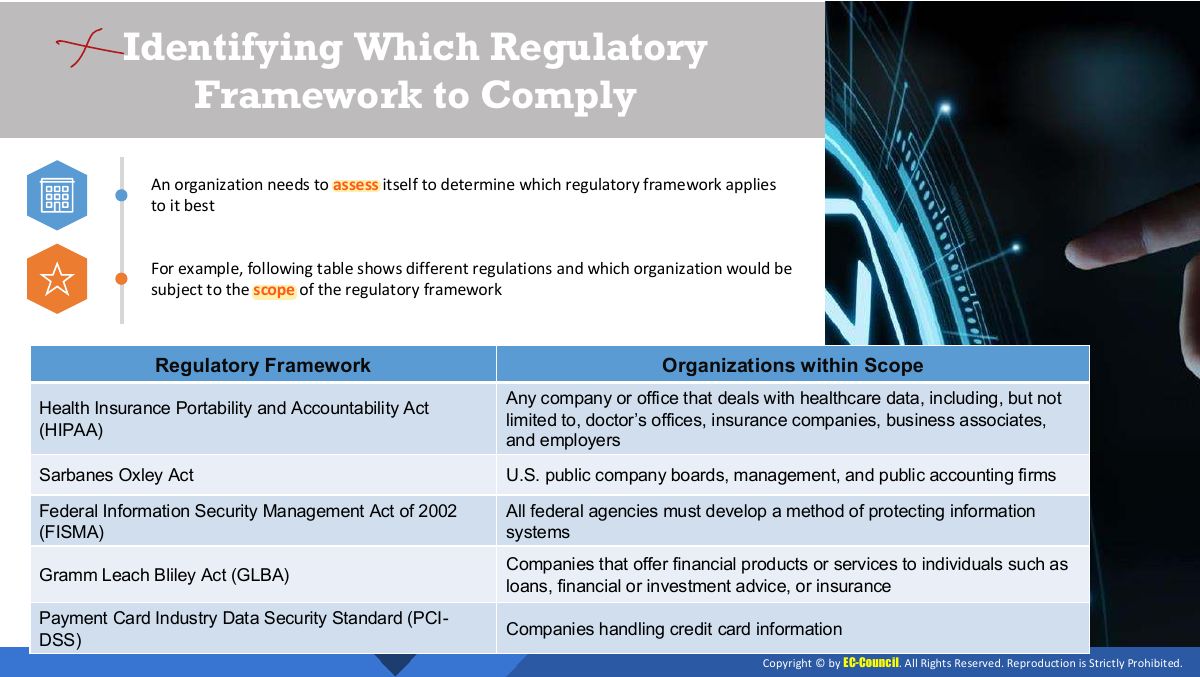
- Regulatory frameworks: PCI DSS (cards), HIPAA (health), SOX (finance), GDPR (EU personal data), ISO 27001.
Exam weight ●○○ Low
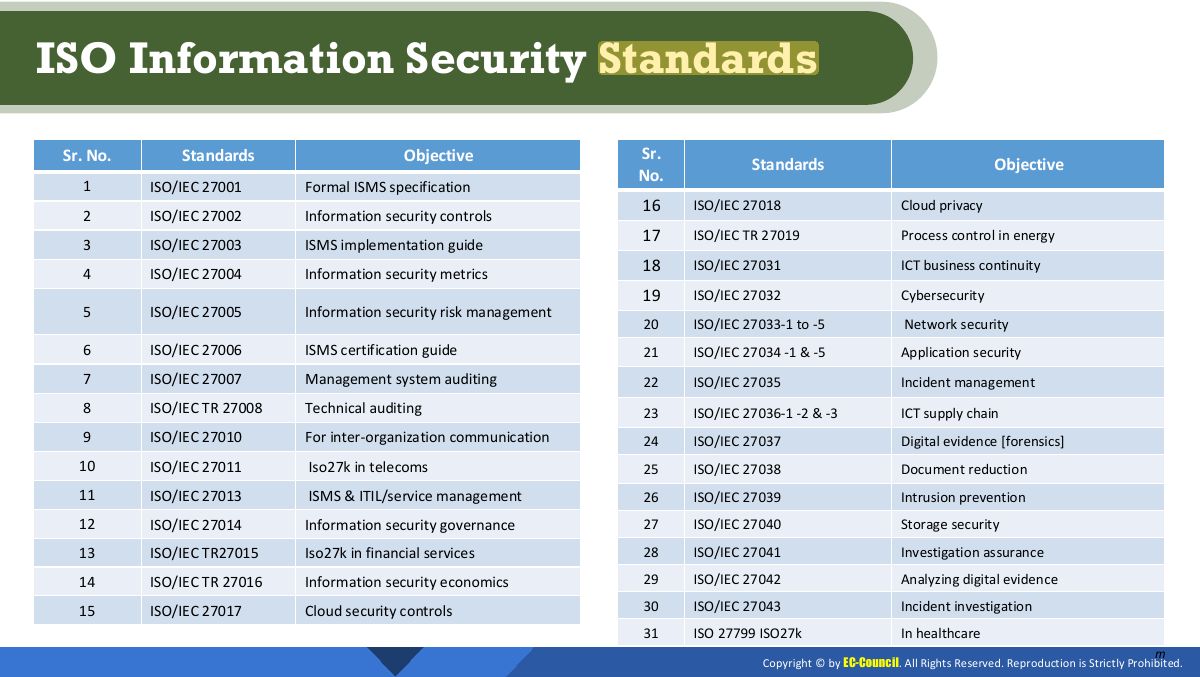
- ISO/IEC 27001: requirements for an Information Security Management System (ISMS); 27002: the controls.
Exam weight ●○○ Low
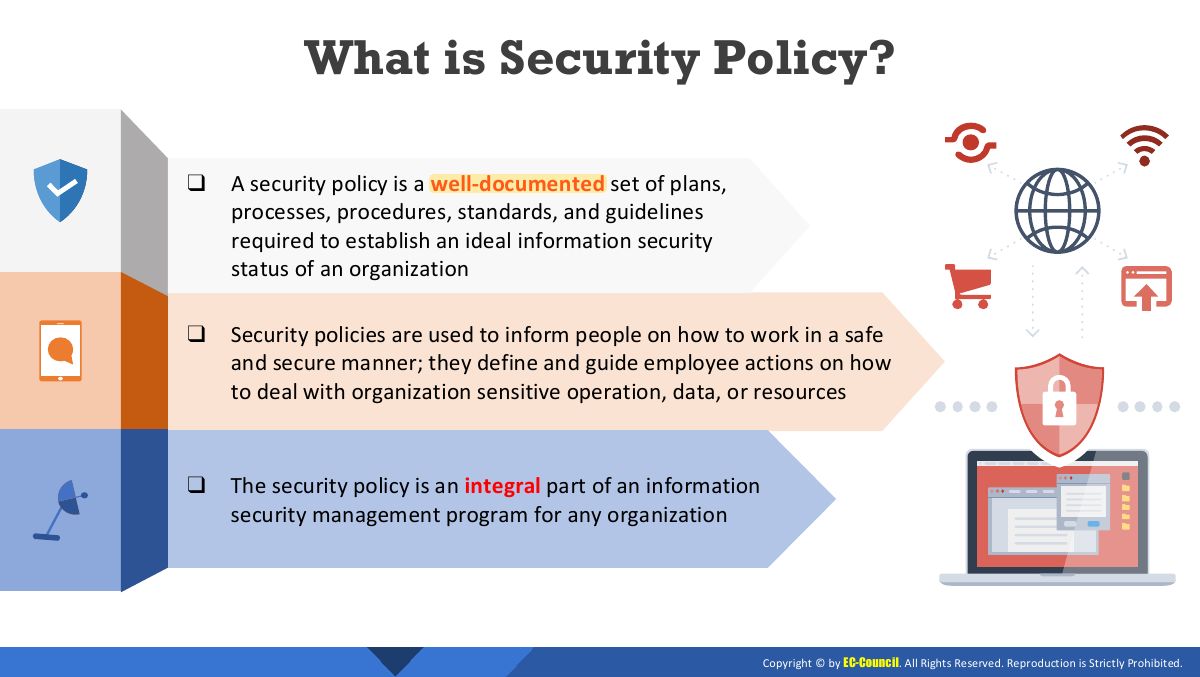
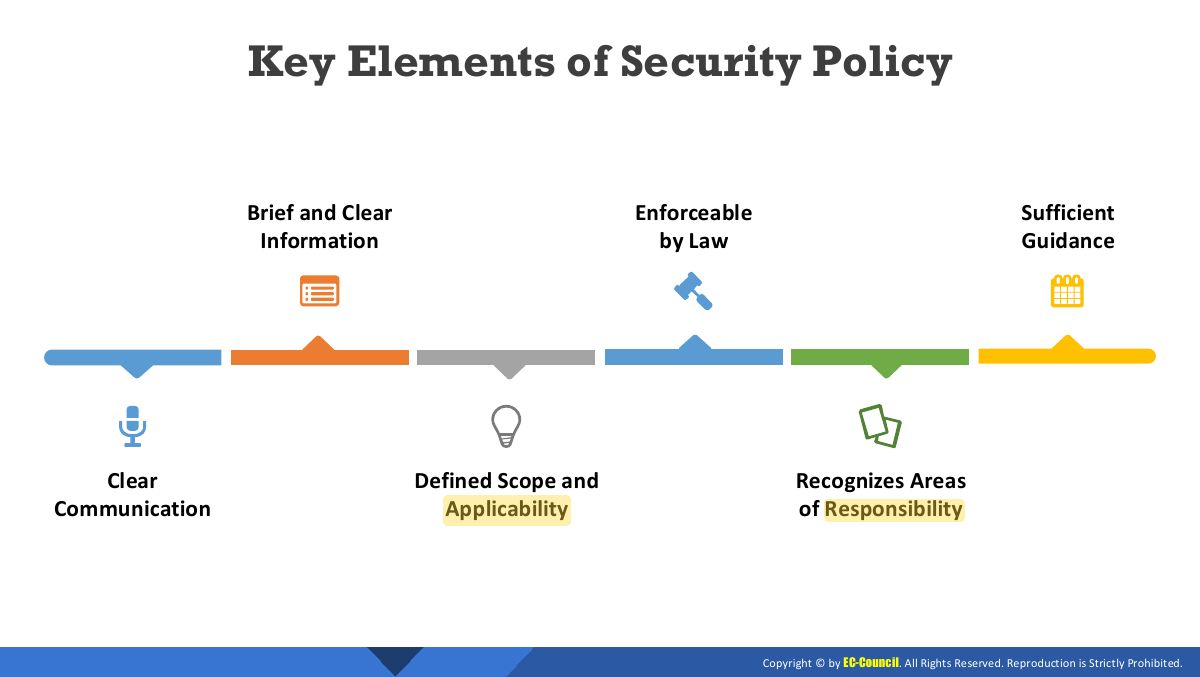
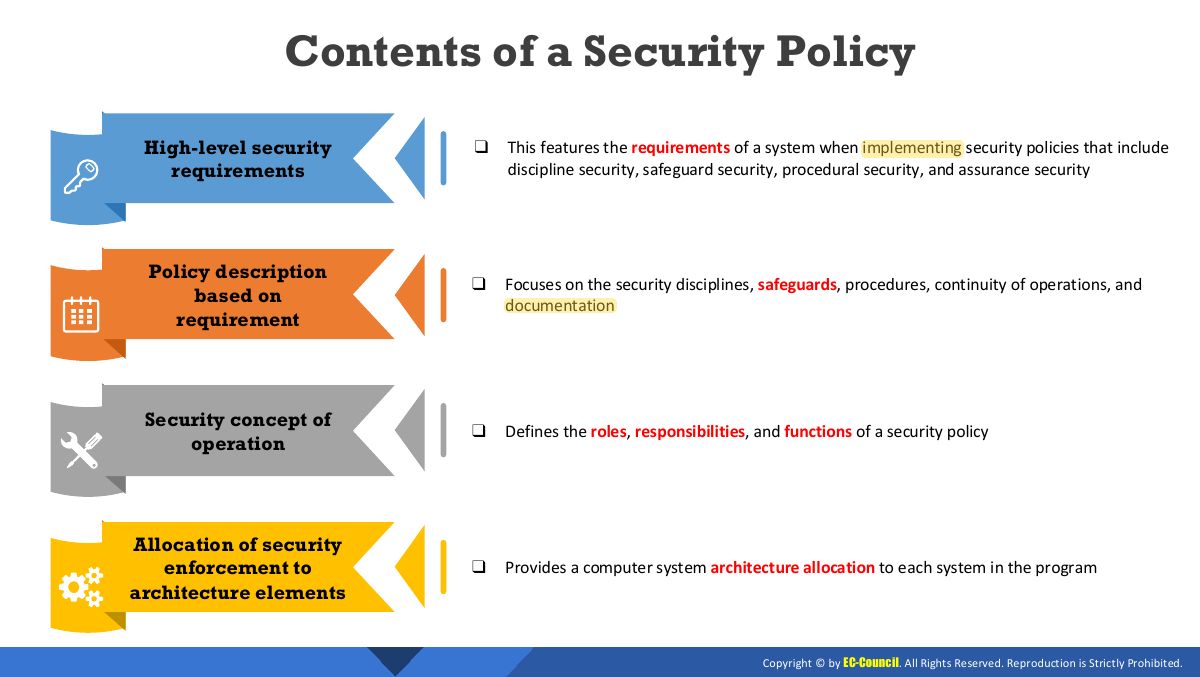
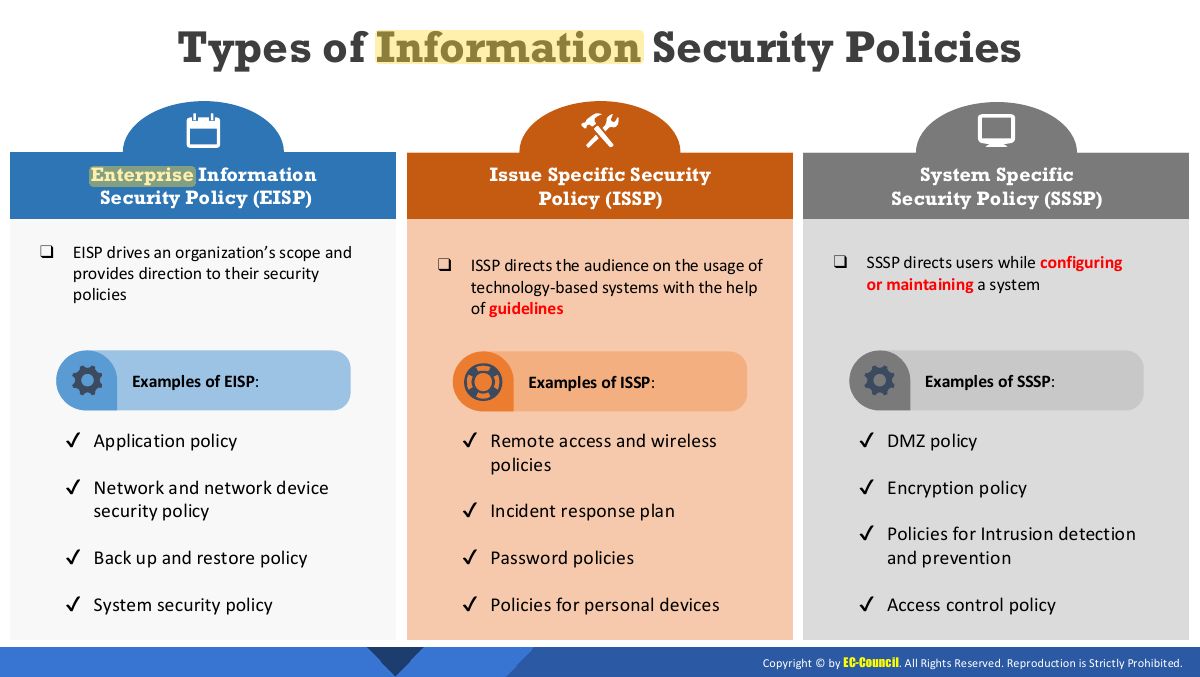
- Security policy: a document stating how the organization protects its assets; sets rules and responsibilities.
Exam weight ●●● High
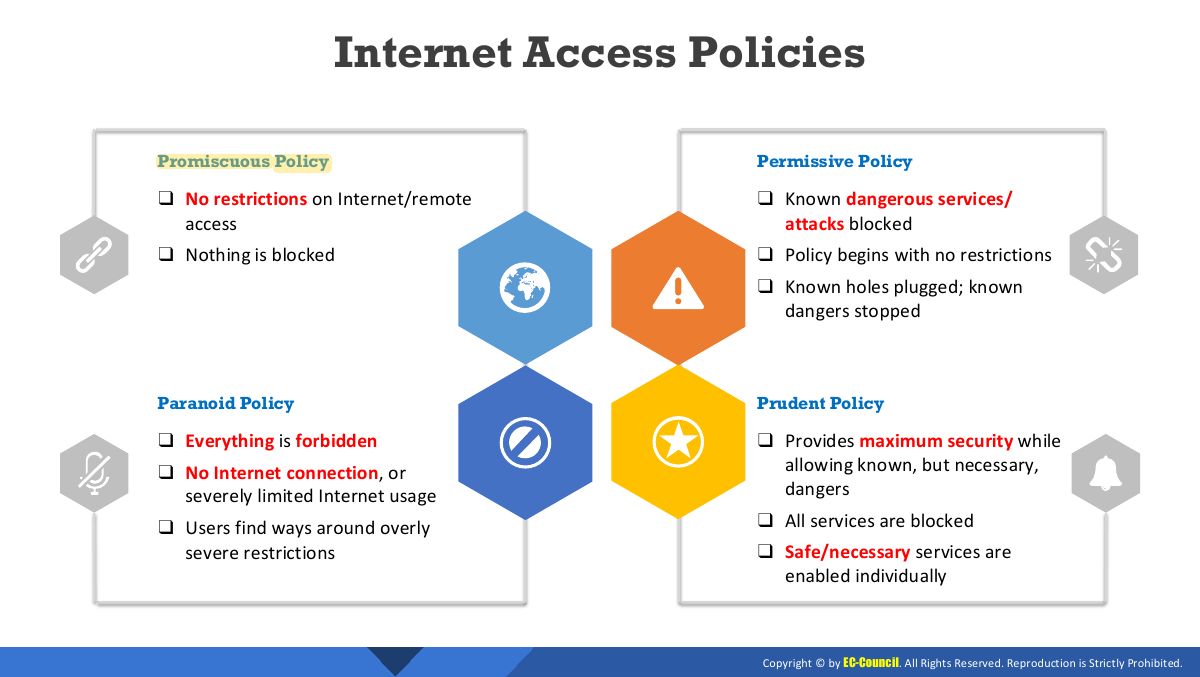
- Policy types by strictness: promiscuous (no restrictions), permissive (block known-bad), prudent (block most, allow needed), paranoid (block everything).
Exam weight ●○○ Low
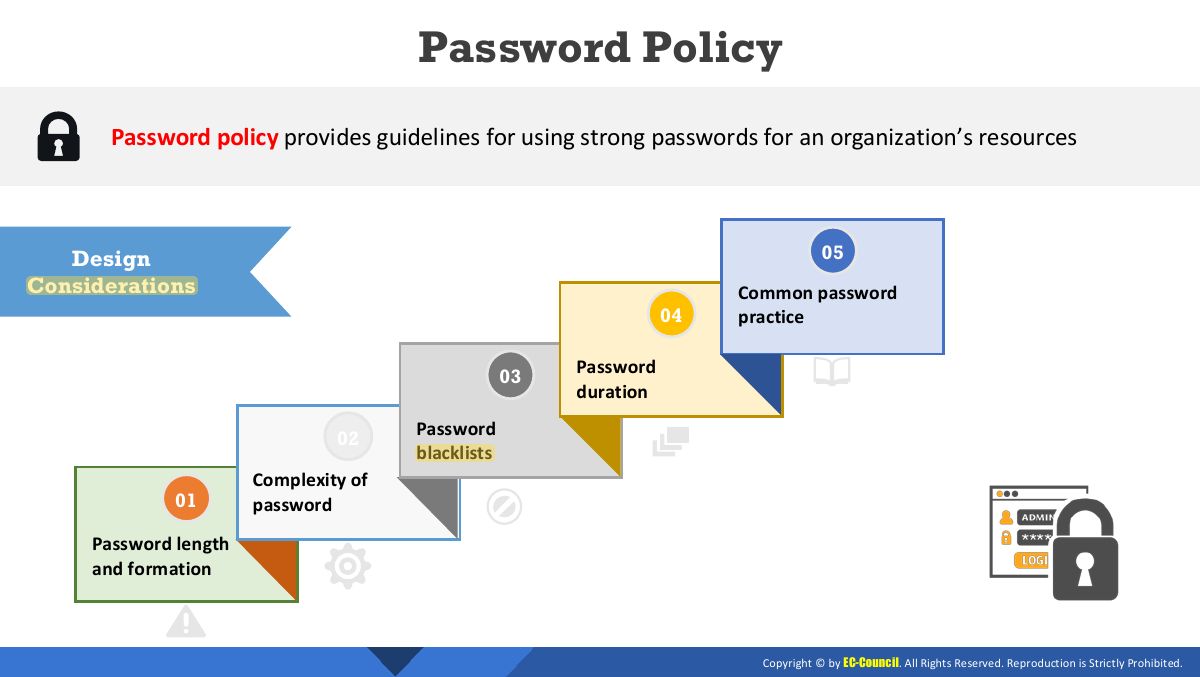
- Password policy: length, complexity, history, expiry, lockout.
Exam weight ●○○ Low
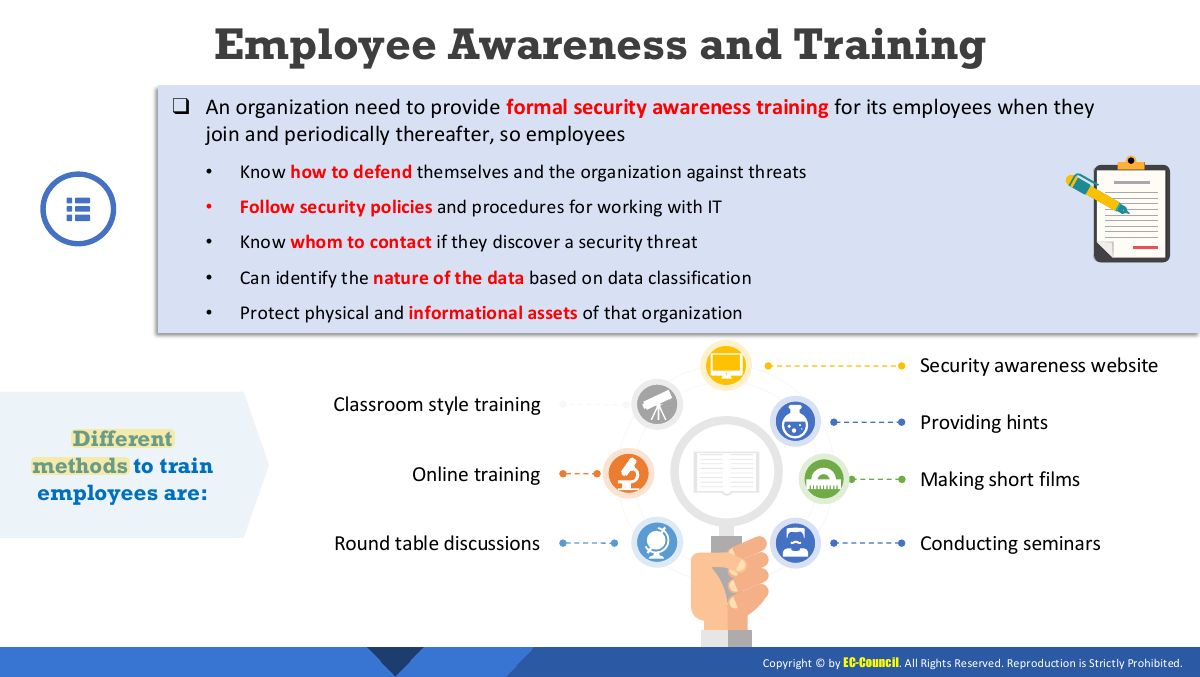
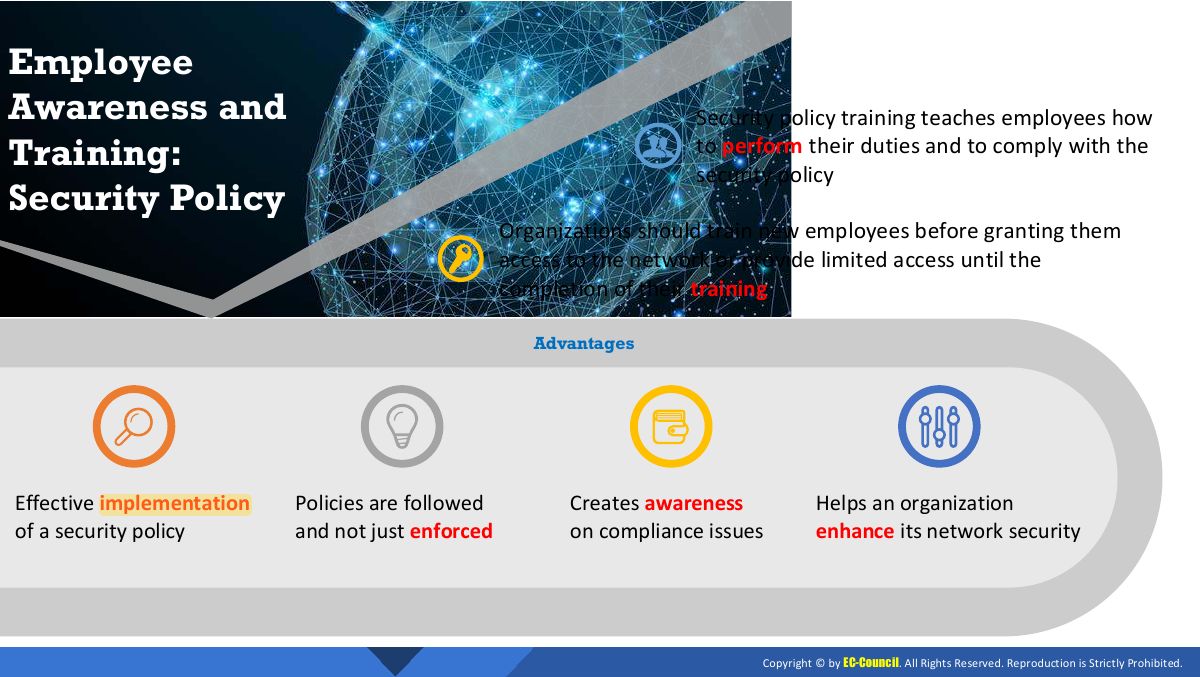
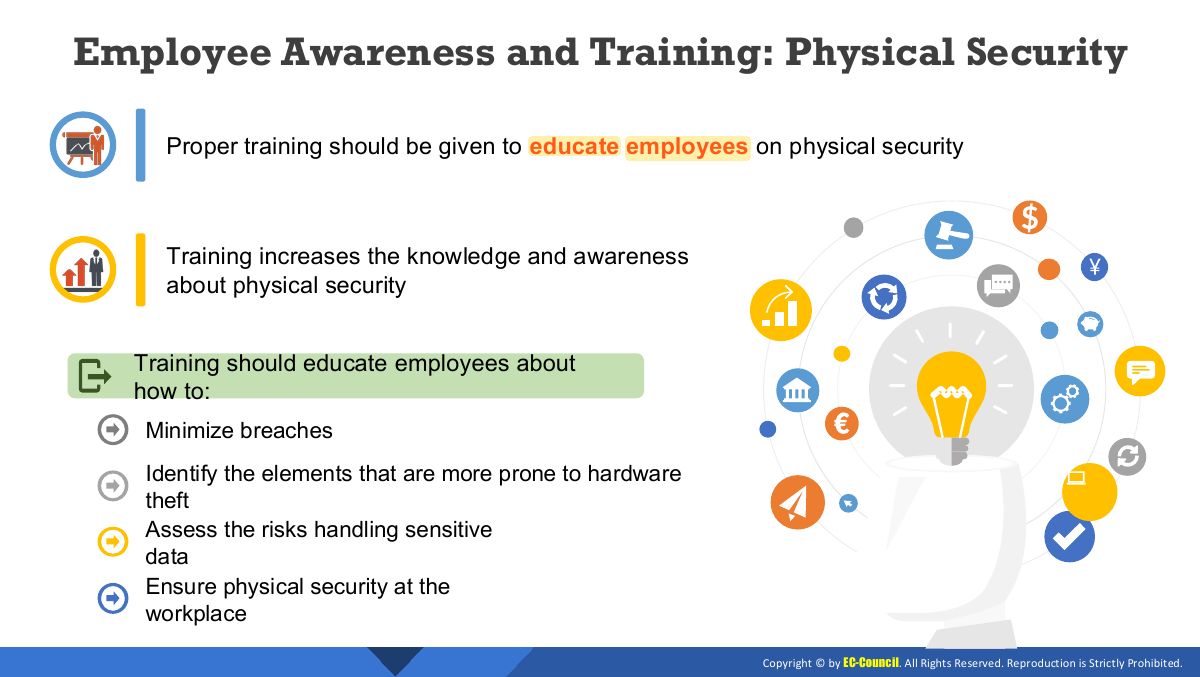
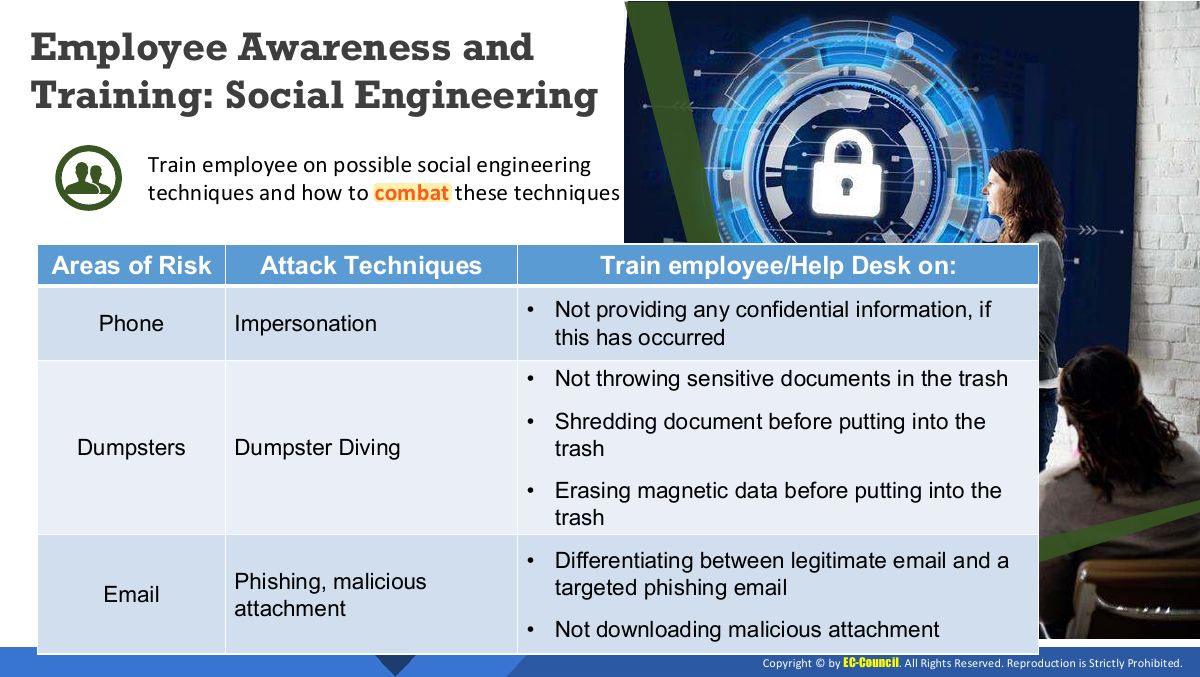
- Awareness training reduces social engineering and policy violations: people are the weakest link.
No slides match this filter.