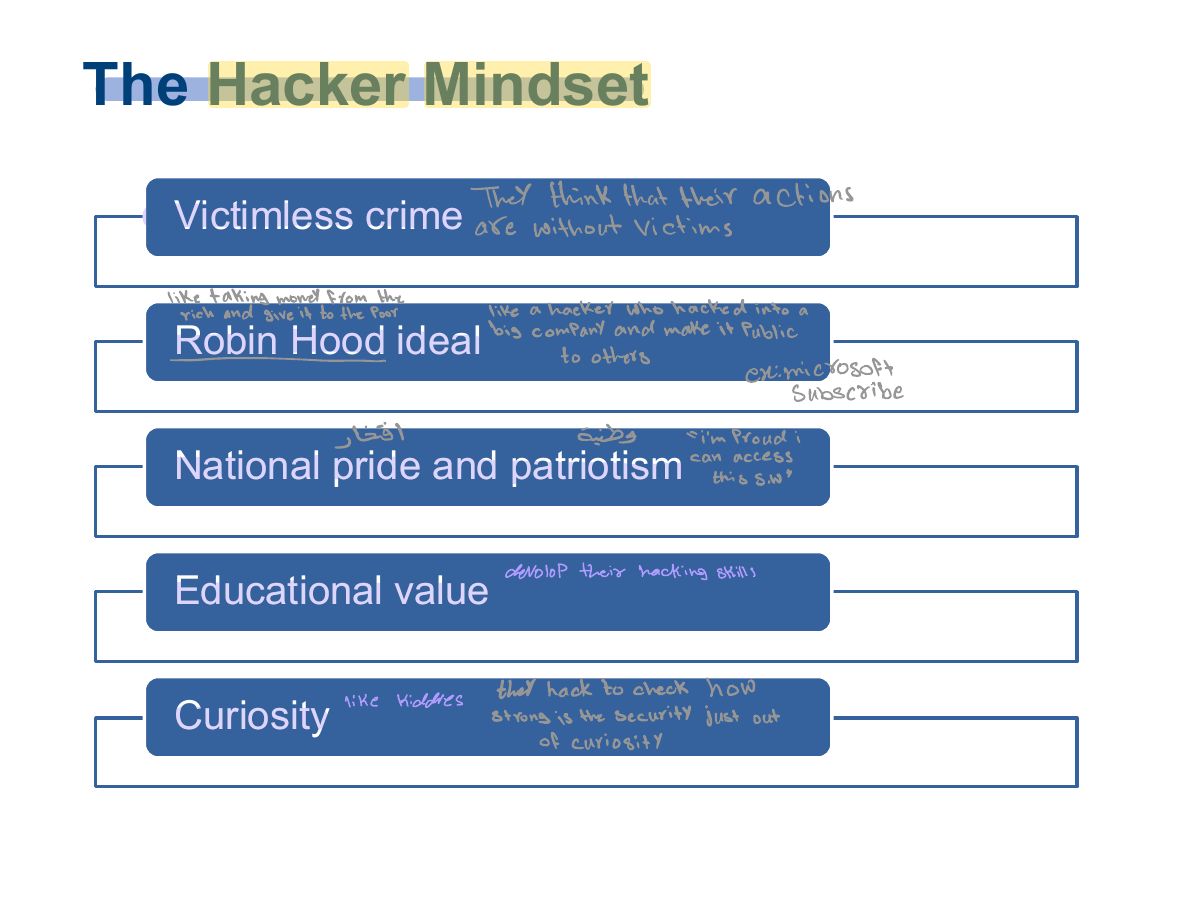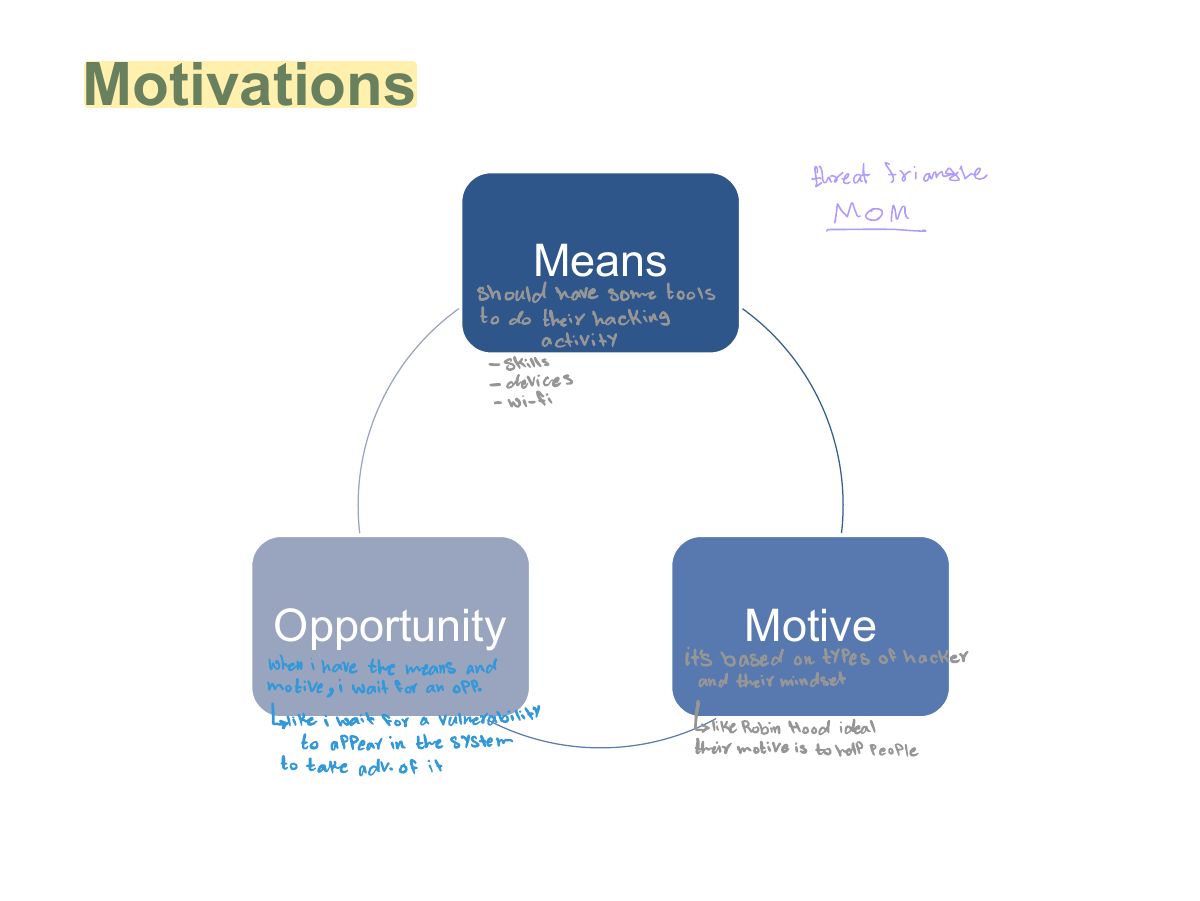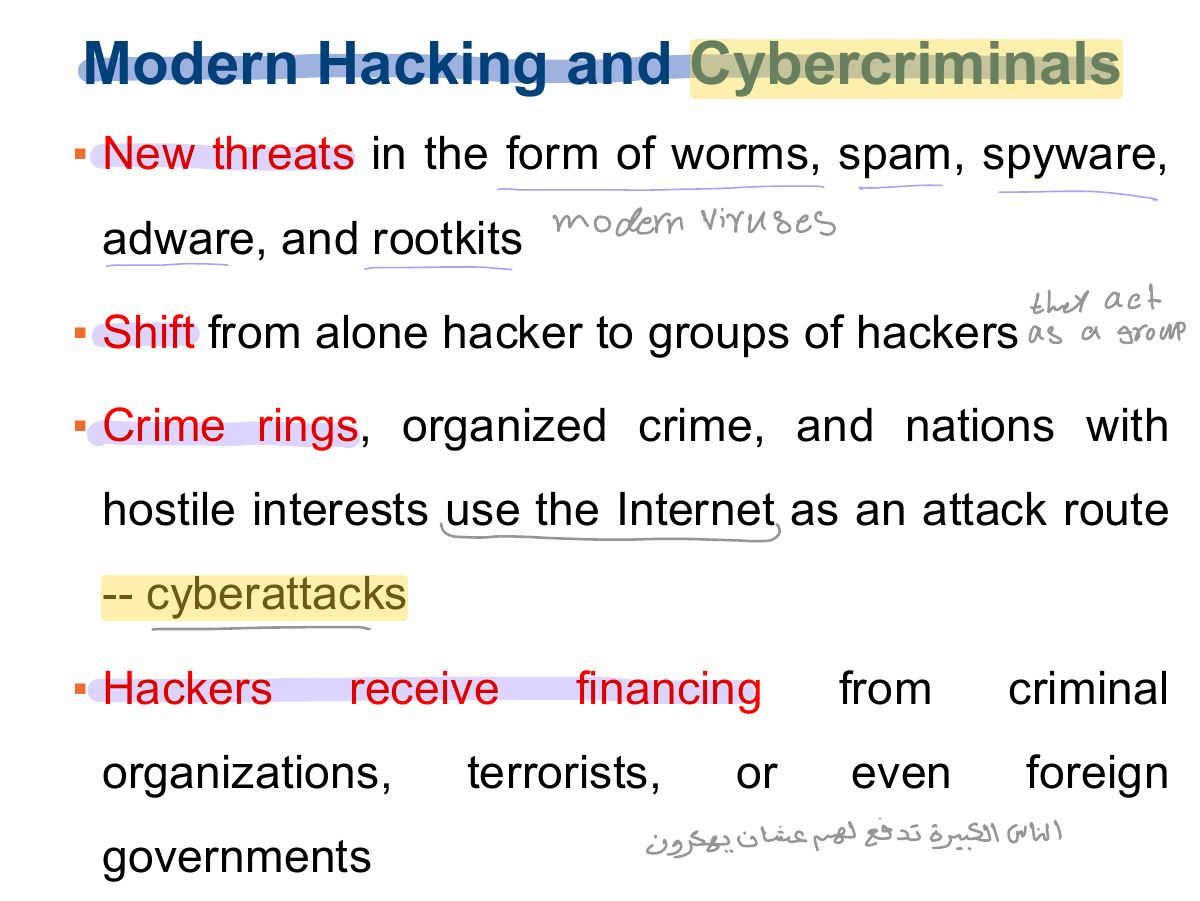
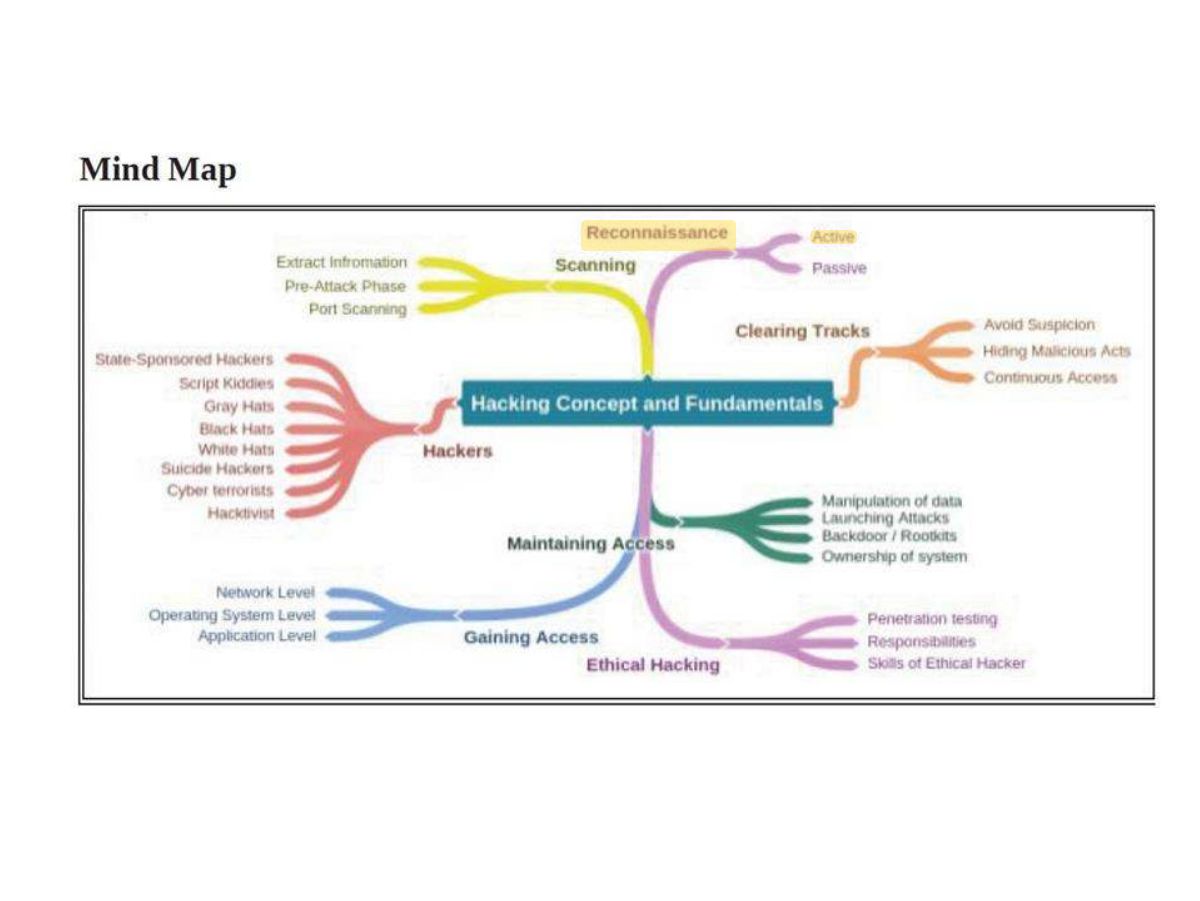
- Hat colours: black hat (malicious), white hat (authorized, ethical), gray hat (in between, may act without permission). Also script kiddies, hacktivists, suicide hackers, state-sponsored, cyber terrorists.
🎯 How this can come up · 1 question
A hacker who works with the owner’s permission to find weaknesses is a:
Correct: White hat.
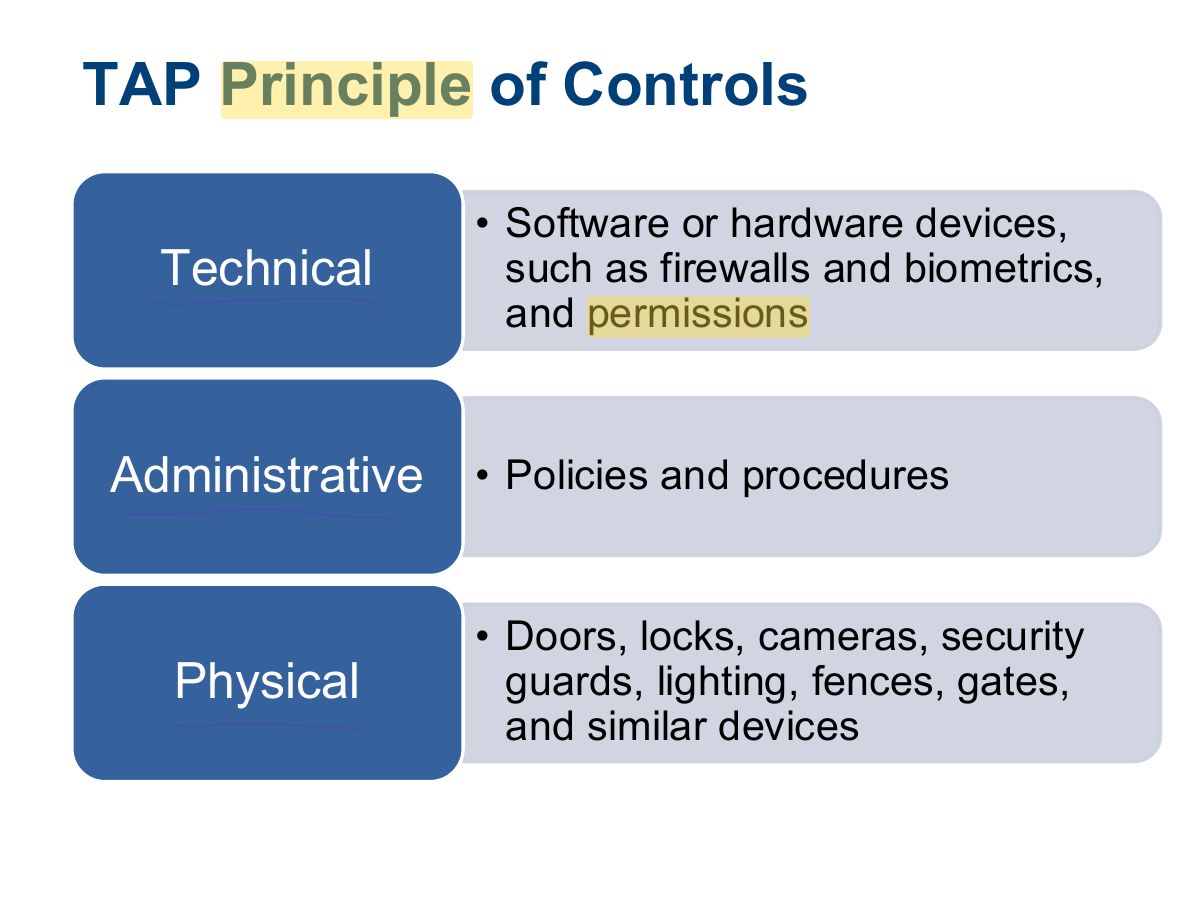
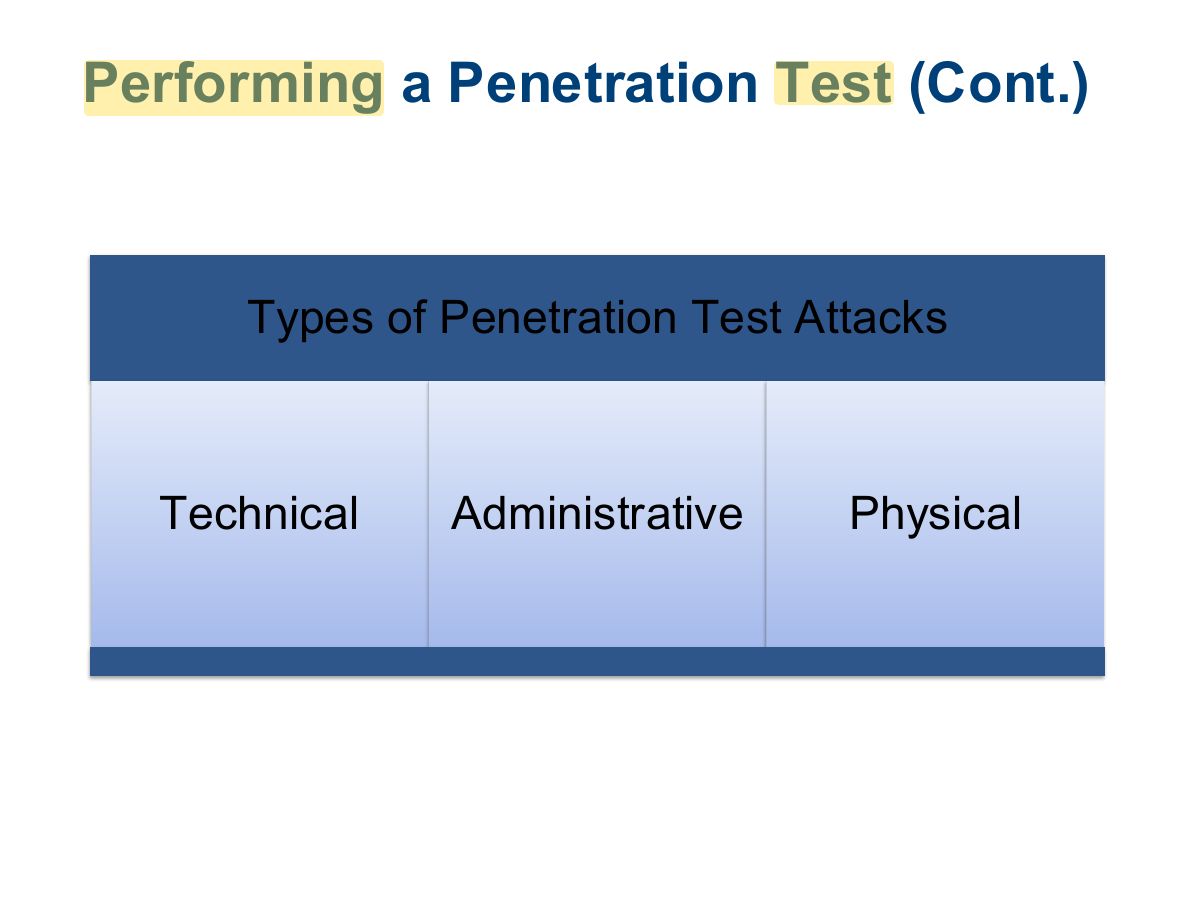
- TAP: controls are Technical, Administrative, Physical.
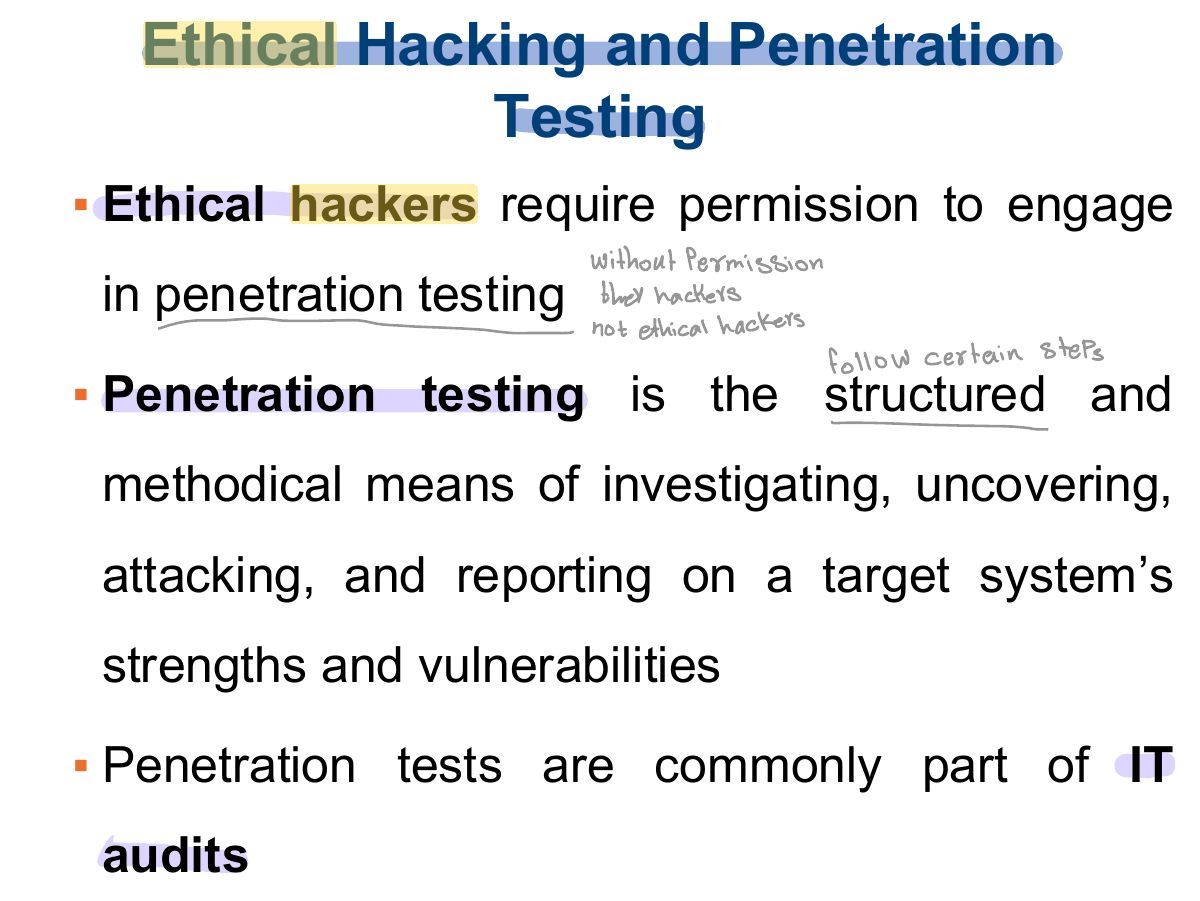
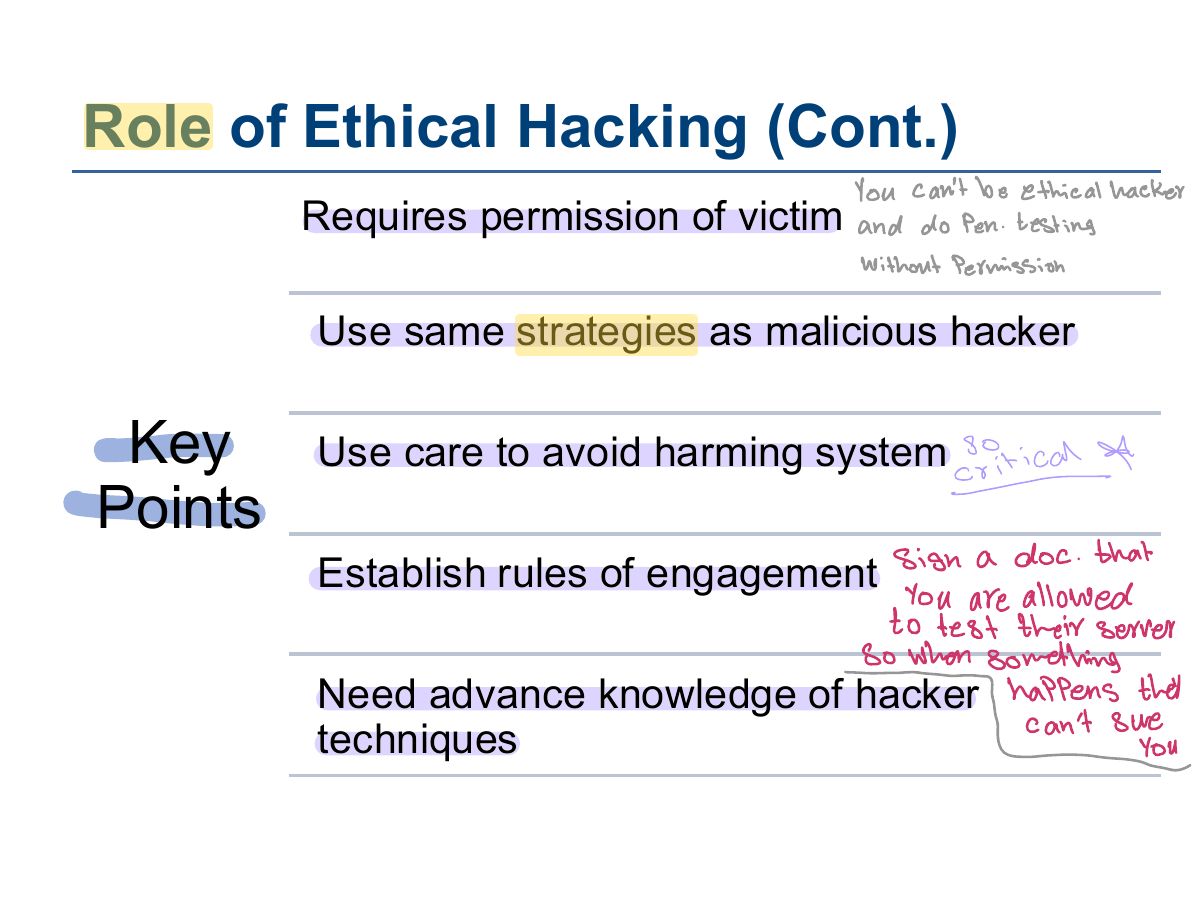
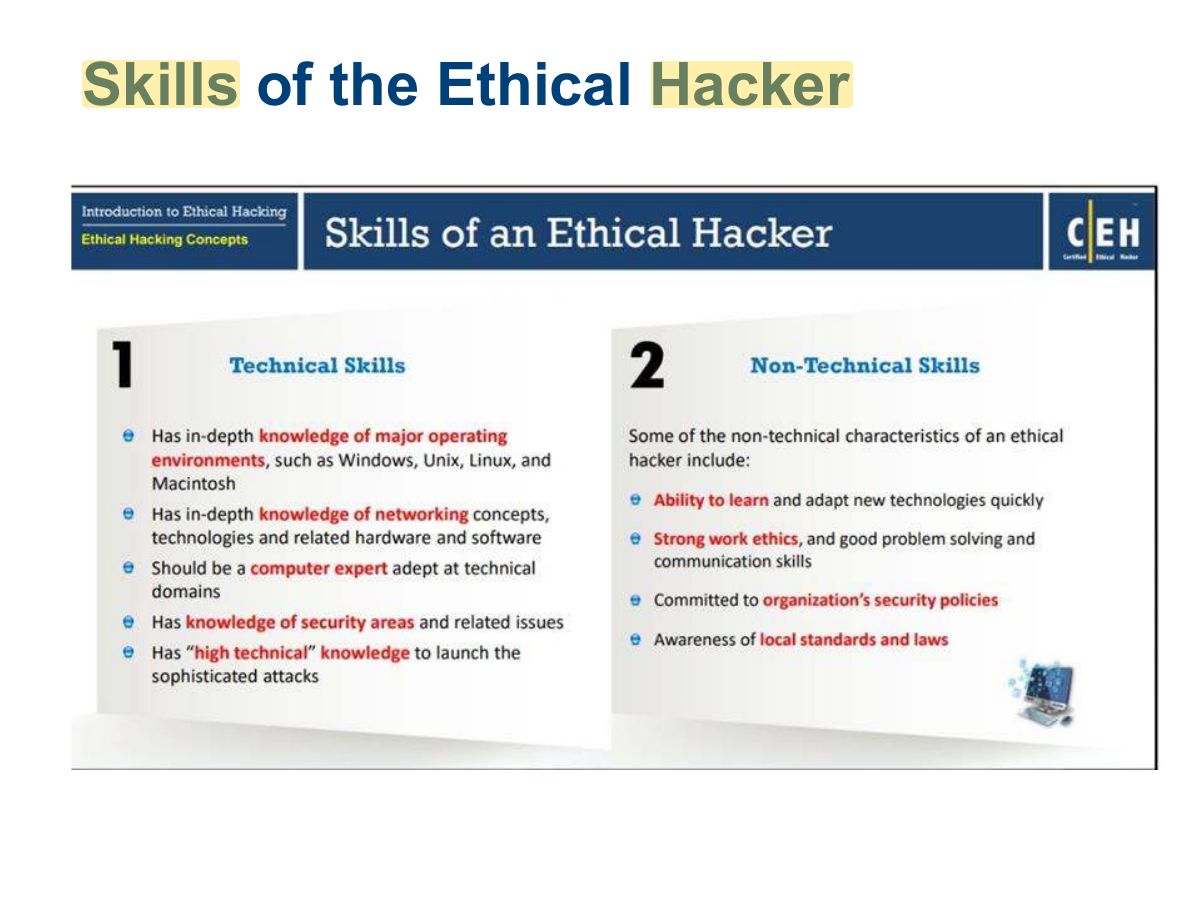
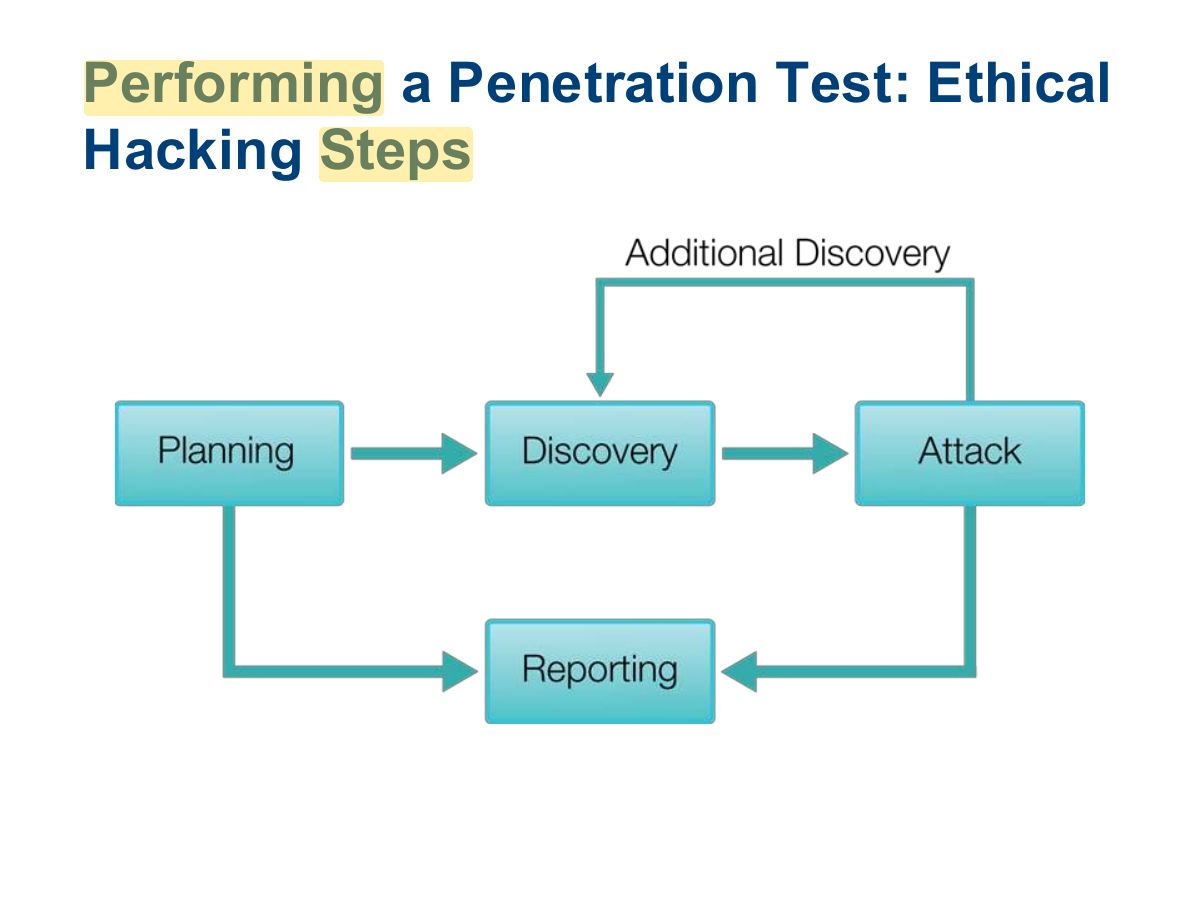
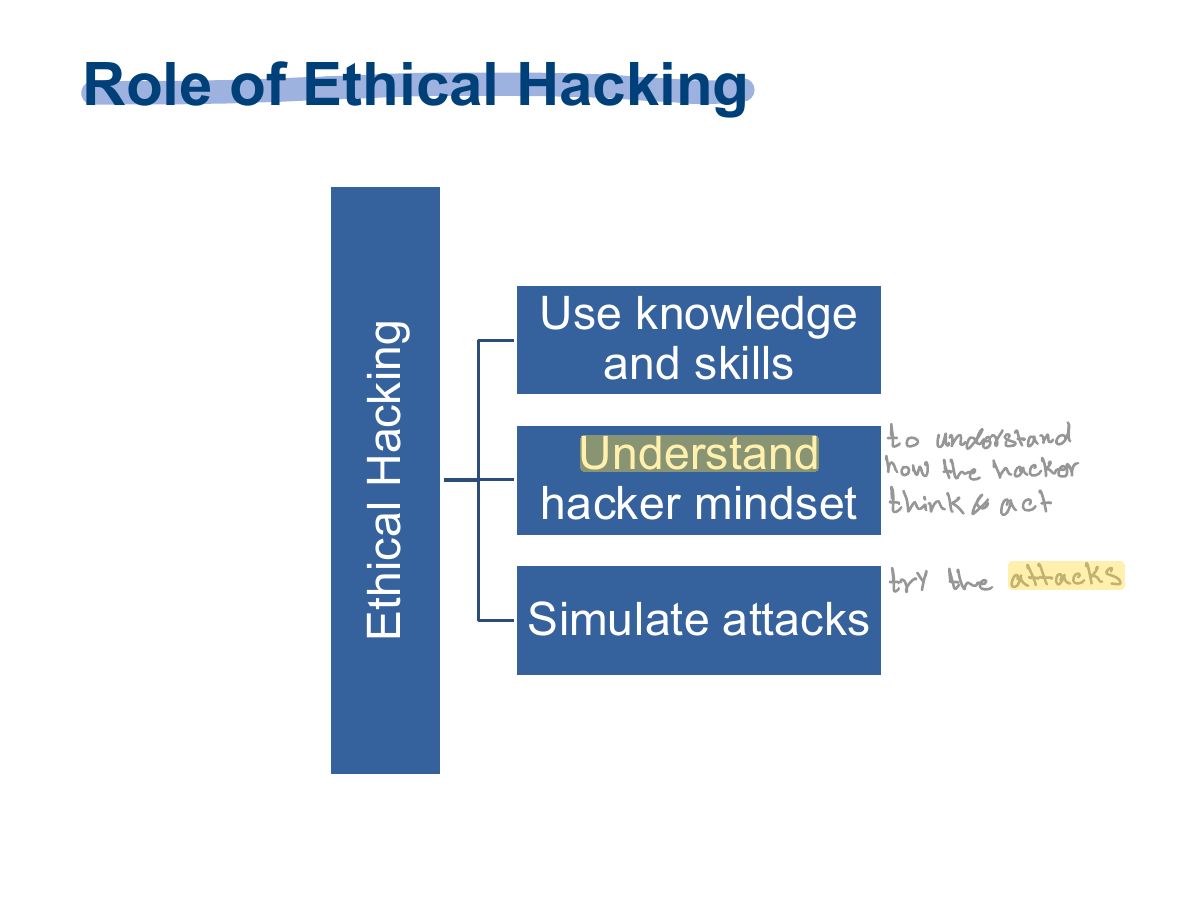
- Ethical hacking = authorized hacking to find and fix weaknesses before attackers do. A pen test simulates a real attack within an agreed scope.
🎯 How this can come up · 1 question
The key difference between an ethical hacker and a criminal hacker is permission (authorization).
True.
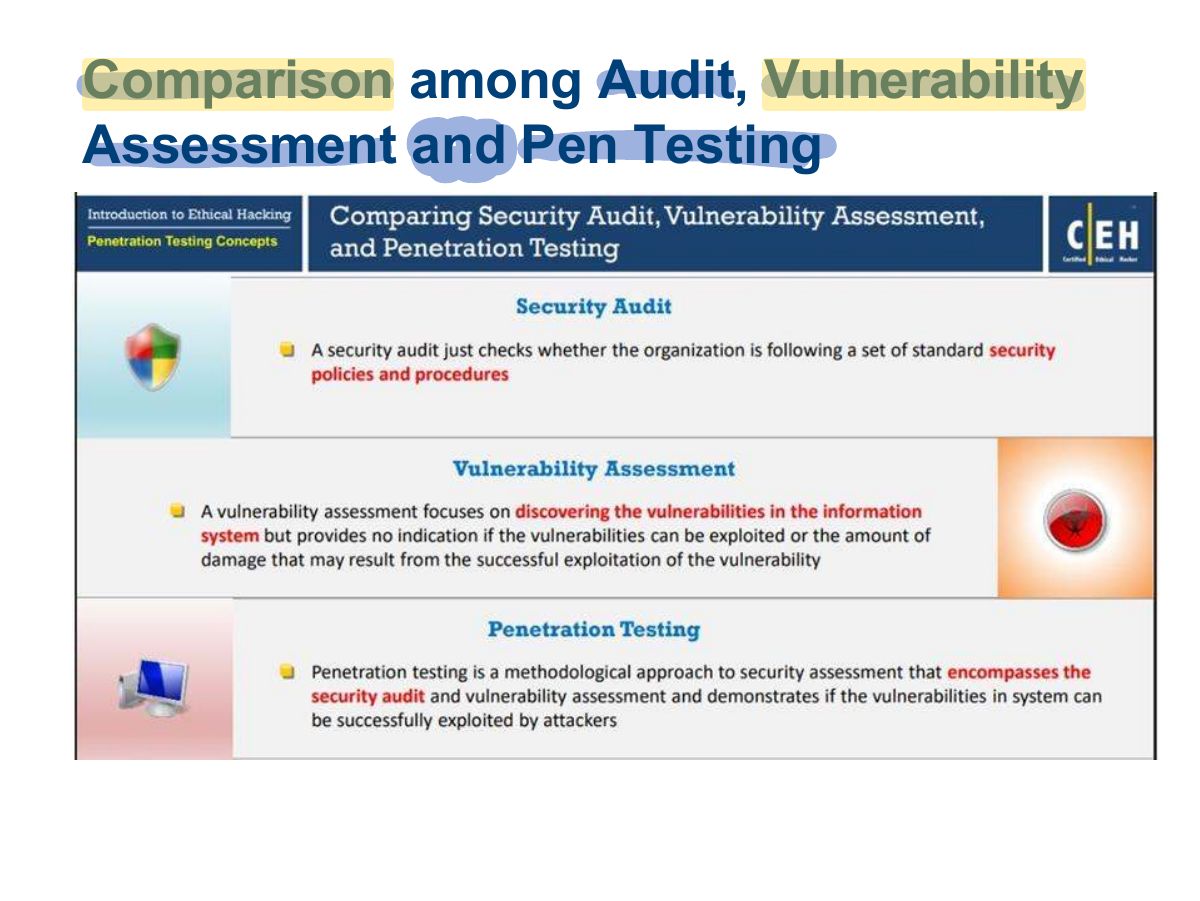
- Audit: checks compliance with a standard. Vulnerability assessment: finds and lists weaknesses. Pen test: actually exploits them to prove impact.
🎯 How this can come up · 1 question
Which activity actually exploits weaknesses to show their impact?
Correct: Penetration test.
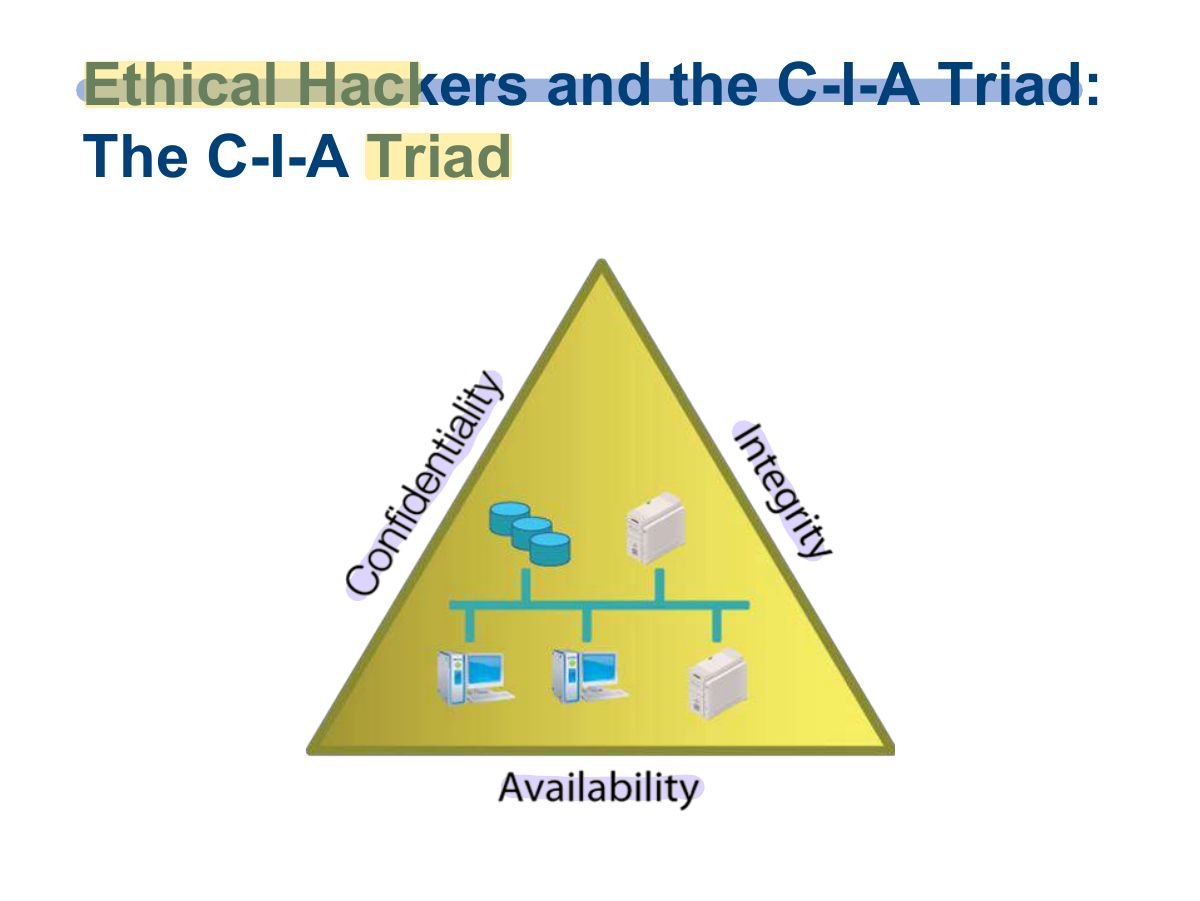
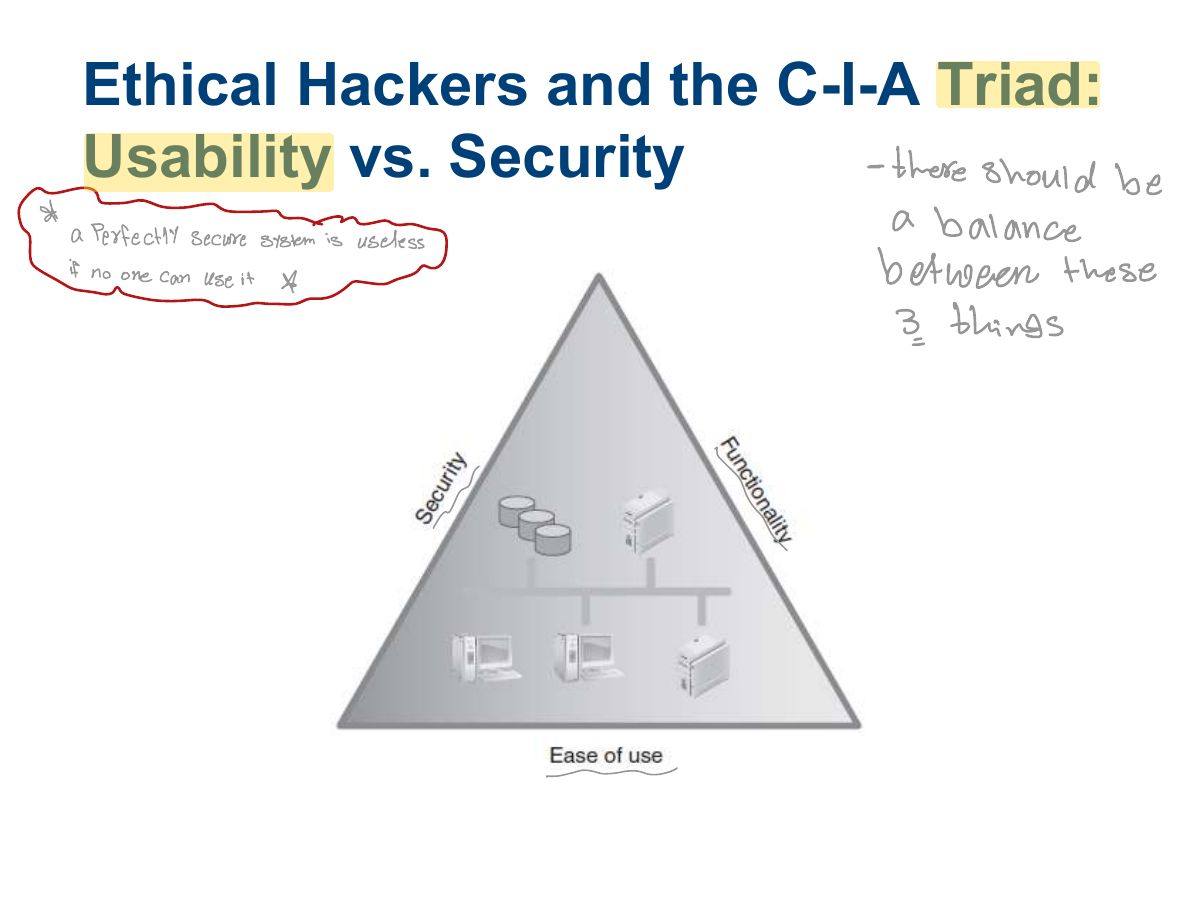
- Attacks map onto the CIA triad: disclosure (confidentiality), alteration (integrity), denial (availability), the DAD triad.
🎯 How this can come up · 1 question
A DoS attack targets:
Correct: Availability.
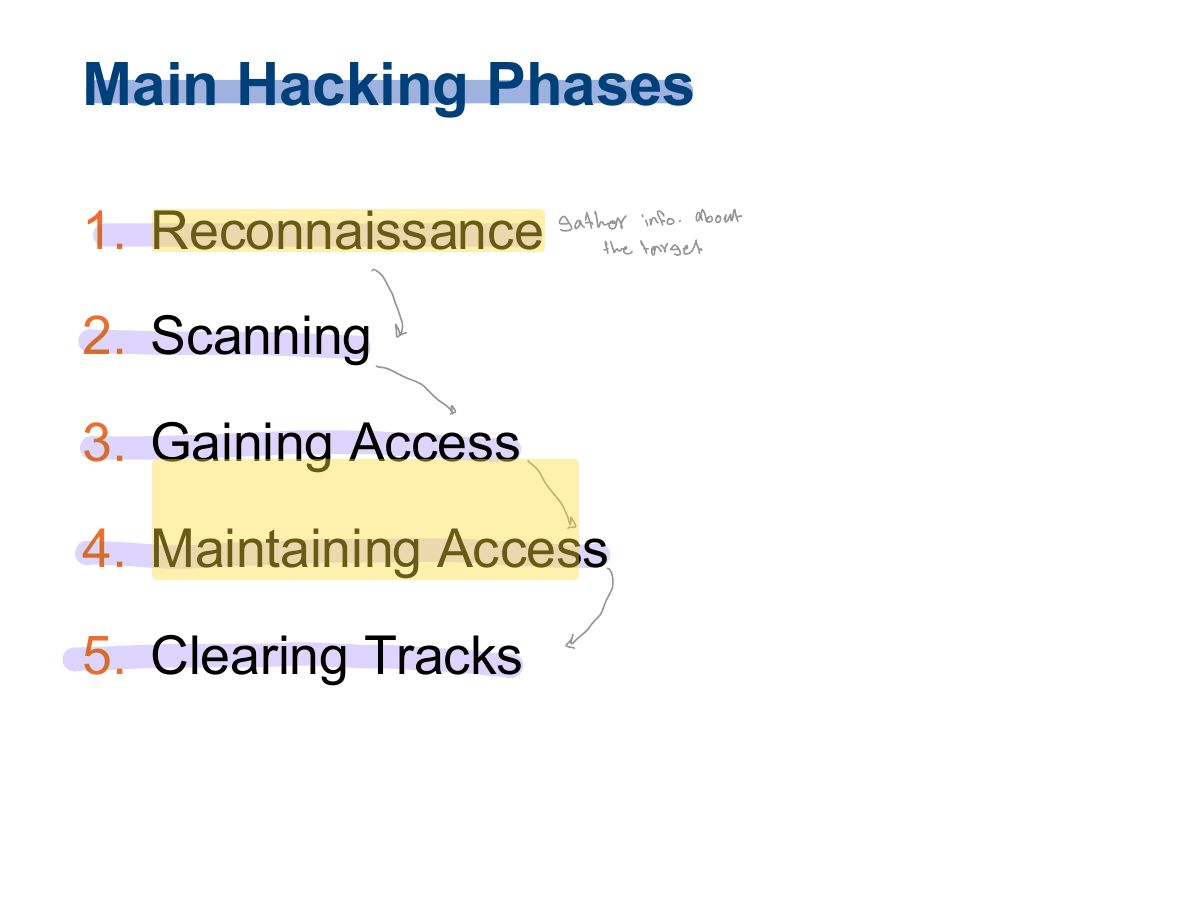
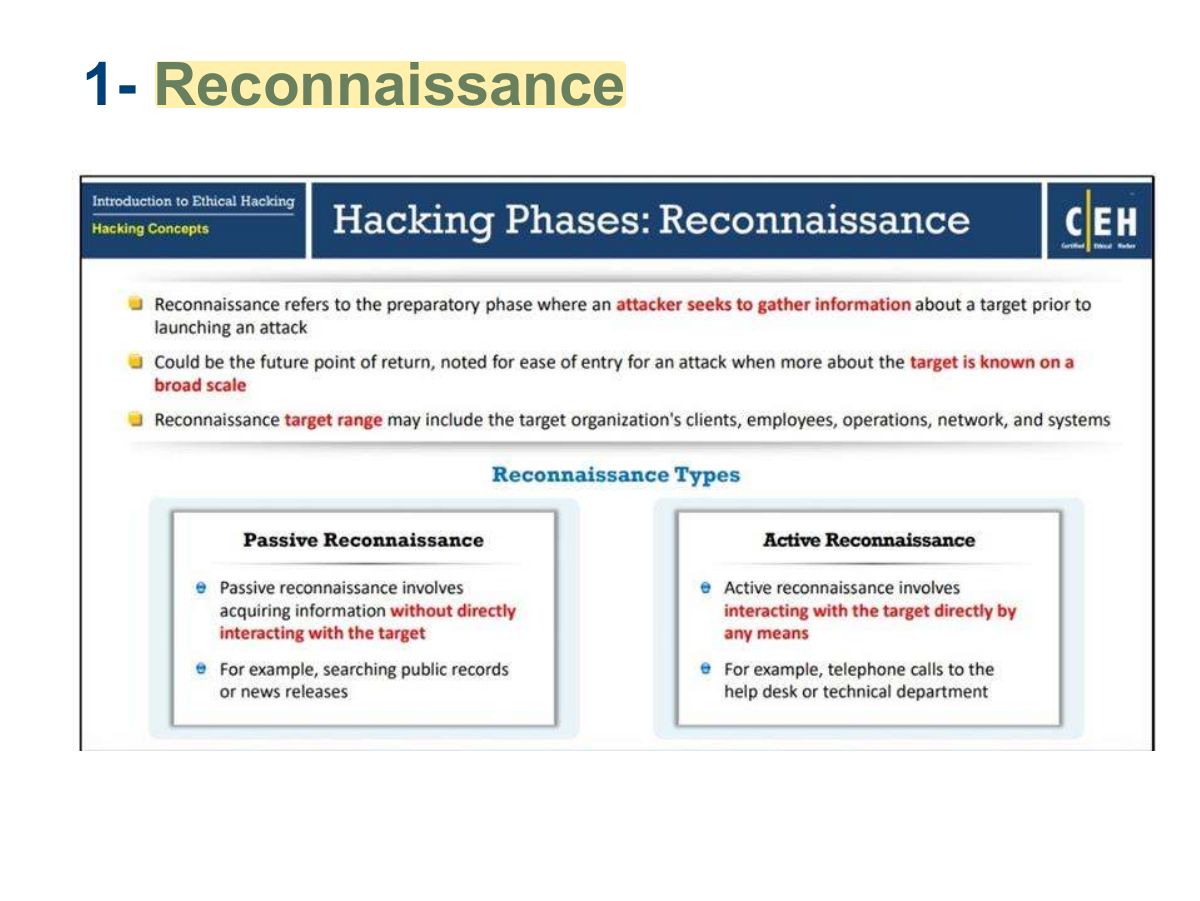
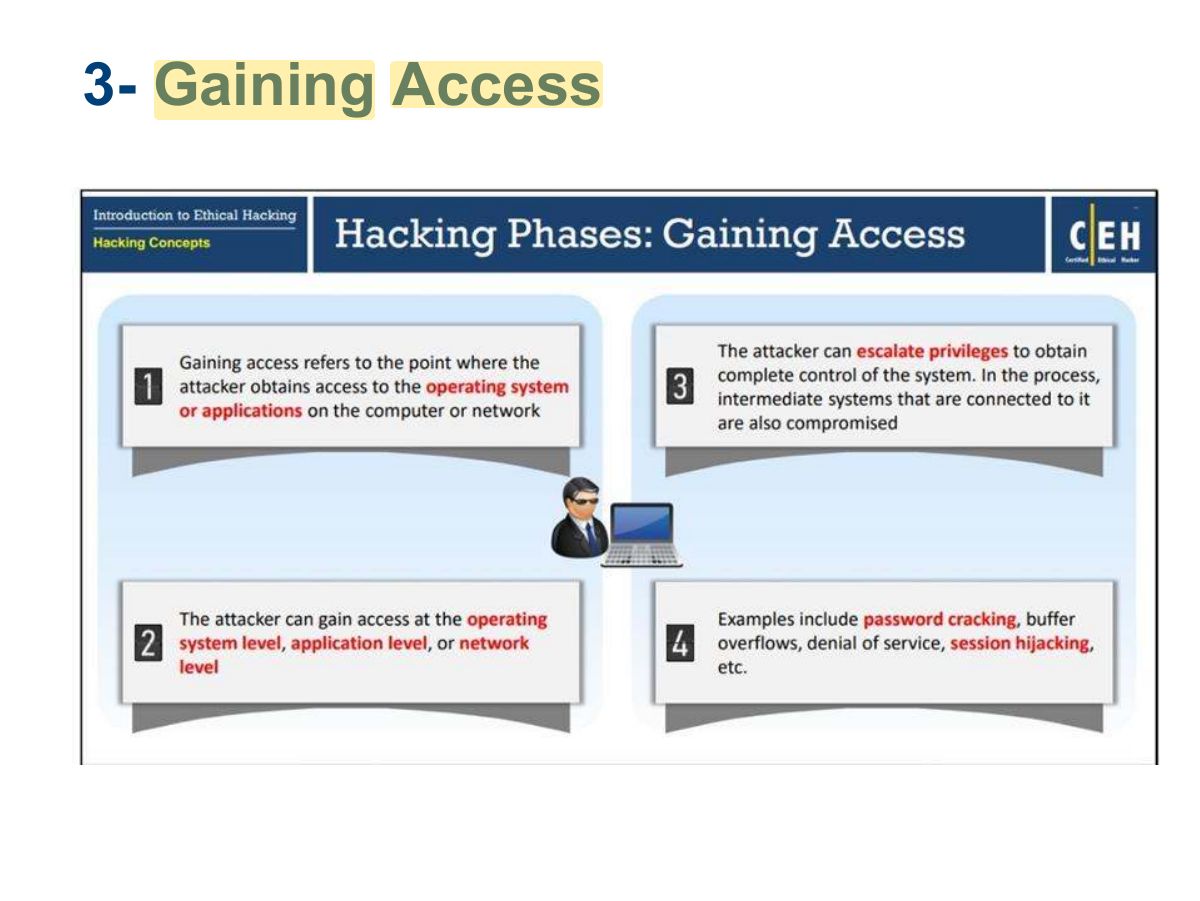
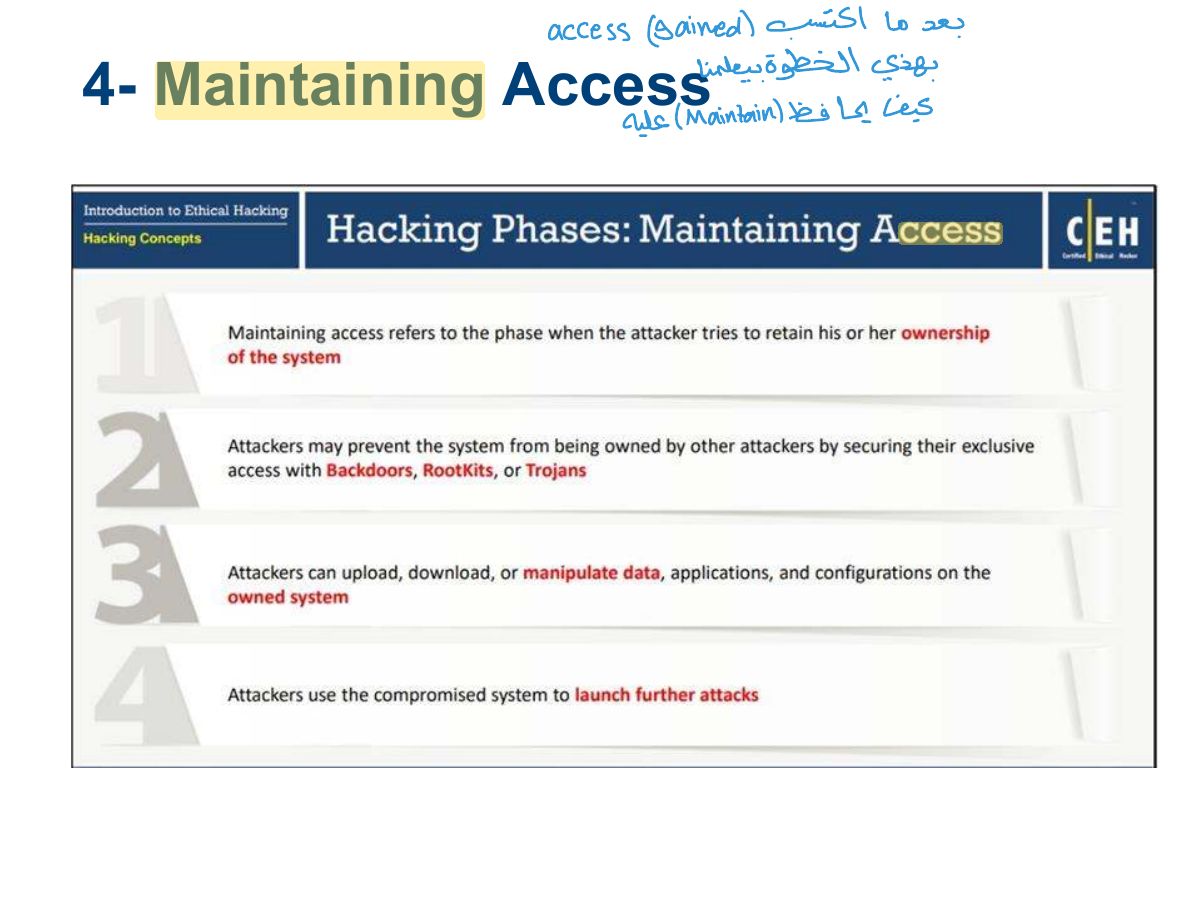
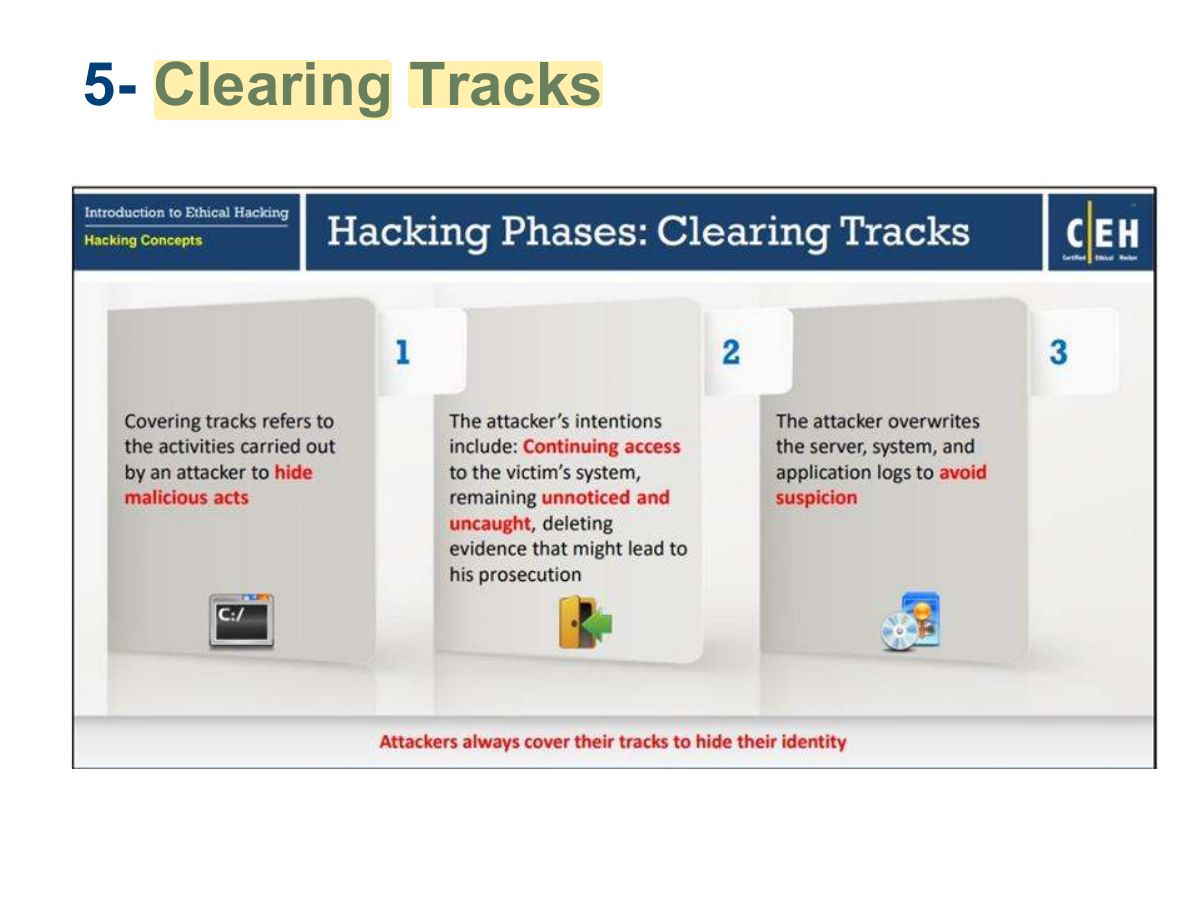
- Five phases: 1 Reconnaissance → 2 Scanning → 3 Gaining access → 4 Maintaining access → 5 Clearing tracks.
- Reconnaissance: gather information. Passive (no direct contact: public sources) vs. active (interacting with the target).
🎯 How this can come up · 1 question
Searching the target’s website and news articles without touching their systems is:
Correct: Passive reconnaissance.
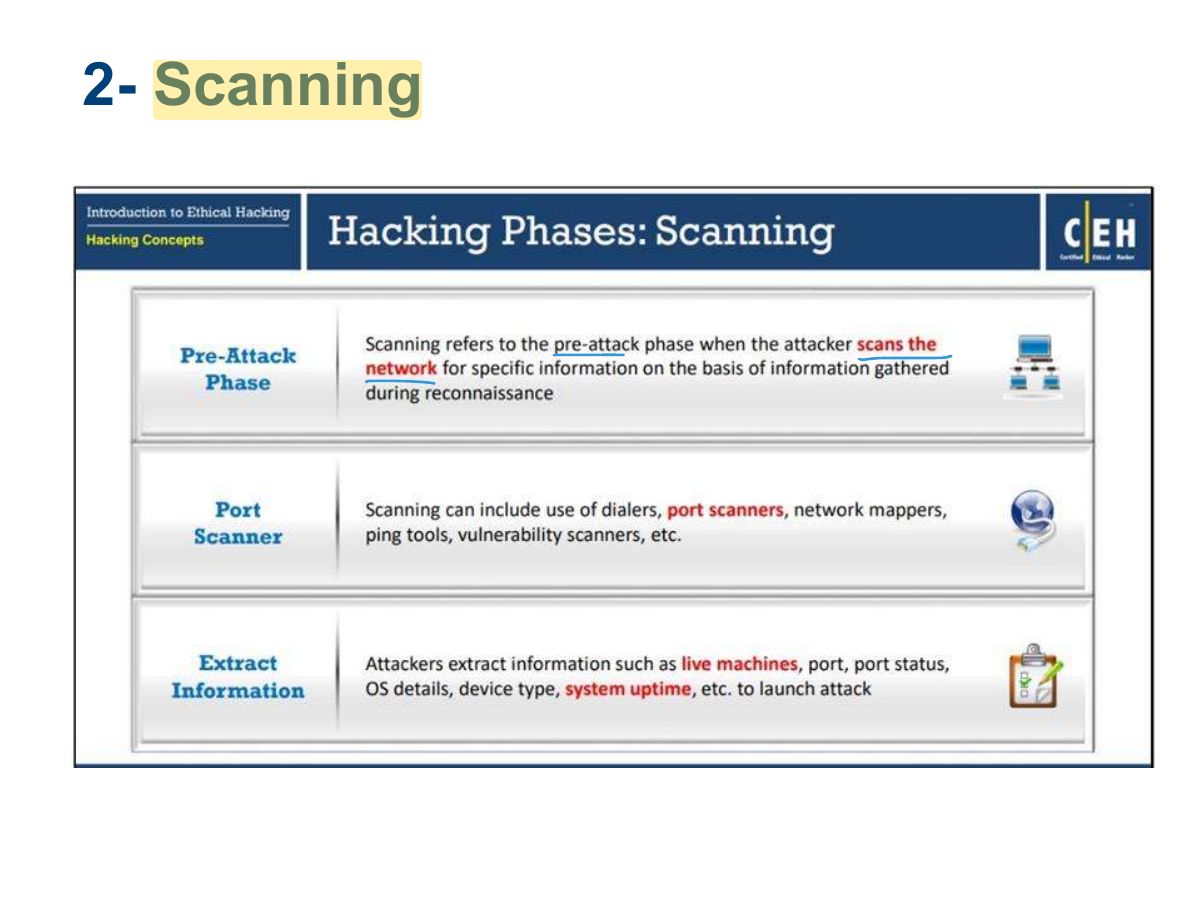
- Scanning: probe the network for live hosts, open ports, services and vulnerabilities.
- Gaining access: exploit a vulnerability (password cracking, buffer overflow, session hijacking…).
- Maintaining access: backdoors, rootkits, Trojans to come back later.
- Clearing tracks: delete logs, hide files, avoid detection.
🎯 How this can come up · 1 question
Deleting log entries happens in which phase?
Correct: Clearing tracks.
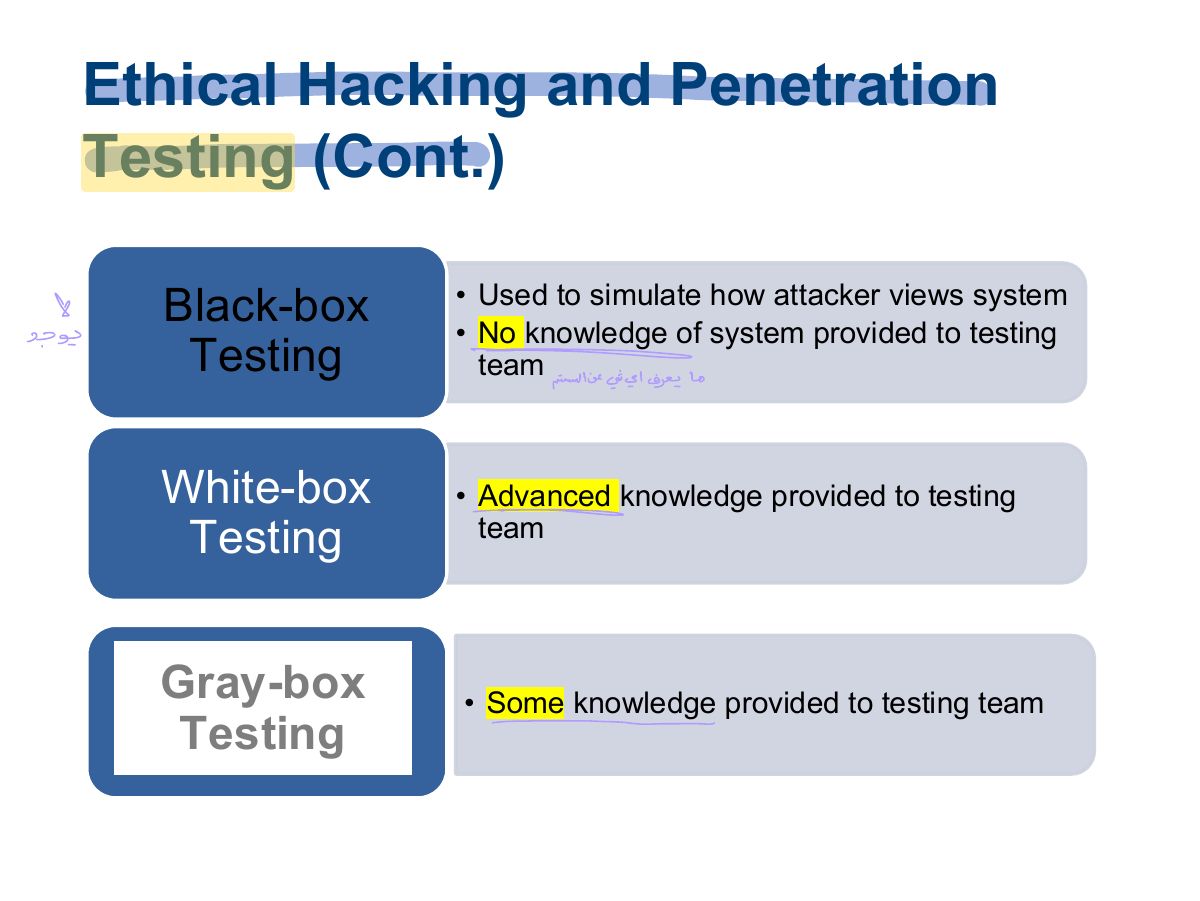
- Before testing: written permission (contract), scope, rules of engagement, NDA. Test types: black box (no knowledge), white box (full knowledge), gray box (partial).
🎯 How this can come up · 2 questions
A test where the tester has no prior knowledge of the target is:
Correct: Black-box.
An ethical hacker may start testing once the scope is agreed verbally.
False. Always get written authorization.
- Laws (e.g. computer-misuse acts) make unauthorized access a crime regardless of intent.
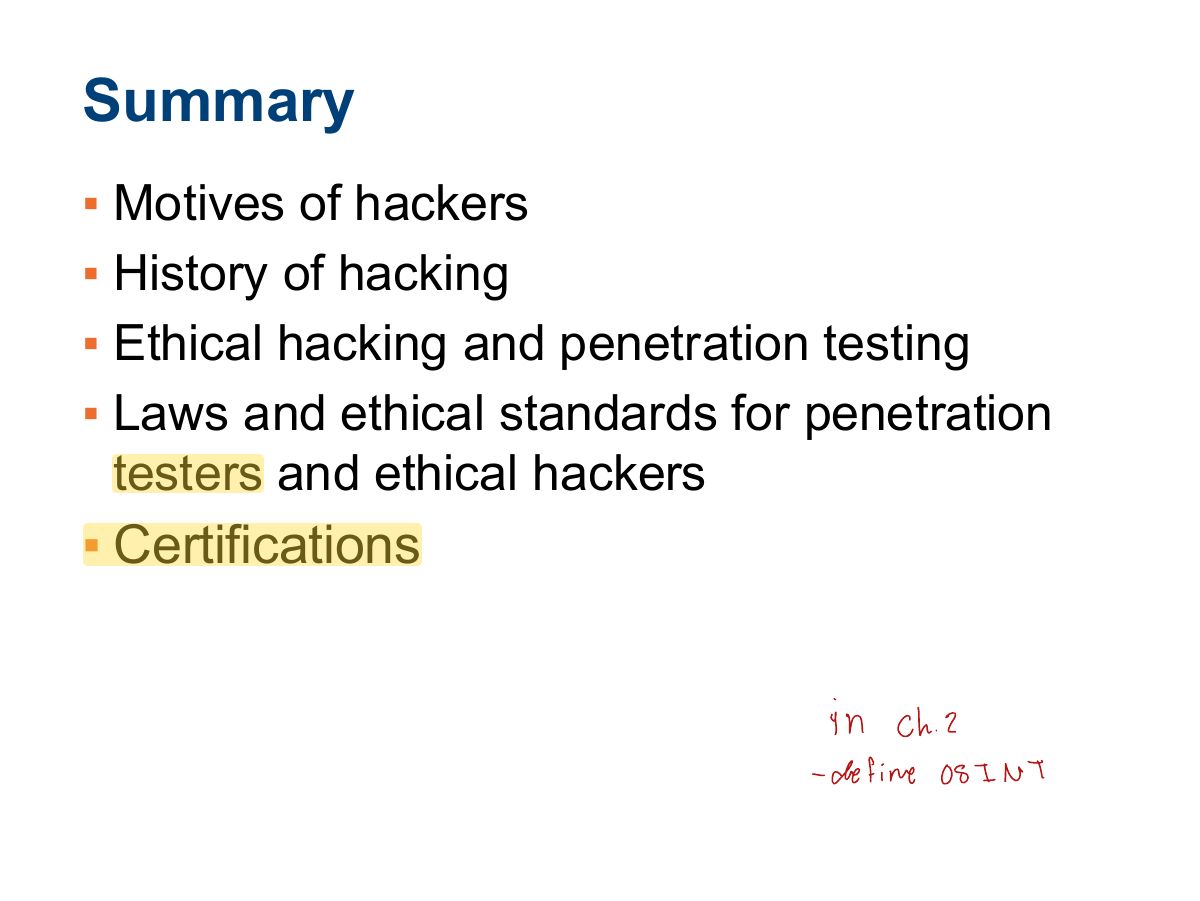
- Certifications: CEH, OSCP, GPEN, CompTIA PenTest+.
No slides match this filter.