CYS401 · Annotated SlidesChapter 9 — ICS/SCADA System Security
Chapter 9 · Annotated slides

ICS/SCADA System Security

Cyber-physical systems and industrial control: IT vs. OT, the Purdue model, the ICS/SCADA architecture (control center, HMI, MTU, PLCs and RTUs, communication network, field instruments), SCADA protocols, vulnerabilities, threats, the security objectives (availability first), security requirements, policies, and governance. (The Slides page lists this PDF under “Systems Architecture Security”; its content is ICS/SCADA.)

Slide text Study notes Highlight: key words Tips, tricks & traps Seen again elsewhere How it can come up

ICS/SCADA System Security for CPS

CYS401 · Chapter 9
1
Slide 2: CHAPTER OVERVIEW
Exam weight Low
  1. Overview: CPS → ICS/SCADA architecture → vulnerabilities and threats → objectives → requirements → governance.

INTRODUCTION TO ICS/SCADA SYSTEMS SECURITY

  • Cyber-physical systems CPSs are a various collection of information communication technology (ICT) and embedded microprocessors which are communicated to the physical world via sensors and actuators.
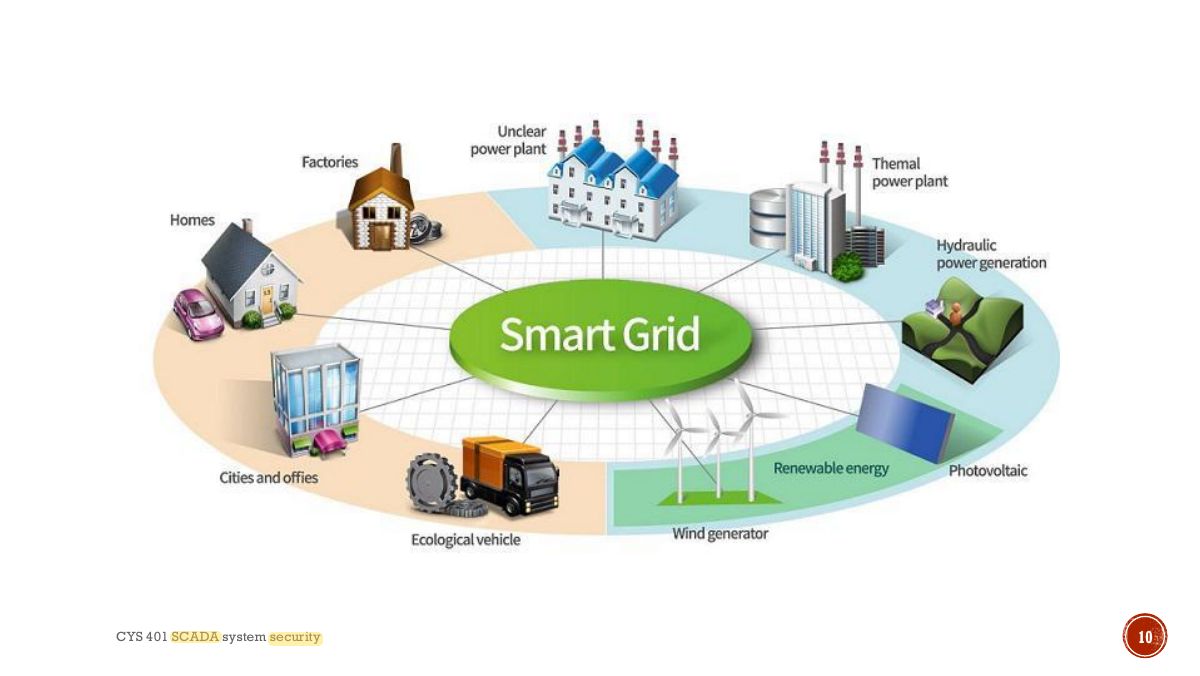
  • Applications of CPS: Smart Grid
  • ICS/SCADA: The remote activities of the CPS applications(smart grid’s) are monitored and controlled by specialized computing system called industrial control systems (ICSs) or super visory control and data acquisition (SCADA) systems (ICS/ SCADA).
  • Importance of ICS/SCADA security: It is very crucial to keep ICS/SCADA system safe and secure in order to prevent any cyber attack that causes a physical hazard to the CPS applications(smart grid), which might affect the human life, national safety, or economy.

CYS 401 SCADA system security

3
Exam weight Low
  1. Cyber-physical systems (CPS): ICT + embedded processors controlling physical processes (smart grid, water, transport, health).
Slide 4: INTRODUCTION TO ICS/SCADA SYSTEMS SECURITY
Exam weight Low
  1. More CPS: water treatment, oil and gas, manufacturing.
Slide 5: INTRODUCTION TO ICS/SCADA SYSTEMS SECURITY
Exam weight Medium
  1. ICS monitors and controls critical infrastructure; it includes SCADA and DCS.
🎯 How this can come up · 1 question
MCQ

Which term is the umbrella that includes SCADA and DCS?

Slide 6: IT VS OT ENVIRONMENTS
Exam weight High
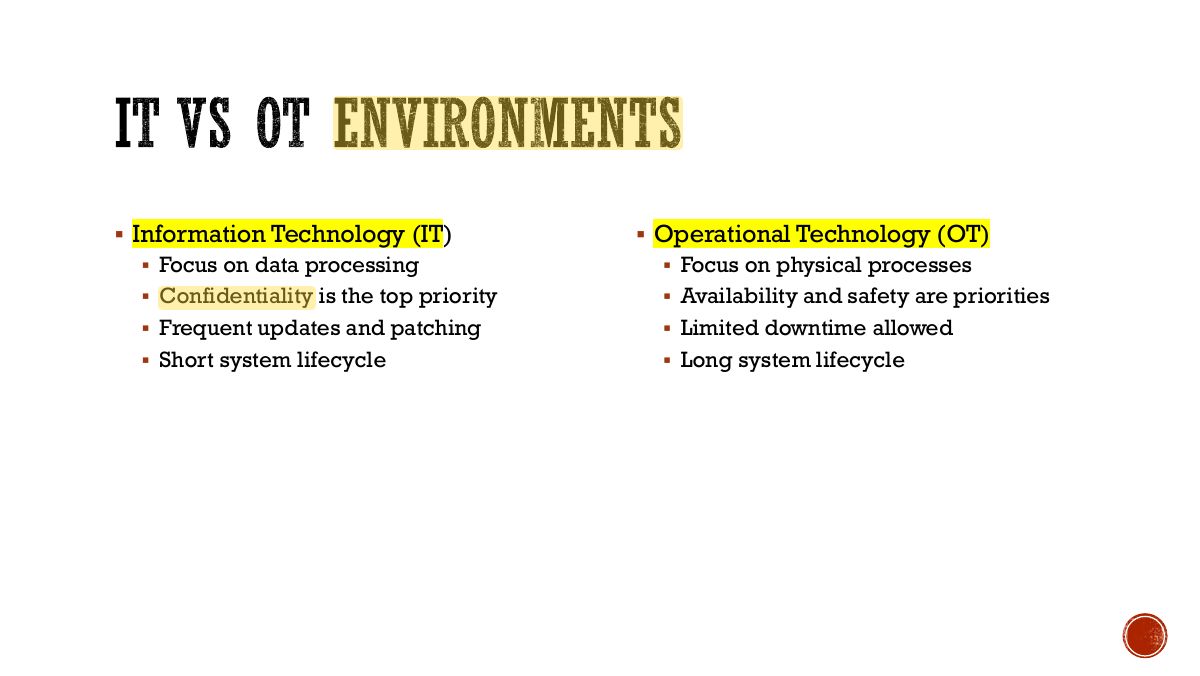
  1. IT vs. OT: IT protects data (confidentiality first); OT controls physical processes (availability and safety first, legacy, long life).
Exam trapIn OT/ICS the priority is AVAILABILITY, then integrity, then confidentiality (A-I-C), the reverse of typical IT.
🎯 How this can come up · 1 question
MCQ

In ICS/SCADA, the top security objective is usually:

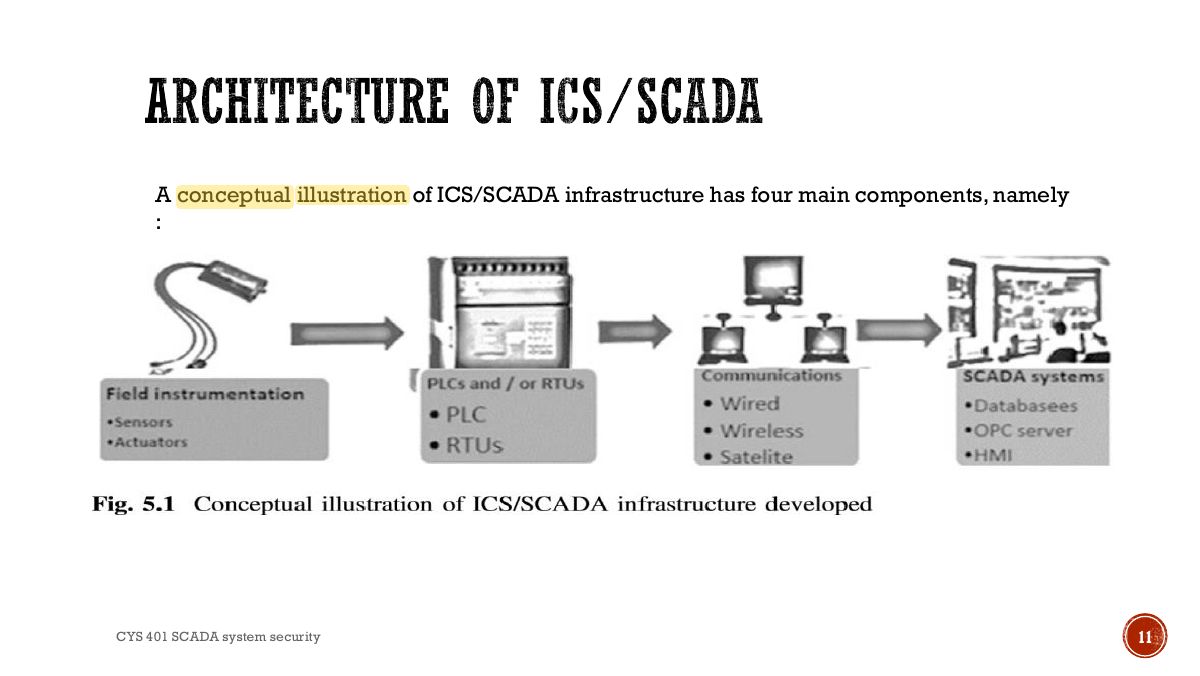
▪ Components of ICS/SCADA : it is composed of computers, networks, and

embedded devices which work together to monitor, manage, and control vital processes in various industrial and critical infrastructure areas such as oil and power management.

This combination consists mainly of:

  • Field instrumentation (Sensors and Actuators)
  • programmable logic controllers (PLCs) and/or remote terminal unit (RTUs),
  • communications networks, and
  • ICS/SCADA host software (Human-Machine Interface (HMI)) CYS 401 SCADA system security
7
Exam weight Low
  1. ICS/SCADA = computers, networks and embedded devices monitoring and controlling industrial processes.
Slide 8: PURDUE ENTERPRISE REFERENCE ARCHITECTURE
Exam weight Medium
  1. Purdue model: level 0 physical process, 1 sensors/actuators/controllers, 2 supervisory (HMI), 3 operations, 4–5 enterprise IT.
🎯 How this can come up · 1 question
MCQ

In the Purdue model, sensors and actuators sit at:

Slide 9: INTRODUCTION TO ICS/SCADA SYSTEMS SECURITY
Exam weight Low
  1. Example: a smart grid’s field instruments controlled remotely through SCADA.
Slide 10: Slide 10
Exam weight Low
  1. SCADA overview figure.
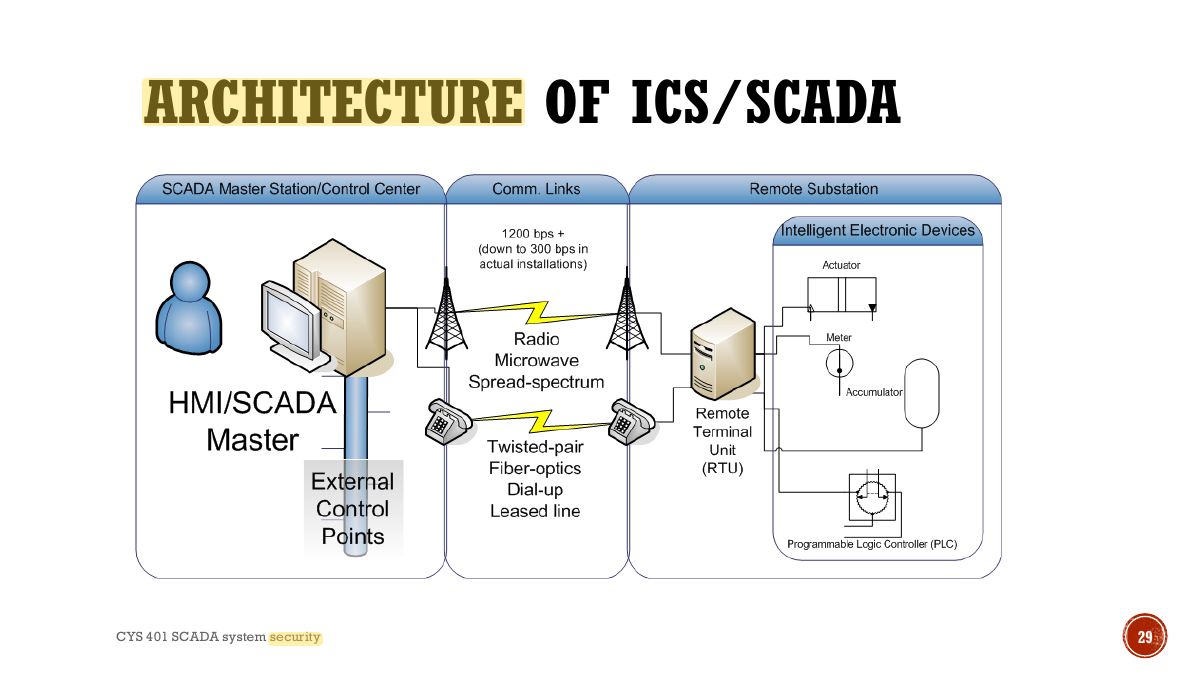
Slide 11: ARCHITECTURE OF ICS/SCADA
Exam weight Low
  1. Four main components: control center, communication network, PLCs/RTUs, field instruments.
Slide 12: ARCHITECTURE OF ICS/SCADA
Exam weight Low
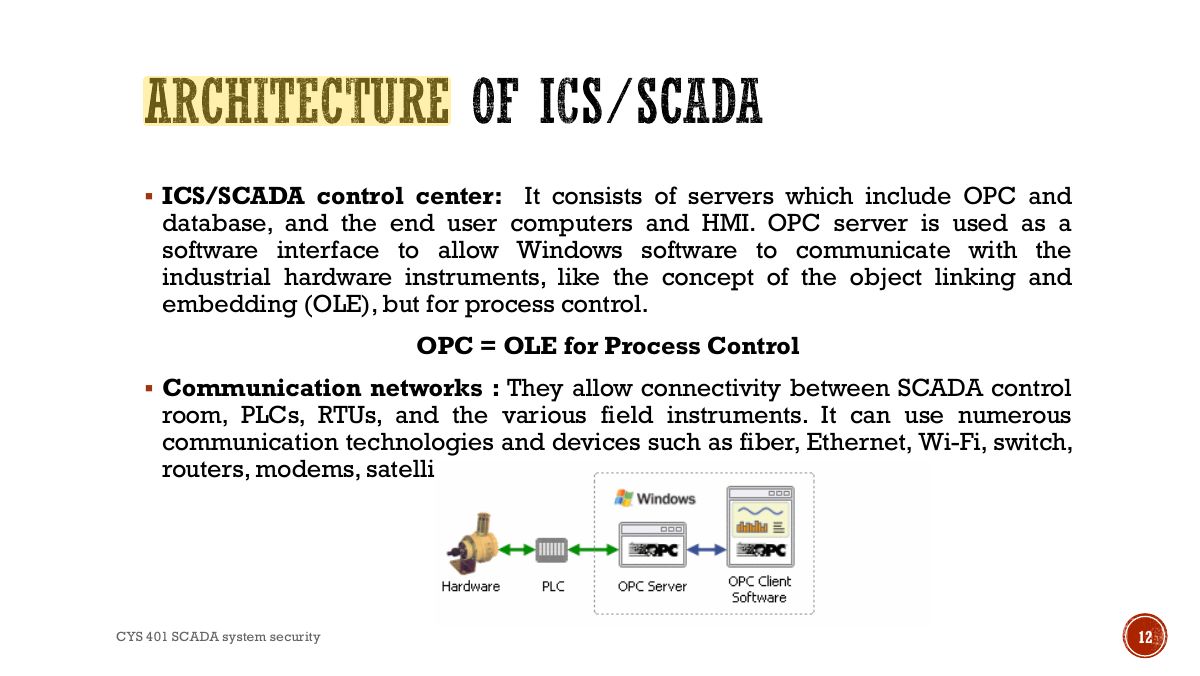
  1. Control center: servers (OPC, historian/database), HMI. Communication networks link the control room, PLCs, RTUs and field devices.
Slide 13: ARCHITECTURE OF ICS/SCADA
Exam weight Low
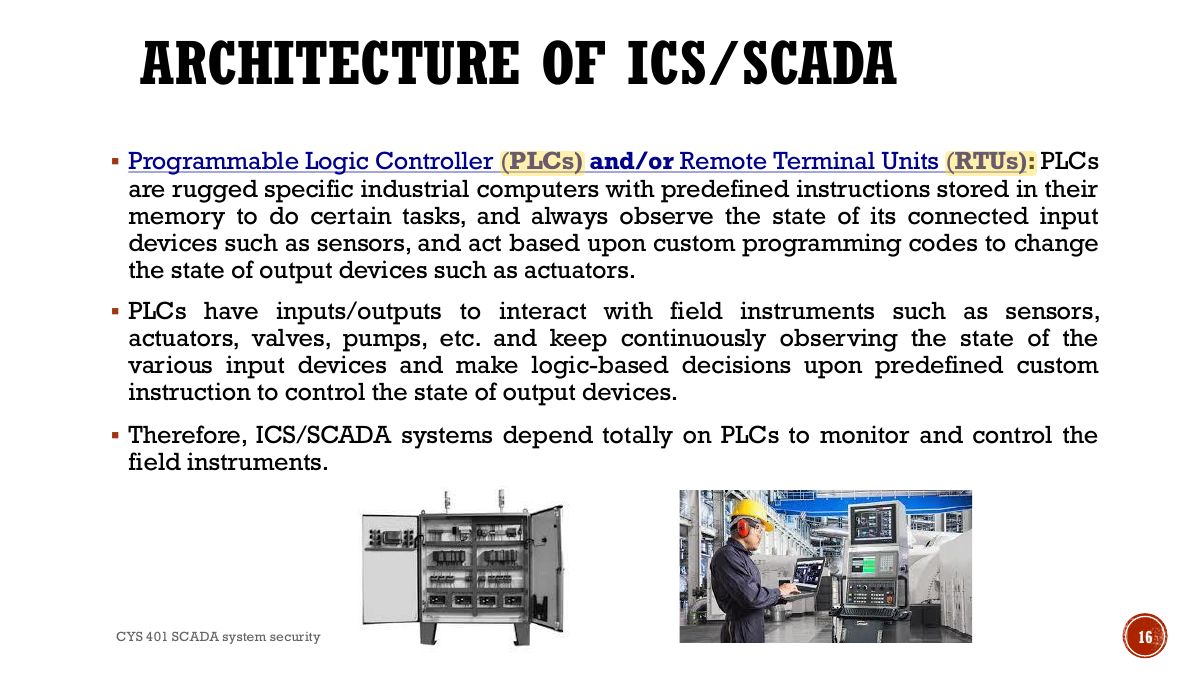
  1. PLCs: rugged industrial computers running stored logic; inputs/outputs to sensors, actuators, valves, pumps.
Slide 14: ARCHITECTURE OF ICS/SCADA
Exam weight High
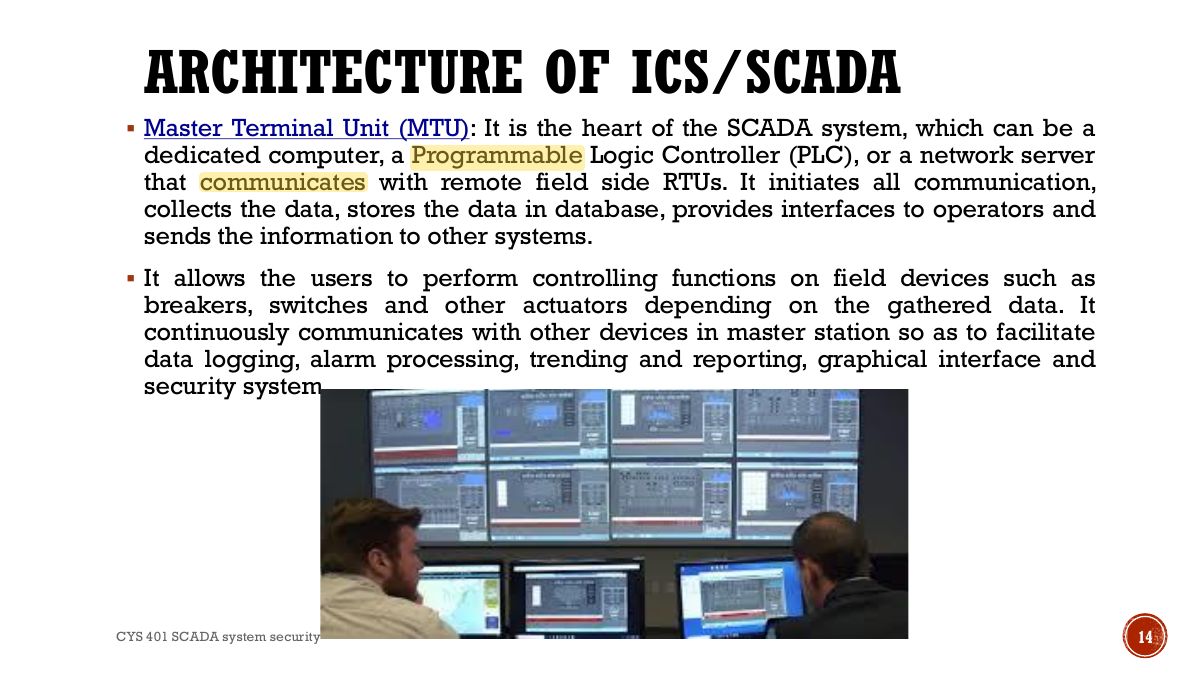
  1. MTU (Master Terminal Unit): the heart of SCADA; polls RTUs and lets operators control field devices.
🎯 How this can come up · 1 question
MCQ

The “heart” of a SCADA system that polls RTUs is the:

SAMPLE SCADA MASTERS

CYS 401 SCADA system security

15
Exam weight Low
  1. Sample SCADA masters.
Slide 16: ARCHITECTURE OF ICS/SCADA
Exam weight Low
  1. PLCs and RTUs again.

CYS 401 SCADA system security

17
Exam weight Low
  1. RTU detail.
Slide 18: Remote Terminal Units (RTUs):
Exam weight High
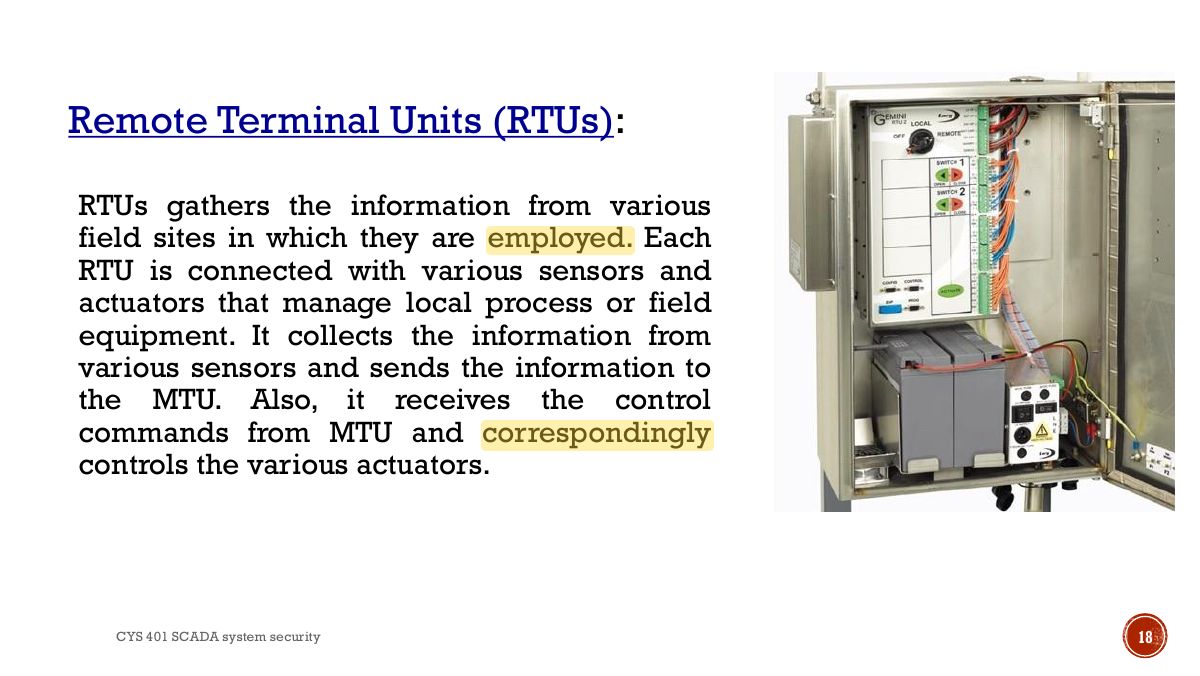
  1. RTUs gather data from field sites and send it to the MTU.
🎯 How this can come up · 1 question
MCQ

Which device collects data from field sensors at remote sites and sends it to the MTU?

CYS 401 SCADA system security

19
Exam weight Low
  1. RTU detail.
Slide 20: ▪ Many RTUs store the data in their database and waits for a request from the MTU
Exam weight Low
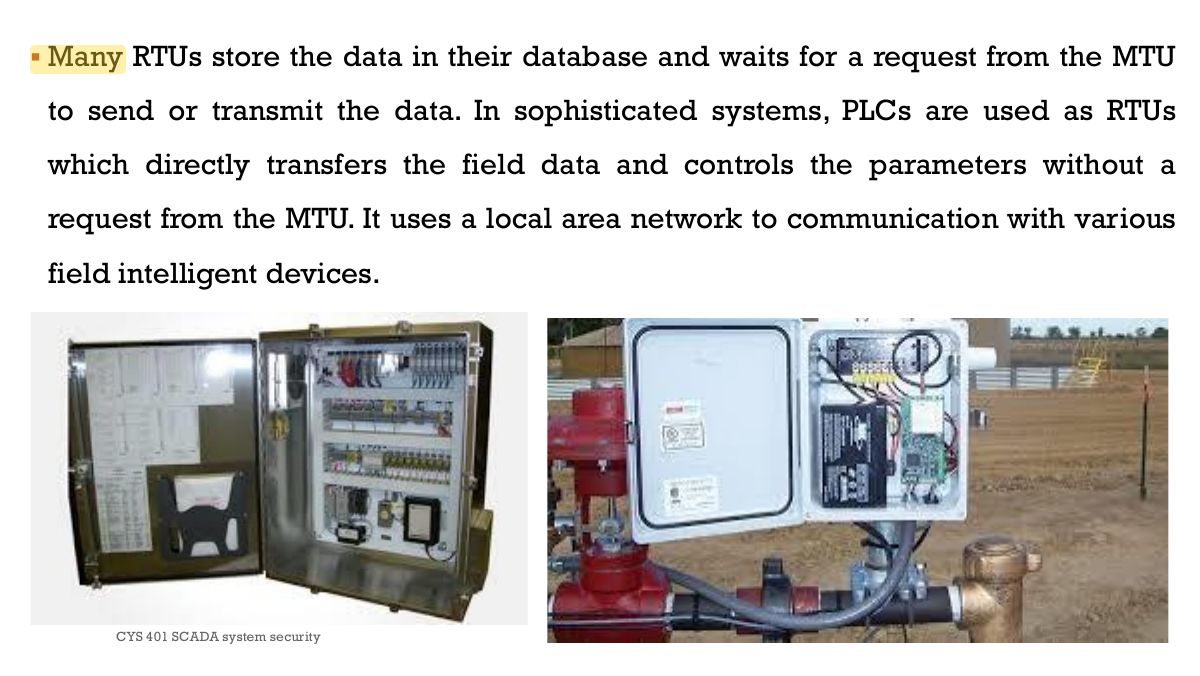
  1. RTUs store data and wait for the MTU to request it; PLCs can act as RTUs.
Slide 21: Slide 21
Exam weight Low
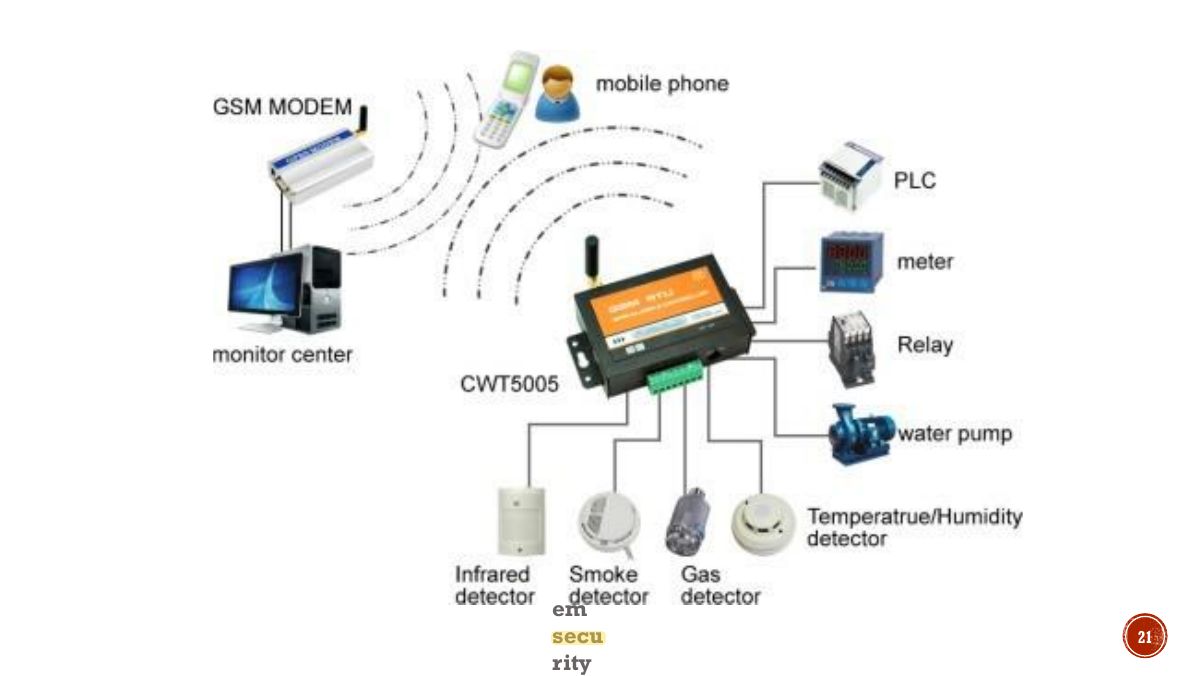
  1. Communication figure.

▪ Communication Equipment/Network: It provides the link between RTUs (in

the field) to MTU (in the control center). The communication can be wired or wireless or through internet which provides bidirectional and uninterrupted communication between RTU and MTU.

  • SCADA systems can be connected using various communication mediums including twisted pair cables, coaxial metal cables, fiber optic cables, satellites, high frequency radio, telephone lines, and microwave radio.
  • The topology of the SCADA system network depends on the type of system or application it is intended for. Mostly redundant topology is recommended for critical control applications. CYS 401 SCADA system security
22
Exam weight Low
  1. Communication: wired or wireless links between RTUs and the MTU.

CYS 401 SCADA system security

23
Exam weight Low
  1. Architecture detail.
Slide 24: ARCHITECTURE OF ICS/SCADA
Exam weight Low
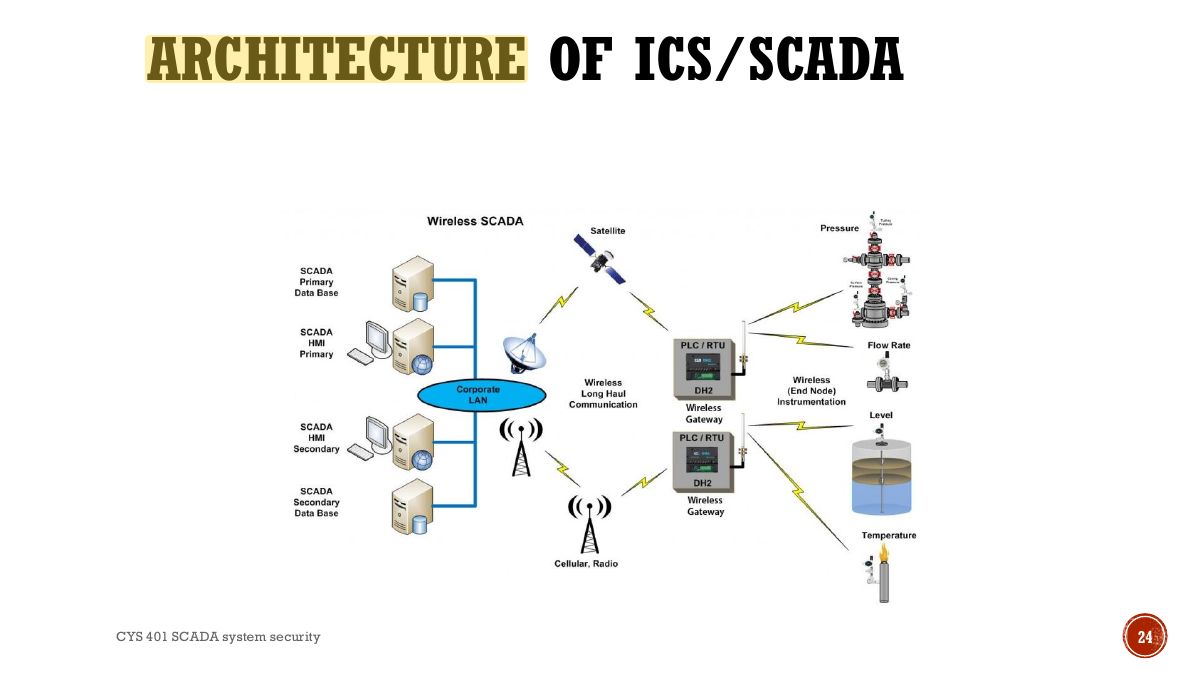
  1. Architecture figure.
Slide 25: ARCHITECTURE OF ICS/SCADA
Exam weight Low
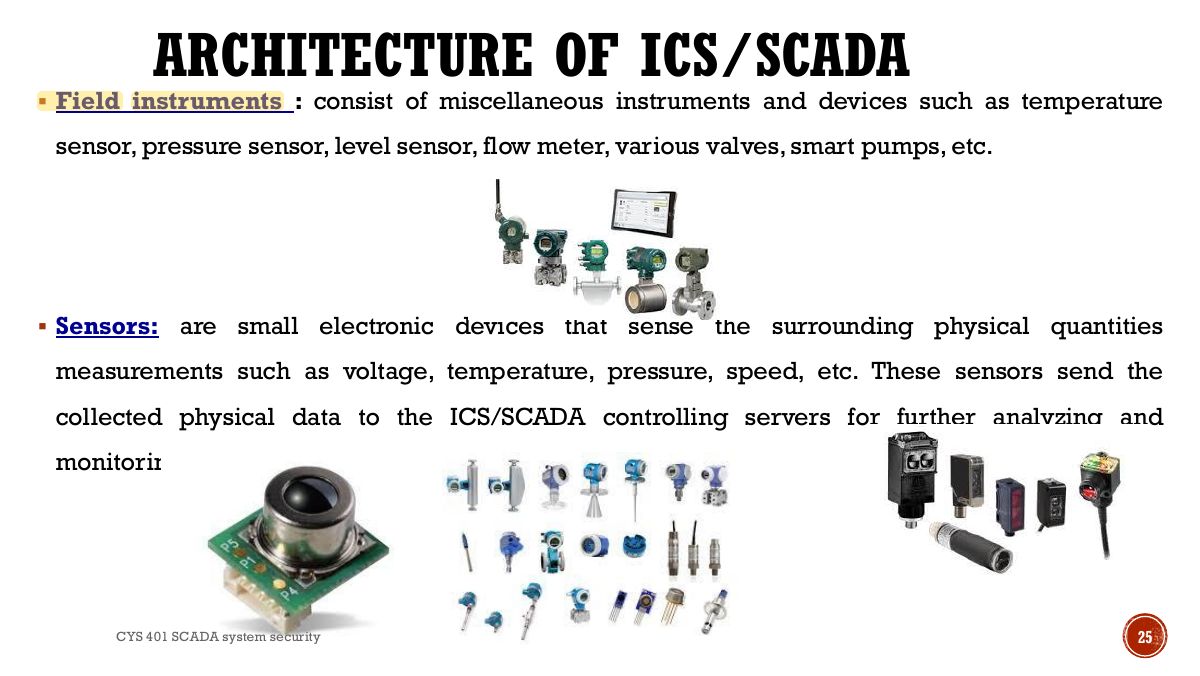
  1. Field instruments: sensors (measure) and actuators (act).
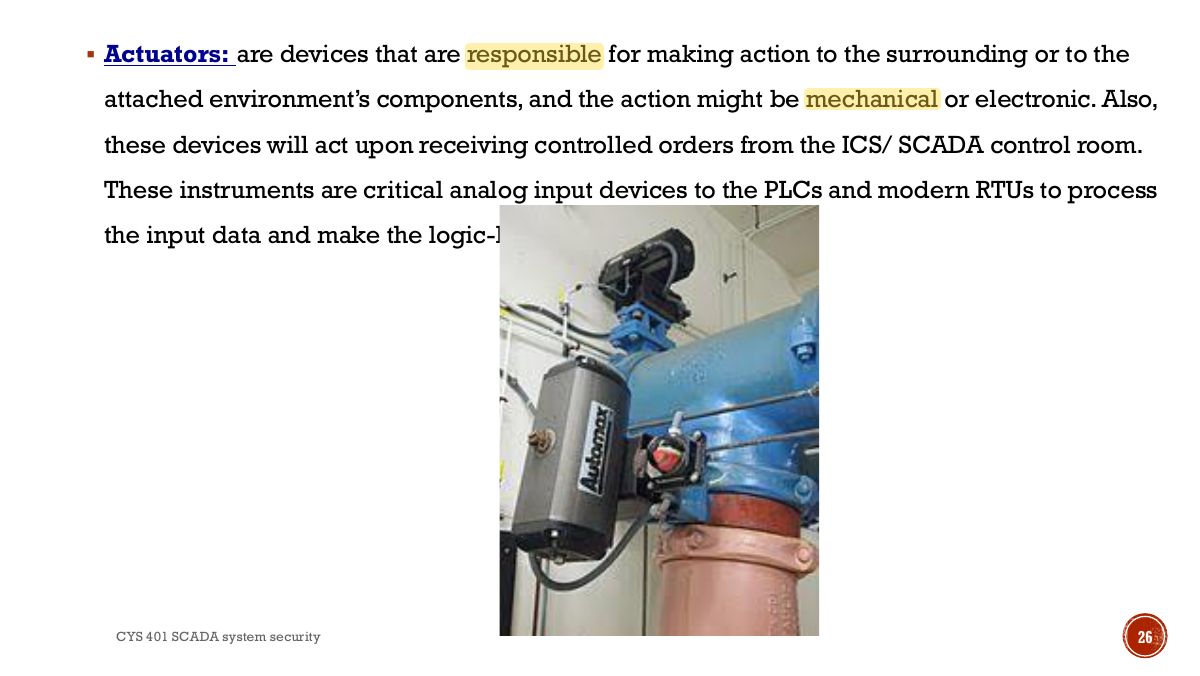
Slide 26: ▪ Actuators: are devices that are responsible for making action to the surrounding or to the
Exam weight Low
  1. Actuators act on the environment (valves, motors) when commanded.

▪ SCADA Software: It is an important aspect of every SCADA system which

presents the information to the user and also allows the user to intervene in the process control. Many SCADA systems use commercial proprietary software upon which SCADA system is developed.

  • This software comprises a computer operating system which controls the central host computer hardware, communication network management, graphical generation tool for HMI, database management and report generation tools.
  • Other components or auxiliary equipment in central station includes HMI station, which gives graphical representation of field parameters, alarm generators to inform normal and abnormal conditions of process and CYS 401 SCADA system security
27
Exam weight Low
  1. SCADA software presents data to operators and lets them intervene.

CYS 401 SCADA system security

28
Exam weight Low
  1. Detail.
Slide 29: ARCHITECTURE OF ICS/SCADA
Exam weight Low
  1. Architecture figure.
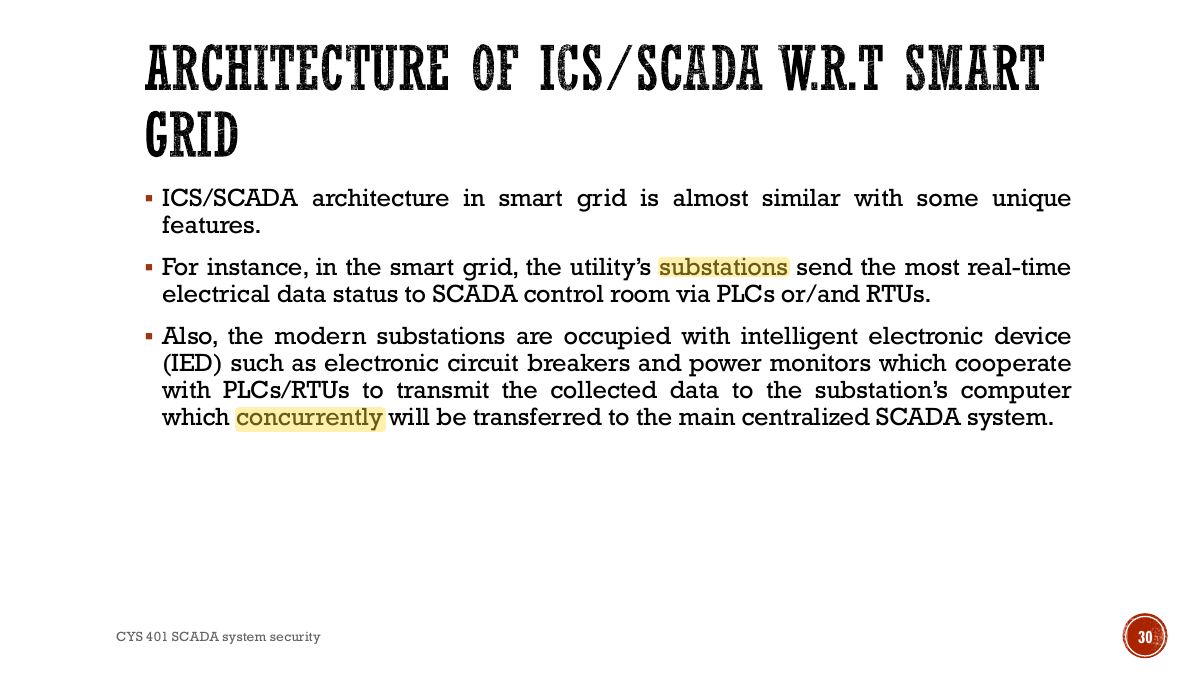
Slide 30: ARCHITECTURE OF ICS/SCADA W.R.T SMART GRID
Exam weight Low
  1. Smart-grid SCADA: substations send real-time data to the control room via PLCs/RTUs.
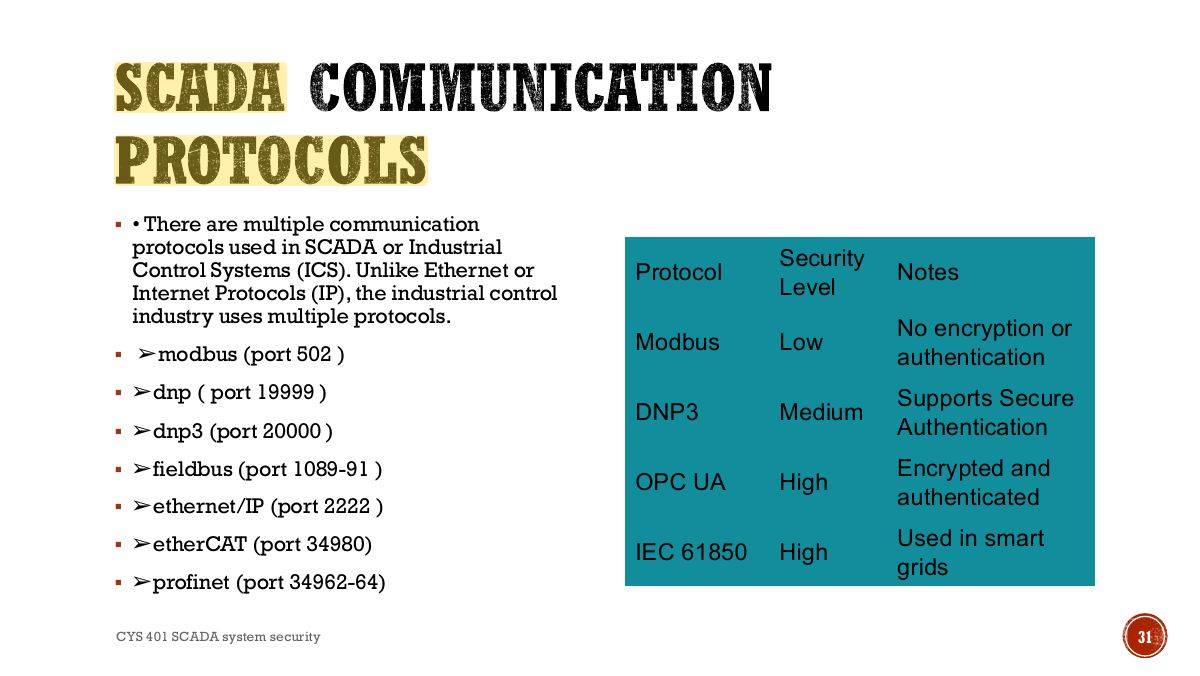
Slide 31: SCADA COMMUNICATION PROTOCOLS
Exam weight High
  1. SCADA protocols (Modbus port 502, DNP3, IEC 61850…) were designed without authentication or encryption.
🎯 How this can come up · 1 question
True / False

Classic SCADA protocols such as Modbus include strong authentication by default.

ICS/SCADA VULNERABILITIES

  • Cyber- physical’s embedded systems are the operation fundamental of the ICS/ SCADA systems which become more vulnerable to exploitation; therefore, they should be well-protected and secured.
  • The vulnerability of the ICS/SCADA system is due to many factors such as:
    • the absence of real-time network scanning to detect suspicious activities,
    • identify the threats, and react accordingly,
    • the slowness for systematic and careful updating and patching, and
    • lack of knowledge about the specification and capabilities of the old and new devices.
    • Also, not having enough information about the network’s traffic status is the core reason for the vulnerability because it stops the security specialists to know about any abnormal activities or potential threats to field instruments and ICS/ SCADA system.
    • Neglected, unskilled, and unsafe practices of authentication give chances to the attackers to gain access to these holes.

CYS 401 SCADA system security

32
Exam weight Low
  1. Vulnerabilities: legacy systems, connection to IT networks/internet, weak protocols, poor patching.

ATTACKING METHODS TOWARDS ICS/SCADA

  • An attacker targeting the ICS/SCADA systems are not in one trial but through a bulkiness of efforts and methods to gather the most applicable and adequate information to create a great negative cause.
  • The type and complexity of attacking methods that are used are determined by
    • how much the attacking purpose is vital,
    • what is the impact level must be achieved to satisfy these purposes, and
    • how much the ICS/SCADA system is secured. For instance, if an attacker has no harm objective, s/he might satisfy using DoS.
  • However, s/he needs to go further to destruct the ICS/SCADA system by manipulating the operational process to achieve the ultimate damage and harms to the structure, equipment, data, and human. Then, a huge systematically attacking method will be used. CYS 401 SCADA system security
33
Exam weight Low
  1. Attacks come through many steps: reconnaissance, initial access, lateral movement, manipulation.

THREATS CATEGORIES FACING ICS/SCADA

The security of the ICS/SCADA operations is threatened by two main categories of intimidation including 1. Unintentional (inadvertent) threats are mainly originated from inside the premises, and the primary sources are the human, devices, or the surrounding nature.

  • The human factor including the employees, contractors, and/or business partners can be a source of threats in the form of neglect, carelessness, or lack of knowledge, so s/he might produce a threat toward the ICS/SCADA system without awareness or intention to do that.
  • the machine’s failure, devices safety weakness, and equipment crashing are a great source of threats to the ICS/SCADA security.
  • the natural disasters such as avalanches and landslides, earthquakes, sinkholes, volcanic eruptions, floods, tsunami, and blizzards can cause disruption to the ICS/SCADA security.

2. Purposeful threats: The ICS/SCADA system can be targeted by the meaning of purposeful attacks by annoyed employees, industrial espionage, sabotage, cyber hackers, viruses and worms, physical theft, and electronic terrorism.

CYS 401 SCADA system security

34
Exam weight Low
  1. Threats: unintentional (negligent staff, accidents) and intentional (hackers, insiders, nation states).
Slide 35: LETS WATCH THIS ...
Exam weight Low
  1. Videos (Stuxnet and other ICS attacks).

THE CHALLENGES TO PROTECT ICS/SCADA

There are many security challenges facing the professionals to protect the ICS/ SCADA systems such as:

  • The old and basic architecture designs in which the security matter is not considered.
  • The message are still transmitted internally and between remote connections using clear text form without adopting any encryption technologies.
  • There are many applications and servers’ operating systems and applications that have no regular patching scheme, even some firmware not updated at all.
  • Another challenge is to secure the remote communication of the ICS/SCADA components which are geographically scattered such as sensors, actuators, RTUs, and PLC. CYS 401 SCADA system security
36
Exam weight Low
  1. Challenges: old designs without security, 24/7 availability needs, hard to patch.

▪ In addition, there are several management, operational, and

technical challenges to secure the ICS/SCADA systems, such as:

  • vulnerability tracking problem,
  • standardization of devices and systems,
  • downtime for maintenance,
  • unsupported OS and applications,
  • exposed to operational technology (OT) network to public networks,
  • unable to pen-test in production real time,
  • limited time for remediation once incidents occur,
  • share accounts or no authentication within users, and
  • secure the connection between information technology (IT) and OT.

CYS 401 SCADA system security

37
Exam weight Low
  1. Management, operational and technical challenges: vulnerability tracking, skills, budgets.

ICS/SCADA SECURITY OBJECTIVES

There are many objectives to protect the ICS/SCADA architectures such as

  • keeping the ICS/SCADA systems functioning as much as possible during the most difficult conditions.
  • This involves creating a redundancy for the most ICS/SCADA critical devices such as historian servers, switches, modems, and the field instrumentations.
  • Also, during a failure, the device should not cause unnecessary traffic on the ICS/ SCADA networks or cause extra trouble elsewhere.

CYS 401 SCADA system security

38
Exam weight Low
  1. Objectives: keep the system functioning even in the worst conditions.
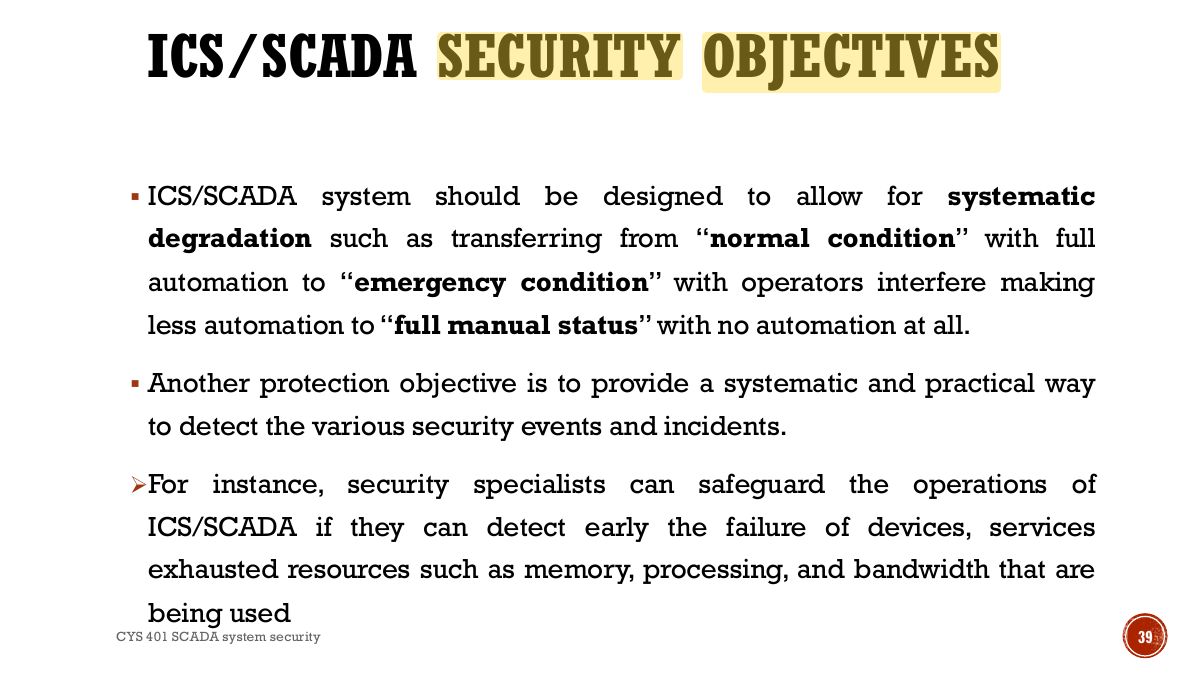
Slide 39: ICS/SCADA SECURITY OBJECTIVES
Exam weight Low
  1. Graceful (systematic) degradation from normal to emergency operation; detect security events.

ICS/SCADA SECURITY OBJECTIVES

The three traditional security objectives for securing the ICS/ SCADA systems are:

  • Availability is on top of security objectives priority list which is focusing on keeping ICS/SCADA systems services offered continuously 24/7 when monitoring and controlling critical infrastructure or life-safety systems.
  • Integrity comes the second order in the list by the ability to offer the operators/controllers the confident needed to fully trust the integrity of the various physical information that is received and to take the most suitable actions based on reading feedback or status from the various instruments and devices.
  • Confidentiality is not as important as the availability and integrity because the received physical information from sensors, PLCs and RTUs, are used and the transmitted is state-based and only valid for that specific time; then, it will CYS 401 SCADA system security processing and storing them in the historian servers. be discarded after
40
Exam weight Medium
  1. Three objectives with availability at the top, then integrity, then confidentiality.

ICS/SCADA SECURITY REQUIREMENTS

  • Importance of Security Countermeasures:
  • Security requirements (countermeasures) are an action, device, procedures, or techniques that reduce a threat, vulnerability, or an attack.
  • These requirements are aimed to eliminate or prevent the threat by decreasing the negative impacts automatically or by discovering and reporting it so that corrective solutions can be taken by the IT specialists or the operators. CYS 401 SCADA system security
41
Exam weight Low
  1. Countermeasures reduce a threat, vulnerability or attack.

ICS/SCADA SECURITY REQUIREMENTS

  • Protecting the field instruments (e.g., sensors, actuators, PLC, and RTU) is the main security concern for securing the operations of the ICS/SCADA system.
  • This protection starts from selecting the right device with compliance to the latest security standards.
  • Security of field instrument should go throughout its life cycle: procurement, installation, monitoring, and maintenance.
  • Field instruments should have met the core security requirements such as the authentication, authorization, and CIA
  • Physical security countermeasures for field instruments should start from providing the applicable secure fences and gates which must be accessed through the combination of traditional hardware and electronic locks.
  • A motion detector linked with closed circuit television (CCTV) is recommended to record and discover any intruder to the remote stations. CYS 401 SCADA system security
42
Exam weight Low
  1. Protect field instruments (sensors, actuators, PLCs, RTUs): choose compliant devices.

ICS/SCADA SECURITY REQUIREMENTS

  • ICS/SCADA control room’s servers and hosts must be well protected from the logical and physical attacks.
  • Moreover, to provide the optimum availability the redundancy and high-capacity links between the servers must be established.
  • It is also recommended establishing load balancing and failover mechanisms between ICS/ SCADA servers and network components, such as switches/routers.
  • ICS/SCADA servers should receive the appropriate configuration/patch management and secure importation and execution of only trusted patches CYS 401 SCADA system security which will help to secure the ICS/SCADA servers.
43
Exam weight Low
  1. Protect control-room servers from logical and physical attacks; redundancy for availability.

▪ Security counter measures at ser vers:

  • strong multifactor authentication,
  • application whitelisting,
  • securing the hosts physically, and logically through adopting and implementing solid access controls using different tools, policies, and protocols to develop the most secure identification, authentication, authorization, and accountability mechanisms. CYS 401 SCADA system security
44
Exam weight Low
  1. Server countermeasures: MFA, application whitelisting, patching, hardening.
ICS/SCADA SECURITY REQUIREMENTS

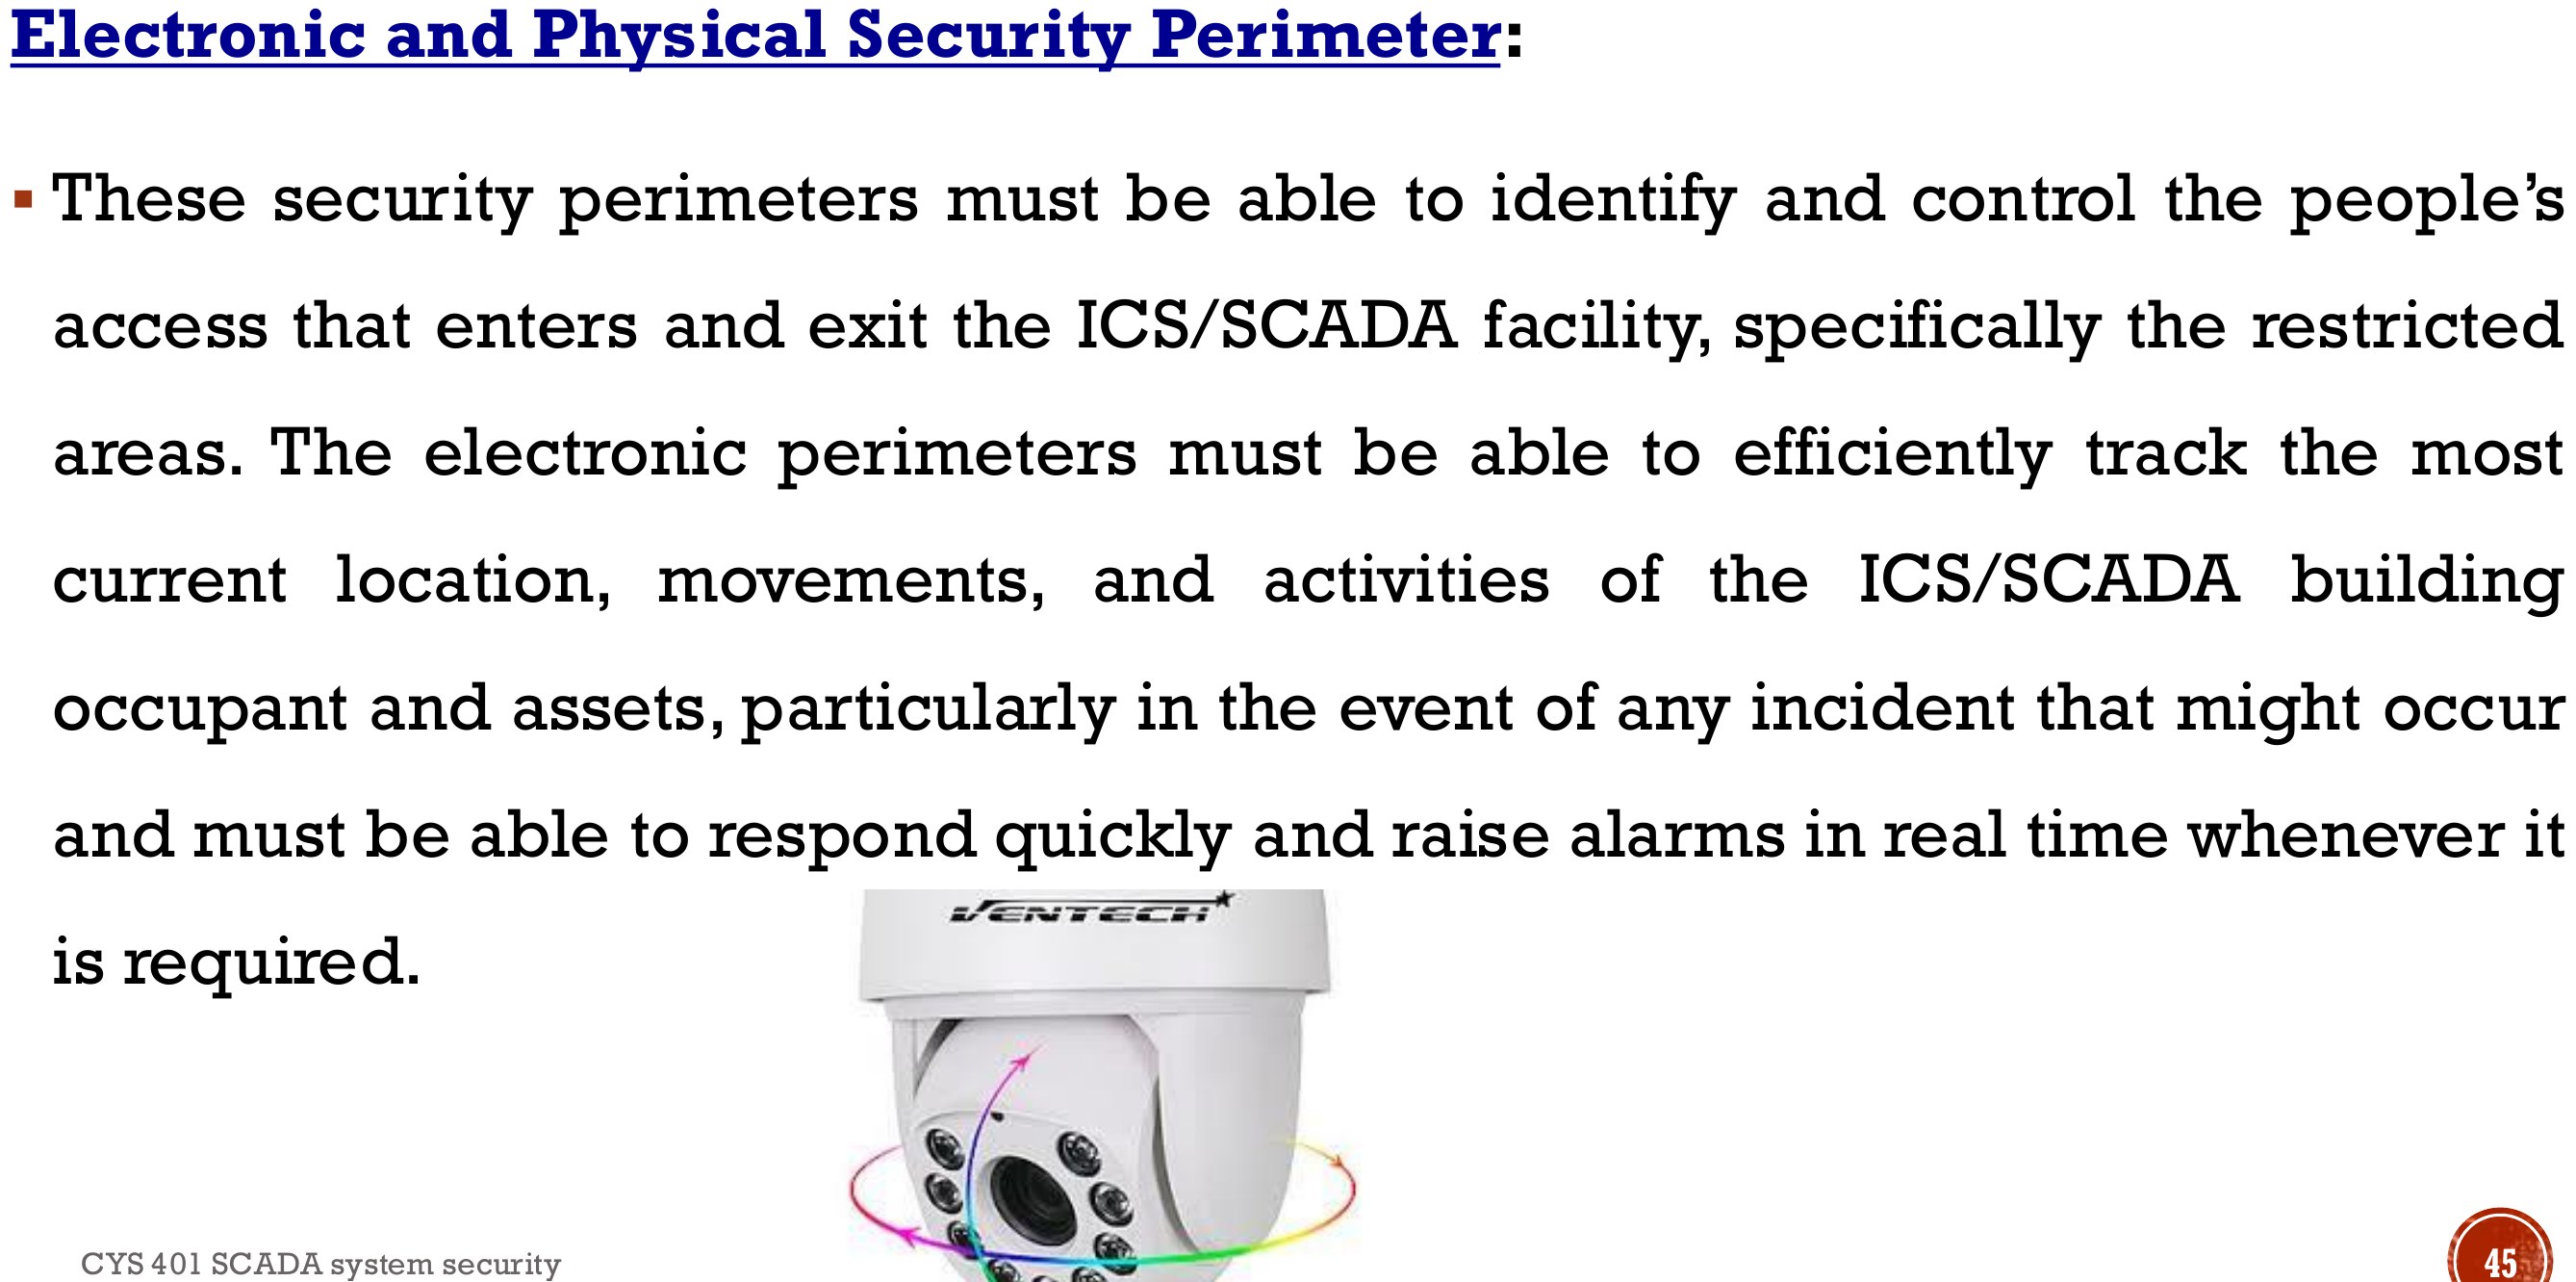
Electronic and Physical Security Perimeter:

  • These security perimeters must be able to identify and control the people’s access that enters and exit the ICS/SCADA facility, specifically the restricted areas. The electronic perimeters must be able to efficiently track the most current location, movements, and activities of the ICS/SCADA building occupant and assets, particularly in the event of any incident that might occur and must be able to respond quickly and raise alarms in real time whenever it is required. CYS 401 SCADA system security
ICS/SCADA SECURITY REQUIREMENTS
45
Exam weight Low
  1. Electronic and physical security perimeters control who enters and exits.

ICS/SCADA SECURITY REQUIREMENTS

  • This unified security package should consist of video surveillance, access control, and perimeter detection tools that are tightly integrated with alarms and events raised in process and safety systems for intelligent, and a coordinated responses mechanism.
  • The unified tool also should occupy with the human — machine interface (HMI) which give common look and feel results. The HMI is enhancing the decision-making because both ICS/SCADA control room consoles and security office desktops have visibility of the real-time events and lead to faster responds and feedbacks.
  • Adopting Mantrap technique (see next slide)
46
Exam weight Low
  1. Unified physical security: CCTV, access control, perimeter detection, integrated with an HMI.

CYS 401 SCADA system security

47
Exam weight Low
  1. Detail.

ICS/SCADA SECURITY REQUIREMENTS

  • Network Communication Security: ICS/SCADA servers and network components work together to manage all communications, evaluate and examine the received data, and show the alerts and events on the HMI workstations.
  • communication technologies include wired such as fiber optics, power line communication, copper-wire line, and wireless such as GSM/GPRS/WiMax/WLAN and Cognitive Radio.
  • However, one of these communication technologies could represent a potential threat to the ICS/SCADA system CYS 401 SCADA system security
48
Exam weight Low
  1. Network communication security: segment, encrypt, authenticate all links.

ICS/SCADA SECURITY REQUIREMENTS

  • Example: using old remote connection technology such as leased-line and dial-up modems for ICS/ SCADA remote communication with distant field devices will facilitate the attacking efforts into the critical networks.
  • These old communication technologies mostly have got no or weak authentication and encryption which can be utilized by attackers to gain access to the ICS/SCADA network.
  • For example, an attacker can access to the old technology modem which is connected to the smart grid’s breakers, disrupting the altering the control configuration settings causing power outages and damages various electrical equipment. CYS 401 SCADA system security
49
Exam weight Low
  1. Old remote access (leased lines, dial-up modems) lacks authentication and encryption.

ICS/SCADA SECURITY REQUIREMENTS

  • It is important to utilize network security monitoring (NSM), NDR (Network Detection & Response) and security information event management (SIEM)
  • NSM is a mean of gathering, analyzing, and rising the right indications or warnings to detect and respond to intrusions attacks.
  • NDR uses passive, behavior-based network monitoring to detect abnormal and malicious activity in SCADA and IT networks in real time, without impacting operations.
  • SIEM system is similar to NSM in providing a real-time analysis and performing data aggregation, association, alerting, dashboards, compliance, maintenance, and forensics investigation CYS 401 SCADA system security
50
Exam weight Medium
  1. Monitoring: NSM, NDR and SIEM to detect intrusions.
🎯 How this can come up · 1 question
MCQ

A system that collects and correlates security events from many sources is a:

ICS/SCADA SECURITY REQUIREMENTS

  • Product, Software, and Hardening:
  • The ICS/SCADA infrastructure occupies a wide range of IT products and software, which should be evaluated and certificated to ensure the quality and to ensure that they are per the standing security standards.
  • These IT-related products and software should be updated, stable versions, tested, verified, and patched regularly to solid the security of the OT operational requirements.
  • Hardening of ICS/SCADA system involves eliminating idle, needless, or unknown components such as modules, services, or ports. The most important in system hardening is selecting and implementing the most secure configuration parameters, as well as installing the security patches. CYS 401 SCADA system security
51
Exam weight Low
  1. Evaluate and certify products and software; harden them.

ICS/SCADA SECURITY POLICIES

  • The objective of ICS/SCADA security policy is to provide management direction and support security professionals in an alignment of the business requirements and relevant laws and regulations.
  • The security policy document should include the individuals who are responsible for the implementing and managing the policy terms, and they should be identified by their names, position details, and the contacts information.
  • Furthermore, the security policy should be systematically reviewed and updated to ensure its continuing suitability, adequacy, and effectiveness CYS 401 SCADA system security
52
Exam weight Low
  1. Security policy gives management direction and assigns responsibilities.

ICS/SCADA SECURITY POLICIES

  • ISO27001 Standard recommended several security policies such as: Clear Desk and Clear Screen Policy,
  • Access Control Policy,
  • Disposal of Information/Media/ Equipment Policy,
  • Data Classification and Control Policy,
  • Mobile Computing and Teleworking Policy,
  • Password policy,
  • Penetration Testing Policy,
  • System/Data Backup and Recovery Policy,
  • Physical Security Policy,
  • System Usage Monitoring Policy,
  • Third Party Access Policy, and
  • Virus /Malware Policy. CYS 401 SCADA system security
53
Exam weight Low
  1. ISO 27001 policies: clear desk/clear screen, access control, backup, mobile devices…
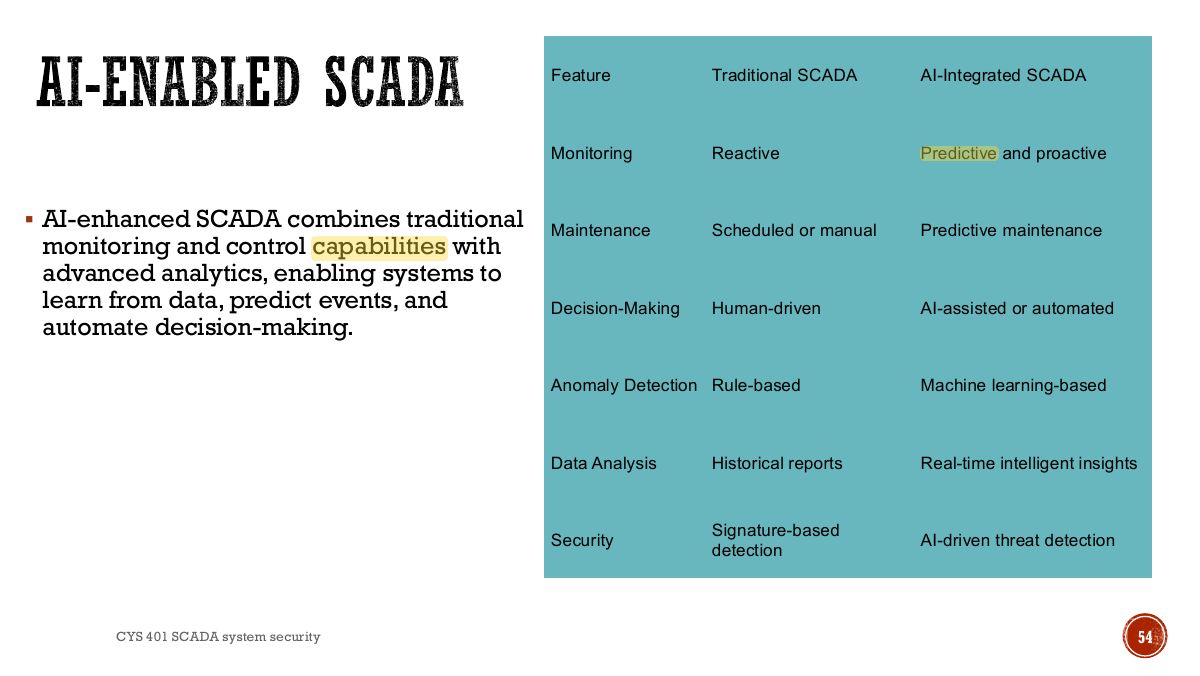
Slide 54: AI-ENABLED SCADA
Exam weight Low
  1. AI-enabled SCADA vs. traditional SCADA.

GOVERNANCE AND COMPLIANCE

  • Governance of the ICS/SCADA Environment
  • Regulatory Compliance and Standard Requirements
  • The Planning Phase to Protect ICS/SCADA

CYS 401 SCADA system security

55
Exam weight Low
  1. Governance and compliance.

GOVERNANCE AND COMPLIANCE

  • Gover nance of the ICS/SCADA Environment:
  • Implementing the ICS/SCADA systems without proper planning processes with a poor risk management study, weak security countermeasures, and inappropriate access control, will lead to ICS/SCADA security program with unsuitable governance.
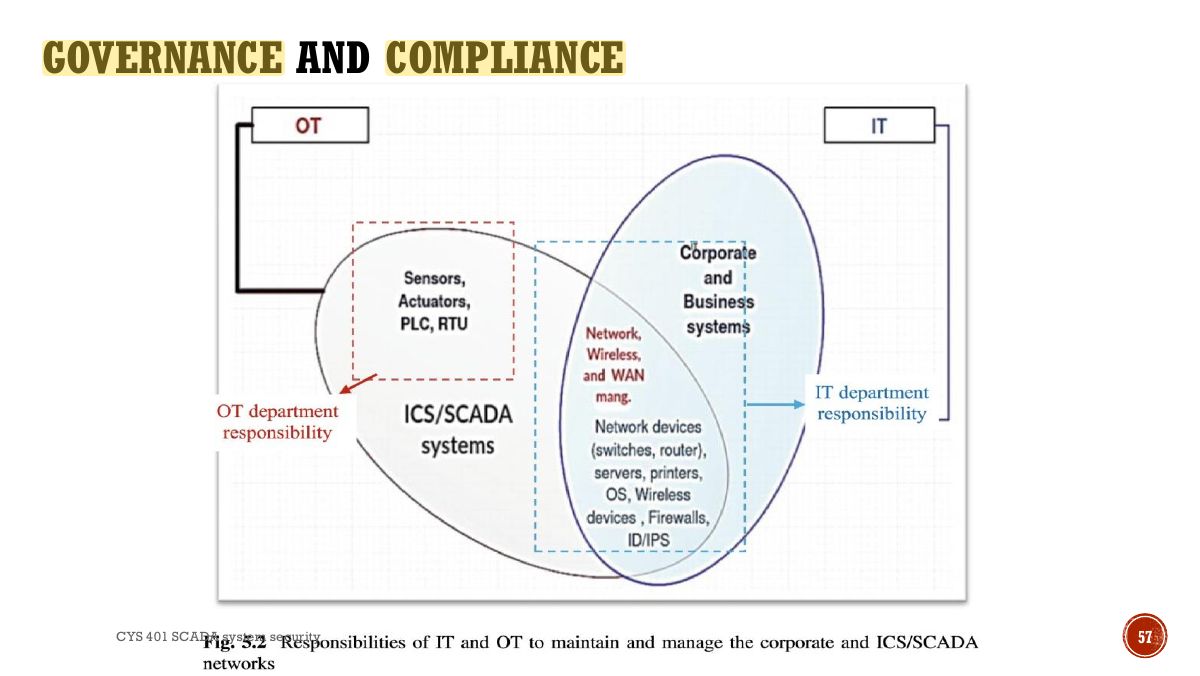
  • One of the ICS/SCADA challenges is governance of OT (ICS/SCADA) security and IT security that are typically managed by different professionals.
  • The OT devices are managed by the controlling, operating, engineering, or automation department, at the same time as the IT components are maintained by the IT department.
  • Moreover, without good coordination, there is often a doubt about which department is responsible for the security of ICS/SCADA infrastructure which might lead to serious gaps in the organization’s security competencies. CYS 401 SCADA system security
56
Exam weight Low
  1. Poor planning and weak governance leave ICS exposed.
Slide 57: GOVERNANCE AND COMPLIANCE
Exam weight Low
  1. Governance figure.

GOVERNANCE AND COMPLIANCE

  • Importance of Governance of the ICS/SCADA Environment:
  • Integrating well-known security standards, best practices, frameworks, and guidelines will give good guidance to develop a satisfactory governance structure for the security of ICS/SCADA infrastructure.
  • The developed governance policy will help the decision-makers to make a better view of the ICS/ SCADA possible threats. It leads to know how to mitigate them, enhance the stakeholder’s internal communications and resources optimization, and clear the roles and responsibilities for the OT and IT
  • Official governance for the management of ICS/SCADA security will help to ensure that stakeholders and departments follow a steady and appropriate security strategy.
  • Besides, the governance delivers clear roles and responsibilities, latest and up-to-date approaches to manage ICS/SCADA security threats, and guarantee that the supportive standards, guidelines, and policies are appropriate and are being implemented and followed. CYS 401 SCADA system security
58
Exam weight Low
  1. Use standards and frameworks (NIST, IEC 62443, ISO 27001).

GOVERNANCE AND COMPLIANCE

  • Regulatory Compliance and Standard Requirements:
  • Several standardization bodies and governmental agencies have developed various standards, guidelines, and policies to protect ICS/SCADA systems
  • DHS catalog of control systems security, which was developed by Homeland Security of USA (2011).
  • North American Electric Reliability Corporation (NERC) Critical Infrastructure Protection (CIP) Standards 002-009 and National Institute of Standards and Technology (NIST) Special Publication 800-82 have good guidance to ICS/SCADA security (NIST 2011).
  • Also, NIST organization has developed the “NISTIR 7628 Guidelines for Smart Grid Cyber Security.

CYS 401 SCADA system security

59
Exam weight Low
  1. Standards bodies and regulators publish ICS security guidance.

GOVERNANCE AND COMPLIANCE

  • The Planning Phase to Protect ICS/SCADA: Preparing a comprehensive security program to secure the ICS/SCADA system is not an easy task because it involves so many procedures and steps A suggestion of seven phases to develop a new security plan for the ICS/SCADA system given as follows: Assessing the existing systems, 1 Documenting the policies and procedures, 2 Training the employees and contractors, 3 4 Segmenting the ICS/SCADA system network and security, Controlling the access to the ICS/SCADA system, 5 Hardening the components of the ICS/SCADA system, 6 Monitoring and maintaining the security of ICS/SCADA system 7 CYS 401 SCADA system security
60
Exam weight Low
  1. Plan a comprehensive ICS security program.

REFERENCES:

  • Cyber-security of SCADA and Other Industrial Control Systems https://www.springer.com/gp/book/9783319321233
  • National Institute of Standards and Technology (NIST) framework for cyber security for SCADA https://www.pcvuesolutions.com/index.php/featured-articles/567-national-institute-of-standards-and-technology-nist-framework-for-cyber-security-for-scada
  • Cyber Threat and Vulnerability Analysis of the U.S. Electric Sector https://www.energy.gov/sites/prod/files/2017/01/f34/Cyber%20Threat%20and

%20Vulnerability%20Analysis%20of%20the%20U.S.%20Electric%20Sector.pdf

  • Security and Privacy in Smart Grids https://www.taylorfrancis.com/books/e/9781439877845/chapters/10.1201/b152

40-14

CYS 401 SCADA system security

61
Exam weight Low
  1. References.