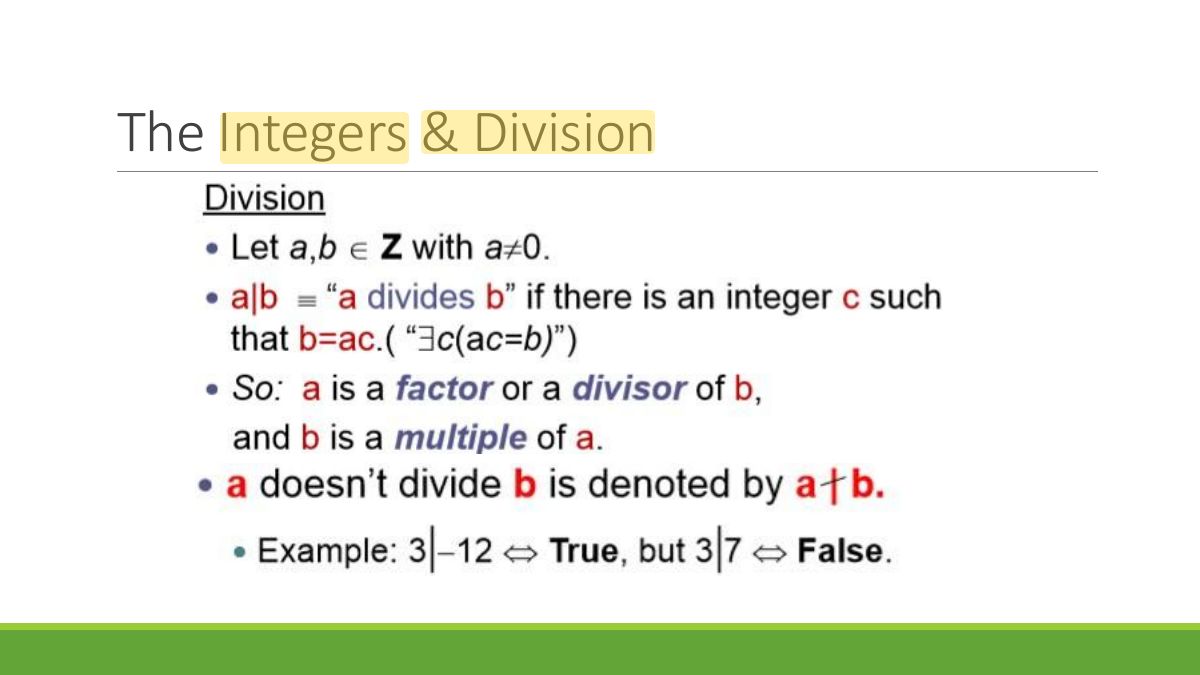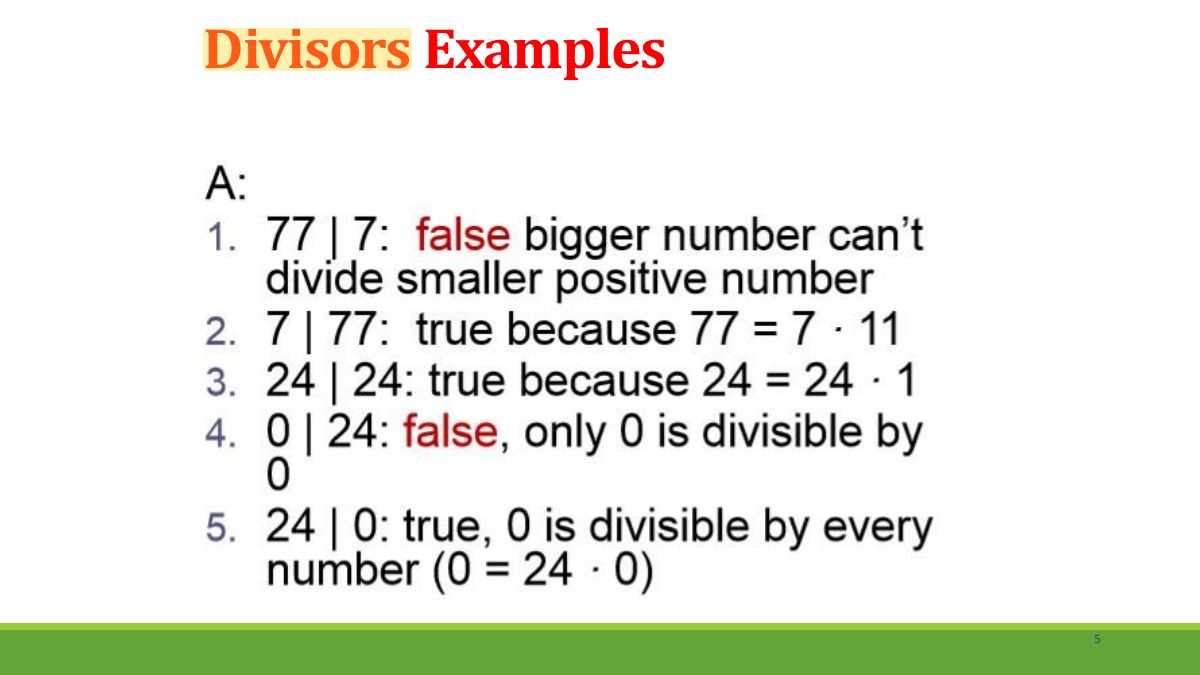
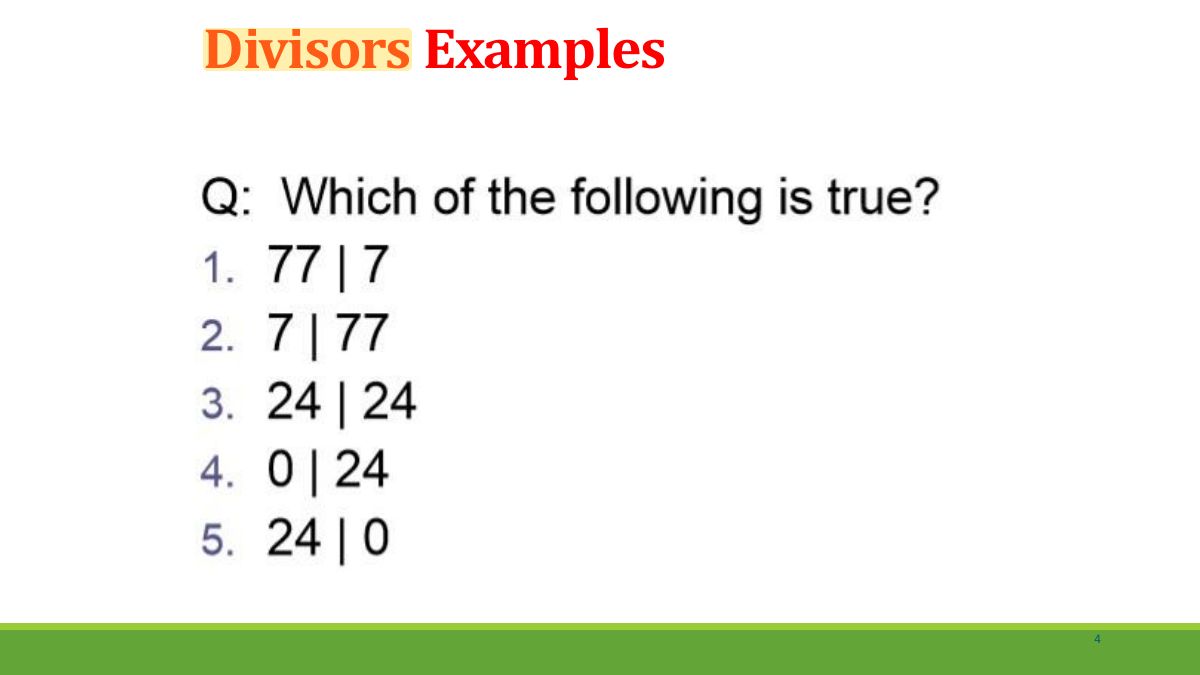
- a | b ("a divides b") when b = ac for some integer c (a ≠ 0).
🎯 How this can come up · 1 question
3 | 12 and 12 | 3.
False. 3 | 12 is true; 12 | 3 is false.
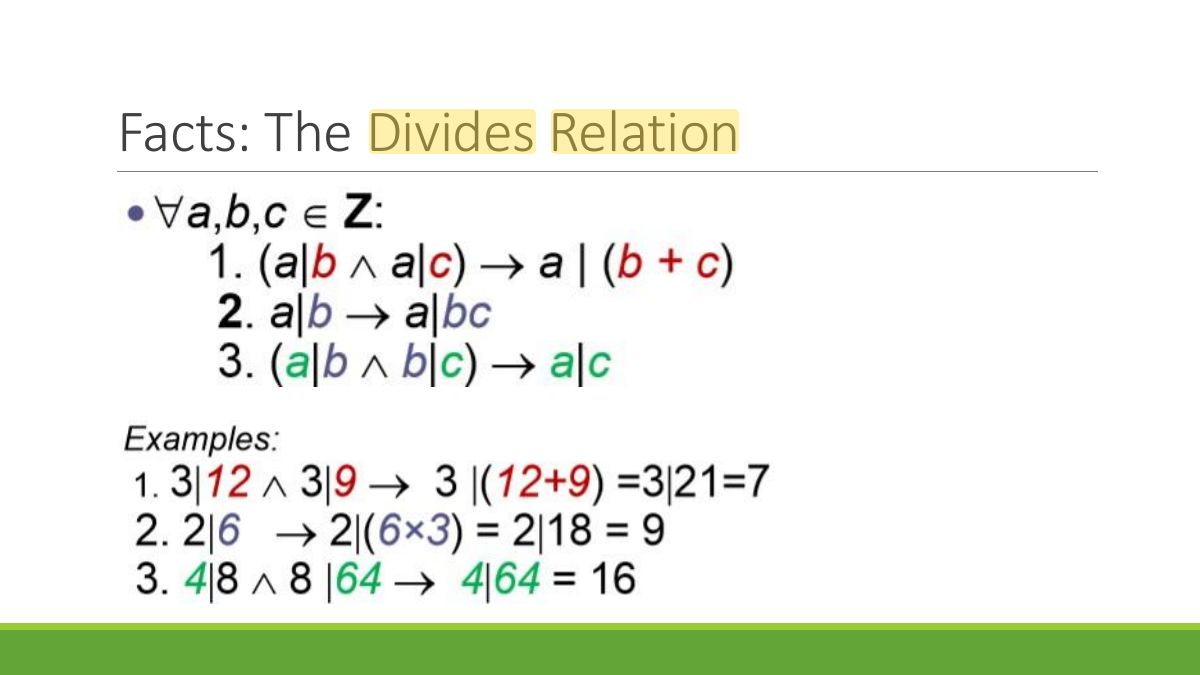
- If a | b and a | c then a | (b + c); if a | b then a | bc; if a | b and b | c then a | c.
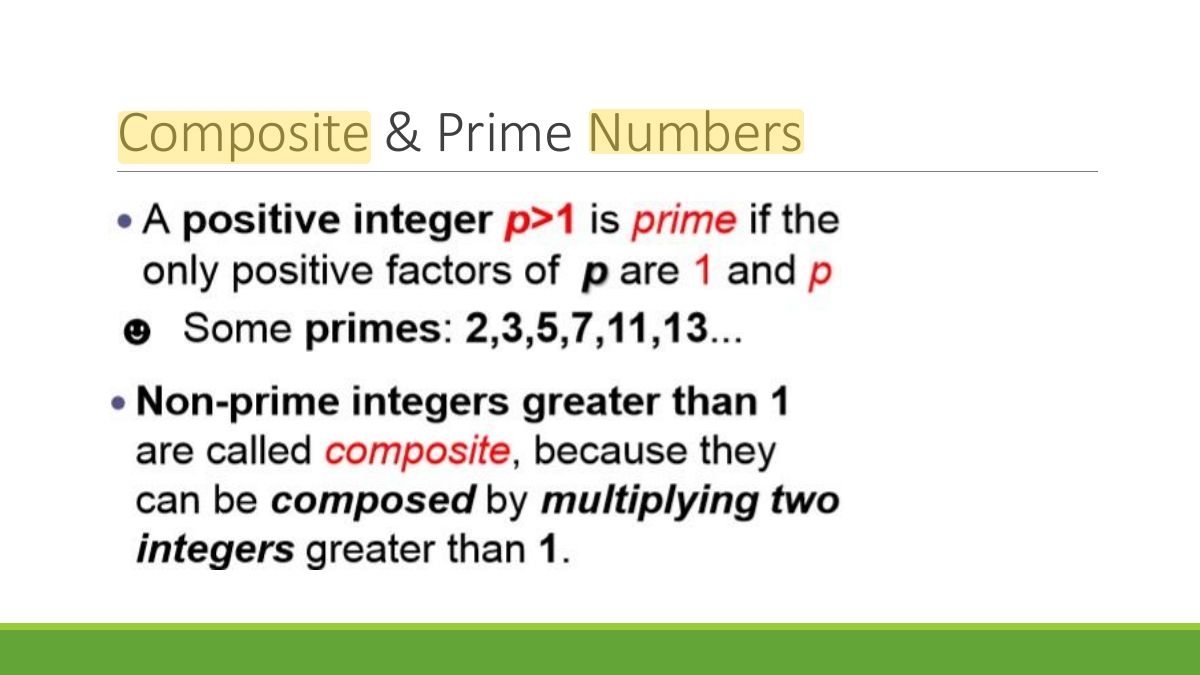
- Prime: integer > 1 whose only positive divisors are 1 and itself. 1 is NOT prime.
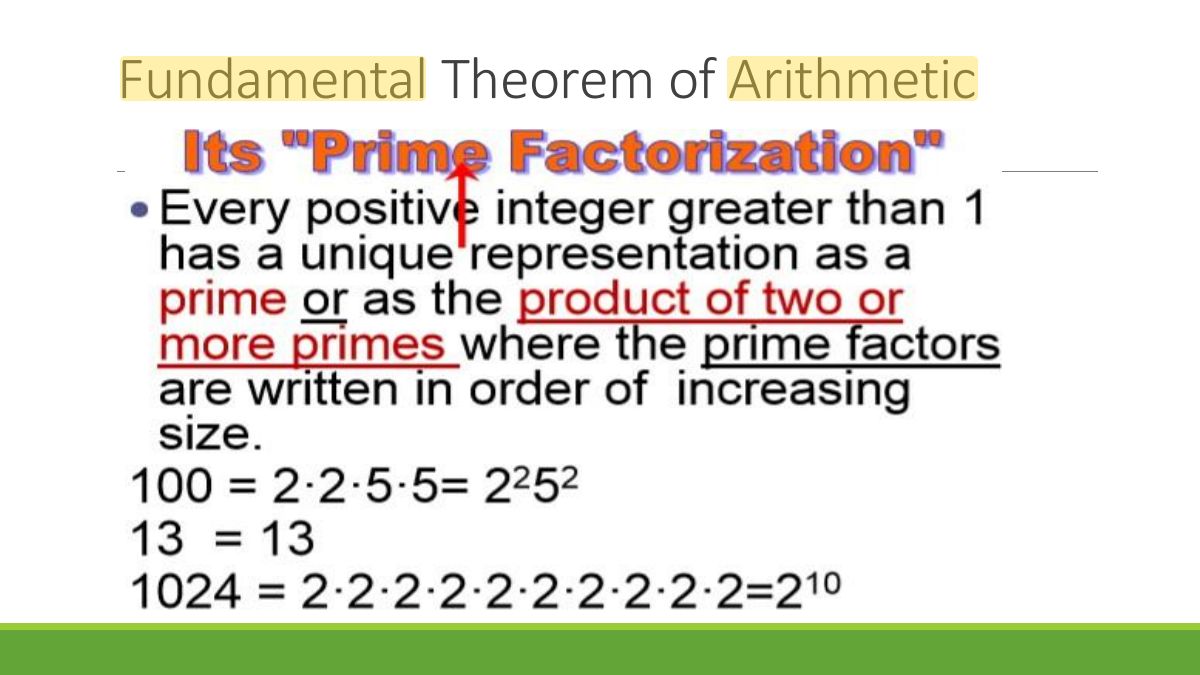
- Every integer > 1 is a unique product of primes (Fundamental Theorem of Arithmetic).
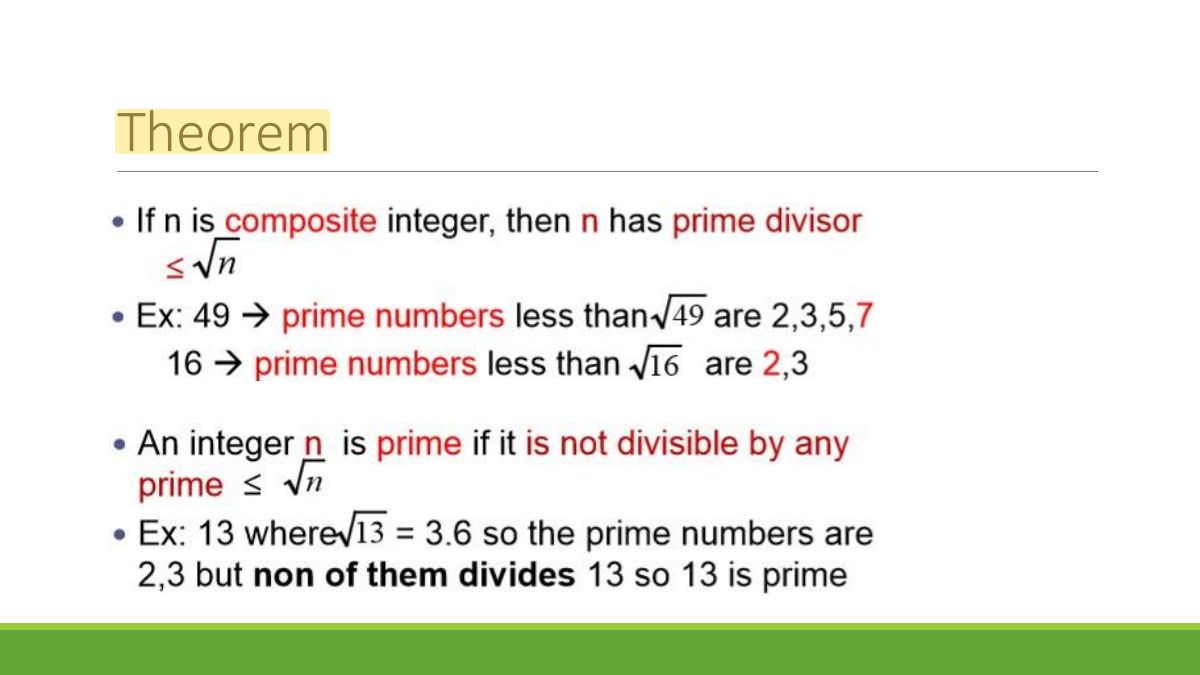
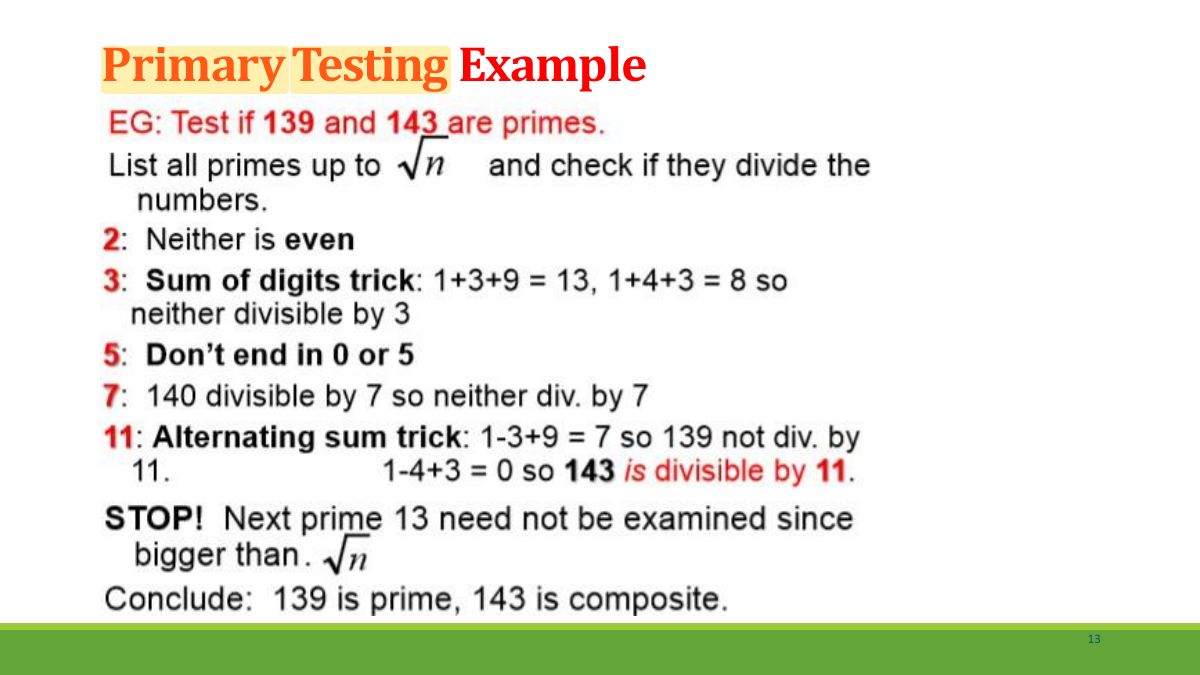
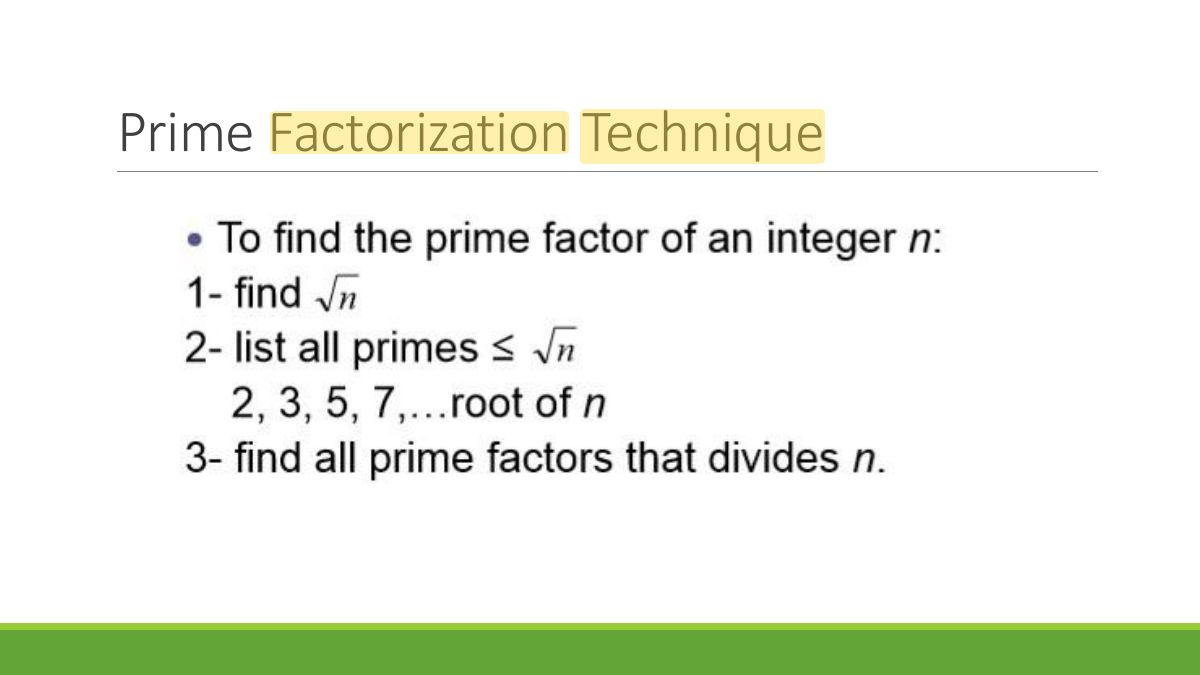
- If n is composite, it has a prime divisor ≤ √n. So test primes up to √n only.
🎯 How this can come up · 1 question
To show 101 is prime it is enough to test divisibility by primes up to:
√101 ≈ 10.05: try 2, 3, 5, 7.
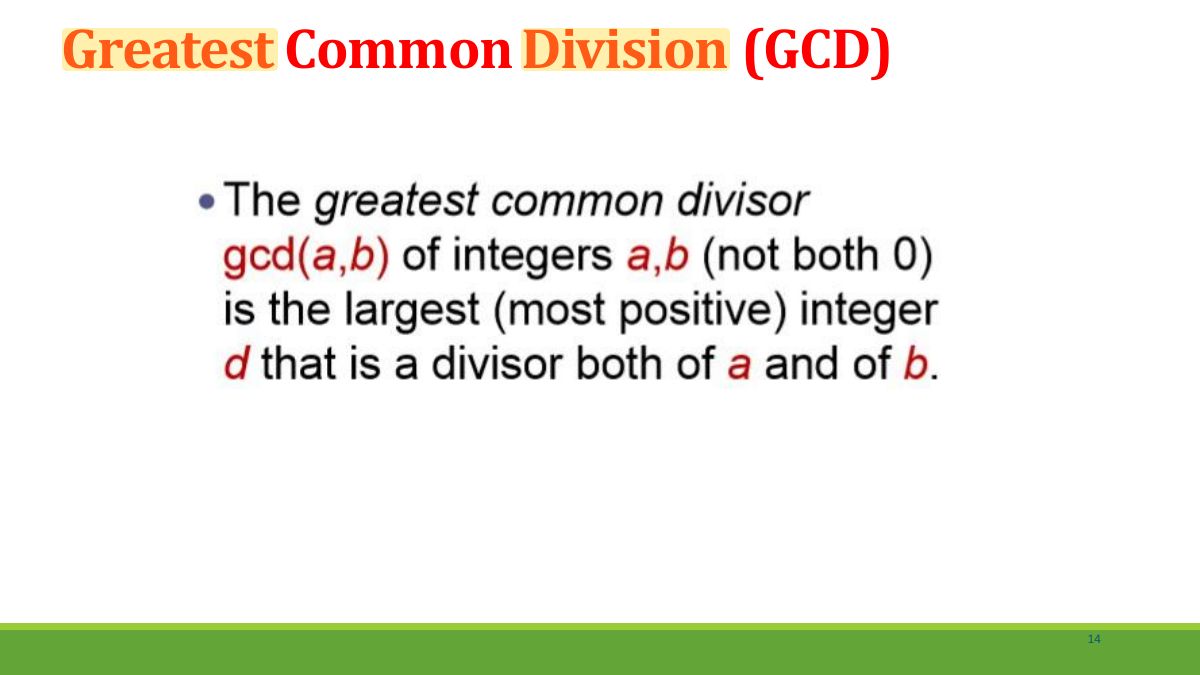
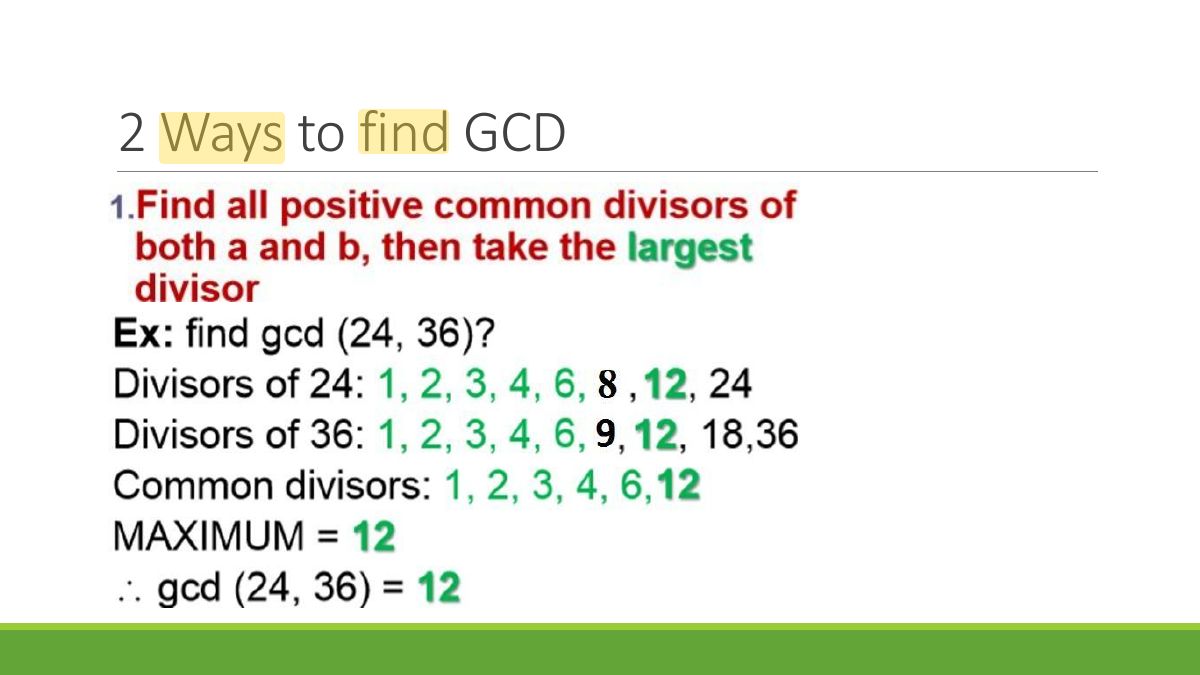
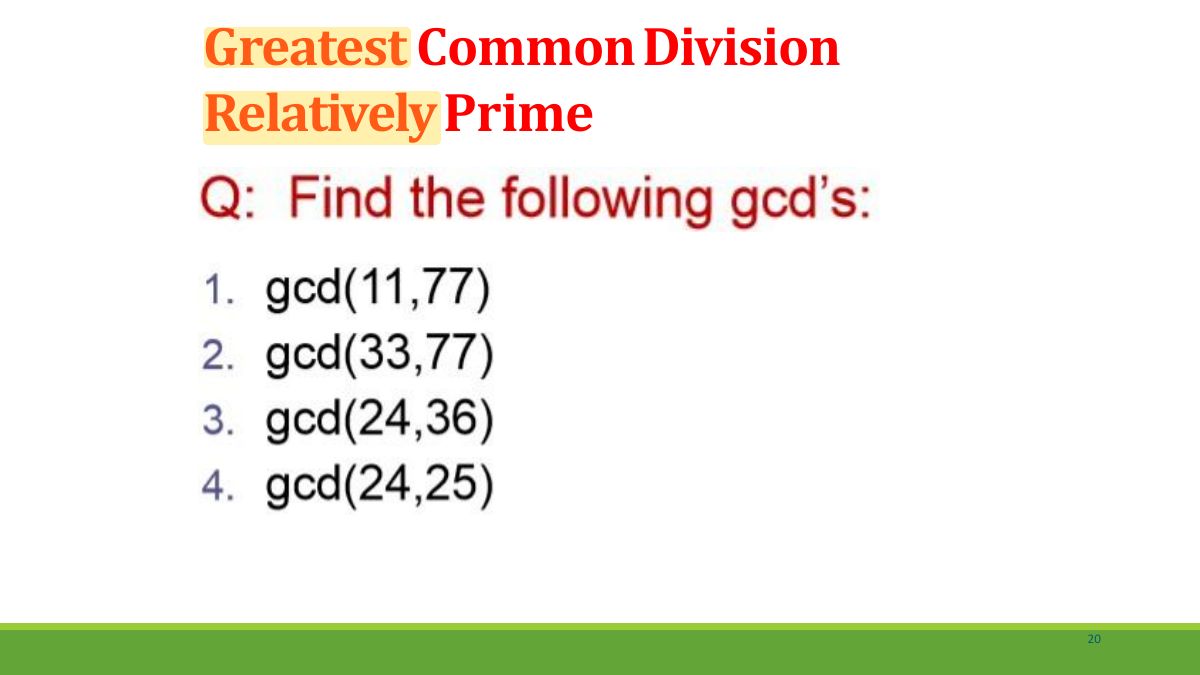
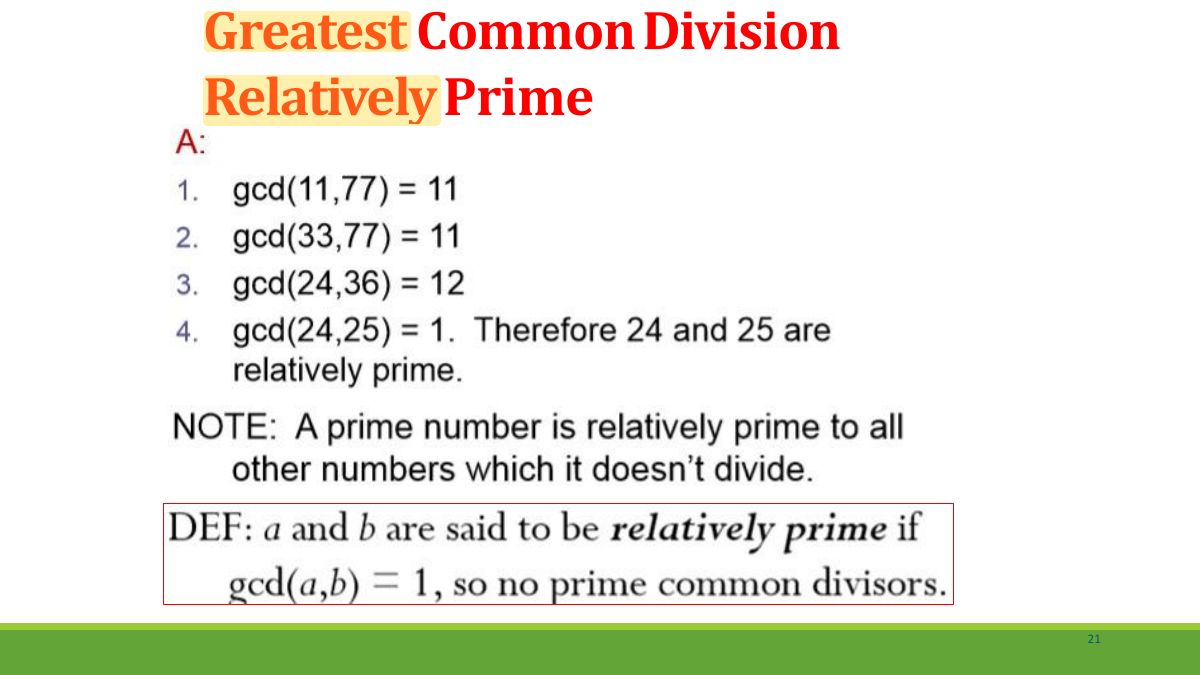
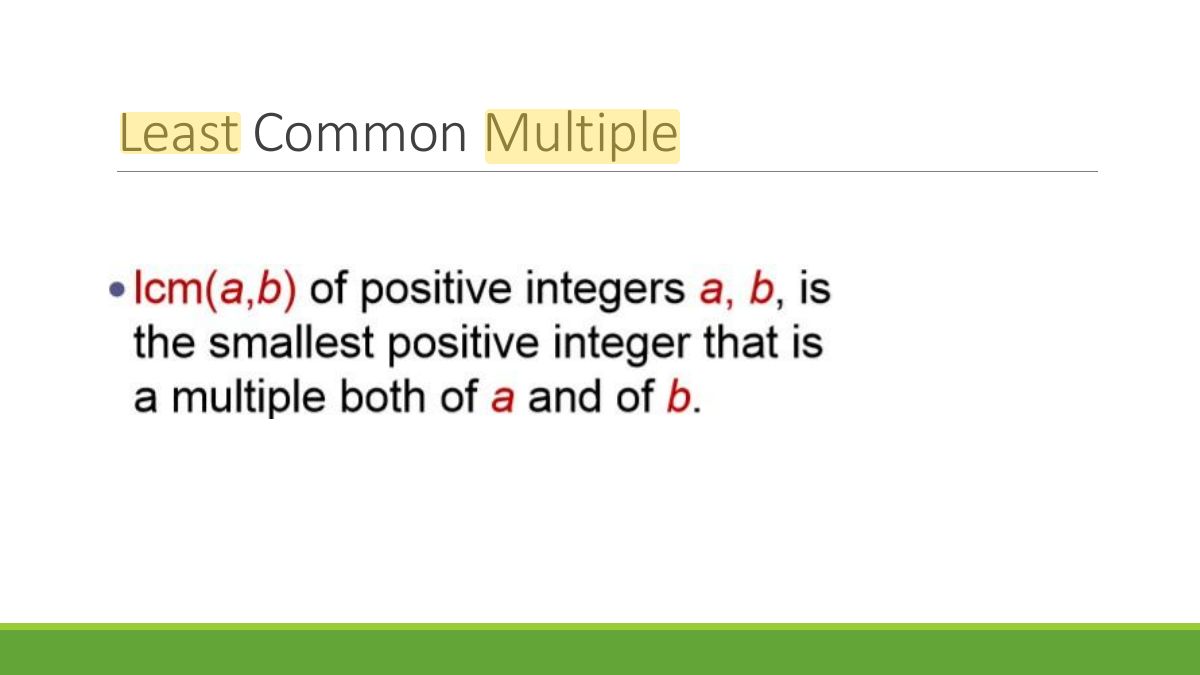
- gcd(a, b): largest integer dividing both. Relatively prime when gcd = 1.
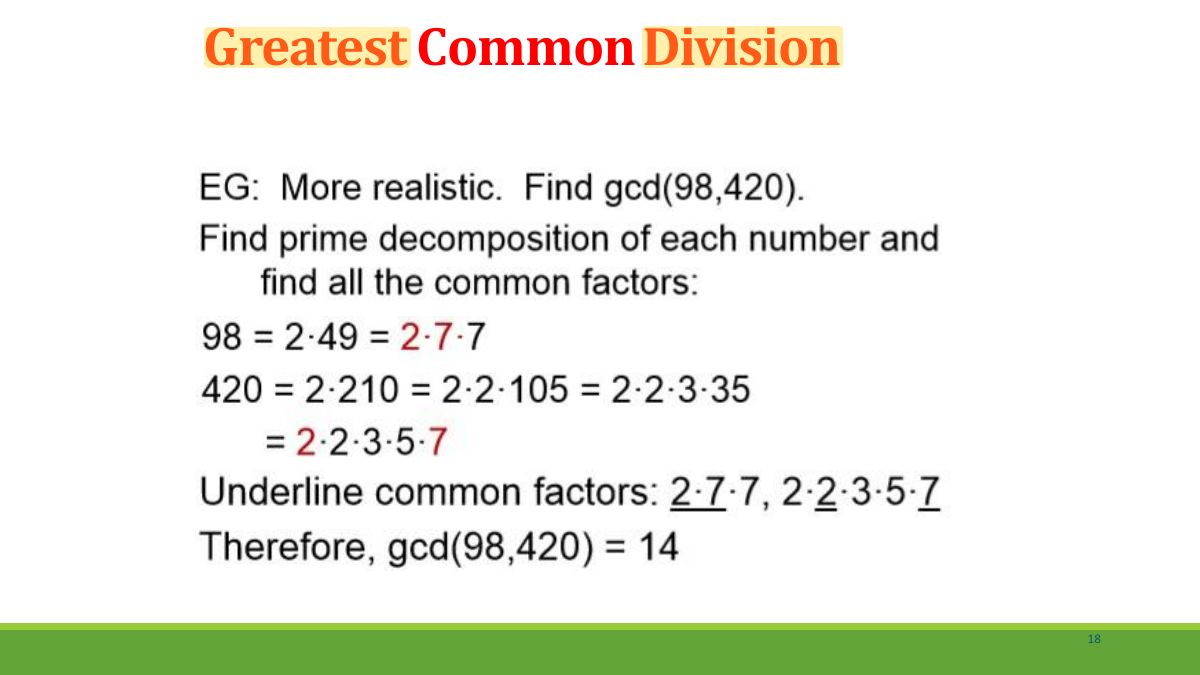
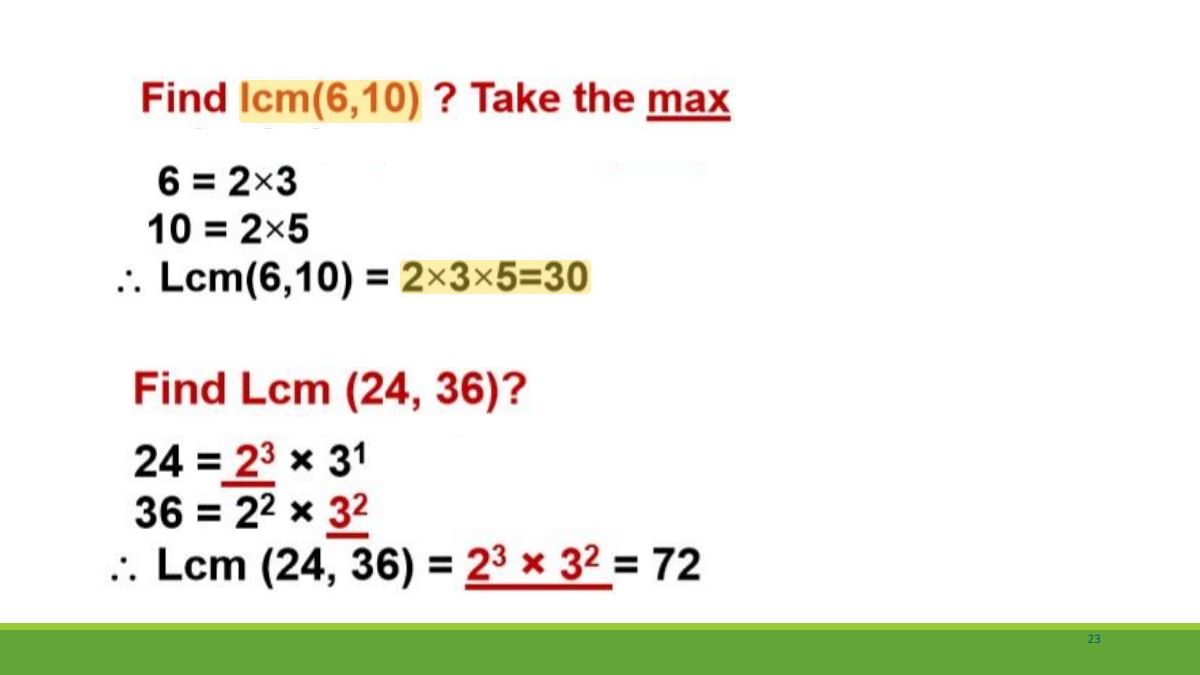
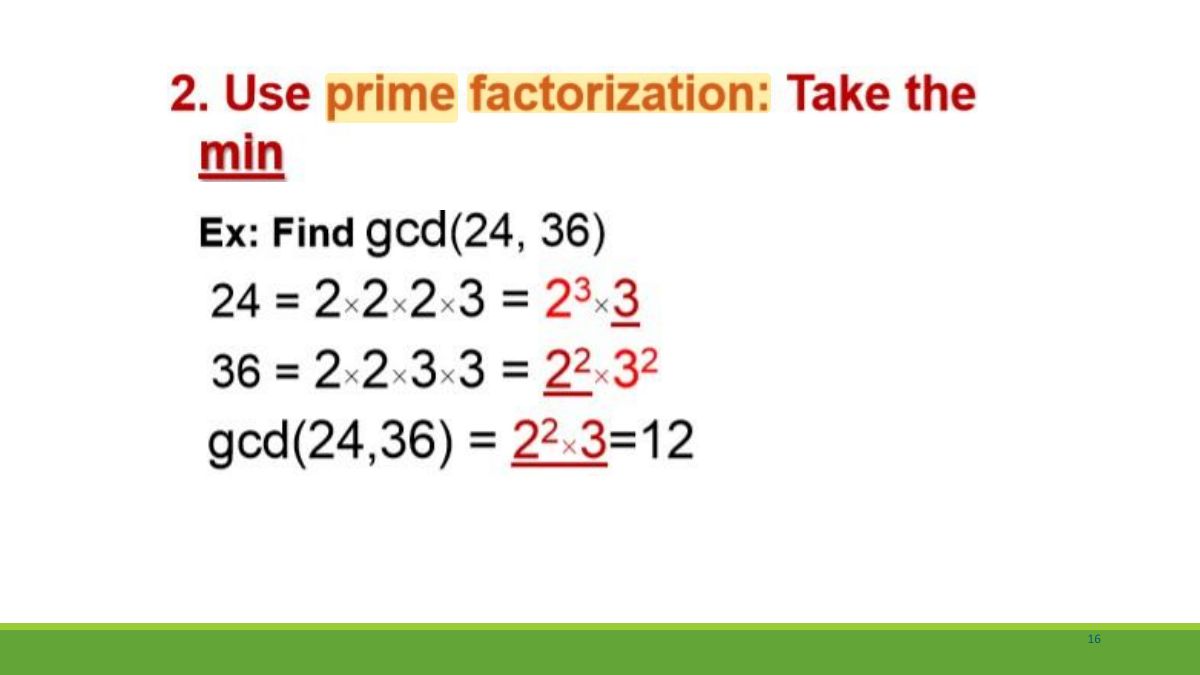
- gcd via prime factorizations: take the MIN power of each prime. lcm: take the MAX power.
- gcd(a, b)·lcm(a, b) = a·b.
🎯 How this can come up · 2 questions
gcd(120, 500) =
2³·3·5 and 2²·5³ → 2²·5.
If gcd(a, b) = 6 and ab = 360, lcm(a, b) =
360 / 6.
- Pairwise relatively prime: every pair has gcd 1.
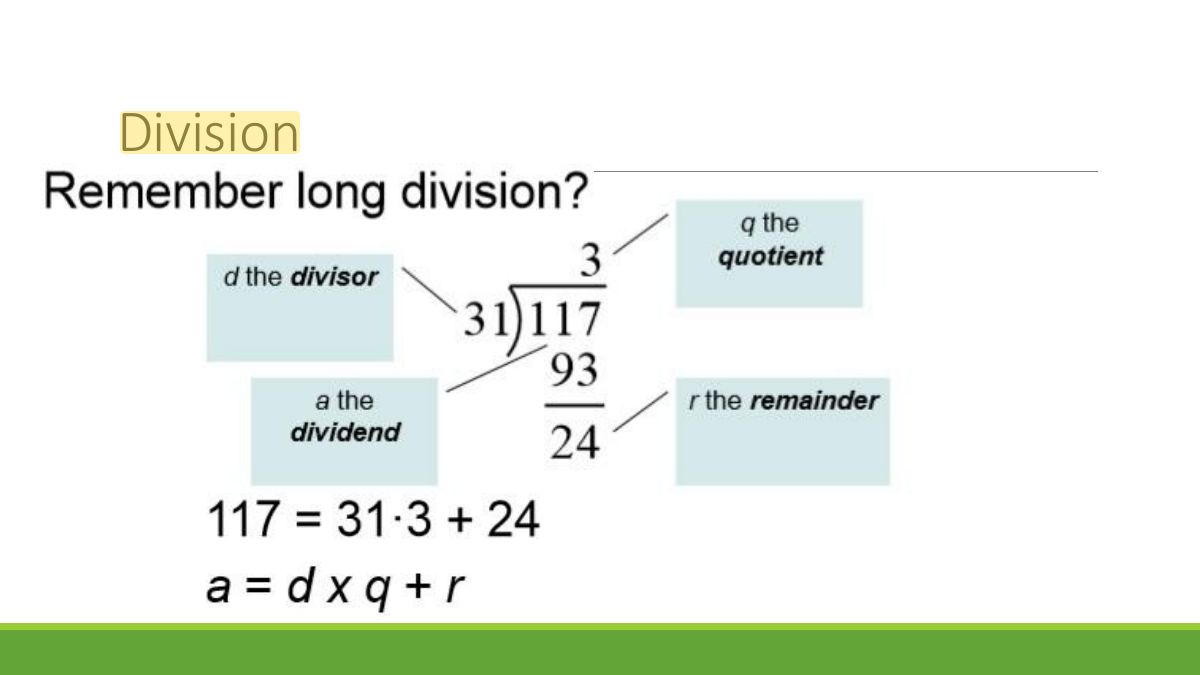
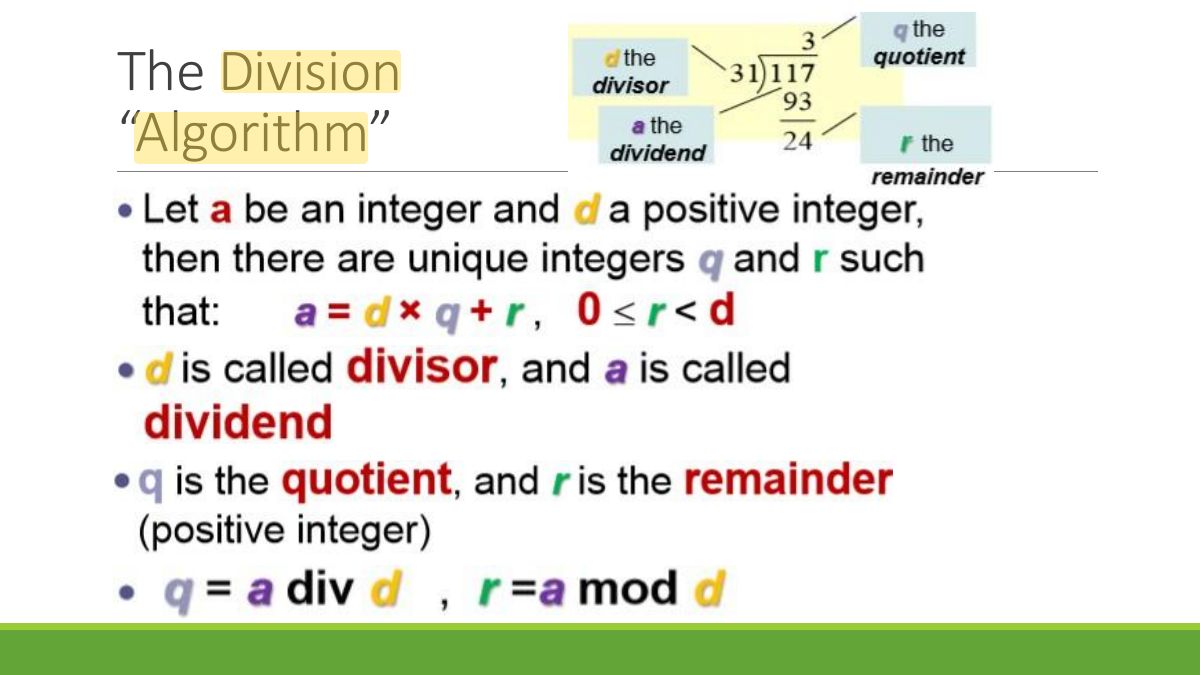
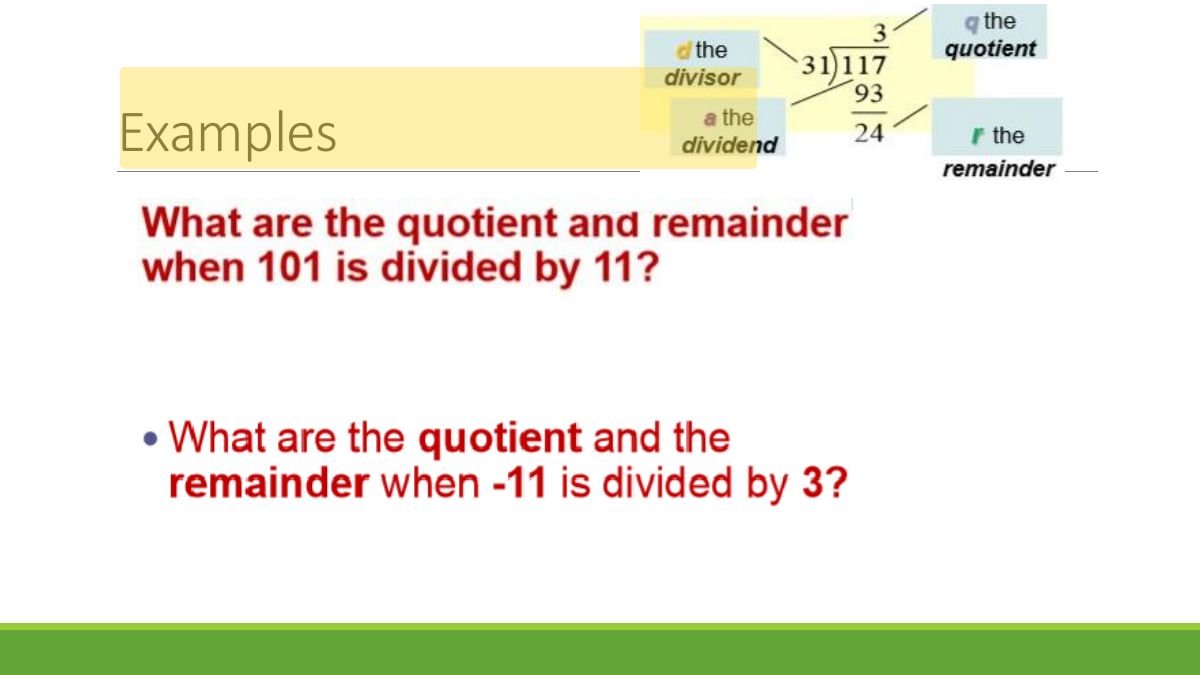
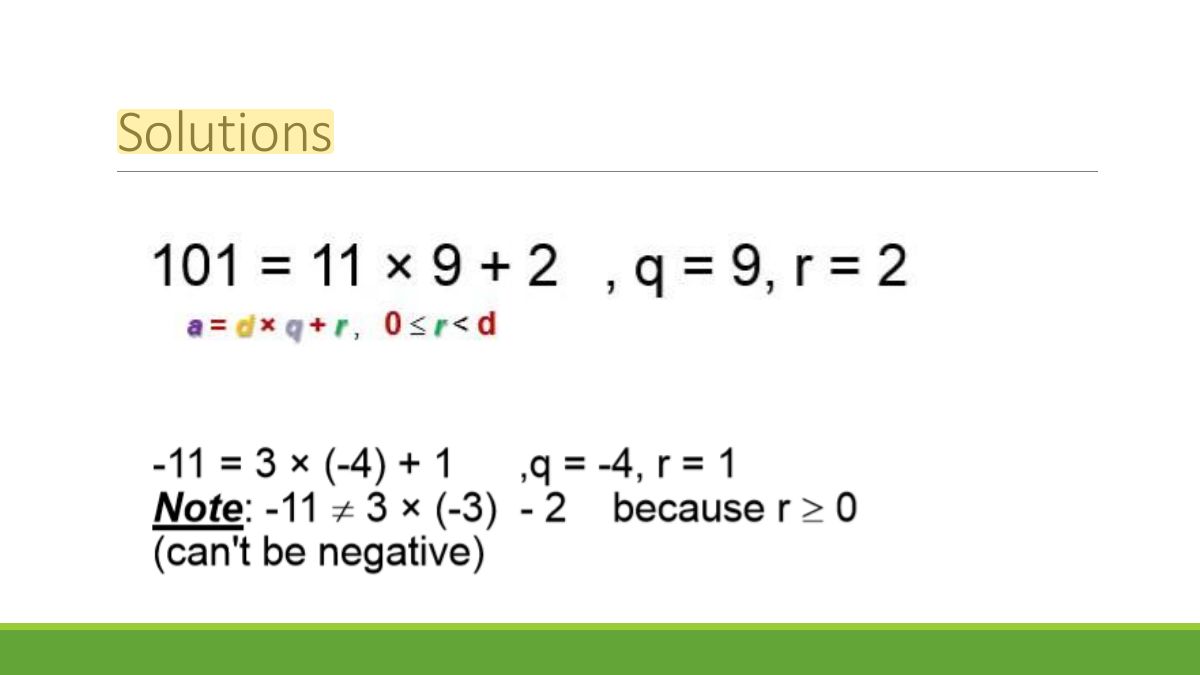
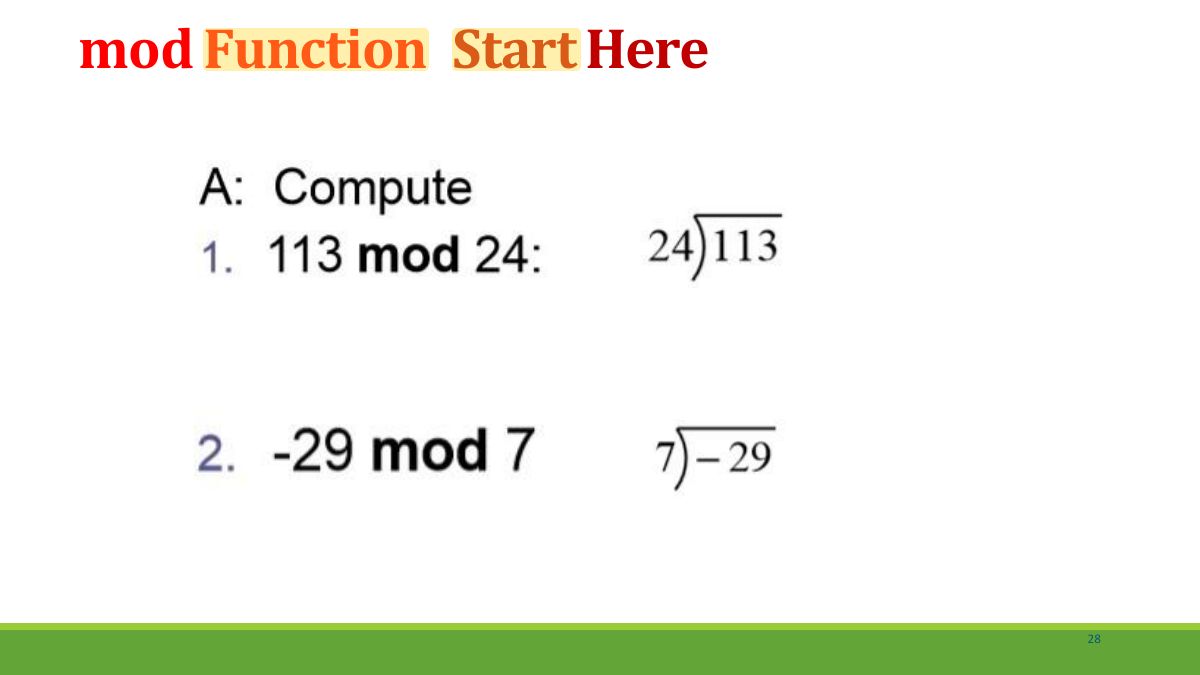
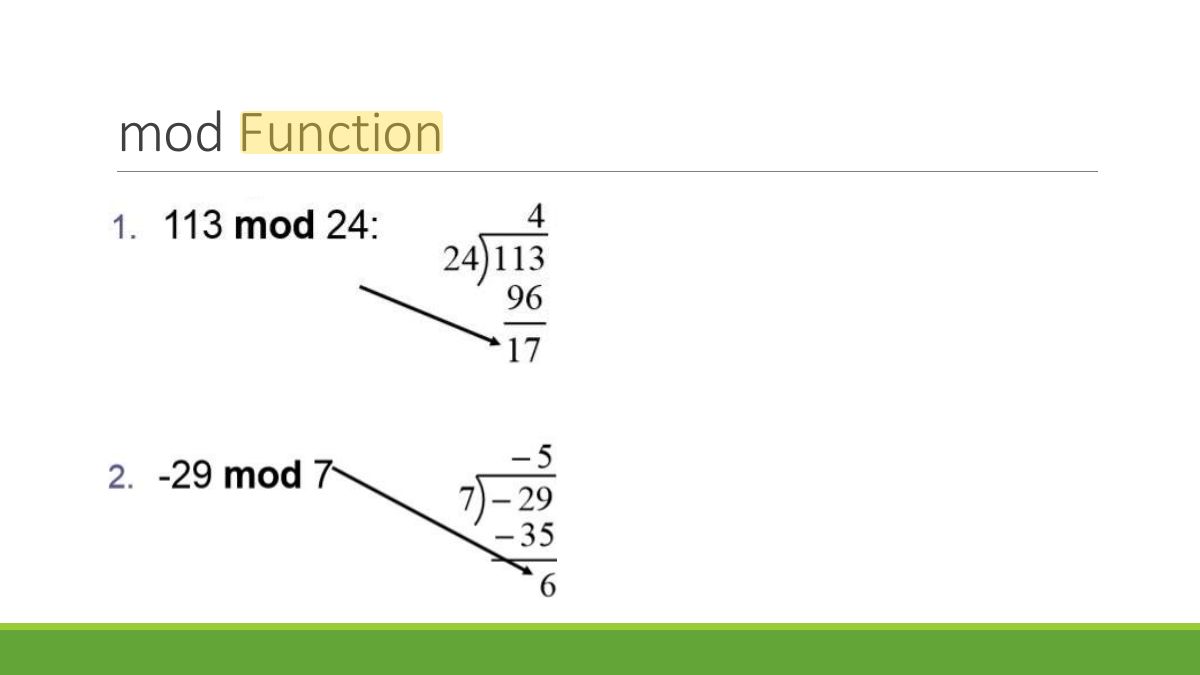
- Division algorithm: a = dq + r with 0 ≤ r < d; q = a div d, r = a mod d.
🎯 How this can come up · 1 question
−11 mod 3 =
Correct: 1.
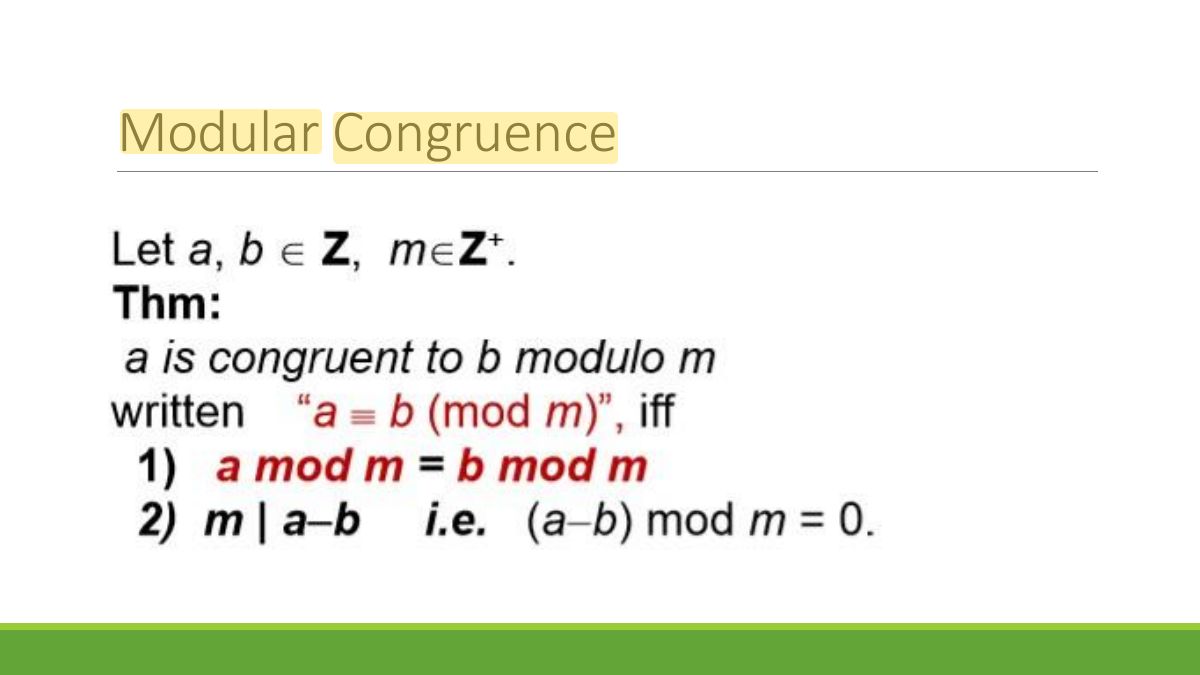
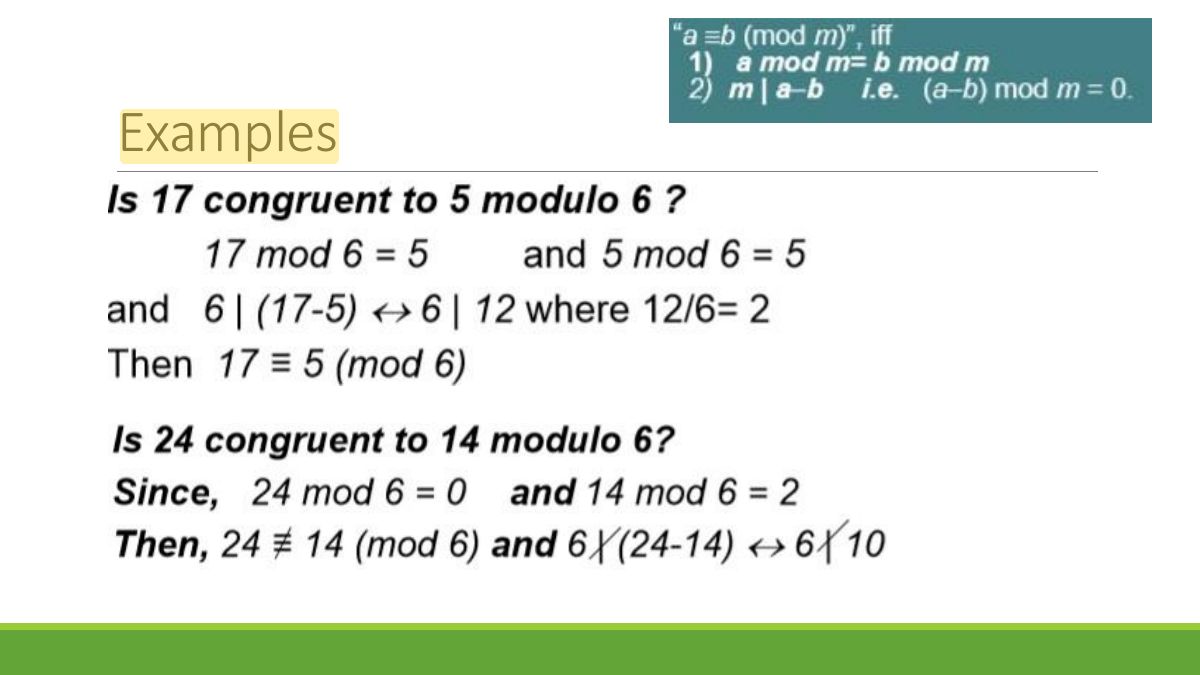
- a ≡ b (mod m) when m | (a − b), i.e. a mod m = b mod m.
🎯 How this can come up · 1 question
17 ≡ 5 (mod 6).
True. 6 | 12.
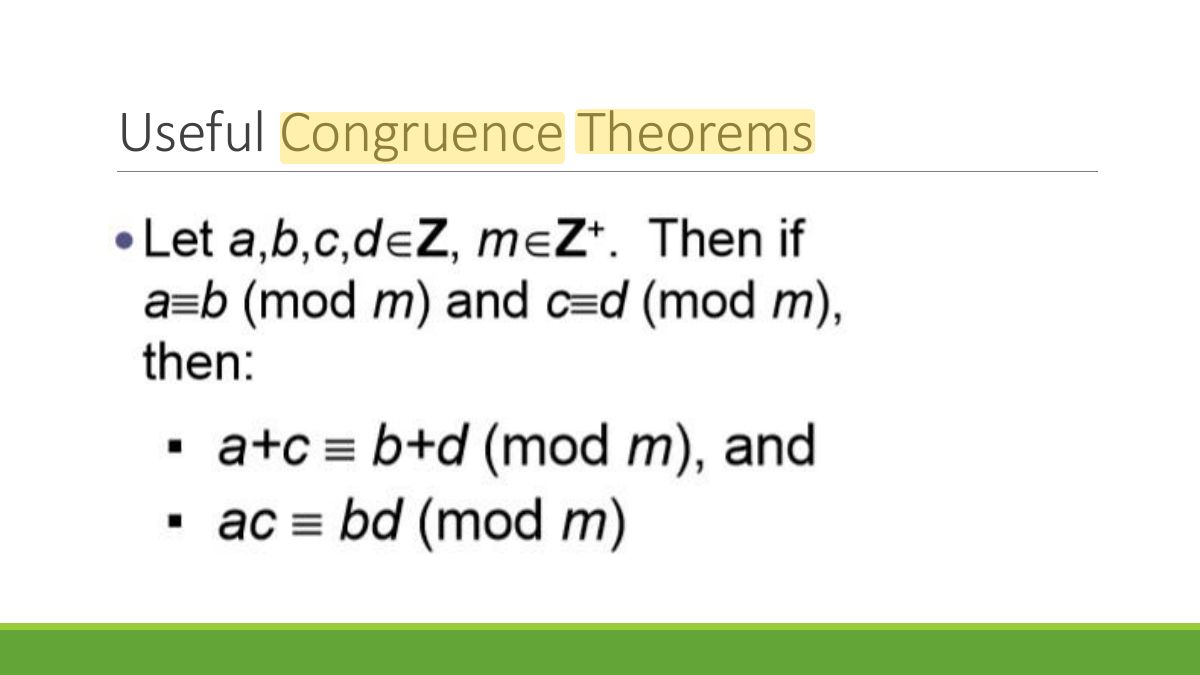
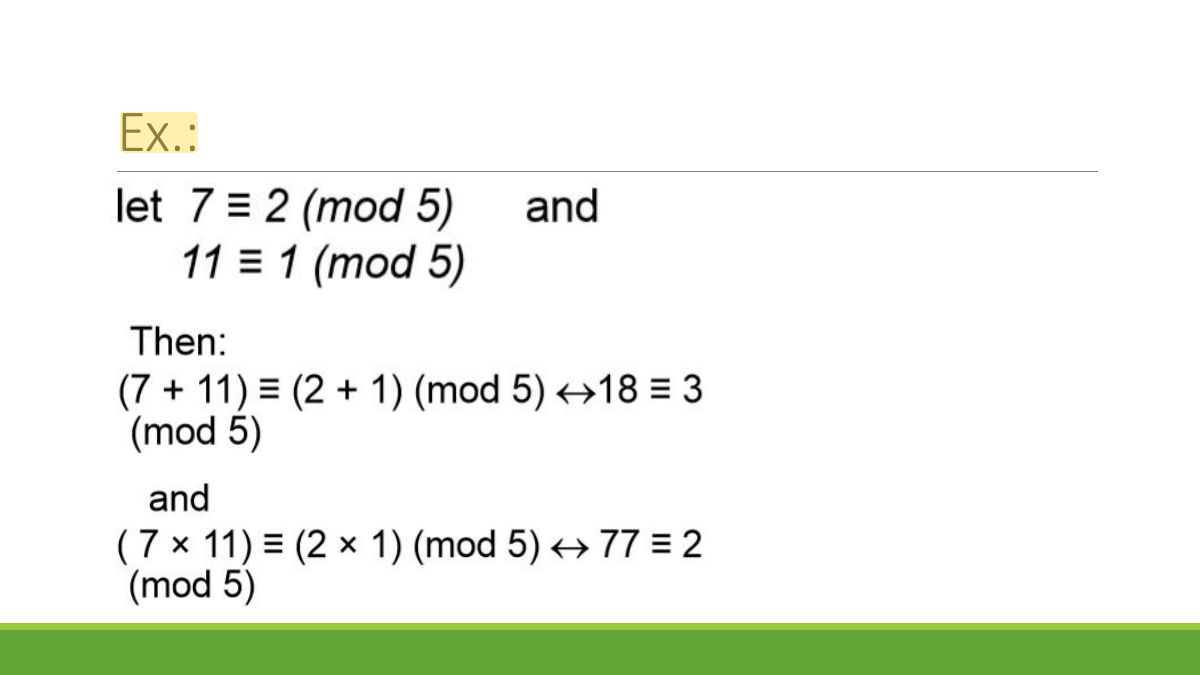
- If a ≡ b and c ≡ d (mod m) then a + c ≡ b + d and ac ≡ bd (mod m).
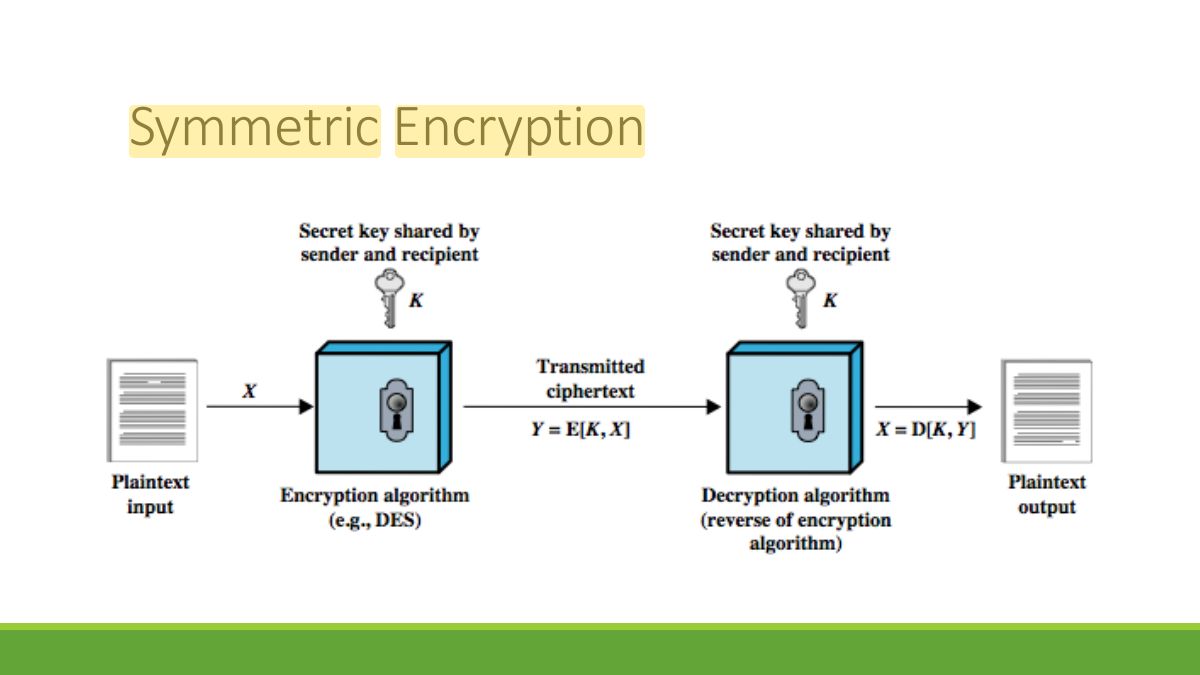
- Symmetric encryption: the same secret key encrypts and decrypts.
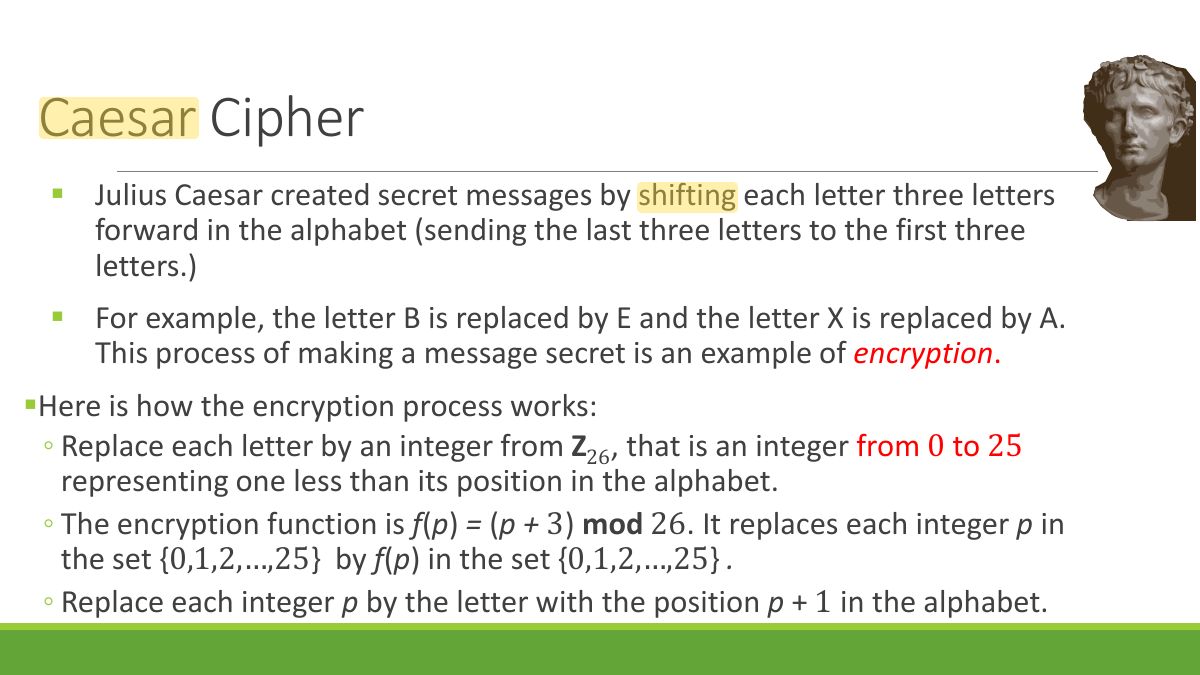
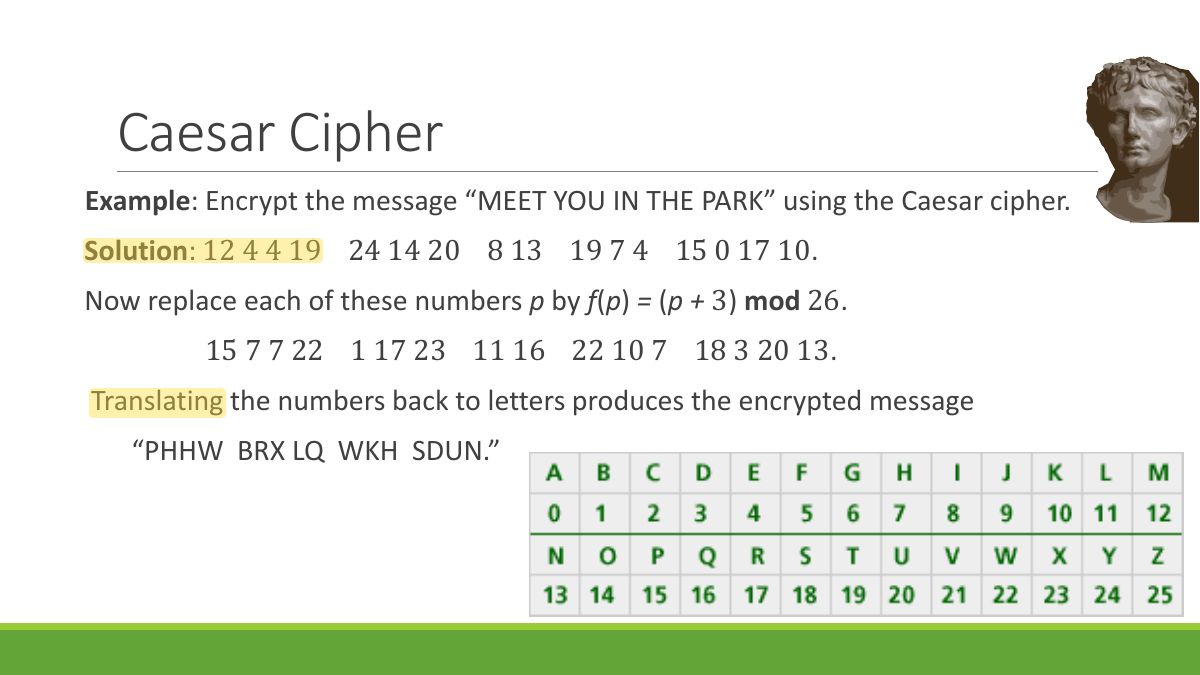
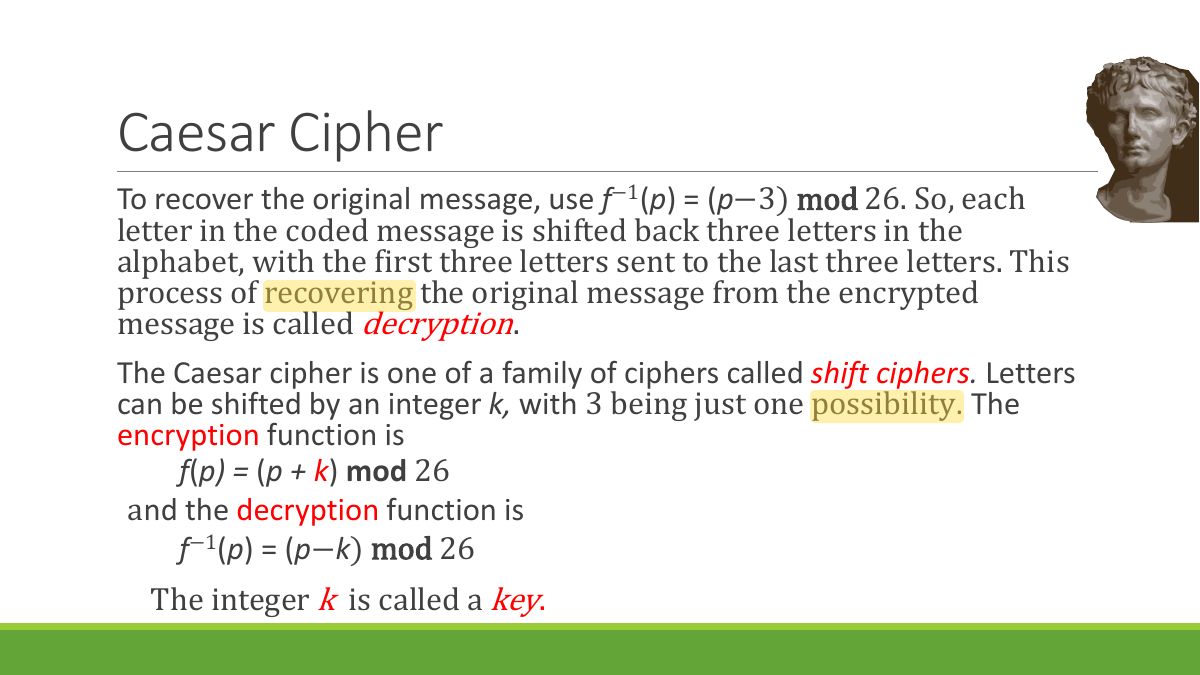
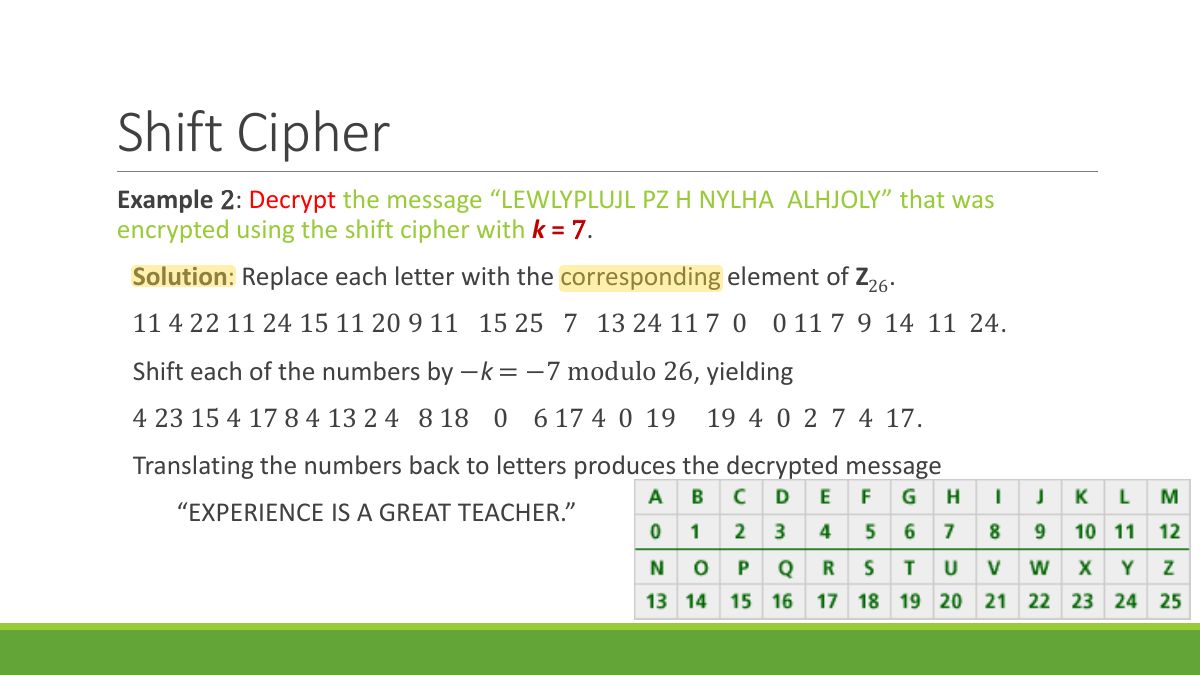
- Caesar cipher: f(p) = (p + 3) mod 26; decrypt with (c − 3) mod 26.
🎯 How this can come up · 1 question
Caesar (shift 3) encrypts "HI" as:
H(7)+3 = K, I(8)+3 = L.
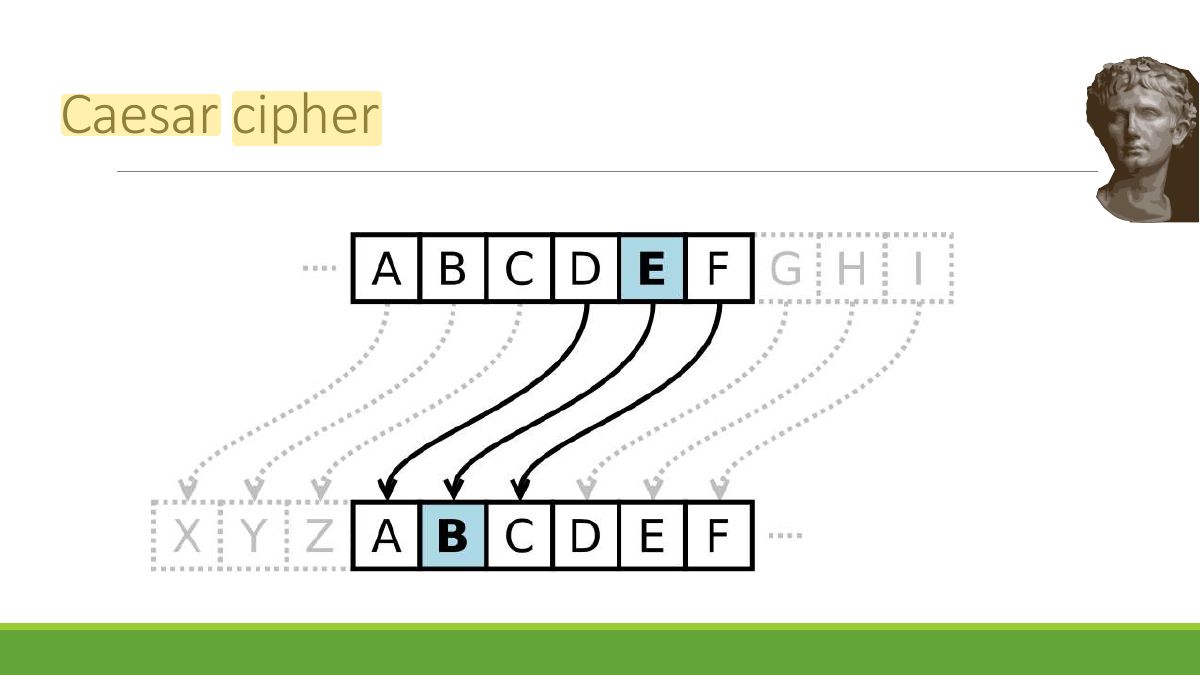
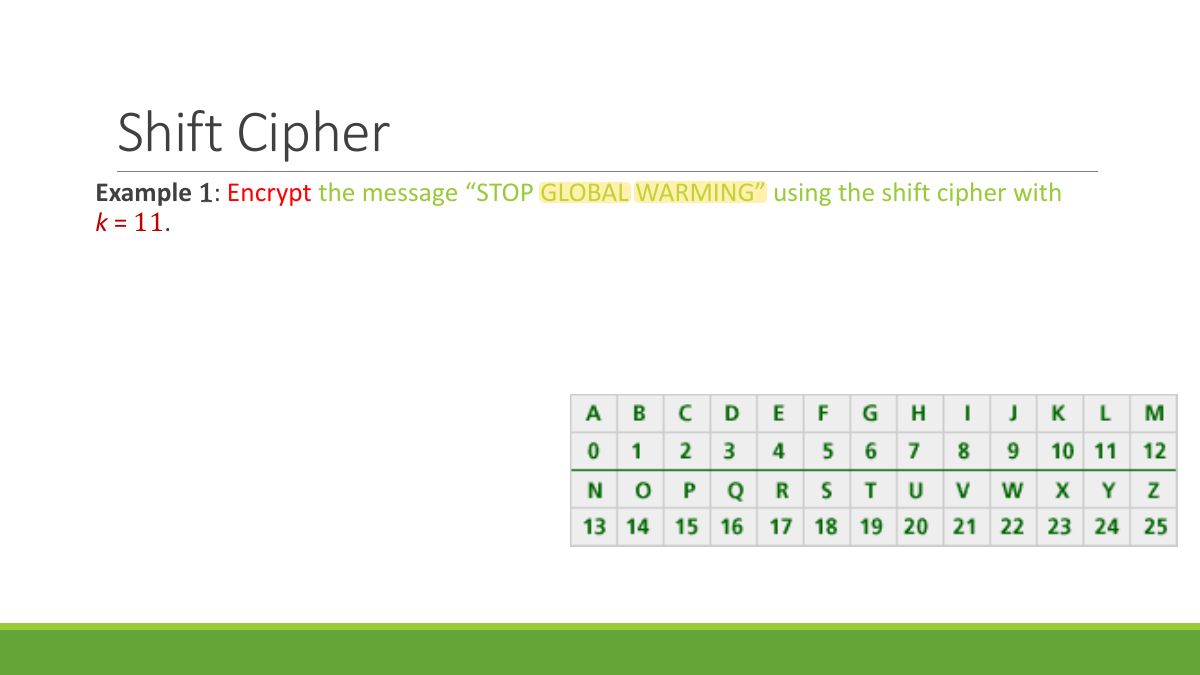
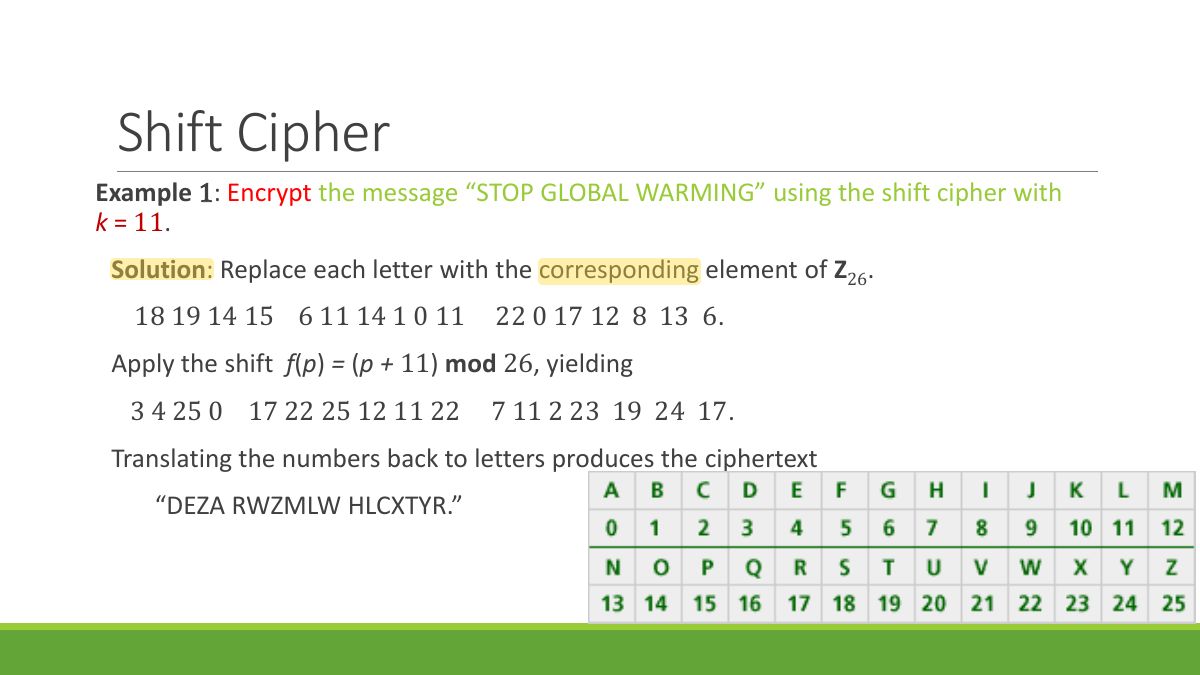
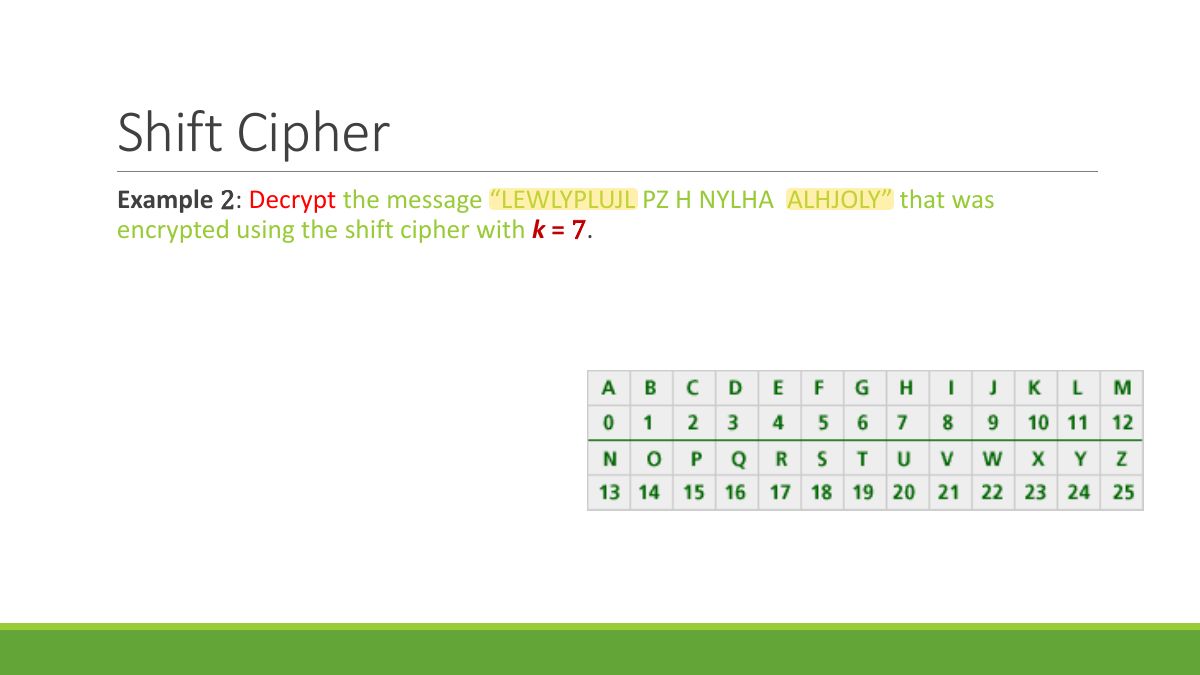
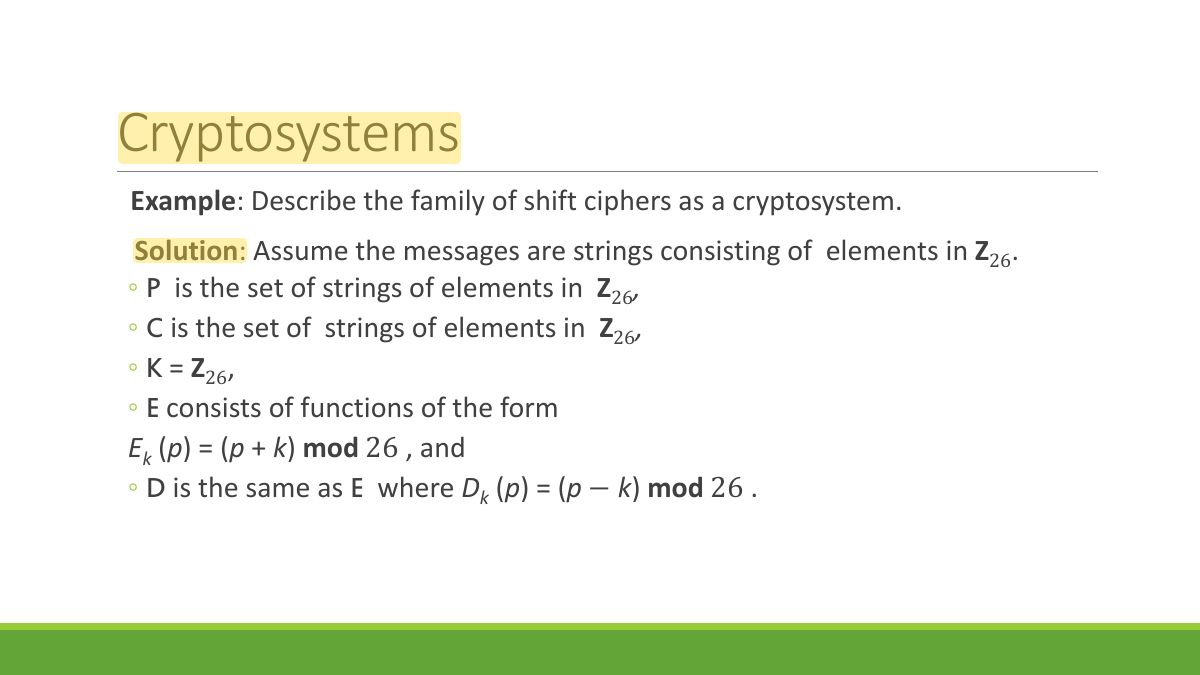
- Shift cipher: f(p) = (p + k) mod 26, f⁻¹(c) = (c − k) mod 26.
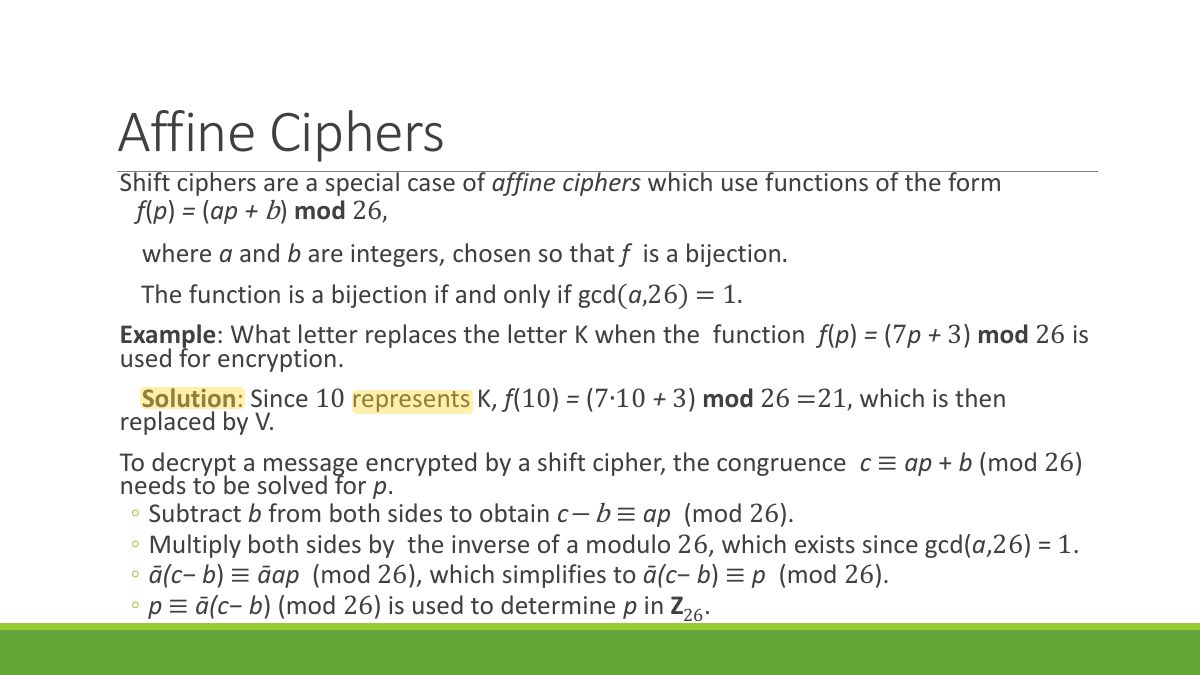
- Affine cipher: f(p) = (ap + b) mod 26 with gcd(a, 26) = 1 so it can be inverted.
🎯 How this can come up · 1 question
In an affine cipher f(p) = (ap + b) mod 26, a must satisfy:
Correct: gcd(a, 26) = 1.
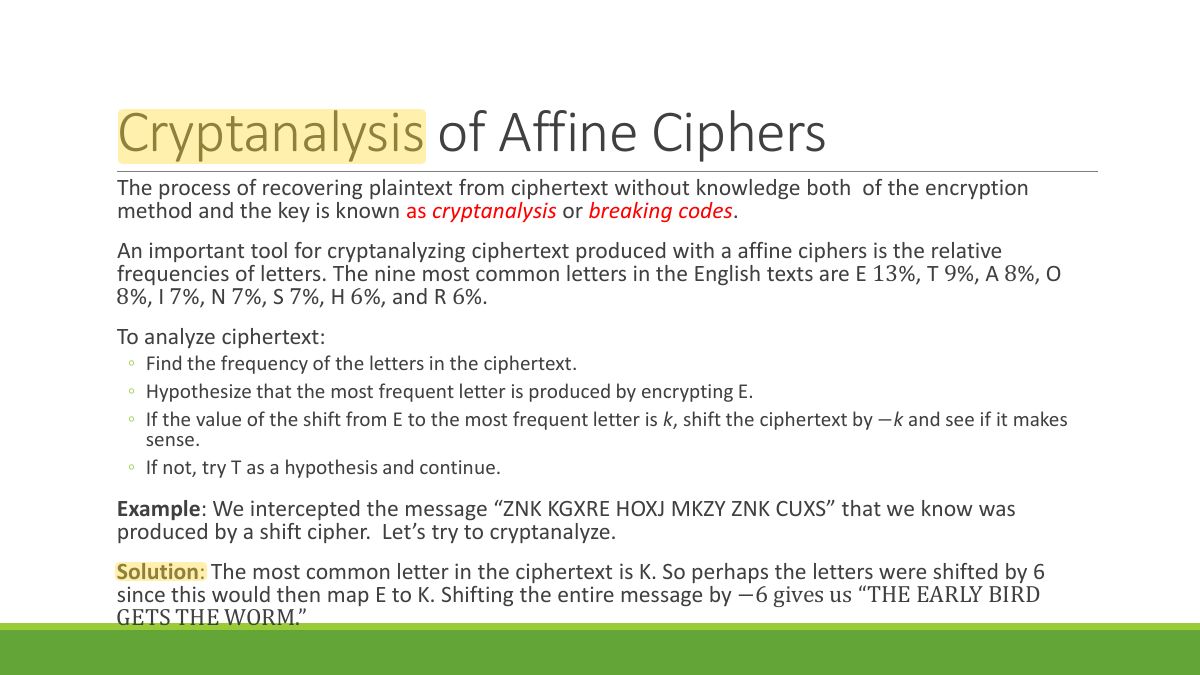
- Frequency analysis breaks shift and affine ciphers (E, T, A are the most common letters).
- Public key: anyone can encrypt with the public key; only the private key decrypts.
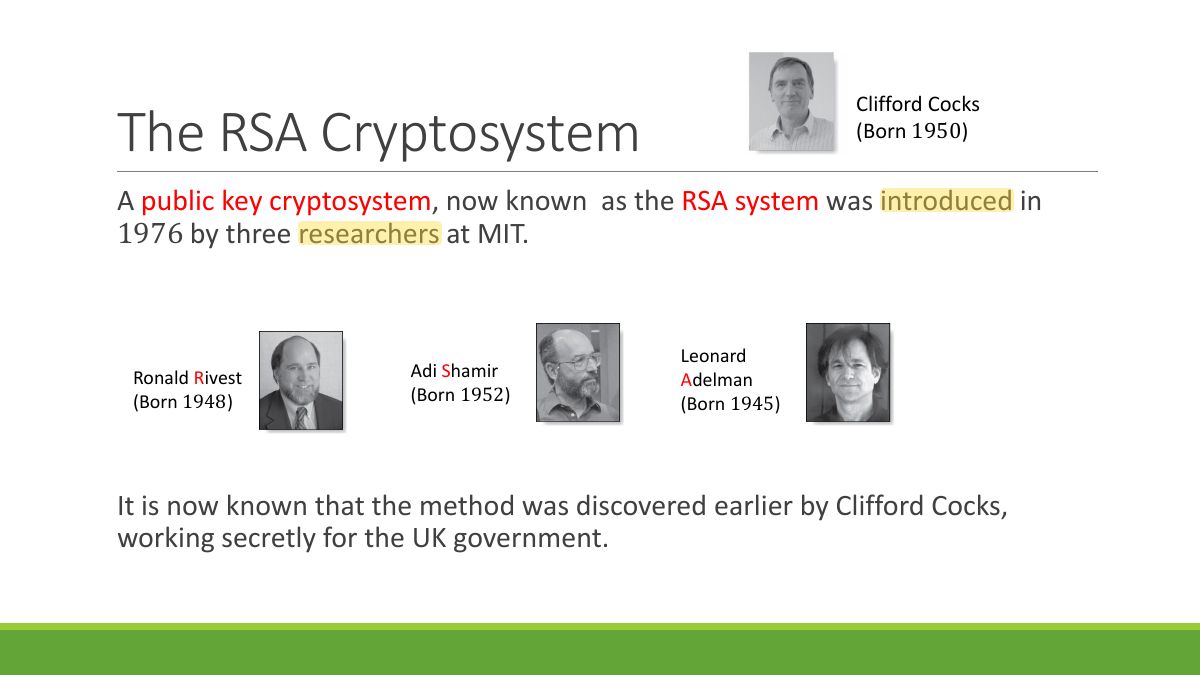
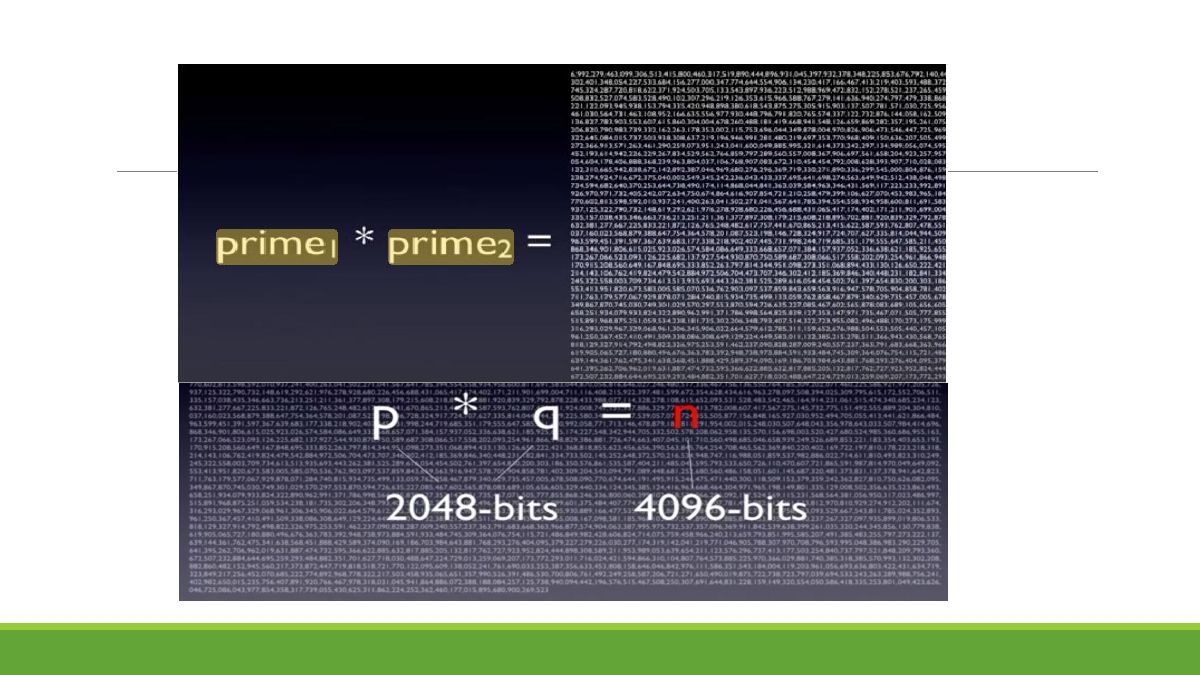
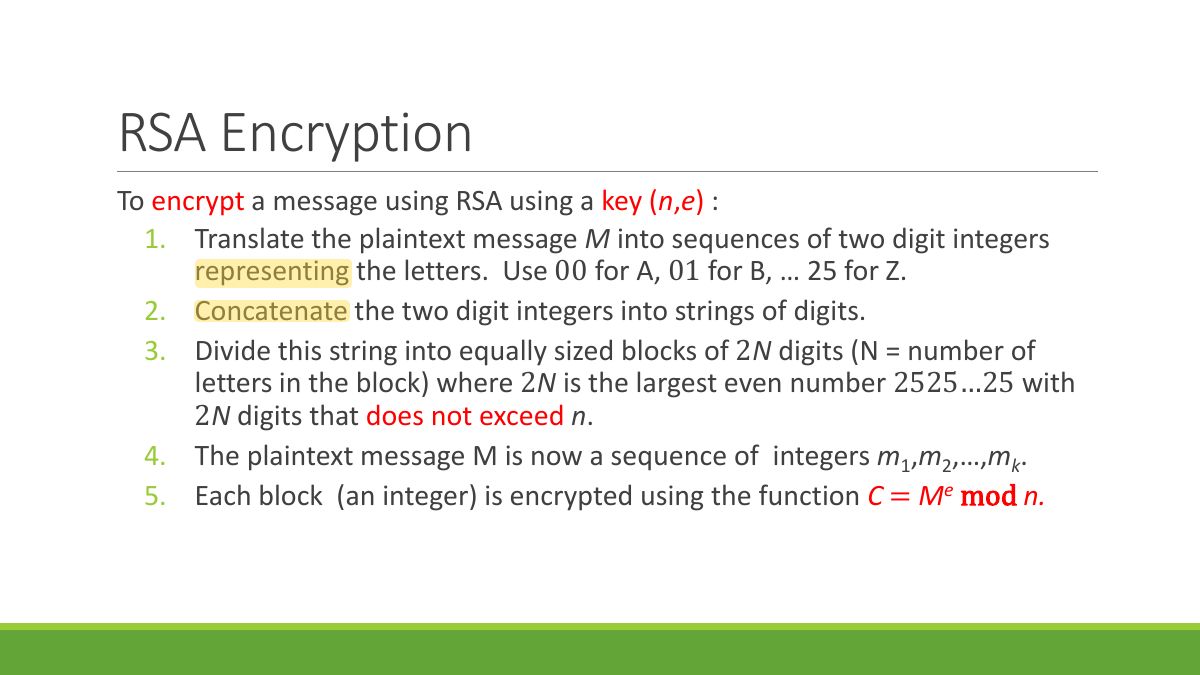
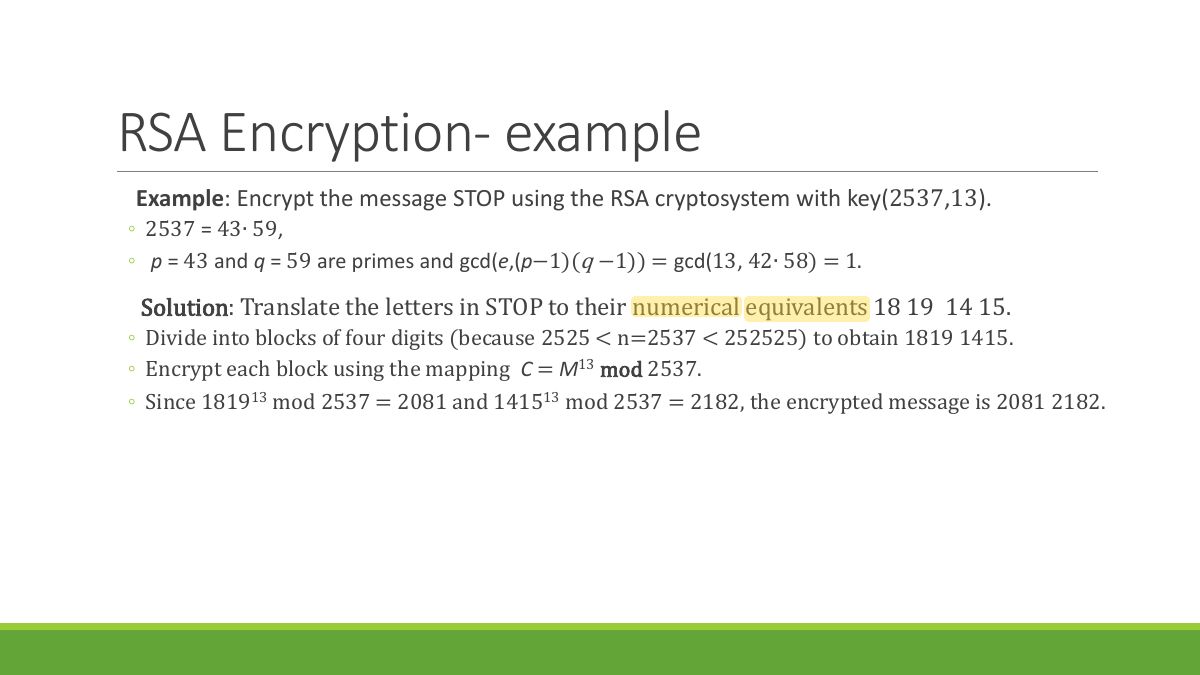
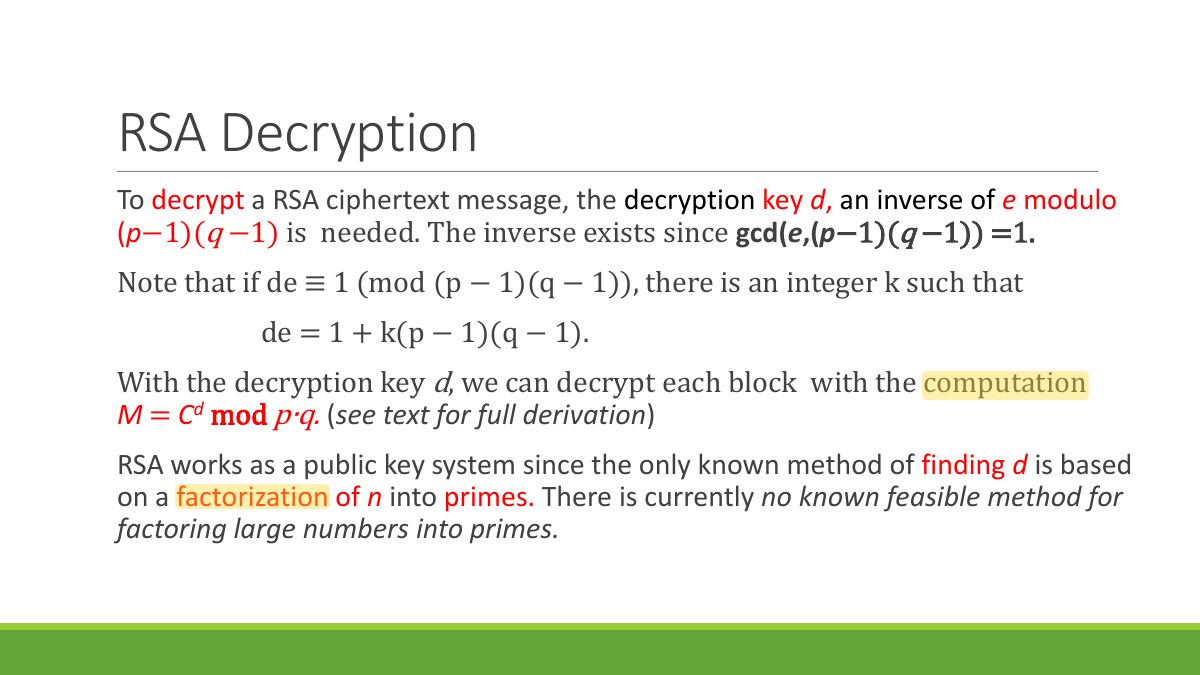
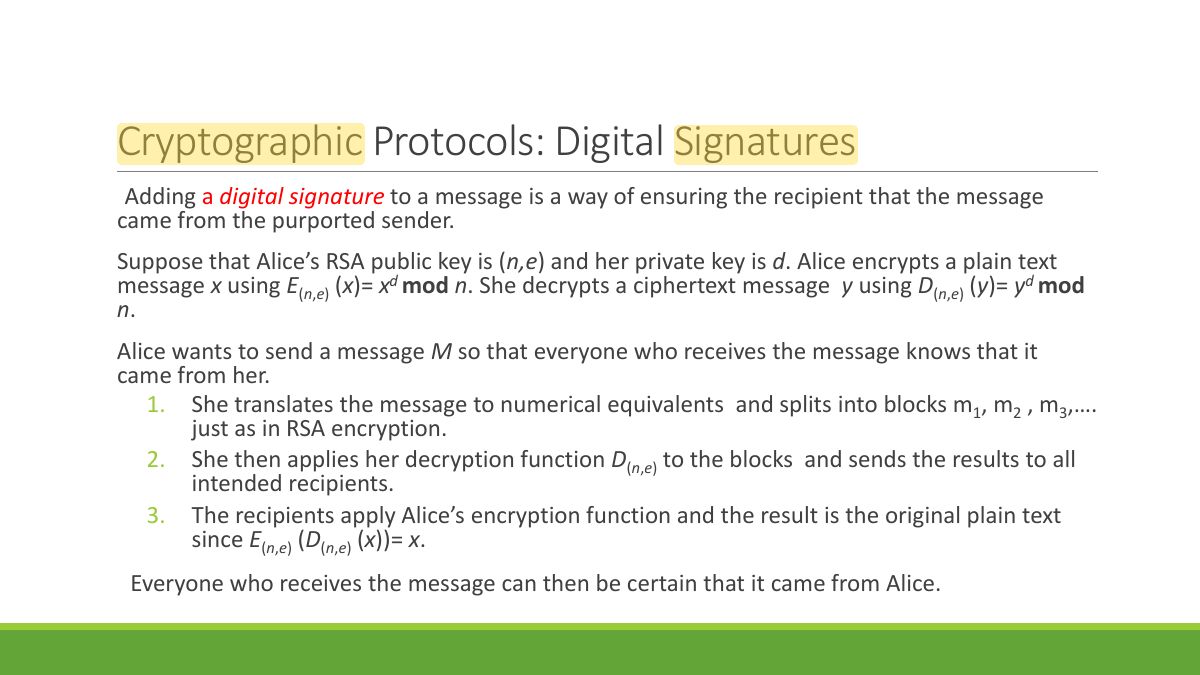
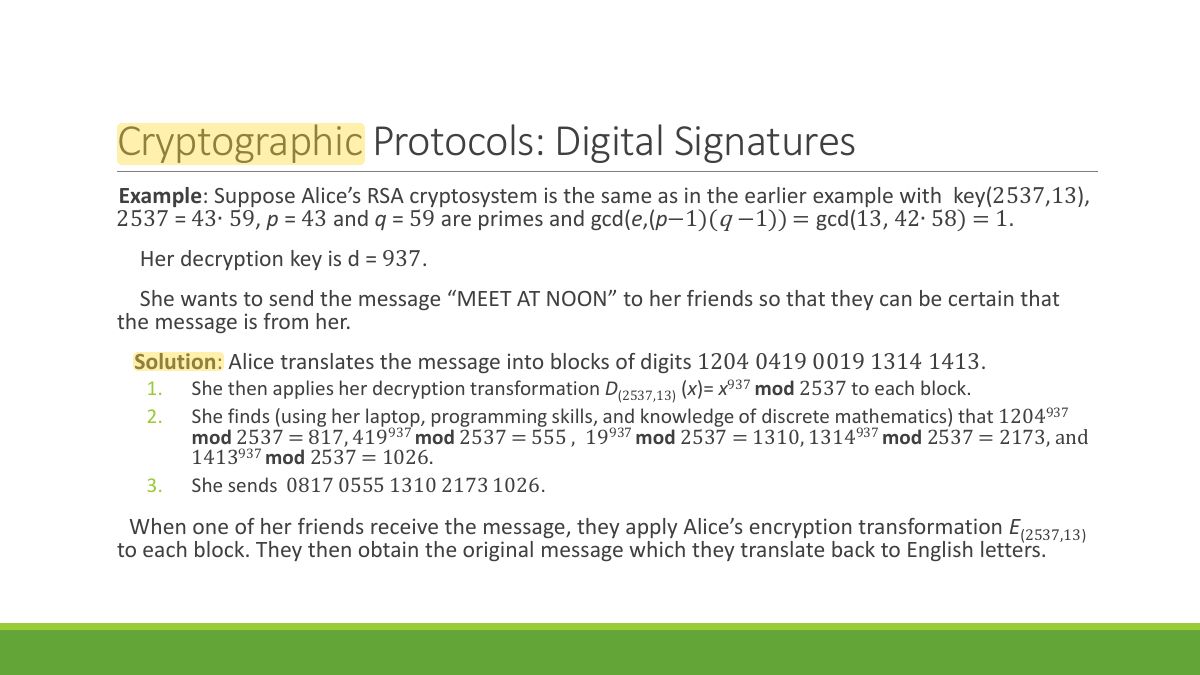
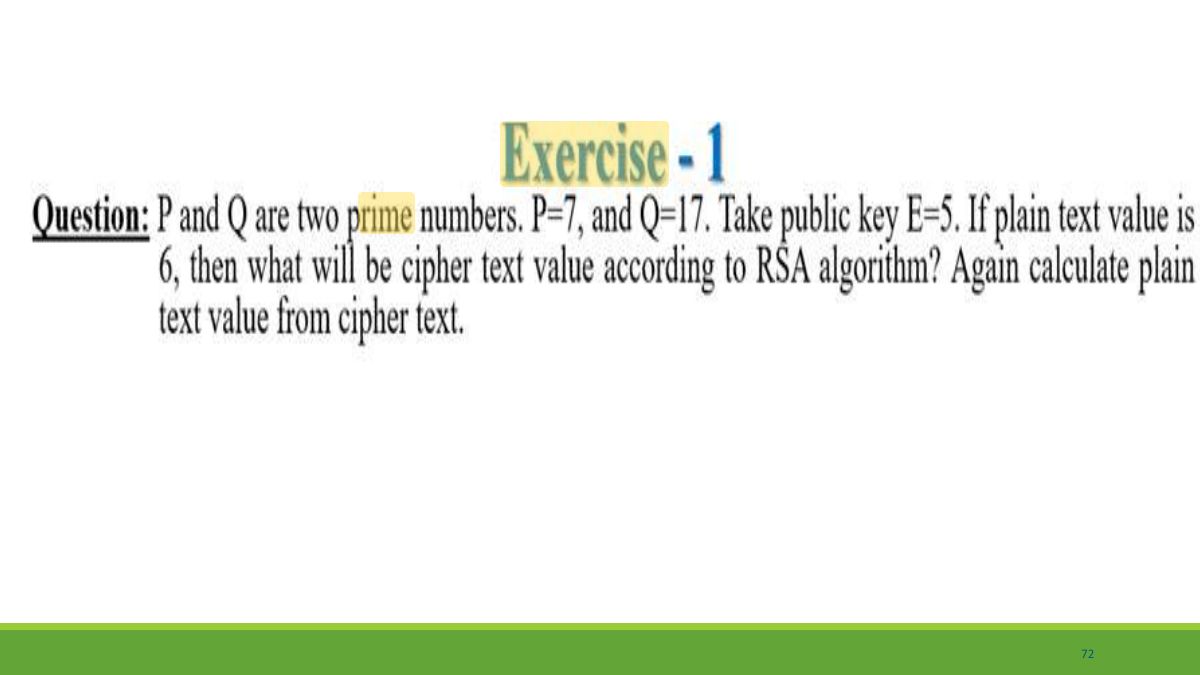
- RSA: n = pq, choose e with gcd(e, (p−1)(q−1)) = 1, d = e⁻¹ mod (p−1)(q−1).
- Encrypt: C = Mᵉ mod n.
- Decrypt: M = Cᵈ mod n.
🎯 How this can come up · 2 questions
RSA with p = 3, q = 11, e = 3. Find n, φ, and d.
n = 33, φ = (p−1)(q−1) = 20. d is the inverse of 3 mod 20: 3·7 = 21 ≡ 1, so d = 7.
In RSA, which key is kept secret?
(e, n) is public.
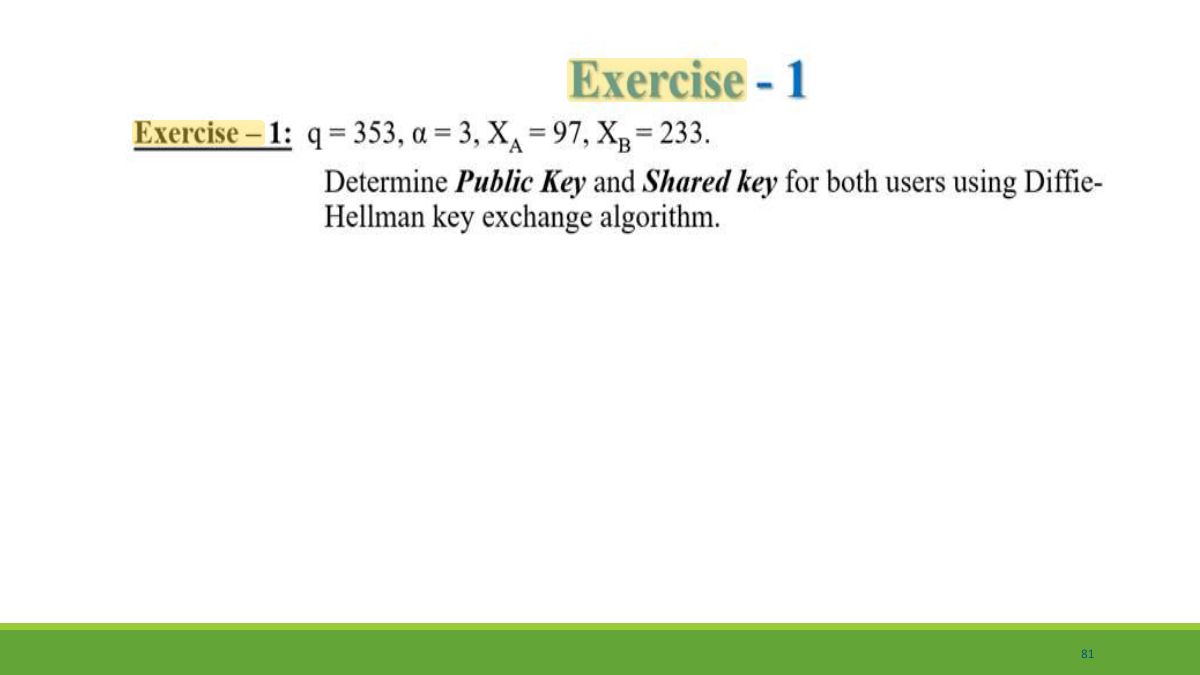
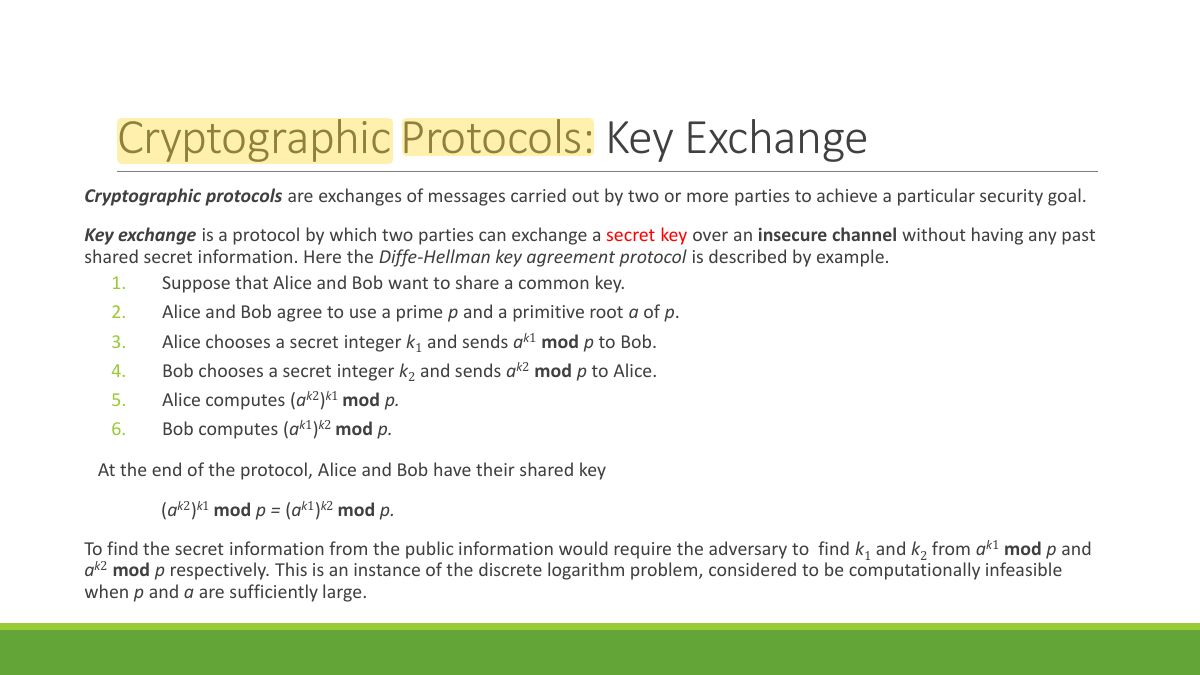
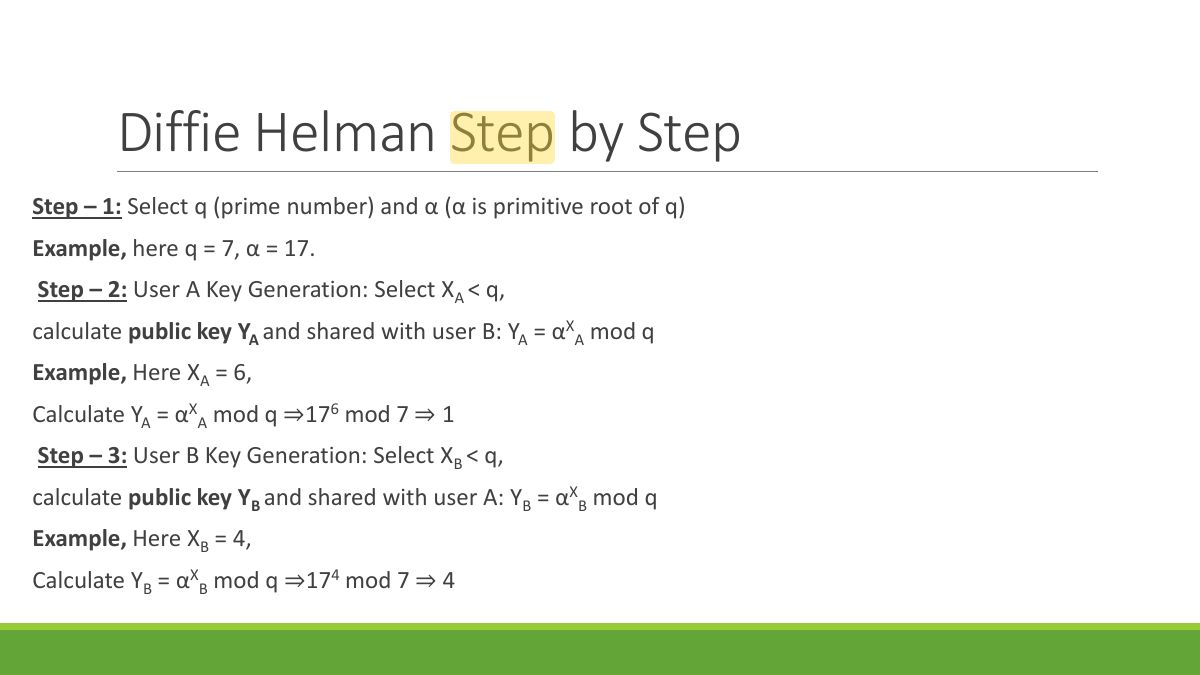
- Diffie–Hellman: agree on prime p and base g; Alice sends gᵃ mod p, Bob sends gᵇ mod p; both compute the shared key gᵃᵇ mod p.
🎯 How this can come up · 1 question
p = 23, g = 5, a = 6, b = 15. Alice sends:
Correct: 5⁶ mod 23 = 8.
No slides match this filter.